



Templates
Wi-Fi Policy Template (Free Word + PDF)
Free Wi-Fi policy template in Word and PDF, with an Excel tracker: 17 sections on SSIDs, WPA3, guest terms of use, BYOD and rogue AP checks.
Free IT governance policy template in Word and PDF, with an Excel tracker: 17 sections, a RACI, decision rights, KPIs and a framework example.

Content writer, trio.so
An IT governance policy says who decides what about technology in your company: who sets IT priorities, who approves an IT investment and up to what amount, how much IT risk you accept, and how the board and management check that IT delivers. This free IT governance policy template gives you that policy as an editable Word document with 17 sections, written for companies of 50 to 1,000 people.
Every decision sits in [brackets] with a default you can keep or change. The download also includes a PDF guide with a one-page IT governance framework example and a worked example of a 200-person company, and an Excel tracker for your RACI, decisions, investments, policies, risks, KPIs and steering committee meetings. The policy maps to COBIT 2019, ISO/IEC 38500:2024, NIST CSF 2.0 and ISO/IEC 27001:2022 by ID.
In short
An IT governance policy is a document the board or owners approve that sets how the company directs and oversees its use of IT. It names the governance bodies and roles, gives each one its decision rights, sets the approval thresholds for IT spending, states the risk appetite, and says which measures the board and management review and how often. The day-to-day records, such as decisions, investments, risks and KPIs, live in a tracker.
It is also the IT governance document people search for: the single place that explains your IT governance framework. The other IT documents sit under it. The information security policy, the acceptable use policy and the access control policy say what the rules are; the governance policy says who sets those rules and who approves them.
An ICT governance policy is the same document under another name.
Without governance, IT decisions get made wherever the budget sits. A business unit buys a SaaS tool nobody reviewed, two projects compete for the same engineers, a risk is accepted by whoever happened to be in the room, and nobody can tell the board whether last year's IT spend delivered what it promised. A written policy fixes six things:
A policy does not make IT governance happen on its own. It works when a steering committee holds its meetings on schedule, looks at the same dashboard each time, and records what it decided. The tracker in this download is built around that rhythm.
The two are easy to mix up, and the policy works better when you keep them apart.
| IT governance | IT management | |
|---|---|---|
| Who | The board, owners and the IT steering committee | The CIO or IT lead and the IT team |
| Question | Are we doing the right things with IT, and is it working? | Are we doing things right? |
| Activities | Engage stakeholders, evaluate, direct, monitor | Plan, build, run, monitor |
| Outputs | Strategy, budget, risk appetite, decision rights, policies | Projects, services, standards, procedures, reports |
| Rhythm | Quarterly committee, yearly board review | Daily, weekly and monthly operations |
ISO/IEC 38500:2024 frames governance as the governing body engaging stakeholders, evaluating, directing and monitoring, while management runs IT within the framework the governing body sets. COBIT 2019 makes the same split: its Evaluate, Direct and Monitor domain holds the governance objectives, and four other domains hold the management objectives.
A policy that only says "IT will be aligned with the business" gives nobody anything to follow. The template has 17 sections in four parts: setting direction, deciding, controlling risk and overseeing results.
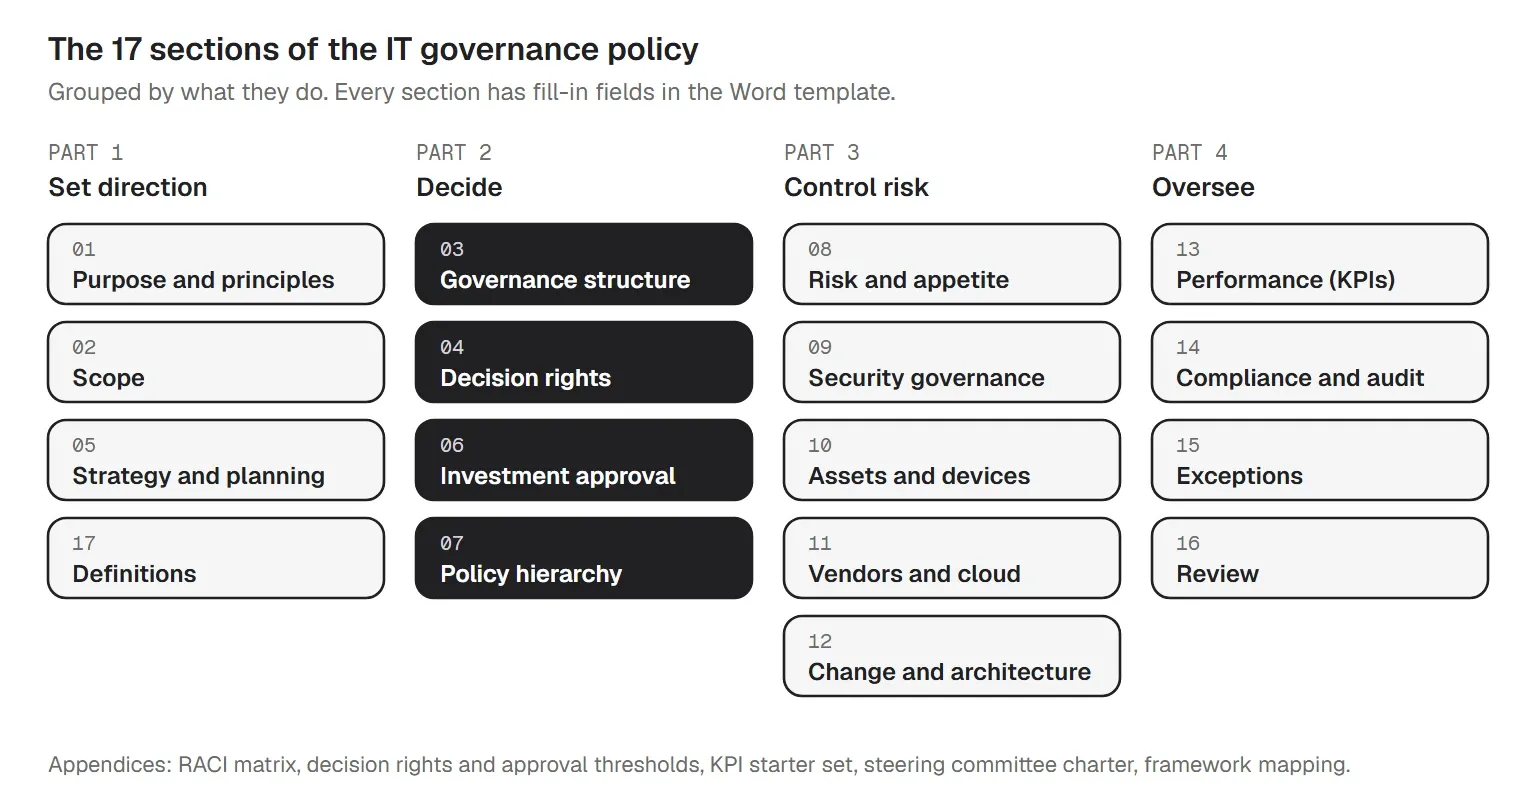
Appendices add a RACI matrix with 16 activities, a decision rights and approval threshold table, a KPI starter set with 16 measures, a steering committee charter with a standing agenda, and a framework mapping. Training and awareness sit in section 7: owners tell staff about new and changed rules, new hires cover them during onboarding, and all staff repeat the training every [12] months.
Most companies of 50 to 1,000 people need four levels. The board or owners approve strategy, budget and risk appetite. An IT steering committee, chaired by the CEO or COO with the CFO, the CIO or IT lead, the security lead and the heads of the main business units, decides within limits every quarter. The CIO or IT lead runs IT. Business and system owners sponsor projects and own their systems and data.
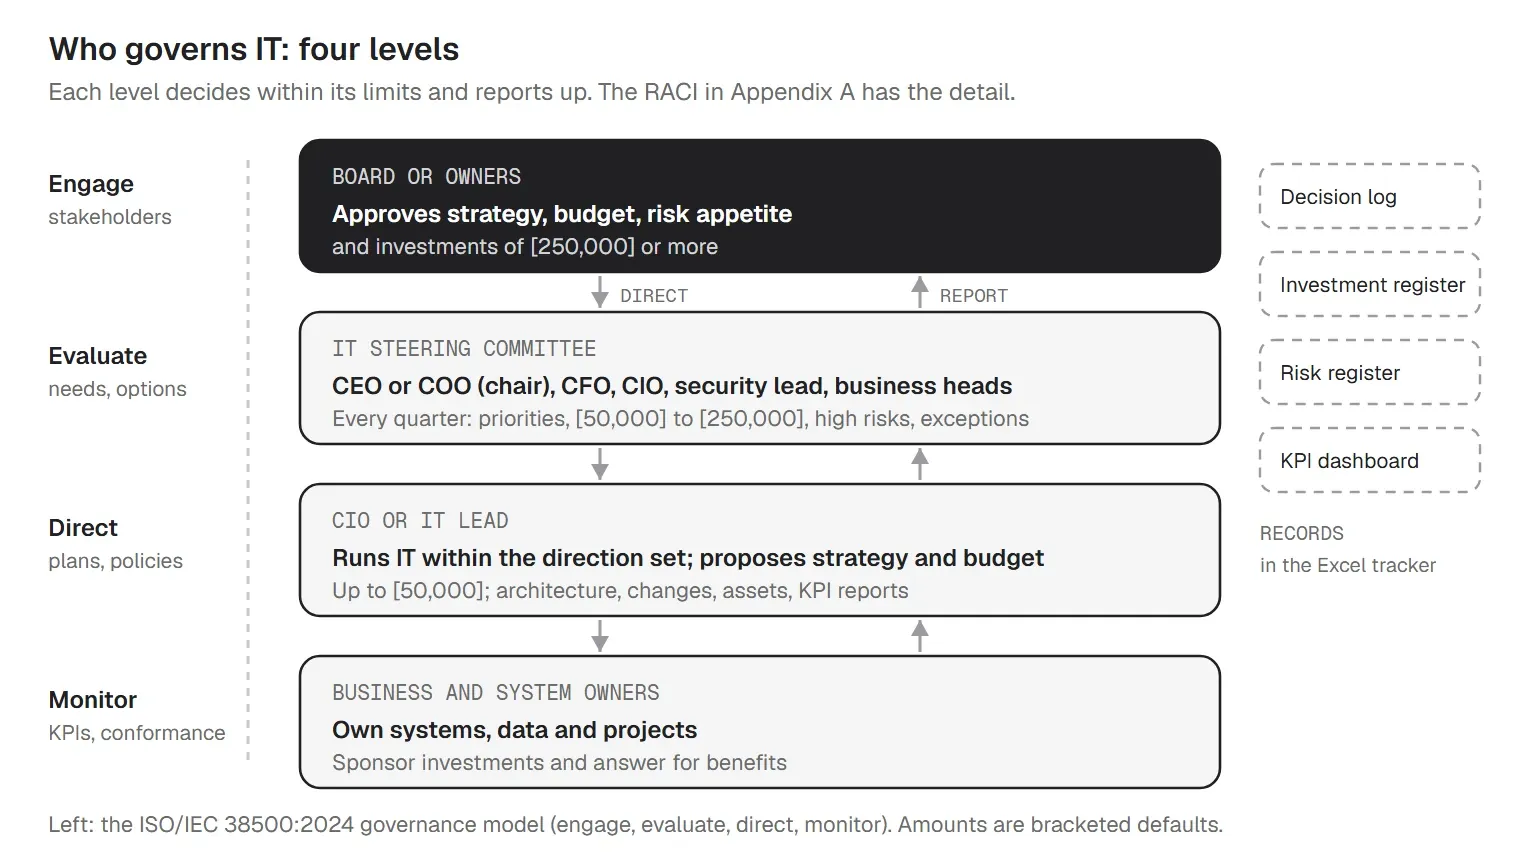
A RACI matrix says who is responsible (R), accountable (A), consulted (C) and informed (I) for each activity. The one rule that matters: exactly one A per row. Here are nine of the 16 rows in Appendix A:
| Activity | Board or owners | IT steering committee | CIO or IT lead | Security lead | Finance | Business and system owners |
|---|---|---|---|---|---|---|
| Approve the IT governance policy | A | R | C | C | I | I |
| Set IT strategy and priorities | A | R | R | C | C | C |
| Approve the annual IT budget | A | R | C | I | R | C |
| Approve investments of [250,000] or more | A | R | C | C | C | C |
| Approve investments of [50,000] up to [250,000] | I | A | R | C | C | C |
| Set risk appetite | A | R | C | C | C | I |
| Accept a high risk | I | A | R | C | I | C |
| Approve architecture and technology standards | A | R | C | C | ||
| Approve the information security policy | I | A | C | R | C |
In a small company one person can hold several roles; the CEO may chair the committee and act for the board. Write the names down anyway. The tracker's RACI tab flags any row without exactly one A.
Decision rights are the part of the policy people use most. For each area, the template names who proposes, who decides and when a decision goes up a level:
| Area | Decides | Goes up a level when |
|---|---|---|
| IT strategy and priorities | Board | The committee recommends; the board approves |
| IT investment | Per the threshold table | Cost above the approver's limit, or a business case is missing |
| Architecture and standards | Steering committee | A project wants a technology outside the standards |
| Security risk acceptance | Per the risk rating | High risks go to the committee; critical risks to the board |
| Vendors and cloud services | CIO | Critical vendors go to the committee |
| Policies and standards | Per the policy hierarchy | Policies to the committee; standards to the CIO; procedures to the process owner |
| Changes | CIO (major); IT lead (standard) | Changes with high business impact go to the committee |
| Exceptions | CIO (standards, procedures); steering committee (policies) | It is an exception to a policy, or it raises a high risk |
For investments, the threshold is the total cost over three years: the purchase plus three years of running costs. That way a SaaS subscription is judged the same way as a purchase.
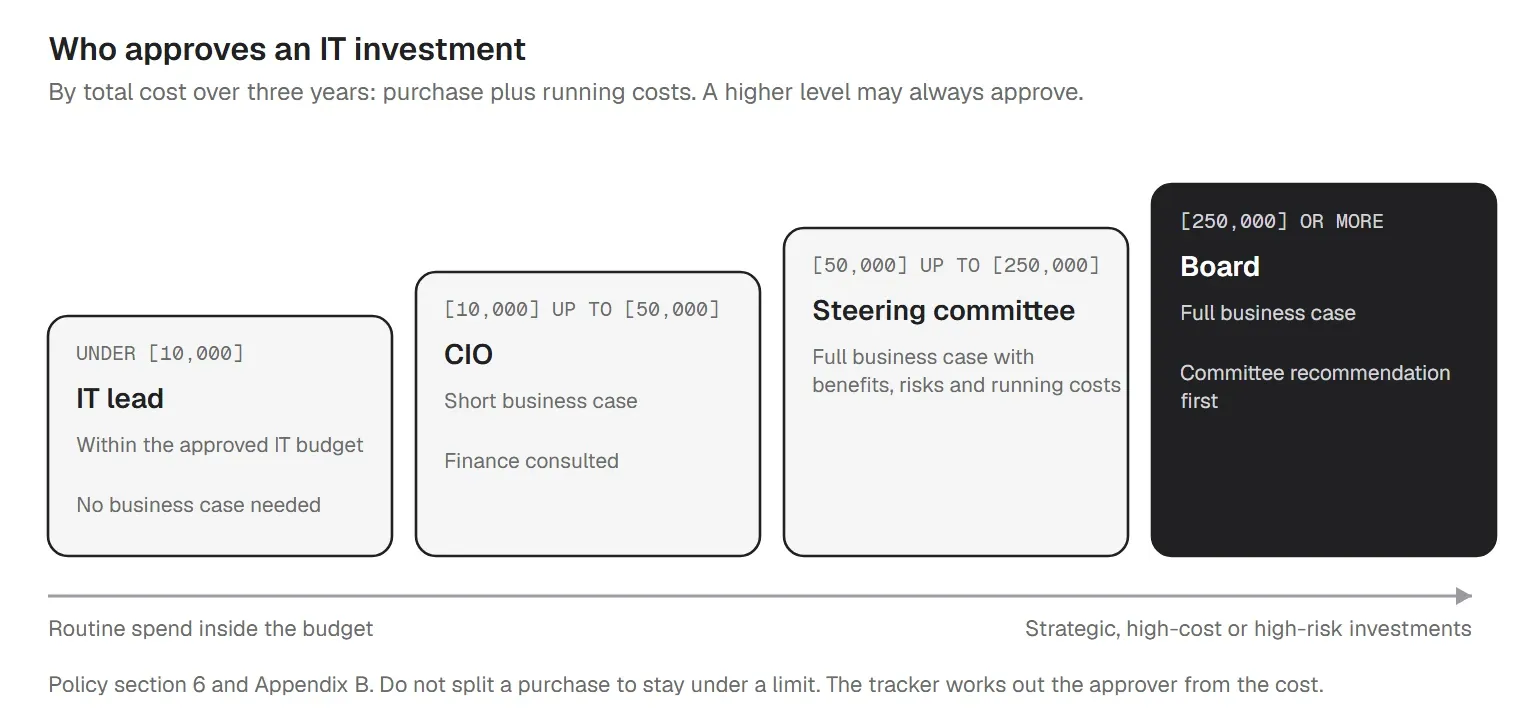
| Total cost (3 years) | Approved by | What is needed |
|---|---|---|
| Under [10,000] | IT lead | Within the approved IT budget; no business case needed |
| [10,000] up to [50,000] | CIO | Short business case; finance consulted |
| [50,000] up to [250,000] | Steering committee | Full business case with benefits, risks and running costs |
| [250,000] or more | Board | Full business case; committee recommendation first |
The amounts are placeholders; set them with your CFO so they match your finance approval limits. Two rules go with them: nobody splits a purchase to stay under a limit, and a project more than [10%] over budget or [two months] late goes back to whoever approved it. Our IT budget template helps with the numbers behind the business case.
Section 8 rates each IT risk by likelihood and impact from 1 to 5. The score sets who may accept the risk instead of treating it: low (1 to 4) the IT lead, medium (5 to 9) the CIO, high (10 to 16) the steering committee, and critical (20 to 25) the board. You write your own risk appetite statement in the brackets, for example that you don't accept high risks to customer data or payments without board approval. Our guide to IT risk management covers the risk process in more depth.
Sections 9 to 12 connect governance to the controls underneath it: the security lead owns the information security policy and reports to the committee; IT keeps an inventory of hardware, devices and installed software with an owner for each; new vendors and SaaS are approved before purchase; and changes follow a change process with the CIO approving major ones. Each of these has its own detailed policy. The IT security policy template, IT asset management policy template, vendor management policy template and IT change management template cover them.
The committee can't oversee what it doesn't measure. Appendix C has 16 starter KPIs across strategy and value, risk and security, operations, compliance and governance itself. Pick eight to twelve, give each a target, an amber limit, a data source and an owner, and look at the reds and ambers at every meeting.
| Area | KPI | Target | Data source |
|---|---|---|---|
| Strategy and value | Approved projects within 10% of budget | at least 85% | Investment register |
| Strategy and value | Approved projects on schedule | at least 80% | Investment register |
| Strategy and value | IT spend against the approved budget | at most 100% | Finance |
| Strategy and value | Projects with a benefits review done | at least 90% | Investment register |
| Risk and security | High and critical risks past their treatment date | at most 0 | Risk register |
| Risk and security | Laptops and phones with disk encryption on | at least 98% | Device management tool |
| Risk and security | Devices with a screen lock policy applied | at least 98% | Device management tool |
| Risk and security | Devices on a supported OS version | at least 95% | Device management tool |
| Risk and security | Known exploited vulnerabilities (CISA KEV) open past [14] days | at most 0 | Vulnerability findings |
| Operations | Availability of critical services | at least 99.5% | Monitoring tool |
| Operations | Major changes with an approved change record | at least 100% | Change log |
| Compliance | Policies past their review date | at most 0 | Policy register |
| Compliance | Exceptions past their expiry date | at most 0 | Exception register |
| Compliance | Audit findings closed by their due date | at least 90% | Audit tracker |
| Compliance | Critical vendors reviewed in the last 12 months | at least 100% | Vendor register |
| Governance | Steering committee meetings held as planned | at least 100% | Committee log |
Targets are starting points; set your own. Pull device measures, such as encryption, screen lock and OS versions, from your device management tool's reports rather than counting by hand.
An IT governance framework is a published reference for how to structure governance. You don't have to adopt one in full; a policy can borrow the parts it needs. The main options:
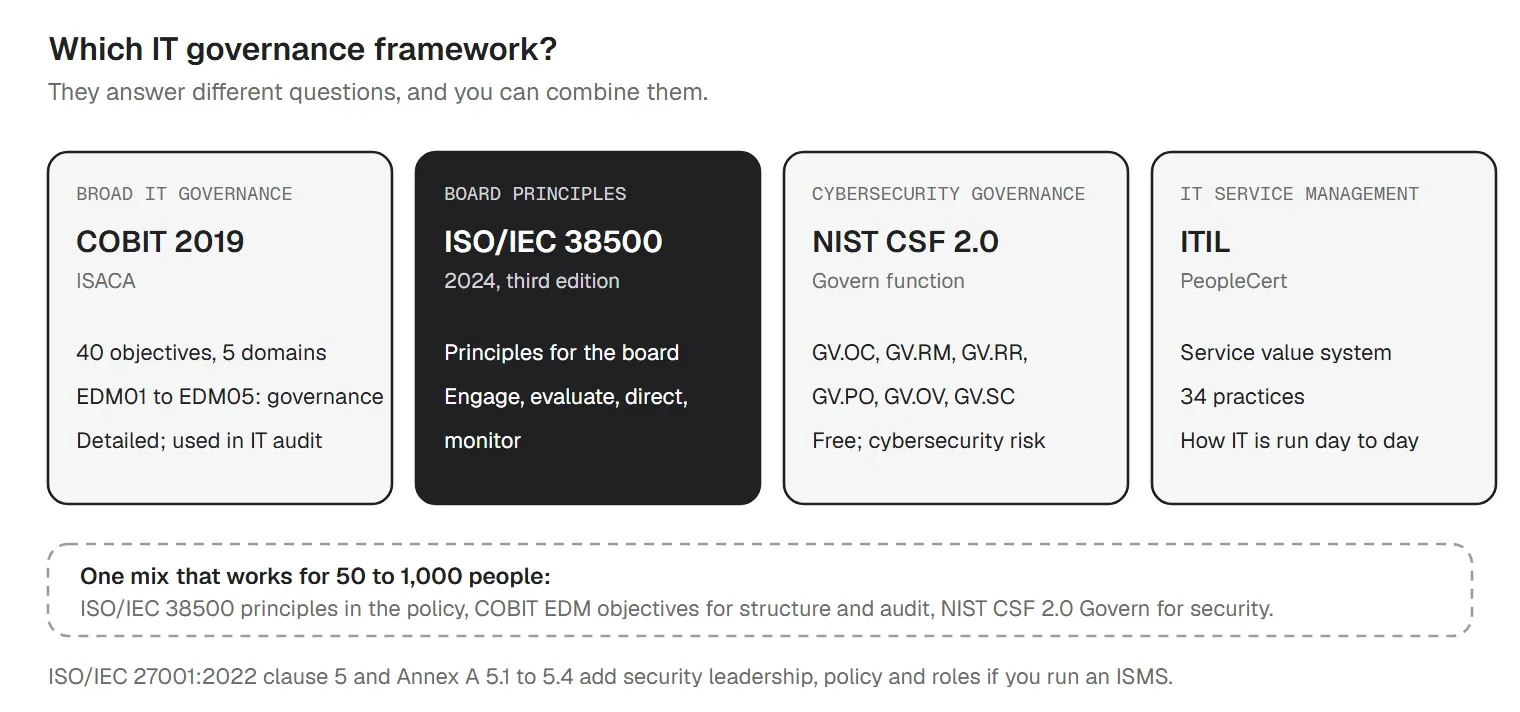
| Framework | Publisher | Use it for |
|---|---|---|
| COBIT 2019 | ISACA | A detailed reference for IT governance and IT audit; a good fit when your auditors already work with it. |
| ISO/IEC 38500:2024 | ISO and IEC | A short, board-level statement of how IT is governed; a good base for the policy's principles. |
| NIST CSF 2.0 | NIST | Governance of cybersecurity risk in particular; free to use. |
| ITIL | PeopleCert (AXELOS) | Running IT services well (management), not governance by itself. Pair it with COBIT or ISO/IEC 38500. |
| ISO/IEC 27001:2022 | ISO and IEC | Security governance, when customers ask about ISO/IEC 27001 or you plan an audit against it. |
Which framework should you choose? For most companies of 50 to 1,000 people, a mix works: ISO/IEC 38500 for the principles in section 1, the COBIT EDM objectives as a checklist for structure and audit, and NIST CSF 2.0 Govern for security risk. Add ISO/IEC 27001 clause 5 if you run an ISMS, and ITIL practices for IT operations. Choose COBIT in more depth if your auditors or lenders already use it.
Here is the whole framework on one page, the way the PDF shows it: the policy on top, three bodies with their own rhythm, five registers, and the data that feeds them.
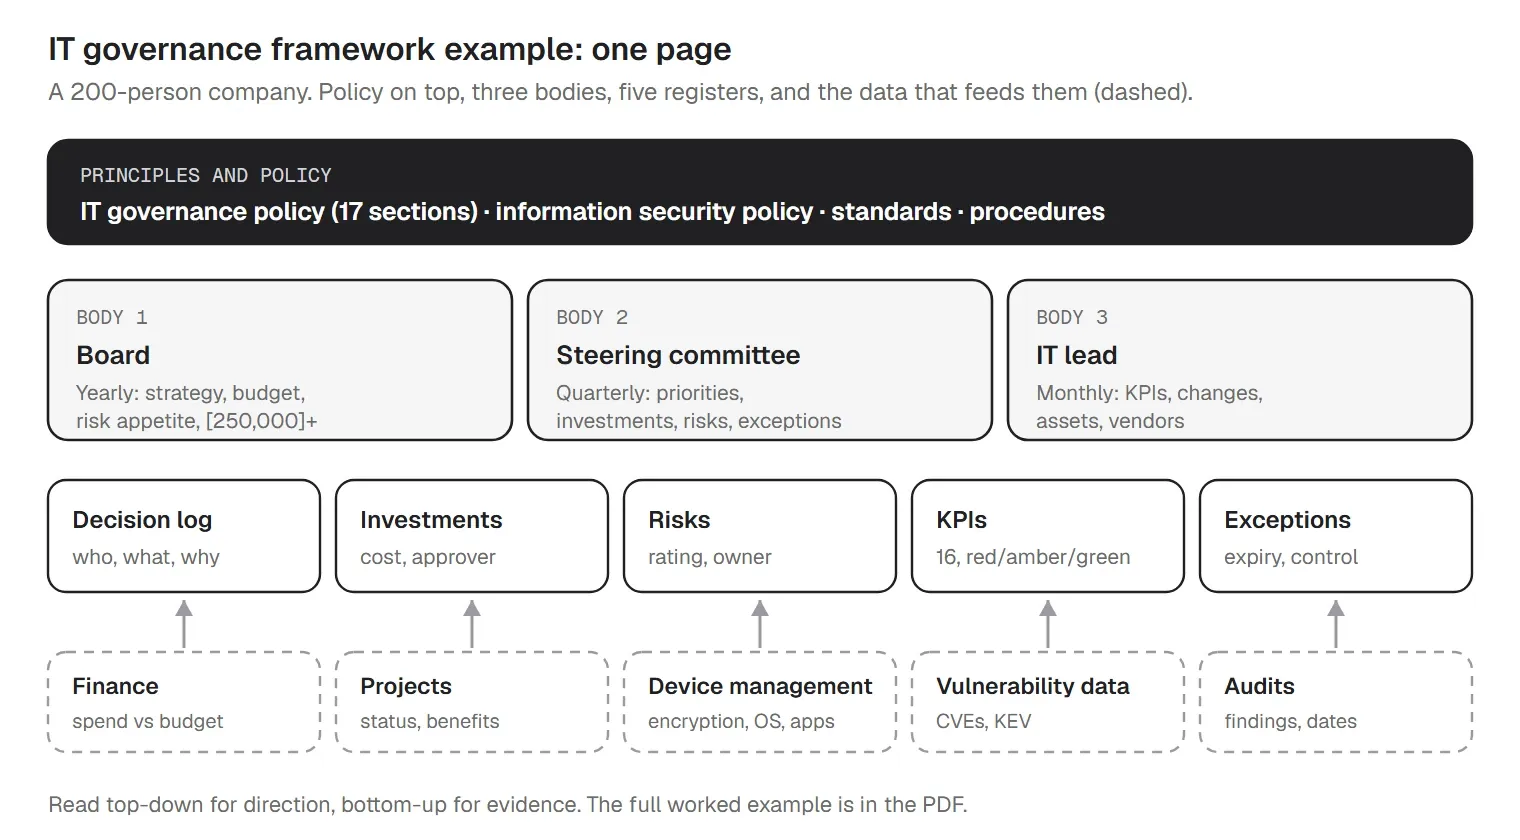
The company in the worked example is a 200-person software and services company with offices in two countries, a CEO, a CFO, an IT lead with a team of four and a part-time security lead. The board of five approves the IT strategy, the budget and the risk appetite once a year. The COO chairs a steering committee with the CFO, the IT lead, the security lead and the heads of engineering and customer success, with a 90-minute meeting every quarter. The IT lead acts as CIO and approves spend up to [50,000]. Four decisions from its first two quarters:
| Decision | Decided by | What happened |
|---|---|---|
| A new CRM, 3-year cost 180,000 | Steering committee | Business case from the head of sales; security review of the vendor; approved with a benefits review after 12 months. |
| A laptop refresh of 60 devices, 90,000 | Steering committee | Inside the approved budget, but above the IT lead's limit, so it goes to the committee as a single decision, not three smaller orders. |
| A design team wants a new file-sharing SaaS | IT lead (non-critical vendor) | Allowed after the security lead confirms it holds no customer data; added to the inventory and vendor register. |
| No MFA on a legacy finance app until it is replaced | Steering committee (exception) | High risk; compensating control: access only from managed devices on the office network; expires in [6 months]. |
On the first KPI dashboard, disk encryption on laptops and phones came in at 97% against a 98% target (amber), and only 62% of approved projects were within 10% of budget (red). The budget KPI went on the agenda, and the CRM project's scope was cut back to its approved budget. These numbers are an illustration, not a benchmark.
Sample clauses from the template, each saying who does what:
IT governance is not a one-time project. The template is built so the policy keeps working after it is approved: a yearly review, a quarterly committee rhythm, and registers that show what was decided and why. The download has three files:
How to roll it out in 90 days:
Each section of the template maps by ID to COBIT 2019, ISO/IEC 38500:2024, NIST CSF 2.0 and ISO/IEC 27001:2022. The mapping is our judgement; check the current official text before you rely on it.
| Section | COBIT | 38500 | CSF 2.0 | 27001 |
|---|---|---|---|---|
| 1. Purpose and principles | EDM01 | Clauses 5, 6 | GV.PO | 5.1, 5.2; A.5.1 |
| 2. Scope | EDM01 | 7.1 | GV.OC | 4.3 |
| 3. Governance structure | EDM01 | 6.2, 7.2.7 | GV.RR | 5.3; A.5.2, A.5.4 |
| 4. Decision rights | EDM01 | 7.2.5 | GV.RR | 5.3; A.5.3 |
| 5. IT strategy alignment and planning | EDM02 | 5.4 | GV.OC | 5.1 |
| 6. Portfolio and investment approval | EDM02, EDM04 | 5.3 | GV.RR | Not mapped |
| 7. Policy hierarchy | EDM01 | 7.2.4 | GV.PO | 5.2; A.5.1 |
| 8. Risk management and risk appetite | EDM03 | 5.10 | GV.RM | 6.1 |
| 9. Information security governance | EDM03 | 5.10 | GV.RR, GV.PO | 5.1 to 5.3; A.5.1, A.5.2 |
| 10. Asset and device management | EDM04 | 7.2.3 | GV.OC | Not mapped |
| 11. Vendor and cloud service governance | EDM03 | 5.10 | GV.SC | Not mapped |
| 12. Change and architecture governance | EDM01 | 7.2.2 | GV.PO | Not mapped |
| 13. Performance measurement | EDM05 | 7.2.6 | GV.OV | 9.1 |
| 14. Compliance and audit | EDM05 | 5.5 | GV.OC, GV.OV | 9.2 |
| 15. Exceptions | EDM03 | 5.10 | GV.RM | 6.1.3 |
| 16. Review | EDM01 | 6.2.4 | GV.OV, GV.PO | 9.3; A.5.1 |
When an auditor, an investor or the board asks how IT is governed, expect to show the approved policy with its review date, the RACI and committee charter with names, committee minutes and board summaries, the decision log, investment approvals at the right level with business cases, the risk register with accepted risks signed off, the KPI history, the policy register, the exception register, and device reports for inventory, encryption and OS versions. For a broader review, see our IT audit checklist, ISO 27001 checklist and IT health check template.
trio.so does not do IT governance: decision rights, committees and oversight are people and process, and the templates in this download cover them. trio.so is device management, and it supplies the device data that governance decisions and KPIs need.
Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026. Framework names and IDs identify their publishers' documents; descriptions are our own summaries. trio.so is not affiliated with or endorsed by ISACA, ISO, IEC, NIST or PeopleCert. COBIT is a trademark of ISACA; ITIL is a trademark of PeopleCert. Bracketed defaults, thresholds and targets are our suggestion, not a framework requirement. Size them to your company, and check your regulators', auditors' and investors' expectations before you adopt the policy.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Free Wi-Fi policy template in Word and PDF, with an Excel tracker: 17 sections on SSIDs, WPA3, guest terms of use, BYOD and rogue AP checks.
Free antivirus and anti-malware policy template in Word and PDF, with a baseline checklist, a filled-in example and an Excel endpoint coverage tracker.
A free compliance checklist template for IT teams: ten areas with owners, status and evidence, plus an Excel workbook, framework crosswalk and Word guide.
Free firewall configuration policy (Word, PDF) and an Excel rule register that flags any-any, unowned, expired and unused rules. Plus how to plan rules.
A free database security policy template, with the key components of a strong policy and best practices for protecting stored data.
Free IT asset disposal policy template with a disposal form, checklist and Excel log. NIST SP 800-88 Rev. 2 methods, ITAD vendor checks and process flow.
Using a proper transition plan template can help organizations manage projects and employees better. Read on to learn more about transition plans.
Free IT incident report template in Word and PDF with an Excel incident log: severity levels, timeline, root cause, postmortem and a filled-in example.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients