



How-Tos
How to Add a Mac to Active Directory (and When to Skip Binding)
Can you join a Mac to Active Directory? Yes. Steps to bind with Directory Utility, common errors, and why many teams now use Entra ID and SSO instead.
What XProtect does on a Mac, whether it runs by itself, how to check its version and last update, and where it stops, with a fleet check for IT teams.

Content writer, trio.so
XProtect is the malware scanner built into every Mac. It runs by itself, with no app to open and no scan button, and Apple updates its signatures separately from macOS updates. It checks apps when they first launch, when they change and when its signatures update, and a companion tool, XProtect Remediator, looks for known infections in the background. On macOS 15 Sequoia and later you can check its version in Terminal with xprotect version. (If you were looking for Milestone XProtect, the video surveillance software, this article covers Apple's built-in tool instead.)
If you only need to confirm XProtect is current on your Mac, jump to "How to Check Your XProtect Version"; the rest is for admins who have to explain and prove it across a fleet.
XProtect is often described as one tool, but it has three parts: the XProtect signature scanner, XProtect Remediator, and a behavior-based engine. Each runs on its own schedule. In early 2025, Check Point researchers reported that the Banshee macOS stealer had copied XProtect's own string encryption to avoid detection by other antivirus tools for over two months, and macOS Sequoia changed where XProtect lives on disk and how it is updated. Both matter if you manage Macs.
This article covers how each component works, what changed in Sequoia, how to check the version, the Full Disk Access question, XProtect's limits for managed fleets, and how to keep its updates enforced.
xprotect command, which normally uses iCloud. The old bundle in /Library/Apple/System/Library/CoreServices/ is still updated by Software Update.If you already know the three components, skip ahead to How XProtect Works: Three Components, One Stack.
XProtect is Apple's built-in, always-on malware detection for macOS. It arrived in Mac OS X 10.6 Snow Leopard in 2009. There is no interface, no settings panel and no manual scan. It runs in the background, and you only see it if you look in Terminal or the logs. It is the Mac's built-in antivirus layer.
It sits in a wider macOS security stack with Gatekeeper, notarization, privacy permissions (TCC) and System Integrity Protection. A short way to remember the first three: Gatekeeper checks apps before they run, notarization means Apple scanned an app before it was distributed, and XProtect scans for known malware. XProtect Remediator adds ongoing clean-up in the background.
There are three components, each with a different job:
This is the core detection layer. It uses YARA rules, patterns that describe known malware by its file structure or content, to identify threats such as known malware families, adware, browser hijackers and trojans.
XProtect Remediator arrived in macOS 12.3 Monterey in 2022 and replaced the older Malware Removal Tool (MRT). It scans periodically in the background, with separate modules for specific malware families, and it only runs when the Mac is awake and not busy.
The newest layer. Apple's Platform Security Guide says XProtect "contains an advanced engine to detect unknown malware based on behavioral analysis," which goes beyond matching known signatures. Apple has published little technical detail about it, and researchers are still studying how it works.
XProtect is not one tool running one scan. It is three layers with different schedules and triggers. An admin who can explain what each layer does, and when, has a much better answer ready when an auditor asks how malware protection works on the fleet. Knowing the mechanics also makes troubleshooting faster: checking the version, the paths and the commands is what separates an answer from a guess.
The signature scanner uses YARA rules, a format widely used across the security industry. Per Apple, on macOS 10.15 and later XProtect checks for known malicious content when an app first launches, when an app has been changed in the file system, and when XProtect's signatures are updated.
XPR scans periodically, only when the Mac is awake and idle. Its modules each target specific malware families, such as Adload and Bundlore, under internal code names. Security researchers keep public lists that map those names to known malware, which helps when you investigate log entries.
Admins cannot schedule or trigger XPR scans. That makes current definitions the thing to control: the scans that do run should use the latest signatures.
On macOS 13 Ventura and later, XPR detections and remediations are available to security software through the Endpoint Security framework. Reading them takes a security tool that uses that framework.
This component looks at behavior instead of known signatures, which in principle lets it catch threats that signature scanning misses. Apple has documented little about how it works, so treat it as a useful extra layer, not something you can configure or report on.
macOS 15 Sequoia changed how XProtect is updated. Before Sequoia, XProtect data came through Software Update into the XProtect bundle at /Library/Apple/System/Library/CoreServices/XProtect.bundle. In Sequoia, the data XProtect actually uses lives in /private/var/protected/xprotect/, and that copy is updated through the new xprotect command, which normally downloads from iCloud. Software Update can still update the old bundle.
So an XProtect update installed with softwareupdate, for example by a management tool, lands in the old bundle. Howard Oakley of The Eclectic Light Company, who documents these changes closely, reports that running sudo xprotect update can copy a newer version from the old location to the new one, but that this behavior has varied between macOS versions. After an upgrade to Sequoia, the new location can take a while to fill.
Sequoia added three commands:
xprotect version: shows the installed XProtect version and its date. No admin rights needed.sudo xprotect check: shows the newest version available from iCloud. Needs an administrator account.sudo xprotect update: downloads and installs a newer version if one exists.If sudo xprotect check shows a newer version but xprotect version does not change after sudo xprotect update, try again later; Eclectic Light has reported that check sometimes returns an error.
XProtect runs by itself, so "running XProtect" in practice means checking that it is current. Three ways:
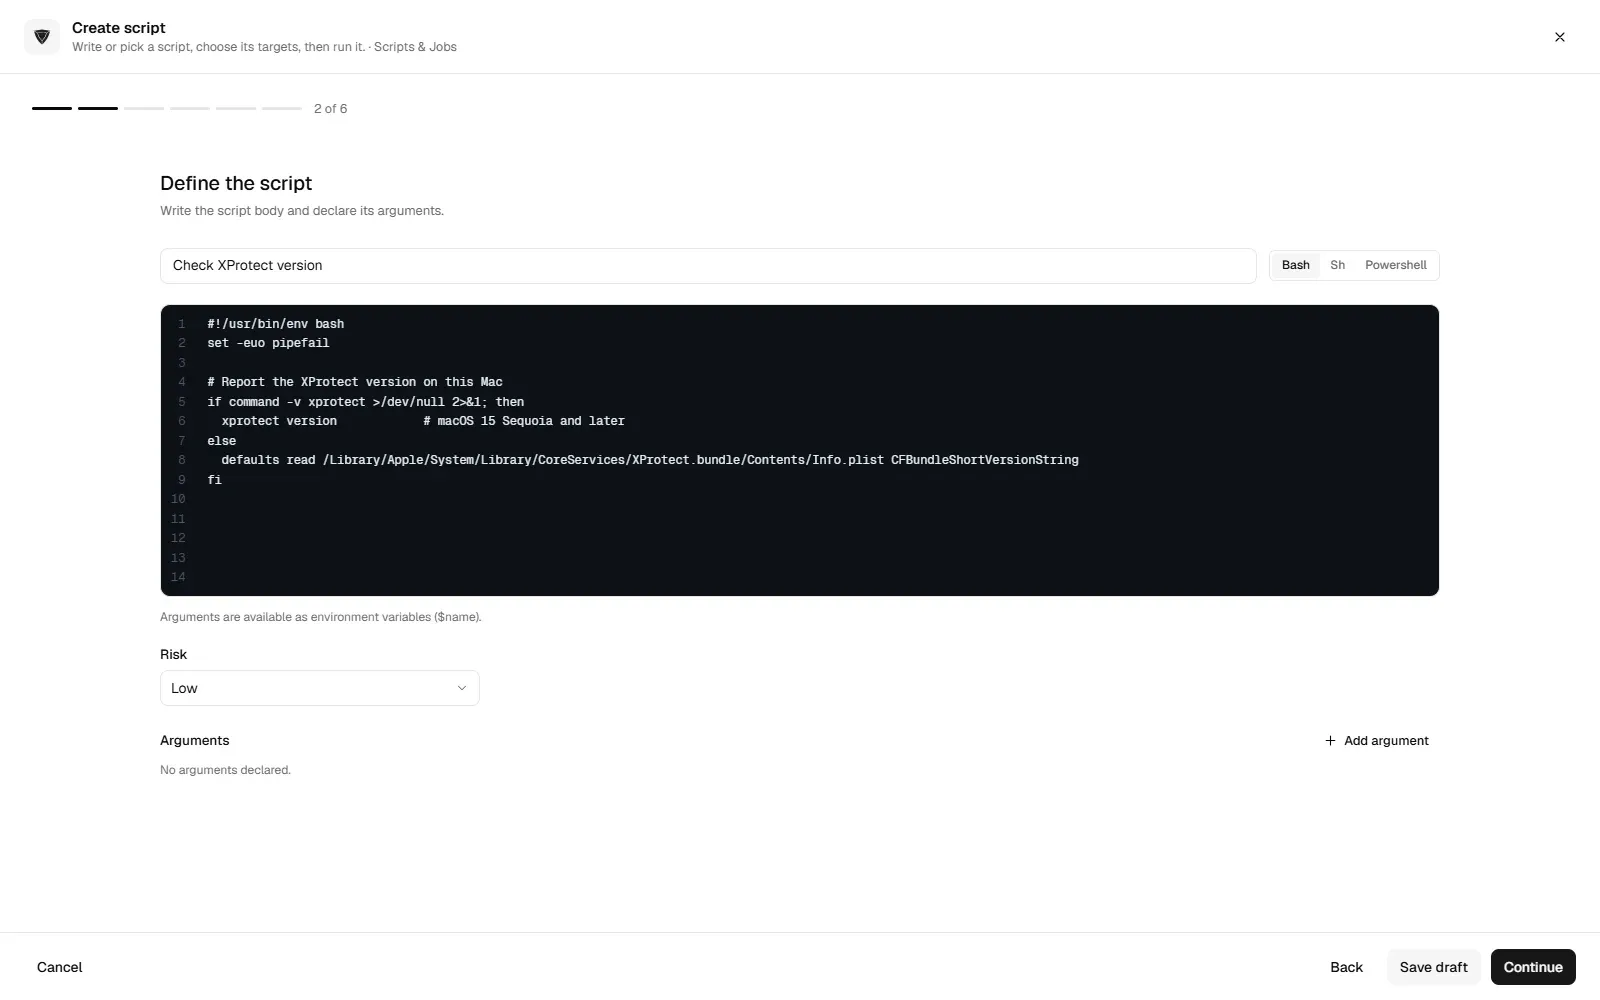
xprotect version.defaults read /Library/Apple/System/Library/CoreServices/XProtect.bundle/Contents/Info.plist CFBundleShortVersionString. To see when updates arrived, run system_profiler SPInstallHistoryDataType and look for the XProtect entries.Compare what you see with the latest version Apple has released. Eclectic Light and SOFA both list it.
It depends on the macOS version. On macOS 15 Sequoia and later, the data XProtect uses is in /private/var/protected/xprotect/. The older bundle, still present and still updated by Software Update, is /Library/Apple/System/Library/CoreServices/XProtect.bundle. On earlier versions, that bundle is the only location.
XProtect also appears in System Settings > Privacy & Security > Full Disk Access, but that is not a way to configure it. There is no app to open. The next section explains the Full Disk Access entry.
| Component | Introduced | How it runs | Scan trigger | Admin-visible logs? |
|---|---|---|---|---|
| XProtect (signature scanner) | Mac OS X 10.6 Snow Leopard (2009) | Always on | First launch, app change, signature update | No user log; a warning only when it blocks |
| XProtect Remediator (XPR) | macOS 12.3 Monterey (2022) | Background, periodically when idle | Automatic, cannot be triggered on demand | Through the Endpoint Security framework (macOS 13 and later) |
| Behavior-based engine | Described in Apple's Platform Security Guide (2024) | Background behavioral analysis | Continuous | Limited |
| Gatekeeper (for context) | OS X 10.8 Mountain Lion and 10.7.5 (2012) | On app launch | The user opens an app | A dialog when it blocks an app |
| Notarization (for context) | Required from macOS 10.15 Catalina | Apple scans apps before distribution | The developer submits an app | No admin log |
Open System Settings > Privacy & Security > Full Disk Access on a Mac and you may find XProtect listed with its switch off. This has worried people since macOS 12 Monterey and comes up often on Reddit and Apple's community forums.
The short answer: it is expected. XProtect is part of macOS and works at the system level. It does not depend on the Full Disk Access permission the way third-party apps do.
The switch does not control XProtect's signature checks or its Remediator scans. Both keep running whether it shows on or off. If an auditor flags the unchecked switch, explain that XProtect is a system component and point to Apple's Platform Security Guide.
XProtect is not an endpoint detection and response (EDR) tool. It is a strong, necessary layer of the macOS security foundation, and it was never designed to replace dedicated security tools. For anyone managing more than a handful of Macs, the better question is whether it is enough on its own, and for most managed fleets the answer is no. The gaps are specific.
Gap 1: No central detection reporting. XProtect has no admin alerts, no exportable scan log and no detection events your management tool can collect. You know it is running, but not what it found on which Mac. Security tools can receive XProtect Remediator events through the Endpoint Security framework on macOS 13 and later, but that needs a tool built for it.
Gap 2: Proof for audits. Auditors often ask for proof of malware protection. XProtect provides the protection but not the report. The DISA STIG for macOS 15 (V-268571, medium severity) requires automatic installation of XProtect Remediator and Gatekeeper updates, set with the com.apple.SoftwareUpdate configuration profile. XProtect does the security work; the profile and your records show the setting is enforced.
Gap 3: New and sophisticated threats. Banshee Stealer avoided detection by many antivirus tools for more than two months by copying XProtect's string encryption. Security researcher Patrick Wardle noted that it still needed the user to bypass Gatekeeper to run. The takeaway is not that XProtect failed, but that threats keep improving, so current definitions and extra layers matter.
If you rely on XProtect alone, one Mac with an old XProtect version, for example after the Sequoia change, is a silent gap. Nothing alerts you.
A simple way to decide:
XProtect updates automatically by default, but on a fleet "automatic" is not the same as guaranteed. You need to enforce it, check it and record it.
The DISA STIG for macOS 15 (V-268571) is a useful baseline even outside government: install XProtect Remediator and Gatekeeper updates automatically, set through the com.apple.SoftwareUpdate configuration profile (the ConfigDataInstall setting) and deployed to every enrolled Mac by your device management tool.
A Sequoia caveat: Software Update installs XProtect into the old bundle, while Sequoia uses the new location. After a profile is deployed, check a few Macs with xprotect version, especially ones recently upgraded to Sequoia. Set it, then check it.
Device management can defer software updates on supervised Macs by up to 90 days. That deferral is meant for macOS updates. Make sure your configuration does not also hold back security data such as XProtect, which should always install automatically.
If Software Update says XProtect is current but xprotect version shows an older number, the update probably went to the old bundle. Run sudo xprotect update, or wait for the iCloud delivery to update the new location.
Checking XProtect on one Mac takes one command. Checking it on fifty is a job for a script. trio.so runs scripts on enrolled Macs from the console, so the version check above can run on every Mac you select. A script on macOS runs when you start it. See Apple device management.
Related reading: anti-malware vs antivirus, macOS system extensions, kernel panic on Mac and should you use FileVault.
trio.so runs scripts on enrolled Macs from one console.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
xprotect version in Terminal. On earlier versions, read CFBundleShortVersionString from /Library/Apple/System/Library/CoreServices/XProtect.bundle/Contents/Info.plist, or use a checker such as SilentKnight.Related
The related industry news, interviews, technologies, and resources.
Can you join a Mac to Active Directory? Yes. Steps to bind with Directory Utility, common errors, and why many teams now use Entra ID and SSO instead.
Should you use FileVault disk encryption? A clear verdict for work Macs, the real performance cost, recovery options, and how IT turns it on for a fleet.
What network users and the Network Account Server setting do on a Mac, how to join a directory, and how to fix network users who cannot log in.
Change a Mac hostname in System Settings or Terminal with scutil: ComputerName, LocalHostName and HostName explained, plus renaming a fleet by script.
What a kernel extension policy does on macOS, how to allow a kext on Intel and Apple silicon Macs, system extensions vs kexts, and how MDM approves them.
Find your Mac administrator name, reset a forgotten admin password from Recovery or your Apple Account, and make a user an admin, with notes for IT.
Apple DEP is now Automated Device Enrollment in Apple Business. What it does, where to log in, what you need, and how zero-touch enrollment works.
Discover how to deploy and manage FileVault disk encryption on Mac using MDM. Learn how to enable, disable, and manage this built-in feature.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients