



Explained
IT Admins' Best Practices for Disaster Recovery Planning
Making a plan for disaster recovery can have many benefits for organizations around the world. Read on to find out how to do so.
What an application catalog is, what belongs in one, how it delivers apps to Windows, Mac, iPhone, iPad, Android and Linux, and how self-service works.

Content writer, trio.so
An application catalog, or app catalog, is the IT-managed list of approved software that an organization installs on its devices. Every app in it has been checked before it is made available, and it reaches devices in one of two ways: IT pushes it automatically to the devices that need it, or employees pick it themselves from a self-service portal that shows only approved apps. Each platform delivers catalog apps differently: installers and packaged apps on Windows, App Store apps and PKG or DMG installers on Macs, App Store apps licensed through Apple Business on iPhones and iPads, managed Google Play on Android, and packages from the distribution's repositories on Linux. A catalog works best with allow and block lists, so software outside it cannot simply be installed from the web.
If you are trying to stop unapproved software from spreading across company devices, the platform section and the "what belongs" checklist below are the practical parts; the rest explains how a catalog supports audits.
If you already run managed devices and just need the setup per platform, skip ahead to "How an Application Catalog Works Across Platforms".
An application catalog is a structured list of approved software that IT maintains, deploys and updates across enrolled devices. Each entry has been reviewed, and nothing reaches a device unless IT made it available. The names vary: "app catalog", "app catalogue", "enterprise app store" and "software catalog" are all used. In this post, the application catalog is the broad idea; an enterprise app store is one form of it, with a self-service interface where employees browse and install approved apps.
The same name is also used for specific products: Microsoft's SharePoint app catalog stores SharePoint add-ins, and the Intune Enterprise App Catalog is Microsoft's library of prepackaged Windows apps for Intune. Both are particular implementations of the general idea described here.
A public app store such as Apple's App Store or Google Play lets any developer publish and any user install. An application catalog is the opposite: IT chooses what is in it, and it is either pushed by IT or offered to users within that approved list. One more distinction for larger teams: a service catalog lists the IT services people can request, while a software catalog tracks which software is licensed and installed where. They can live in the same tool but answer different questions.
Without a catalog, people install whatever they need to get work done, and IT finds out later. Unapproved software is common: Productiv's 2024 SaaS research found that shadow IT made up about half of the app portfolio at midsize and large companies and more at smaller ones, and Zylo's 2024 SaaS Management Index estimated that enterprises waste about $18 million a year on unused SaaS licences.
The costs show up in three places. Security: unmanaged apps are not patched on your schedule and may handle data in ways nobody reviewed. Support: help desk staff troubleshoot software they have never seen. Audits: when a licence audit or a customer questionnaire arrives, there is no clean list of what is installed and who approved it, and building one becomes a project of its own.
People install their own tools mostly because the approved ones are hard to get. A catalog with a self-service option makes the approved path the easiest one.
An application catalog is a concept that each operating system implements differently. The MDM or endpoint management tool sits on top: it holds the catalog, knows which devices should get which apps, and uses each platform's own delivery mechanism. This is the core of mobile application management. To stop software from outside the catalog, pair it with application allowlisting and blocklisting.
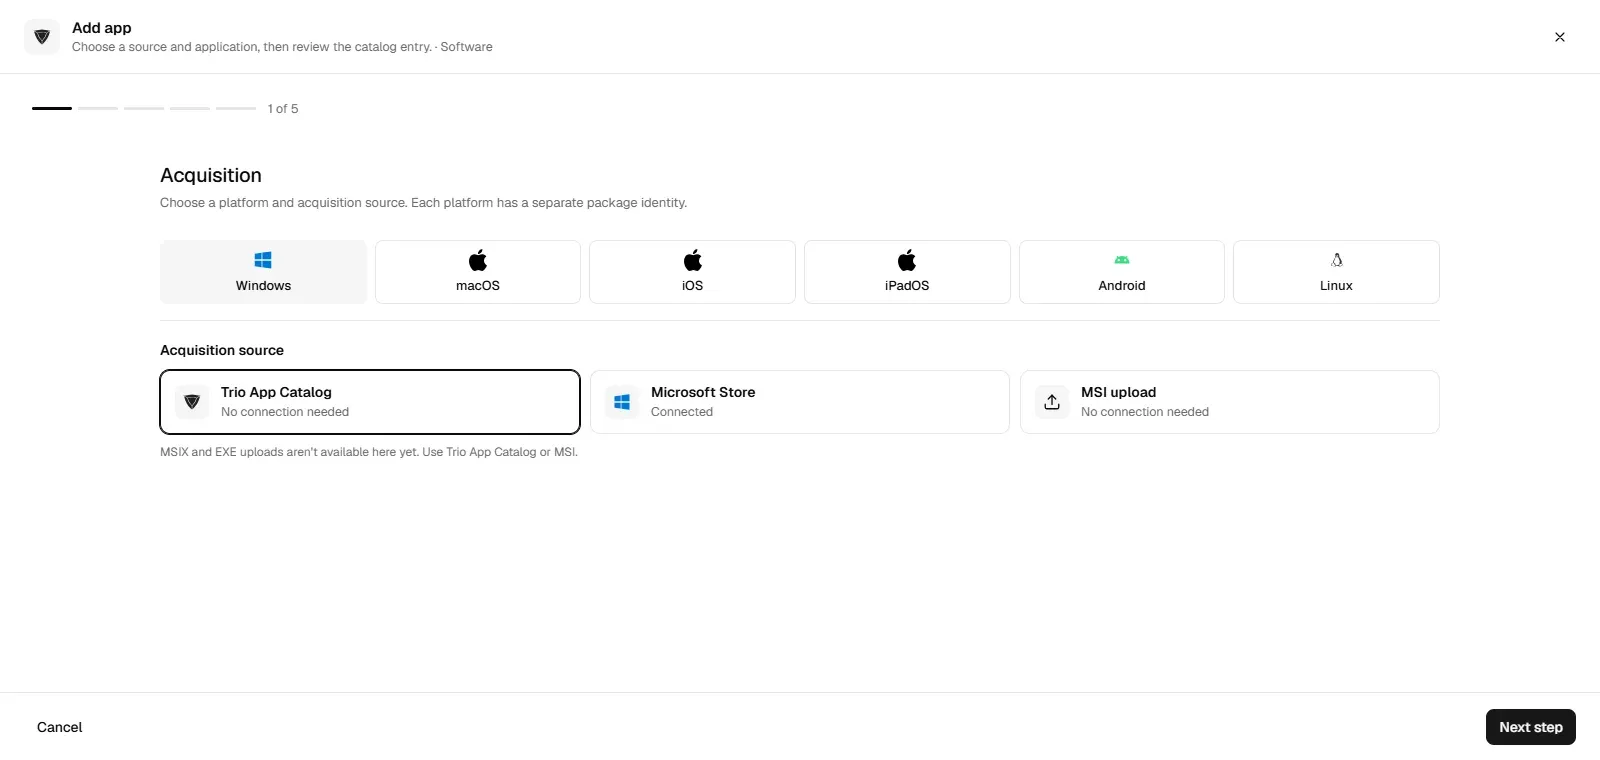
Windows apps come as MSI or MSIX packages, EXE installers, Microsoft Store apps or packages from the Windows Package Manager (winget). An MDM installs MSI packages silently, and many tools add a curated catalog of common apps that are already packaged and kept up to date. In Microsoft's own stack, the Intune Enterprise App Catalog provides prepackaged Win32 apps with the install and uninstall commands filled in. It is part of Intune's Enterprise App Management, which is licensed on top of standard Intune, so check whether your Microsoft plan includes it before you plan around it.
A macOS app catalog has two layers. Mac App Store apps are licensed in volume through Apps and Books in Apple Business (formerly Apple Business Manager) and installed by the MDM without users signing in with an Apple Account. Many business apps, such as browsers, chat and design tools, are not in the Mac App Store and come as PKG or DMG installers, which the MDM uploads and installs. Some Mac admins also use the open source Installomator script to download and install the latest versions of common non-store apps. Because the store and non-store layers are managed differently, check that your tool covers both.
iPhone and iPad apps come from the App Store, licensed through Apps and Books in Apple Business and assigned by the MDM. On supervised devices they install silently, and when a device leaves management its licences return to the pool for the next device. Custom apps built for one organization can be distributed privately through Apps and Books as well. Apps built in-house under Apple's Developer Enterprise Program are a separate route that uses the organization's own distribution certificate. See the Apple VPP token for the licence connection.
Android catalog delivery runs through managed Google Play, Google's app store for organizations. IT chooses apps in the MDM, which installs required apps silently and shows optional ones in the work Play Store, where users see only the apps IT made available. Private apps can be published to the organization without going through the public store. See managed Google Play.
Linux has no common app store for organizations. Apps are installed as packages from the distribution's repositories (apt on Debian and Ubuntu, dnf on Fedora and RHEL) or as Flatpak or Snap packages, and how much an MDM supports varies by vendor.
| Platform | How catalog apps are delivered | Self-service | Watch out for |
|---|---|---|---|
| Windows | MSI or MSIX packages, curated catalog apps, Microsoft Store, winget | Through the MDM's portal or Intune's Company Portal | EXE installers vary in how silent they are; Intune's Enterprise App Catalog needs an extra licence |
| macOS (App Store apps) | Apps and Books licences through Apple Business | Through the MDM's self-service portal | The content token expires every year |
| macOS (other apps) | PKG and DMG installers, or Installomator | Depends on the MDM | Each app needs its own update process |
| iOS and iPadOS | Apps and Books licences through Apple Business | Through the MDM's self-service portal | Silent installs need supervised devices |
| Android | Managed Google Play | The work Play Store shows approved apps | Devices need Google Play services |
| Linux | Distribution packages, Flatpak or Snap | Rarely | Support differs most between tools |
Configuring the tool is the easy part. Deciding what goes in the catalog is where most teams stall, and it works best with two tiers.
Tier 1, mandatory apps, installed on every device in a group at enrollment:
Tier 2, optional apps, available on request or through self-service:
Three rules decide whether an app belongs:
Not sure where to start? Begin with the apps IT already gets help desk tickets about. For each entry, record the app name, version, licence type, owner, renewal date and support contact; these are the fields you will want when a vendor audit arrives. When an app leaves the catalog, treat it as a change: tell users, offer a replacement and remove it from devices. Software upgrade best practices covers how to roll out new versions.
An application catalog creates audit evidence: a record of which software is approved, who approved it and where it is installed.
A catalog supports these requirements; on its own it does not make an organization compliant.
trio.so deploys apps from one console: catalog apps and MSI installers on Windows, App Store apps and PKG or DMG installers on Macs, App Store apps licensed through Apple Business on iPhones and iPads, managed Google Play apps on Android, and packages by name on Linux. Allow and block lists control what else can run on Windows, Mac, iPhone, iPad and Android devices, and users can install approved apps themselves from a self-service portal. See app management and how to deploy an application.
Related reading: deploy an application, managed Google Play, how to disable the App Store and private app store for Android.
trio.so deploys catalog apps, installers and store apps to Windows, Mac, iPhone, iPad, Android and Linux devices from one console.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Making a plan for disaster recovery can have many benefits for organizations around the world. Read on to find out how to do so.
A crucial aspect of MDM solutions is MDM migration. This article will explore MDM migration, its types, benefits, challenges, and best practices.
On-premise MDMs have specific advantages to them, but are they better than cloud –based MDM solution? Read on to find out.
Cloud Mobile Device Management solutions are changing how IT administrators manage organizational devices. Let’s discuss how they achieve that.
Delve into the intricacies of Mobile Content Management (MCM) and its relationship with mobile device management systems.
Data breaches happen through unauthorized access of individuals to sensitive and confidential data resulting in catastrophic consequences.
What remote wipe is, how to wipe a lost phone or laptop on Android, iPhone, Mac and Windows, full vs selective wipe, and what to set up first.
Vulnerability management is of utmost importance to protect your business from cybersecurity threats. Read this blog to learn more.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients