



Explained
7 Best Practices for Effective Machine Identity Management
Looking to simplify machine identity management? This guide uncovers proven methods for credential rotation, monitoring, and unified policy enforcement.
Ten Microsoft Entra conditional access policy templates with what each does, the order to enable them in report-only mode, licensing, and a free download.

Content writer, trio.so
Conditional Access policy templates are ready-made Microsoft Entra ID policies that you create in a few clicks from the Entra admin center (Entra ID > Conditional Access > Create new policy from templates), instead of building each rule from scratch. Most tenants start with the same set: require multifactor authentication for all users and for admins, block legacy authentication, require a compliant device, and block sign-ins from countries you do not operate in, then add risk-based policies if they have Entra ID P2. Every template is created in report-only mode, so you check the sign-in logs before turning it on, and you exclude at least two emergency access accounts first. The ten templates below come with what each does, the licence it needs and the order to enable them.
If you are setting up Conditional Access for the first time, or you are an MSP rolling the same baseline out to client tenants, start with the quick reference table and the report-only section; the free template download is just below.
If you have already run at least one Conditional Access policy in production, skip to the templates.
Conditional Access evaluates each sign-in against signals: who the user is and their roles, the device's platform and compliance state, the location or IP address, the app being opened, and, with Entra ID P2, the sign-in and user risk. If a policy's conditions match, its grant control applies. Grant controls include requiring MFA (or a specific authentication strength), requiring a compliant or Microsoft Entra hybrid joined device, requiring an app protection policy, requiring a password change, or blocking access.
Session controls are lighter: they set how often users must sign in again, or turn off persistent browser sessions, without blocking access. They suit personal and unmanaged devices.
Microsoft describes Conditional Access as its Zero Trust policy engine. Every sign-in passes through it, and if any applicable policy blocks, the sign-in fails, whatever other policies allow. When a sign-in is blocked and you cannot tell why, open the sign-in logs in Entra ID: the Conditional Access tab on each entry shows which policies applied and what each returned.
Download the template to plan your policies before you build them: users and exclusions, conditions, grant and session controls, and the date each one moves from report-only to on.
Microsoft's template list changes as it adds and renames policies, so check the names in your Entra admin center. The ten below are the ones most tenants need, in the order most teams deploy them. Some challenge the user (MFA), some require a condition (a compliant device, a trusted location), and some simply block.
The first policy for most organizations: every user must complete multifactor authentication to reach cloud apps. Microsoft reports that MFA blocks the large majority of automated account compromise attacks.
Microsoft now enforces MFA for its admin portals on its own, but this policy is still needed for everything else. If users are blocked instead of prompted, check that they have registered an authentication method; the "Securing security info registration" template protects that registration step.
The same control, scoped to privileged roles such as Global Administrator, Security Administrator and the other admin roles in the template.
Even if the all-users policy covers admins, a separate admin policy makes it harder to exclude an admin by accident.
Blocks sign-ins over older protocols that cannot do MFA, such as POP, IMAP, SMTP authentication, older Exchange ActiveSync clients and basic authentication.
Before you enforce it, run it in report-only mode and filter the sign-in logs by client app to find printers, scanners, service accounts and old mail clients that still use these protocols. If something stops working afterwards, its sign-in entries show the client app it used.
Allows access only from devices that are marked compliant by an MDM connected to Microsoft Entra ID, or that are Microsoft Entra hybrid joined, depending on the template you choose.
Plan for the effect: unmanaged personal devices lose access to the targeted apps until they are enrolled, so decide your BYOD approach first. The "Require compliant or Microsoft Entra hybrid joined device or multifactor authentication" template is a softer starting point.
Blocks sign-ins from countries where you have no reason to expect them.
Decide how to treat IP addresses that cannot be mapped to a country. Location is checked when the user signs in; it is a sign-in filter, not a firewall, and it does not stop anyone reaching the sign-in page.
Uses your office IP ranges as a trusted named location, in one of two ways: skip some prompts on the trusted network, or allow access only from it.
If your network uses IPv6 to reach the internet, add the IPv6 ranges too, or users in the office will still be treated as outside.
Limits mobile access to apps that have an Intune app protection policy, which suits personal phones that are not enrolled.
Microsoft retired the older "Require approved client app" grant in June 2026 (Microsoft 365 message center, MC1220751). Policies that use that grant are now read-only, so check older policies and move them to "Require app protection policy". Not every app that worked with the old grant supports app protection policies, so check the apps you need.
Uses Microsoft Entra ID Protection's real-time risk detection, such as anonymous IP addresses or unfamiliar sign-in properties, and challenges risky sign-ins.
Responds to signs that an account itself is compromised, such as leaked credentials, by requiring a secure password change.
Microsoft recommends configuring both risk policies in Conditional Access rather than in the older Identity Protection policy pages.
Shortens how long sessions last on devices you do not manage.
Expect help desk calls from people who can no longer stay signed in on personal laptops, and tell them before you enforce it.
| Template | Use | Licence | Grant control | Exclude emergency accounts? |
|---|---|---|---|---|
| Require MFA for all users | Baseline for all cloud access | Entra ID P1 | Require MFA | Yes |
| Require MFA for admins | Protect privileged roles | Entra ID P1 | Require MFA | Yes |
| Block legacy authentication | Stop protocols that cannot do MFA | Entra ID P1 | Block | Yes |
| Require compliant device | Only managed, compliant devices | P1 plus a compliance-reporting MDM | Require compliant device | Yes |
| Block by country or region | Limit sign-ins to allowed countries | Entra ID P1 | Block | Yes |
| IP-based named location | Trust or require office networks | Entra ID P1 | Block or require MFA | Yes |
| Require app protection policy | Protected apps on personal phones | P1 plus Intune | Require app protection policy | Yes |
| Sign-in risk policy | Challenge risky sign-ins | Entra ID P2 | Require MFA | Yes |
| User risk policy | Reset compromised accounts | Entra ID P2 | Require password change | Yes |
| Session controls for unmanaged devices | Short sessions on personal devices | Entra ID P1 | Sign-in frequency, no persistent session | Yes |
MSPs usually apply the same baseline to every client tenant. Microsoft's partner tools support this: with granular delegated admin privileges (GDAP), the MSP gets limited admin roles in each client tenant, and Microsoft 365 Lighthouse lets partners apply baselines and review tenants from one place. Each template can also be exported as JSON from the admin center and imported into another tenant with the "Upload policy file" option. Whichever route you use, start every policy in report-only mode in each tenant, because each client's apps and accounts are different.
Treat this as a gate every policy passes through, not a one-time setup step.
Report-only mode evaluates every sign-in and records what the policy would have done, without enforcing it. Review the sign-in logs, filter on the Conditional Access tab, and look for users and service accounts that would be blocked. A few days of logs is a minimum for a small tenant; one to two weeks catches accounts that only sign in occasionally.
Emergency access (break-glass) accounts come first. Create at least two cloud-only accounts, exclude them from every Conditional Access policy, protect them with strong, phishing-resistant credentials kept securely, and alert on any sign-in from them. Microsoft's templates exclude only the person who creates the policy, so add the emergency accounts to each policy yourself.
Before you switch a policy on, ask: are the emergency accounts excluded, have I reviewed the report-only logs, and have I checked service accounts and shared mailboxes?
Conditional Access produces sign-in records that show access controls working, which auditors often ask for. The mapping below is a guide, not audit advice; your auditor decides what evidence satisfies each control.
Report-only logs are not evidence of enforcement, so make sure the policies are on before an audit period starts. For the access side of an audit, see the user access review template.
When a user is blocked after a change, find the failed sign-in in the logs and open its Conditional Access tab; it names the policy that failed. For the principles behind these policies, see the least privilege access model and policy enforcement points.
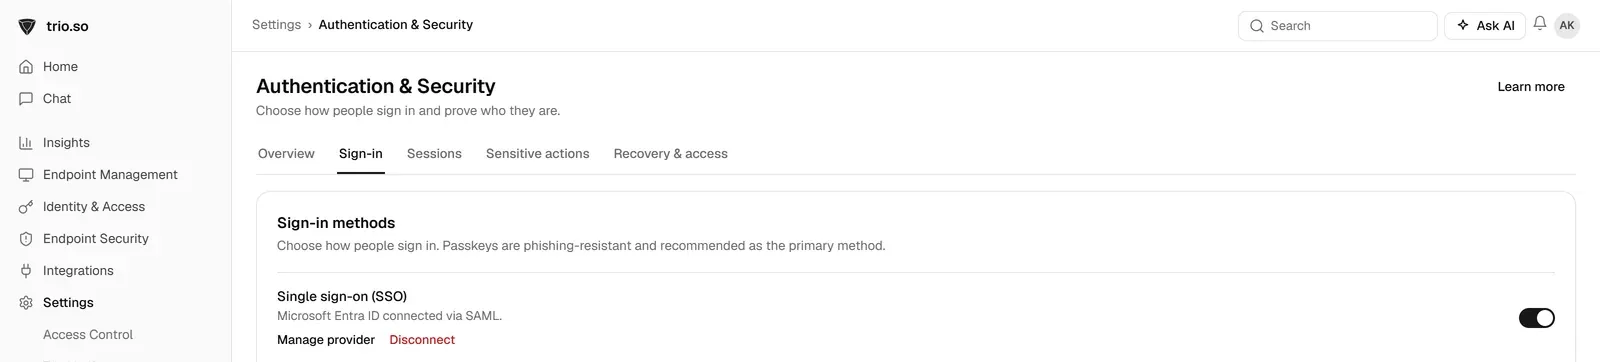
Conditional Access controls who can sign in to Microsoft 365 and under what conditions; the devices still need managing. trio.so syncs users and groups from Microsoft Entra ID, supports SCIM 2.0 user provisioning with Entra ID and SAML single sign-on, and shows each device's encryption status. For MSPs, trio.so manages several client companies from one console, with each client's devices, users and policies kept separate. See Windows device management.
Related reading: user access review template, multi-tenant Active Directory, Kipling method zero trust and MDM vs MAM.
trio.so syncs users and groups from Microsoft Entra ID, supports SCIM provisioning and SAML single sign-on, and manages every platform from one console.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Related
The related industry news, interviews, technologies, and resources.
Looking to simplify machine identity management? This guide uncovers proven methods for credential rotation, monitoring, and unified policy enforcement.
Seven best practices for cloud identity and access management, from least privilege and MFA to permission reviews and access logs.
Discover expert insights on Directory Management, covering groups, active directory management, and more for IT professionals.
SCIM vs JIT user provisioning: how each method works, where they differ, and how to choose or combine them.
Read this blog to explore attribute-based access control examples, its benefits, and challenges to see if it fits your access management needs.
Learn the 8 best practices for implementing centralized user management, including RBAC, compliance, and scalability planning.
Microsoft Entra ID (formerly Azure AD) vs Auth0: features, sign-in, use cases, and a detailed comparison to help you choose.

Wondering how to improve IT workflows? Automated user provisioning offers faster onboarding, error reduction, and better compliance.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients