



How-Tos
8 Ways IT Admins Can Block Ads on Windows 10 Managed Devices
Tired of intrusive ads on Windows 10? Discover effective methods for how to block ads on Windows 10 and enhance your browsing experience.
What each PowerShell execution policy does, how to check and set it with Set-ExecutionPolicy, and how to fix "running scripts is disabled".

Content writer, trio.so
A PowerShell execution policy is a Windows setting that decides whether PowerShell runs scripts, and under what conditions. There are six policy types (Restricted, AllSigned, RemoteSigned, Unrestricted, Bypass and Undefined) and five scopes, and Group Policy beats everything set locally. Check the current state with Get-ExecutionPolicy -List and change it with Set-ExecutionPolicy. If you see "running scripts is disabled on this system", the usual safe fix is Set-ExecutionPolicy RemoteSigned -Scope CurrentUser.
If that error is what brought you here, the fix is in the next section; if you set policy for a fleet, the scope, enforcement and compliance sections are for you.
Get-ExecutionPolicy -List, not just Get-ExecutionPolicy, to see which scope controls the effective policy on a machine.Set-ExecutionPolicy alone does not.The full error reads something like: File C:\scripts\setup.ps1 cannot be loaded because running scripts is disabled on this system. It means the effective execution policy on that PC is Restricted, which is the default for Windows client computers in Windows PowerShell 5.1. Restricted allows single commands but no script files.
Fix it for your own account, without admin rights and without opening the whole machine:
Set-ExecutionPolicy -ExecutionPolicy RemoteSigned -Scope CurrentUser
RemoteSigned runs scripts you wrote locally and blocks unsigned scripts downloaded from the internet. If the script you need was downloaded and you trust it, unblock that one file instead of loosening the policy:
Unblock-File -Path .\setup.ps1
To run one script once without changing any setting, start a session with the policy for that session only:
powershell.exe -ExecutionPolicy Bypass -File .\setup.ps1
Avoid Set-ExecutionPolicy Unrestricted as a permanent fix. If the change does not take, run Get-ExecutionPolicy -List: a value at MachinePolicy or UserPolicy means Group Policy sets it, and only a Group Policy change will move it.
PowerShell execution policies are preference settings. They tell PowerShell whether to run scripts, and under what conditions. They are not a firewall, not an antivirus layer and not an access control mechanism. Microsoft's documentation is direct on this point: the execution policy isn't a security boundary, and users can bypass it by typing the script contents at the command line.
Its real purpose is to prevent accidental script execution: a double-click on a .ps1 file, or an unintended run from an Explorer context menu. That is a legitimate operational safeguard. It is also why some practitioners call it security theater, and that criticism is worth taking seriously. Execution policy works alongside other controls, and the enforcement method and the layered stack are what make the environment defensible. That is why this article covers more than the six policy types.
Two PowerShell engines are in common use: Windows PowerShell 5.1, which ships with Windows 10, Windows 11 and Windows Server, and PowerShell 7, which is cross-platform and installed side by side. They keep separate execution policy settings, so setting the policy in one engine has no effect on the other. Microsoft's PowerShell 7 documentation lists RemoteSigned as its default on Windows.
If you have ever set RemoteSigned and still had a script blocked, or set a policy that seemed to apply but did not stop anything, the answer is almost always in the scope chain, or in the fact that execution policy was never meant to catch an attack in the first place. Both topics are covered below.
Setting the execution policy correctly means understanding two separate things: the type (what behavior you want) and the scope (where it applies and who it affects). A RemoteSigned policy at the CurrentUser scope behaves very differently from the same policy enforced at MachinePolicy through Group Policy. The combination of type and scope determines the actual outcome on the machine.
Scopes are evaluated from highest to lowest priority. The first scope with a defined (not Undefined) value wins.
$Env:PSExecutionPolicyPreference variable and disappears when the session ends. It is the right scope for temporary exceptions and automation jobs.Set-ExecutionPolicy alone is not enough for fleet enforcement: a standard user can change their own scope.Group Policy wins. When MachinePolicy or UserPolicy is set through Group Policy, a local Set-ExecutionPolicy command will not change the effective policy. Run Get-ExecutionPolicy -List to see every scope and its value, not just the effective policy.
If you rely on -Scope Process for build pipelines or automation jobs, note that Process scope does not carry over between sessions. Each new session starts with whatever the scope chain says, so the parent process has to set it every time.
If Set-ExecutionPolicy reports that the setting is overridden by a policy defined at a more specific scope, check whether MachinePolicy or UserPolicy is already set through Group Policy. That is the scope that wins, and the local command has no effect on it.
| Policy type | Scripts blocked? | Signature required? | Default on | Use case |
|---|---|---|---|---|
| Restricted | All scripts | N/A | Windows clients (Windows PowerShell 5.1) | Locked-down endpoints with no scripting need |
| AllSigned | Unsigned scripts | Yes, all scripts (local and remote) | None | Environments with a mature PKI; strictest scripting control |
| RemoteSigned | Unsigned scripts from the internet | Internet-origin scripts only | Windows Server; PowerShell 7 on Windows | Standard enterprise baseline for managed endpoints |
| Unrestricted | Nothing (prompts only) | No | PowerShell 7 on Linux and macOS (fixed there) | Non-Windows platforms; avoid on Windows production machines |
| Bypass | Nothing | No | None | Controlled automation and CI/CD pipelines, session scope only |
| Undefined | Inherits from the next scope | N/A | Every scope not configured | Intentional fallthrough when a higher scope sets the rule |
Setting the execution policy correctly starts with knowing what is already configured, before you change anything. These are the commands you will use in practice.
Get-ExecutionPolicy returns the effective (winning) policy only. It does not tell you which scope enforces it or what the other scopes are set to.
Get-ExecutionPolicy -List returns all five scopes and their values, highest priority first. This is the command to run before any troubleshooting:
Get-ExecutionPolicy -List

        Scope ExecutionPolicy
        ----- ---------------
MachinePolicy       Undefined
   UserPolicy       Undefined
      Process       Undefined
  CurrentUser    RemoteSigned
 LocalMachine      Restricted
Here the effective policy is RemoteSigned, because CurrentUser outranks LocalMachine. A scope that shows Undefined has no policy and falls through to the next one.
To check whether a specific script is tagged as an internet download, use:
Get-Item .\script.ps1 -Stream "Zone.Identifier"
This is checking for the Mark of the Web. If the stream shows ZoneId=3, the file comes from the internet zone and is blocked under RemoteSigned unless it is signed. To remove the tag:
Unblock-File -Path .\script.ps1
This removes the Zone.Identifier stream, so RemoteSigned treats the script as local. Note that some download methods, such as curl.exe and Invoke-WebRequest, may not add the tag at all.
Set RemoteSigned for all users on the machine (needs an elevated session):
Set-ExecutionPolicy -ExecutionPolicy RemoteSigned -Scope LocalMachine
This sets the LocalMachine scope. It affects all users, but a CurrentUser value or a Group Policy setting can override it.
Set Bypass for the current session only (no elevation needed):
Set-ExecutionPolicy -ExecutionPolicy Bypass -Scope Process
This applies only to the current session and does not persist. It is the recommended approach for a temporary exception without changing the machine's standing policy.
Set RemoteSigned for the current user only:
Set-ExecutionPolicy -ExecutionPolicy RemoteSigned -Scope CurrentUser
To remove a setting from a scope, set that scope to Undefined. Running these commands on 200 devices one at a time is not realistic, which is what the enforcement section below addresses.
Changing the execution policy on one machine is straightforward. Getting that change applied consistently across every endpoint in your fleet, and keeping it there, is the harder problem. There are two main paths, depending on how your environment is built.
For domain-joined machines, configure the execution policy in Group Policy at this path:
Computer Configuration > Administrative Templates > Windows Components > Windows PowerShell > Turn on Script Execution
Enabling the setting maps three options to policy types: Allow all scripts (Unrestricted), Allow local scripts and remote signed scripts (RemoteSigned) and Allow only signed scripts (AllSigned). Disabling it is the same as Restricted. The setting creates a MachinePolicy value, which overrides any local Set-ExecutionPolicy command, and users cannot change it. The same setting exists under User Configuration; the Computer Configuration one takes precedence.
For scripted auditing across the fleet, the Windows PowerShell 5.1 policy value is here:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows\PowerShell
  ExecutionPolicy (REG_SZ)
This Group Policy path applies to Windows PowerShell 5.1. PowerShell 7 ships its own administrative templates (PowerShellCoreExecutionPolicy.admx), and it stores local settings in powershell.config.json files instead of the registry. If both engines run on your machines, configure both.
For Microsoft Entra joined, Intune-managed devices without on-premises Group Policy, the execution policy is set through the Intune Settings Catalog under Windows PowerShell. The MDM setting applies the same Turn on Script Execution policy, so users cannot override it locally. That answers one of the most common questions from cloud-first admins: how to enforce the execution policy when there is no on-premises Group Policy.
One thing worth naming: getting a Group Policy change approved through change control, tested in a lab and staged to production usually takes longer than the technical change itself. Build that into your plan.
How should I enforce execution policy across my fleet?
Get-ExecutionPolicy -List on a sample of devices. If MachinePolicy shows a value, Group Policy is already in play. If everything is Undefined or only LocalMachine is set, you have no fleet enforcement yet.Execution policy on its own prevents accidents, not attacks. The documented bypass techniques take seconds for anyone who knows them, and MITRE ATT&CK tracks PowerShell abuse as its own technique, T1059.001. Execution policy will not stop it.
Common bypass approaches include passing -ExecutionPolicy Bypass to powershell.exe, encoding script content in Base64, running script text through Invoke-Expression, loading script content straight into memory, and using the PowerShell 2.0 engine, which predates many modern controls. Admins who set Unrestricted to unblock a problem script quickly create exactly the gap these techniques use: a persistent, machine-wide setting with no audit trail.
The PowerShell 2.0 downgrade matters most, because it gets around both execution policy and AMSI. Disabling PowerShell 2.0 is covered in the AMSI section below.
This is why Script Block Logging and AMSI belong on top of execution policy. The full stack is what makes the environment defensible, not any single setting.
AMSI passes PowerShell script content to the installed antimalware product at runtime, independent of execution policy. Even when the policy is Bypass, a compatible antivirus or EDR product can still detect and block malicious content before it runs. AMSI is available on Windows 10, Windows Server 2016 and later, and works when a compatible security product is installed.
One gap: the PowerShell 2.0 engine predates AMSI, so a downgrade to it avoids the scan. That is why the DISA STIG for Windows 10 requires PowerShell 2.0 to be disabled (WN10-00-000155).
If AMSI blocks a script you know is safe, the cause is usually pattern matching. The fix is an exclusion for that specific script in your antivirus or EDR product, not disabling AMSI.
Script Block Logging records the content of executed script blocks, whatever the execution policy. A script run with Bypass is still logged. Without it there is no forensic record of what ran.
Enable it in Group Policy: Computer Configuration > Administrative Templates > Windows Components > Windows PowerShell > Turn on PowerShell Script Block Logging. Events appear as Event ID 4104 in the Microsoft-Windows-PowerShell/Operational log.
Once you enable Script Block Logging, expect a clear increase in log volume on endpoints. Make sure your SIEM or log forwarding can handle the extra data before you enable it fleet-wide.
Constrained Language Mode restricts which .NET types and PowerShell language elements a session can use, which breaks many attack techniques even when execution policy is bypassed. Windows Defender Application Control (WDAC, now called App Control for Business) applies it automatically when script enforcement is on. For remoting, Just Enough Administration (JEA) adds another layer by restricting which cmdlets a user can run, whatever the execution policy.
AllSigned is the strictest scripting policy available and technically the most secure. The reason most mid-sized organizations do not use it is operational, not technical.
To run AllSigned across a fleet, you need a PKI (Active Directory Certificate Services internally, or a commercial CA), certificates with the Code Signing EKU (OID 1.3.6.1.5.5.7.3.3), and a consistent process for signing every script before deployment. The key commands:
Set-AuthenticodeSignature -FilePath .\script.ps1 -Certificate $cert   # signs a script
Get-AuthenticodeSignature .\script.ps1                                  # checks the signature
New-SelfSignedCertificate                                               # lab use only
That last point matters: a self-signed certificate is not trusted on other machines unless you distribute it, so a certificate that works where it was created fails everywhere else. This is not a PowerShell quirk; it is how certificate trust works.
The friction in AllSigned is usually not the PKI setup itself. It is getting every script author to sign every script before deployment, and keeping that discipline across teams over time.
Most mid-sized organizations settle on RemoteSigned plus Script Block Logging plus GPO or MDM enforcement as their practical baseline. AllSigned is the right answer for high-security environments with the PKI and the discipline to support it. Both are defensible choices, and the decision depends on your actual risk and operational capacity.
Execution policy is rarely a single checkbox in a compliance audit. It shows up as evidence under several controls across several frameworks. The common thread is that the policy needs to be documented, enforced through GPO or MDM, and auditable.
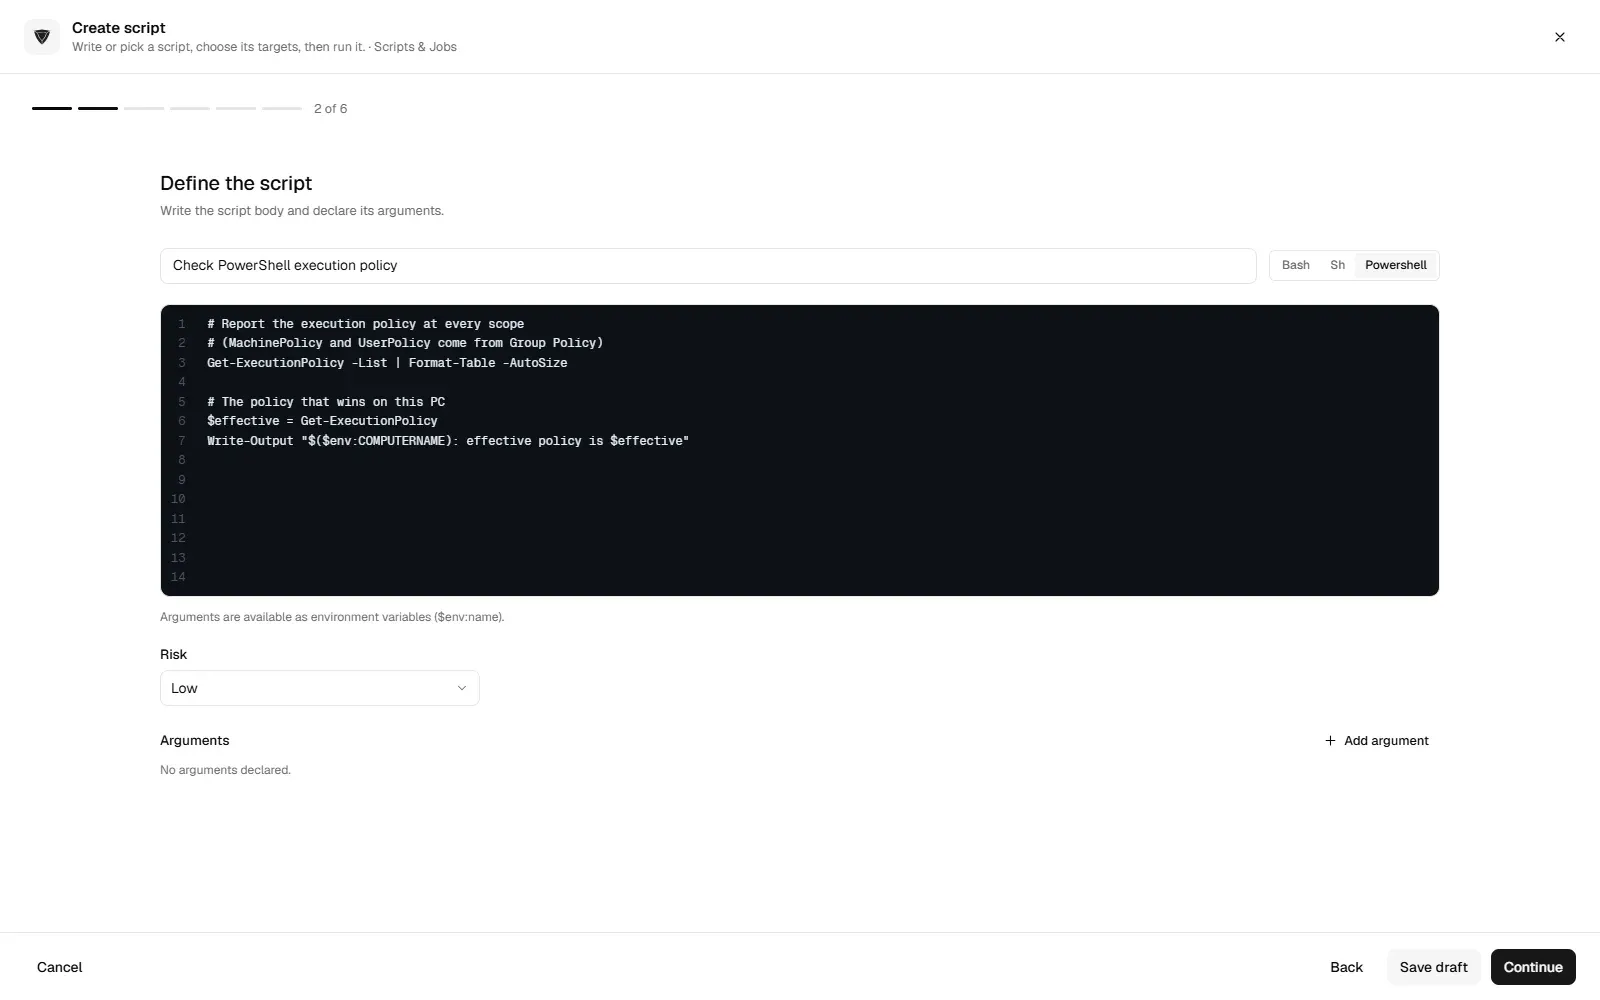
Configuring the execution policy on one machine takes 30 seconds; knowing what it is on 200 machines is the hard part. trio.so runs scripts on enrolled Windows PCs from the console, so you can write a Get-ExecutionPolicy -List check once and run it on the PCs that need it. See remote terminal and script runs.
Related reading: how to back up files from Command Prompt, how to remove a service with CMD, how to disable startup programs from Command Prompt and how to enable System Protection from Command Prompt.
trio.so runs PowerShell scripts on enrolled Windows PCs from one console.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Set-ExecutionPolicy RemoteSigned -Scope CurrentUser. It lets your own local scripts run without admin rights. For a single downloaded script you trust, run Unblock-File on it instead. If the setting does not change, Group Policy controls it.Get-ExecutionPolicy -List to see which scope controls the machine.Get-ExecutionPolicy -List in each engine to confirm both.Get-ExecutionPolicy -List on each machine through PowerShell remoting (Invoke-Command), read the policy registry values remotely, or use a management tool that runs a script on many devices and shows the results in one place.Related
The related industry news, interviews, technologies, and resources.
Tired of intrusive ads on Windows 10? Discover effective methods for how to block ads on Windows 10 and enhance your browsing experience.
Curious about patch management challenges? WSUS vs SCCM offers unique solutions for efficient updates and robust system security in your firm.
How to pause, delay or disable Windows Update on Windows 11 and 10 with Settings, Group Policy, the registry and services, and why IT should defer instead.
Intune vs SCCM compared: cloud vs on-premises, co-management, Configuration Manager's future, and which fits a small, mid-size or hybrid fleet.
How to delete a Windows service with sc delete or PowerShell, fix "marked for deletion", and what to check first. One PC or many.
Disable Control Panel and Settings with Group Policy: the exact policy, its registry value, how to exempt admins and how to allow only some items.
Disable a GPO safely: disable the link, disable user or computer settings, or unlink it, and why to leave the Default Domain Controllers Policy alone.
Turn on Remote Desktop for Windows machines with Group Policy: the exact policy path, the firewall rule, NLA, and how to check it worked.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients