



Explained
Best Security Practices for Android Zero-Touch Enrollment
Android zero-touch enrollment is a capability that many organizations take advantage of. Read on to learn about how to make it more secure.
Android Enterprise enrollment explained: work profile, fully managed and dedicated devices, QR code and zero-touch setup, and which method to use when.

Content writer, trio.so
Android Enterprise enrollment is the process of registering an Android phone or tablet with a device management (MDM) service under Google's Android Enterprise framework, so it receives your policies, apps and security settings from one console. It is a two-step choice. First you pick the management mode: a work profile on a personal phone, a fully managed company phone, a company-owned phone with a work profile, or a dedicated device locked to one task. Then you pick how the device gets there: zero-touch enrollment, a QR code, an enrollment token or link, or the older DPC identifier and NFC methods.
If you have a stack of Android devices to enroll and a list of methods with no clear signal about which one fits, this guide maps each mode to the methods that work for it, walks through zero-touch setup step by step and lists the errors you are most likely to hit.
If you already know the difference between a fully managed device and a work profile, skip ahead to the methods breakdown.
Most guides treat Android Enterprise enrollment as one thing. It is really two decisions made in order: first the management mode the device will run in (the enrollment type), then the way you get it there (the provisioning method). Mixing them up is the most common source of confusion in Android Enterprise rollouts. The enrollment profile is ready, but nobody decided cleanly which mode each group of devices needs.
The mode decision comes down to two tracks. On corporate-owned devices, IT controls the hardware. On personally owned devices, a separate work profile keeps work apps and data apart from the employee's personal side, and IT manages only the work side. Everything else follows from that split.
Android Enterprise replaced the legacy Device Administrator model, which Google deprecated in Android 9 because it was not built for modern management. If your devices still run under Device Administrator, the move to Android Enterprise is overdue rather than a future project.
There are four management modes inside Android Enterprise: fully managed, work profile, company-owned work profile (COPE) and dedicated device. The next section maps each one to the methods that work for it. In practice, the longest delay is often not technical: it is scheduling the factory reset with employees whose devices are already in use.
The enrollment types and the enrollment methods are not the same list. One describes what the device will be managed as; the other describes how you get it there. This section covers both together, because the mode you need decides which methods are even available.
The whole device is under IT control. There is no personal space and no apps beyond what IT approves. This is the right mode for company phones used only for work: field staff, shared roles and any case where the organization owns both the hardware and the use.
Fully managed enrollment makes your MDM app the device owner, which gives IT control over apps, network settings, security settings and restrictions. The device must be factory reset before enrollment; you cannot convert a phone that has already been set up.
Provisioning methods:
Key points:
If you enroll devices as fully managed and later find employees need personal apps, you have to factory reset and enroll them again as COPE. There is no in-place conversion between modes, so if personal use is even a possibility, plan for COPE from the start.
The Android work profile creates a separate space on the employee's own phone for work apps and data. IT manages only that space, not the phone. This is the right mode for BYOD programmes where employees use their own devices for work.
Provisioning methods:
Many MDM platforms moved personally owned work profile enrollment to Google's Android Management API with a web-based enrollment flow. If yours has, new BYOD enrollments use that web flow by default. For most teams it is simpler for employees, not a breaking change.
Key points:
Who owns the device you are enrolling?
The company owns the device, but the employee gets a personal side next to the managed work profile. IT manages the device and the work profile, while the personal side stays private. It is the middle path for organizations that want company control without handing staff a phone they can only use for work.
Minimum version: Android 11 or later for the current COPE model. Provisioning: factory-reset enrollment by QR code or zero-touch; a device already in use cannot be converted.
Key points:
The device is locked to one app or a small set of approved apps, often called kiosk mode. There is no personal use and no general navigation. Retail point of sale, warehouse scanners, digital signage and delivery tablets all belong here.
Provisioning: factory-reset enrollment by QR code, zero-touch or an enrollment token.
Zero-touch enrollment is the hands-off option for company-owned fleets. Your reseller registers the devices to your zero-touch account when you buy them. When an employee turns one on for the first time and connects to the internet, the device finds its assignment, downloads your MDM's app and enrolls itself before the home screen appears, with no IT hands on the device.
Requirements: a device running Android 9 or later (Android 8.0 on some compatible devices, Android 7.0 on Pixel phones), bought from a reseller that supports zero-touch, and a zero-touch customer account the reseller sets up for you. You cannot add devices bought outside the programme yourself, which catches admins who bought phones elsewhere.
The zero-touch portal also has audit logs and three access roles (Manager, Assigner and Viewer), so you can let someone assign devices without giving them full control of the account.
Zero-touch suits large fleets bought through a participating reseller. QR code enrollment is the right call for almost everyone else. It works for fully managed, COPE and dedicated devices without any reseller involvement.
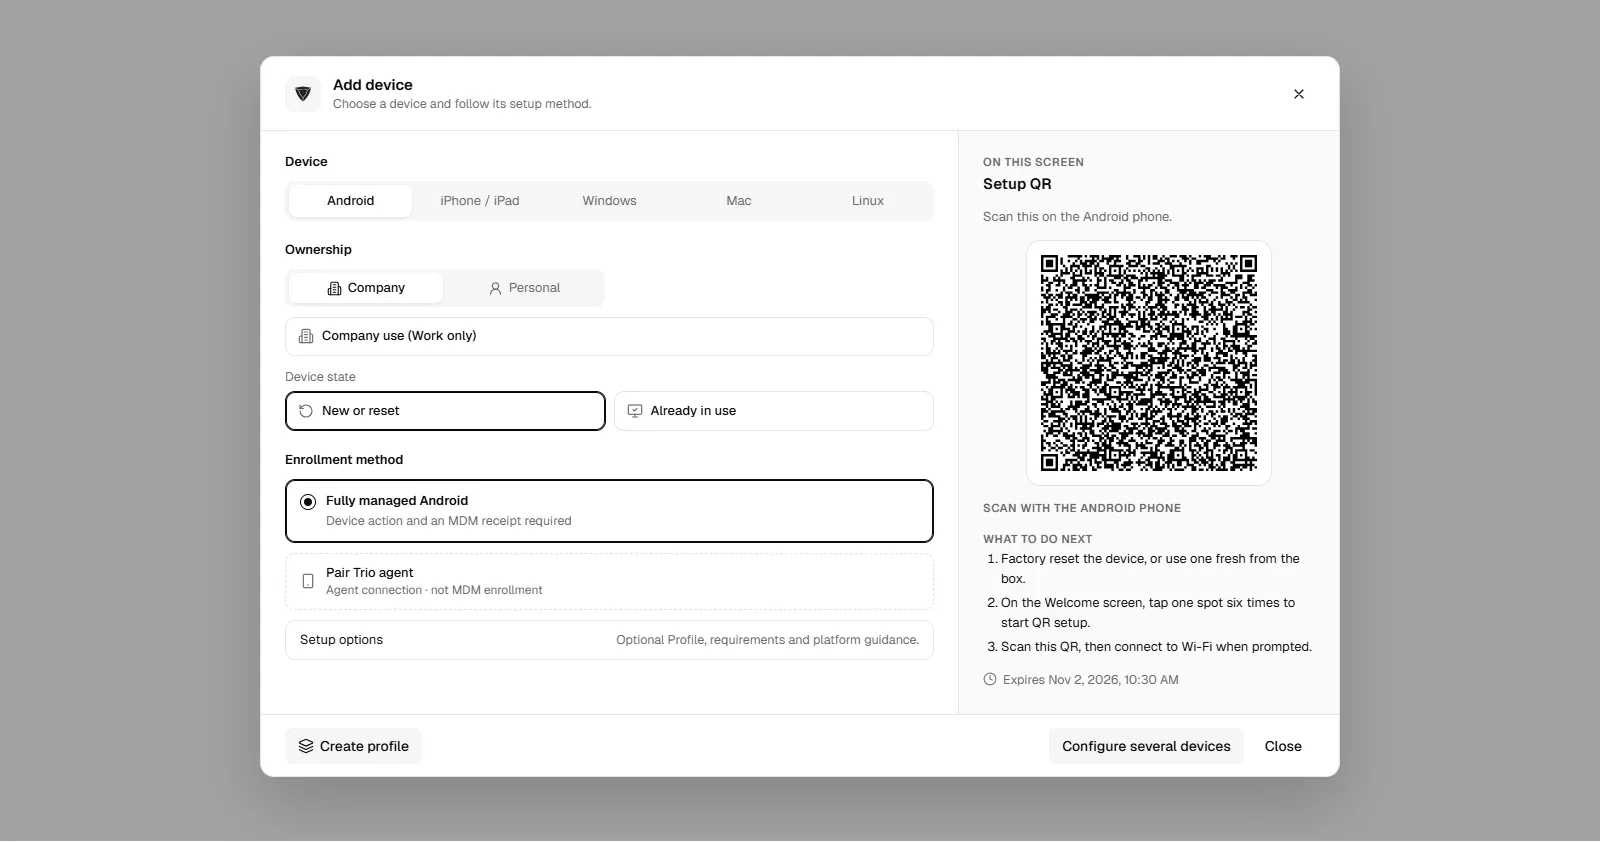
On the first setup screen, the admin taps the screen several times to open the QR scanner and scans a code generated by the MDM. The device downloads the management app and enrolls. It is simple and flexible.
Troubleshooting note: if the device fails to connect to Wi-Fi during QR enrollment, check the network details inside the QR payload and make sure the network is not behind a captive portal. Captive portals block the app download without a clear error.
These methods are less automated than zero-touch or QR codes, and most teams use them only when the others are not an option. With a DPC identifier, the admin types a code that starts with afw# in place of a Google account on the sign-in screen during setup, and the device downloads the vendor's management app. Each MDM vendor publishes its own identifier.
NFC provisioning works by bumping a configured provisioning device against the new device during setup, so the enrollment details transfer over. It needs an NFC-capable provisioning device kept on hand, and newer Android versions and MDM services increasingly favour QR codes instead.
| Method | Management modes | Ownership | Reseller needed? |
|---|---|---|---|
| Zero-touch enrollment | Fully managed, COPE, dedicated | Corporate-owned | Yes |
| QR code | Fully managed, COPE, dedicated, work profile | Corporate-owned and BYOD | No |
| Enrollment token or DPC identifier (afw#) | Fully managed, dedicated | Corporate-owned | No |
| NFC bump | Fully managed | Corporate-owned | No |
| Enrollment link | Work profile | Personally owned | No |
| Play Store app download | Work profile | Personally owned | No |
| Knox Mobile Enrollment (Samsung only) | Fully managed, COPE, dedicated | Corporate-owned | Yes (Samsung reseller) |
Zero-touch is the method most admins search for and the one with the most moving parts. These are the steps in the zero-touch portal:
If a device you bought does not appear in the portal, ask the reseller to register it. For the wider picture across Apple, Windows and Android, see zero-touch deployment and device provisioning.
Before you generate a single QR code or set up the zero-touch portal, your MDM has to be linked to Android Enterprise. That link creates your enterprise in Google's system and turns on Managed Google Play. Without it, app deployment and policy enforcement do not work, and no enrollment will finish.
There are two ways to link, depending on your Google setup. If your organization uses Google Workspace or Cloud Identity, a super admin of your managed Google domain approves the link. If you do not, you can sign up for a managed Google Play account with an ordinary Google account and link it to your MDM. Several MDM services can be linked to the same Google Workspace domain at once, each with its own enterprise ID.
Most "Organization enrollment failed" errors in Google Workspace environments come from an old MDM link that was never removed. If you see that error, check for a stale link from a previous platform and remove it before linking again.
A few recent changes affect how teams enroll and manage Android devices. Check Google's Android Enterprise help for the latest details before you change a live setup.
Zero-touch portal roles and audit logs. The zero-touch customer portal now has Manager, Assigner and Viewer roles instead of all-or-nothing admin access, and it keeps audit logs of portal changes. For any team where more than one person touches the portal, you can give a device provisioner Assigner access without handing over full control.
Web-based work profile enrollment. Many MDM platforms moved personally owned work profile enrollment to the Android Management API with a web-based flow. If yours has, the web flow is now the default for new BYOD enrollments. It is simpler for employees and needs less on the device.
Managed Google Play and security additions. Managed Google Play accepts Android App Bundles for private apps, so internal apps no longer have to be uploaded as APKs. Google has also brought Advanced Protection, its one-switch hardening for phishing, malware and scam calls, to managed devices.
Enrollment errors nearly always come from one of three causes: something left on the device from an earlier setup, a network block, or a Google services connection problem. Knowing which one you are dealing with cuts troubleshooting time.
trio.so enrolls Android devices through Android Enterprise as a work profile on personal phones, fully managed company phones or dedicated (kiosk) devices, using a QR code, an enrollment token or zero-touch enrollment, after you link Android Enterprise once. When a personal phone is unenrolled, its work profile is removed. Android devices sit in the same console as your Windows, macOS, Linux and iOS/iPadOS devices. See MDM enrollment.
It is the process of registering an Android device with an MDM under Google's Android Enterprise framework, in a chosen management mode, so the device receives policies, apps and security settings from a central console.
There are four management modes: work profile on a personal device, fully managed, company-owned work profile (COPE) and dedicated device. The provisioning methods (zero-touch, QR code, token, link) are how a device gets into one of those modes.
A zero-touch reseller registers the devices you buy to your zero-touch account. You assign them a configuration that points to your MDM, and each device enrolls itself the first time it is turned on and connected to the internet.
A work profile manages only a separate work space on the device, usually a personal phone, and leaves personal data private. Fully managed puts the whole device under IT control and is used on company-owned phones.
Only as a work profile. Fully managed, COPE and dedicated modes all need a factory-reset device, because the management app has to be set up during the first setup.
Related reading: Android work profile, Android QR code enrollment, Managed Google Play and zero-touch deployment.
trio.so supports work profile, fully managed and dedicated Android devices, with QR code, token or zero-touch enrollment.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Android zero-touch enrollment is a capability that many organizations take advantage of. Read on to learn about how to make it more secure.
Complete guide to pushing Android remote updates with MDM. Learn methods for app, system, and policy updates across managed devices.
Remove a work profile from Android or a Samsung phone in a few taps, what gets deleted, why removal can be blocked, and how IT removes it at offboarding.
How to give Android work devices a private app store: managed Google Play private apps and web apps, distribution, updates and access control.
Android device offboarding secures corporate data during employee exits through factory resets, account removal, and compliance documentation that prevents unauthorized access.
Android RMM software enables remote monitoring and management of Android devices across distributed workforces. Explore tools, features, and deployment strategies for IT teams.
Use Mobile Device Management to enforce location services on Android devices through Android Enterprise policies, preventing users from disabling GPS tracking on company-owned phones.
What Lost Mode means on Android: Google Find Hub's Secure device, Samsung's Lost mode, what happened to AndroidLost, and how IT locks lost company phones.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients