



Explained
HIPAA Technical Safeguards Explained for IT Teams
HIPAA technical safeguards are the 5 standards in 45 CFR 164.312. What each one requires, required vs addressable, and the device settings that meet it.
What is CIS compliance? There is no CIS certificate for companies. What it means for the CIS Controls and Benchmarks, and how to assess and show it.

Content writer, trio.so
CIS compliance usually means one of two things. Either your organization has put the CIS Controls in place up to a chosen Implementation Group, or your systems are configured to a CIS Benchmark at Level 1 or Level 2. Often it means both. There is no official CIS certification for organizations: CIS certifies vendor products against its Benchmarks, but it does not issue a certificate that says a company is CIS compliant.
You show CIS compliance with evidence instead, such as a self-assessment against the Safeguards, configuration scan reports and records from the tools that enforce your settings. This guide covers both meanings, how a CIS Controls assessment works, the state laws that reward a CIS-based program, and which parts software can take over.
In short
Not for organizations. CIS publishes the Controls and the Benchmarks as voluntary guidance, and its own mapping and compliance pages make no certification claims for companies (CIS). What CIS does run is aimed at products and service providers:
| Program | Who it is for | What it confirms |
|---|---|---|
| CIS Benchmarks certification | Software vendors | The product can accurately assess, configure or remediate against a specific Benchmark. Renewed every year, and new Benchmark versions must be supported within 90 days. |
| CIS Controls Accreditation (with CREST) | Consulting and assessment firms | The firm is accredited to deliver CIS Controls implementation, audit or assessment services. |
| CIS SecureSuite membership | Organizations and vendors | Access to CIS-CAT Pro, Build Kits and other Benchmark formats, plus commercial-use rights. It is a subscription, not a certificate. |
So a vendor that calls its scanner CIS certified is talking about the scanner (CIS product certification). A customer who asks whether you are CIS compliant wants to know what you have implemented and what you can show for it.
CIS publishes two different things, and "CIS compliance" can refer to either.
| CIS Controls compliance | CIS Benchmark compliance | |
|---|---|---|
| Question it answers | Are we running the security practices CIS prioritizes? | Are our systems configured the way CIS recommends? |
| Unit | Safeguard (153 in v8.1) | Recommendation in the Benchmark for one product version |
| Tiers | Implementation Groups IG1, IG2, IG3 | Profiles Level 1, Level 2 (STIG on some) |
| Typical evidence | Self-assessment scores, policies, records, tool reports | Scan reports, device settings reports, an exceptions register |
| CIS tool | CSAT (Controls Self Assessment Tool) | CIS-CAT Lite or Pro |
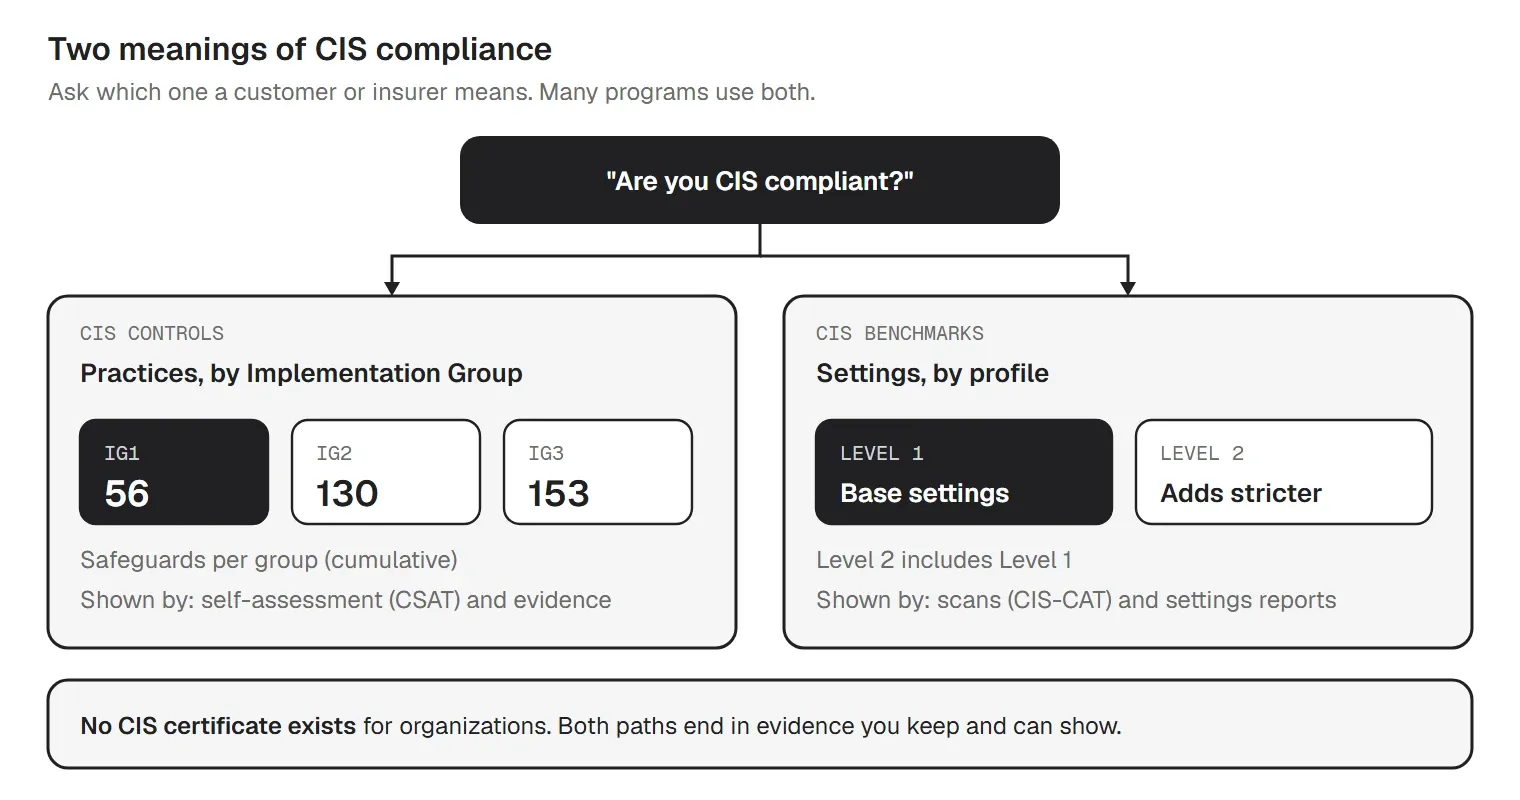
When a questionnaire asks about CIS, check which one it means and answer that. "CIS Level 1" is a Benchmark profile; "IG1" is a set of Controls Safeguards.
The current version is CIS Controls v8.1, released in June 2024, with a minor document revision (v8.1.2) in March 2025. It has 18 Controls and 153 Safeguards, and v8.1 added a Govern security function to line up with NIST CSF 2.0 (CIS Controls v8.1). Each Safeguard is tagged with the Implementation Groups it belongs to, and the groups are cumulative:
Controls 13, 16 and 18 (network monitoring, application software security and penetration testing) have no IG1 Safeguards. Several IG1 Safeguards live on laptops and phones: 1.1 keeps an asset inventory, 3.6 encrypts data on end-user devices, 4.3 locks idle sessions (after no more than 15 minutes on computers and 2 minutes on mobile devices), and 7.3 patches operating systems automatically, at least monthly. The CIS Controls guide lists all 18 Controls.
Benchmark compliance is narrower. It means a system matches a CIS Benchmark for its exact product version, at Level 1 or Level 2, with any deviations written down. Level 2 includes everything in Level 1. You measure it per device with a scan, so the result is a score per Benchmark rather than a yes or no for the company. Our guide to CIS Benchmarks covers the levels, the current device Benchmarks and how to apply one.
An assessment turns "we follow CIS" into something a customer, insurer or auditor can check. A workable sequence:
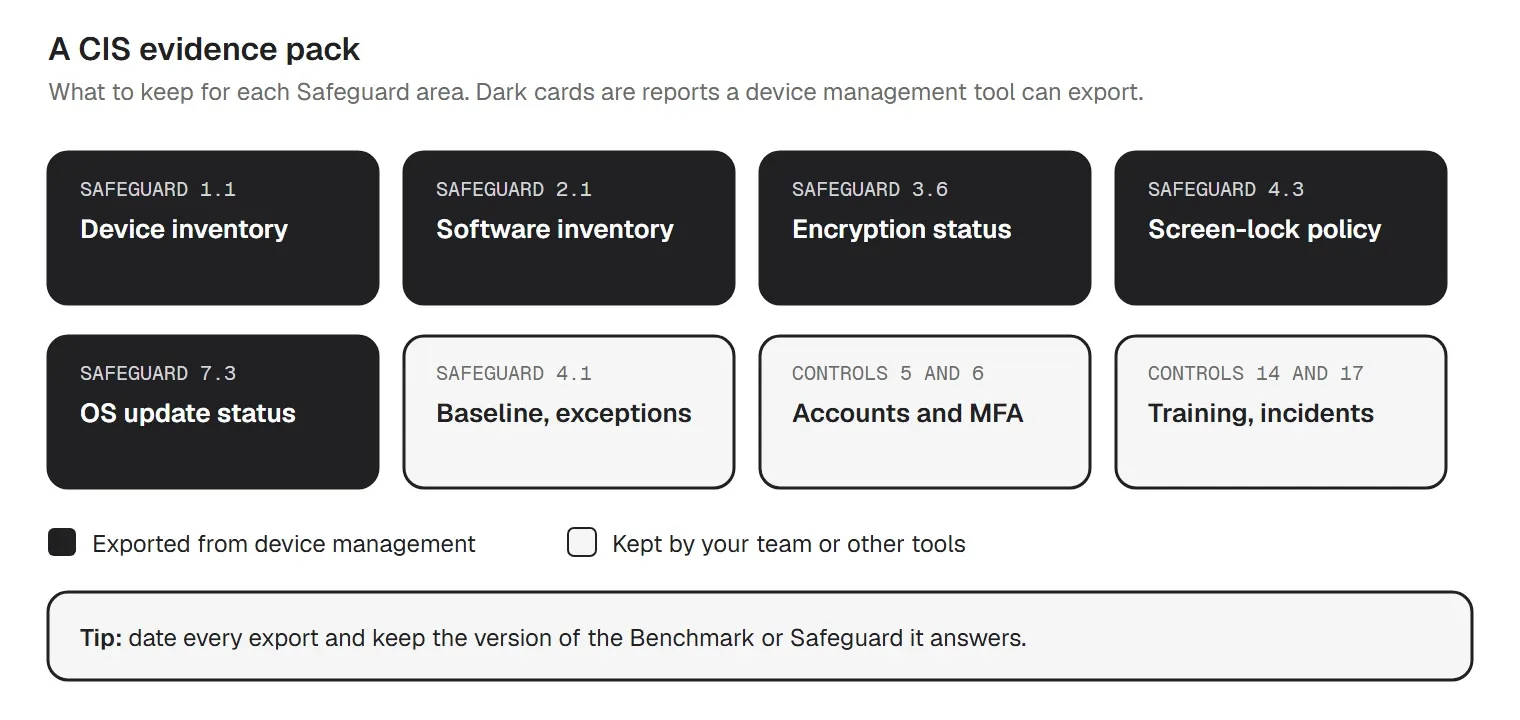
| Safeguard area | Evidence to keep |
|---|---|
| Asset inventory (1.1) | Device inventory export with owner, OS version and last check-in |
| Software inventory (2.1) | Installed software list and your approved software list |
| Device encryption (3.6) | Encryption status for each laptop and phone |
| Secure configuration (4.1) | Baseline per platform, exceptions register, scan reports |
| Session locking (4.3) | Passcode and screen-lock policy settings |
| OS patching (7.3) | OS update status per device |
| Accounts and MFA (5, 6) | Account list, MFA settings from your identity provider |
| Training and incidents (14, 17) | Training records, incident contacts and process |
If you need to justify why you stopped at a Safeguard or an IG, CIS RAM, the free CIS Risk Assessment Method, gives you a structured way to define acceptable risk.
Customer security questionnaires often ask about CIS. So do cyber insurers: in November 2025 CIS and CyberAcuView launched Control Assist, which maps IG1 to common underwriting questions for small businesses (CIS).
Several US states also give some legal protection in data breach lawsuits to businesses whose written security program follows a recognized framework, and the CIS Controls are on each list (CIS):
| State | Law | What it gives | In force |
|---|---|---|---|
| Ohio | Data Protection Act (R.C. 1354) | Affirmative defense to tort claims after a data breach | November 2018 |
| Utah | Cybersecurity Affirmative Defense Act | Affirmative defense in breach lawsuits | May 2021 |
| Connecticut | Public Act 21-119 | No punitive damages in breach tort cases | October 2021 |
| Iowa | Code chapter 554G | Affirmative defense to tort claims | July 2023 |
| Texas | SB 2610 | No exemplary damages for businesses under 250 employees with a qualifying program; names CIS IG1 for businesses with 20 to 99 employees | September 2025 |
These laws offer a defense or a limit on damages, not immunity, and only for claims under that state's law (Ohio, Texas). The program has to be written down and kept current: Iowa, for example, expects it to follow a revised framework within one year of the revision. This is not legal advice; ask counsel how the law in your state applies.
CIS publishes mappings from CIS Controls v8.1 to NIST CSF 2.0, NIST SP 800-53 Rev. 5, NIST SP 800-171 (Rev. 2 and Rev. 3), PCI DSS v4.0, HIPAA and ISO/IEC 27001:2022 (CIS mappings). They show where one piece of work counts toward several frameworks. A mapping does not replace the other framework's own requirements or audit. If you are weighing CIS against NIST, see NIST vs CIS; for ISO, the ISO 27001 checklist.
CIS compliance software is a loose label. It helps to sort tools by the job they do: configuration assessment (CIS-CAT and scanners certified for Benchmark assessment), device management (enforcing and reporting device settings), assessment and GRC platforms (tracking Safeguards and evidence), and the tools behind specific Controls, such as log management, backup and malware protection.
| Area | Software can | Your team owns |
|---|---|---|
| Inventory | Find enrolled devices and installed apps, and export the lists | Deciding what is authorized and what to do about unknown devices |
| Secure configuration | Enforce settings by policy and check devices against Level 1 or Level 2 templates | Choosing the profile for each device group and accepting exceptions |
| Encryption and patching | Enforce disk encryption and OS updates, and report status per device | How long updates may be deferred, and what to do with devices that can't update |
| Assessment | Track Safeguard status, store evidence and schedule reviews | Scoring honestly and choosing the Implementation Group |
| Configuration scans | Scan systems against Benchmarks and produce reports | Reading the results and deciding what to fix first |
| People and process | Deliver training, track completions, store plans and contracts | Training content, vendor decisions, running an incident |
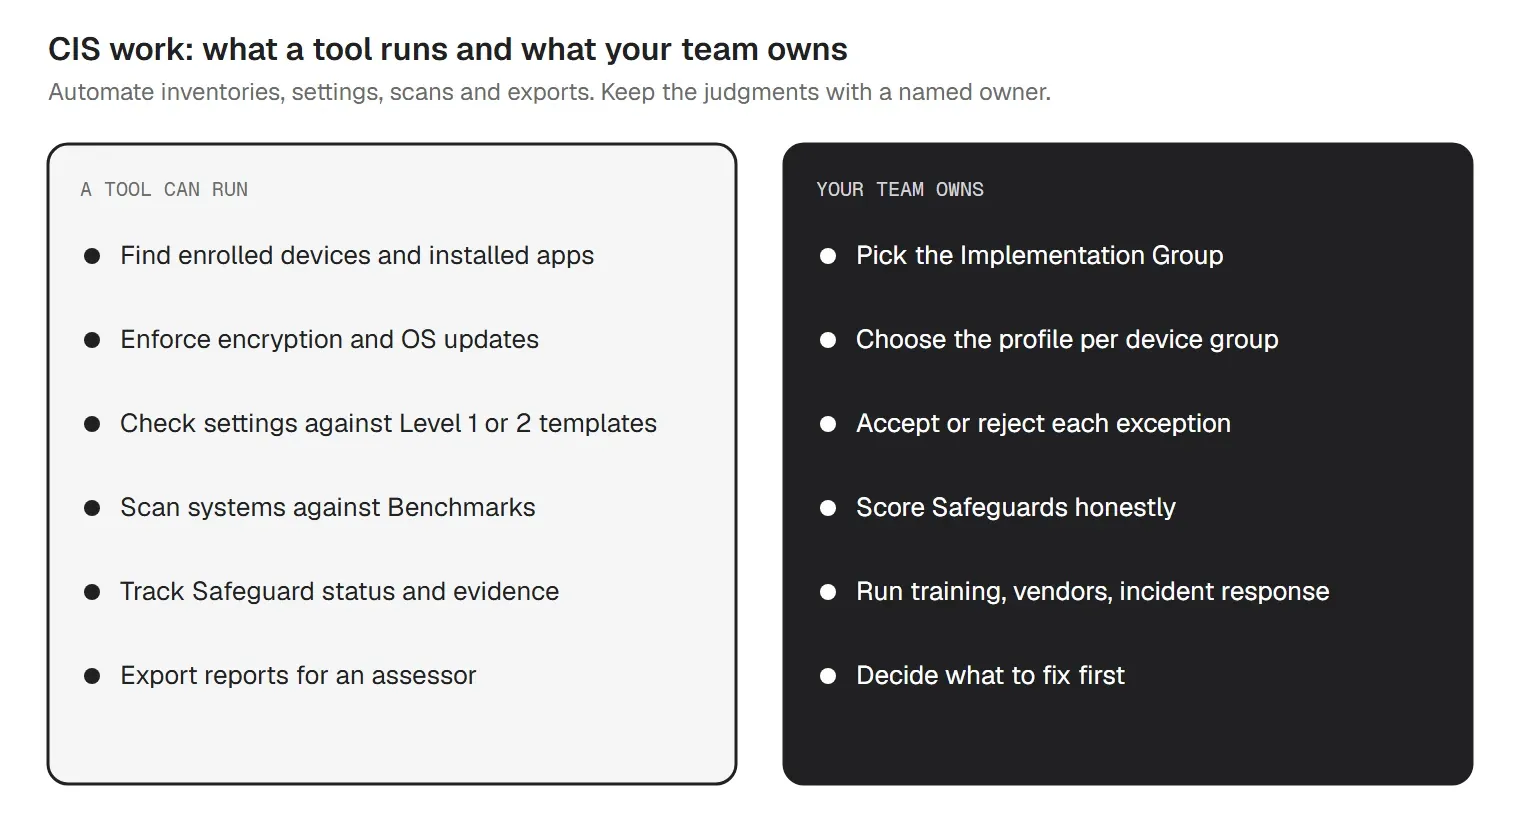
A green dashboard shows that settings match a template. It doesn't show that you picked the right Implementation Group, that your exceptions are justified, or that people know what to do in an incident.
More CIS guides for IT teams
trio.so is device management software. On Windows, Mac, iOS and Android, from one console, it enforces and reports the device settings behind several CIS Safeguards:
trio.so does not make you CIS compliant, and CIS does not certify organizations. Your team still owns the decisions: which profile fits each device group, which exceptions you accept, and the Controls that live outside devices, such as training, service providers, incident response and penetration testing. Learn more about compliance automation.
Plans start at $5 per device.
14-day free trial. No credit card required.
More CIS guides: the CIS Controls v8.1 guide, what CIS Benchmarks are and how to apply them, and NIST vs CIS. For the evidence side, see continuous compliance monitoring.
Sources. Last reviewed October 2026. This article is guidance, not legal or audit advice. CIS Controls® and CIS Benchmarks™ are marks of the Center for Internet Security, Inc.; trio.so is not affiliated with or endorsed by CIS. Safeguard titles are paraphrased.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA technical safeguards are the 5 standards in 45 CFR 164.312. What each one requires, required vs addressable, and the device settings that meet it.
Shadow AI breaches average $4.63M. Here is how to detect shadow AI using DNS logs, OAuth audits, and your endpoint inventory, step by step.
Declarative device management is Apple's answer to MDM polling delays and unreliable compliance data — here's how it works and how to start using it.
An APNS certificate is what lets your MDM platform send commands to iPhones, iPads, and Macs — here's how to create, renew, and protect it.
Device location history works differently on Android, iPhone, and MDM platforms. Here's what each one actually stores and how to access it.
Unlike full-device VPN, per-app VPN tunnels only the apps you choose — and without MDM enforcement, users can bypass it entirely on unmanaged devices.
A remote wipe on a Mac is only possible if the right tools are in place first — here is how MDM, Find My, and native macOS each handle device erasure.
Compare SOC 2 Type 1 and Type 2 audits. Discover key differences, audit scope, duration, and how to choose for compliance needs.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients