



Explained
Automated Tools for PCI DSS Compliance: A Full Guide
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
PCI compliance checklist for PCI DSS v4.0.1: the 12 requirements, the 51 future-dated items, CDE scoping and SAQ vs ROC, with a free PDF and Excel tracker.

Content writer, trio.so
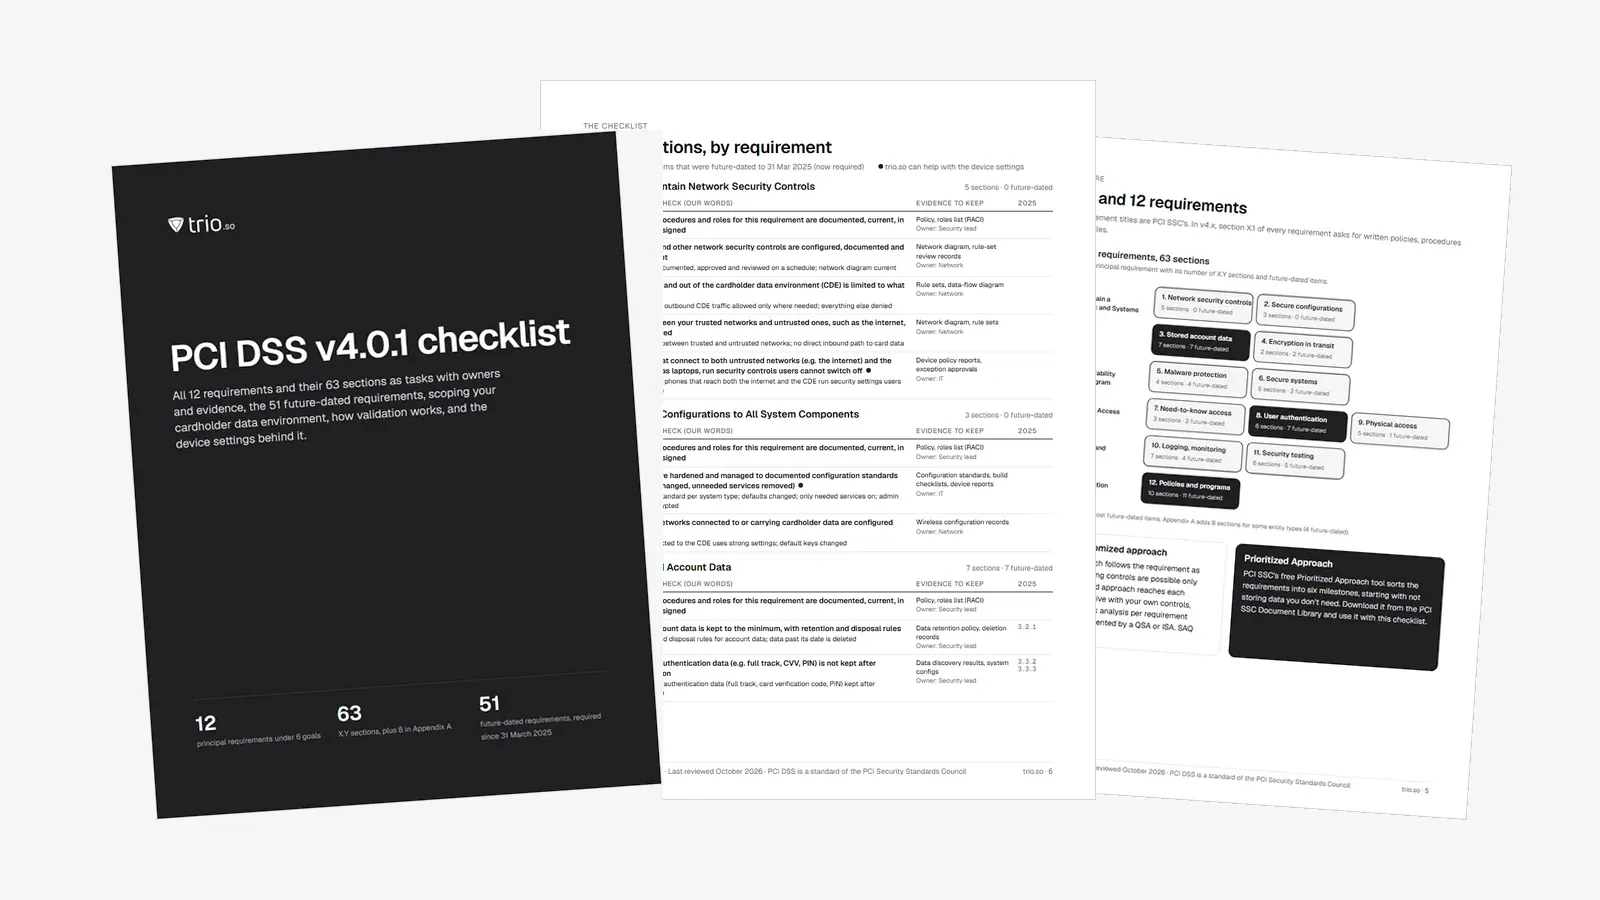
A PCI compliance checklist turns the Payment Card Industry Data Security Standard (PCI DSS) into tasks you can assign and prove. This one follows PCI DSS v4.0.1, the only version in force, and covers all 12 requirements, their 63 sections and the 51 requirements that became mandatory on 31 March 2025.
It is written for IT managers, security leads and MSPs at merchants and service providers that take, process or store card payments. Use it to scope your cardholder data environment, run a gap analysis and get ready for an SAQ or a QSA assessment.
The free download has a PDF guide and an Excel tracker. The tracker lists every requirement section with a future-dated flag, owner, status and evidence columns, and comes with a scope inventory, a device controls sheet, an SAQ selector and a progress dashboard.
In short
PCI DSS is a set of technical and operational security requirements for anyone that stores, processes or transmits payment card data, or could affect its security. The PCI Security Standards Council (PCI SSC) publishes it. American Express, Discover, JCB International, Mastercard and Visa founded the council, and each of them runs its own compliance program.
It is an industry standard, not a law. PCI SSC writes the standard and trains assessors, but it does not enforce compliance or decide who has to validate. The card brands and acquiring banks do that, and the obligation reaches a merchant through card-brand rules and the merchant agreement with its acquirer. If a requirement ever conflicts with local law, the law wins.
The standard protects "account data". That covers cardholder data (the card number, or PAN, plus the cardholder name, expiry date and service code) and sensitive authentication data such as full track data, card verification codes and PINs. It applies whatever your size or transaction volume. What changes with size is how you prove it, which our guide to PCI DSS compliance for small business covers in more detail.
PCI SSC published PCI DSS v4.0.1 on 11 June 2024. It is a limited revision of v4.0 (March 2022) with no added or deleted requirements: clarifications, corrected errors and extra guidance. One change matters for patching. Requirement 6.3.3 again sets the one-month deadline for critical vulnerabilities only, as v3.2.1 did.
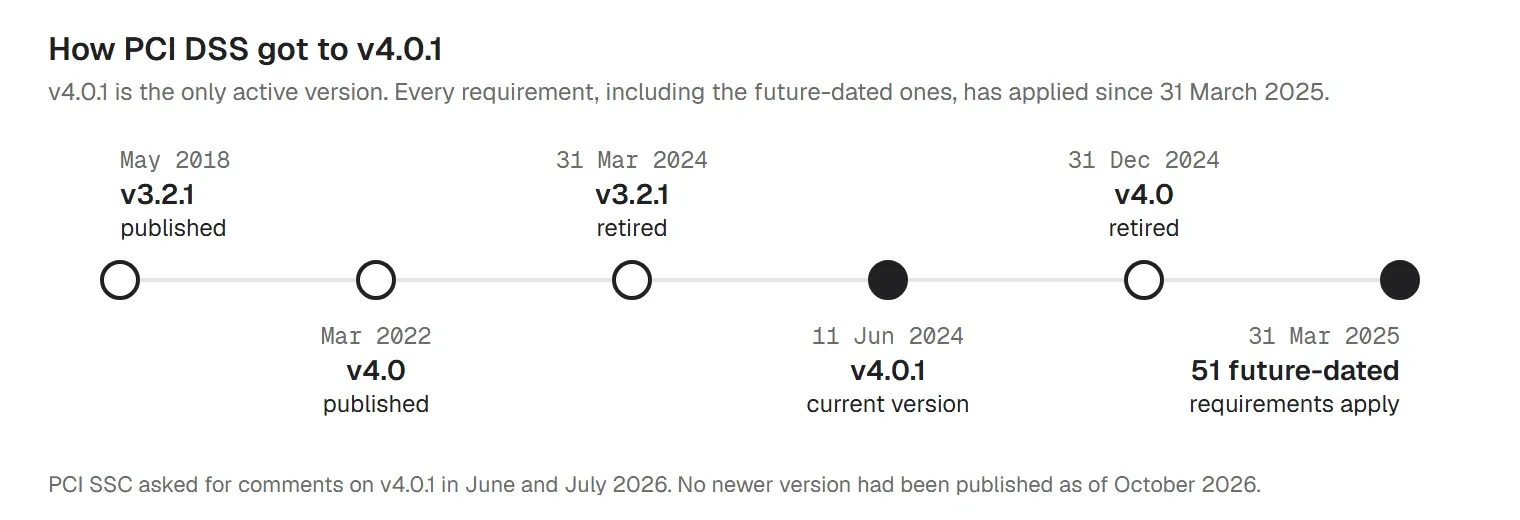
v4.0 brought in 64 new requirements. Thirteen applied at once. The other 51 were best practice until 31 March 2025 and are now mandatory in every assessment. If your last gap analysis predates that date, the PCI DSS 4.0 requirements you marked "future" are now open findings. No newer version has been published; PCI SSC asked for comments on v4.0.1 in June and July 2026 without naming a date for the next one.
PCI DSS scope decides how much of this checklist applies to you, so do it before anything else. The cardholder data environment (CDE) is the people, processes and technology that store, process or transmit account data. Systems that connect to the CDE, or could affect its security, are in scope too: the directory that controls logins to it, the admin laptops that reach it, and the patch, logging and anti-malware servers that serve it.
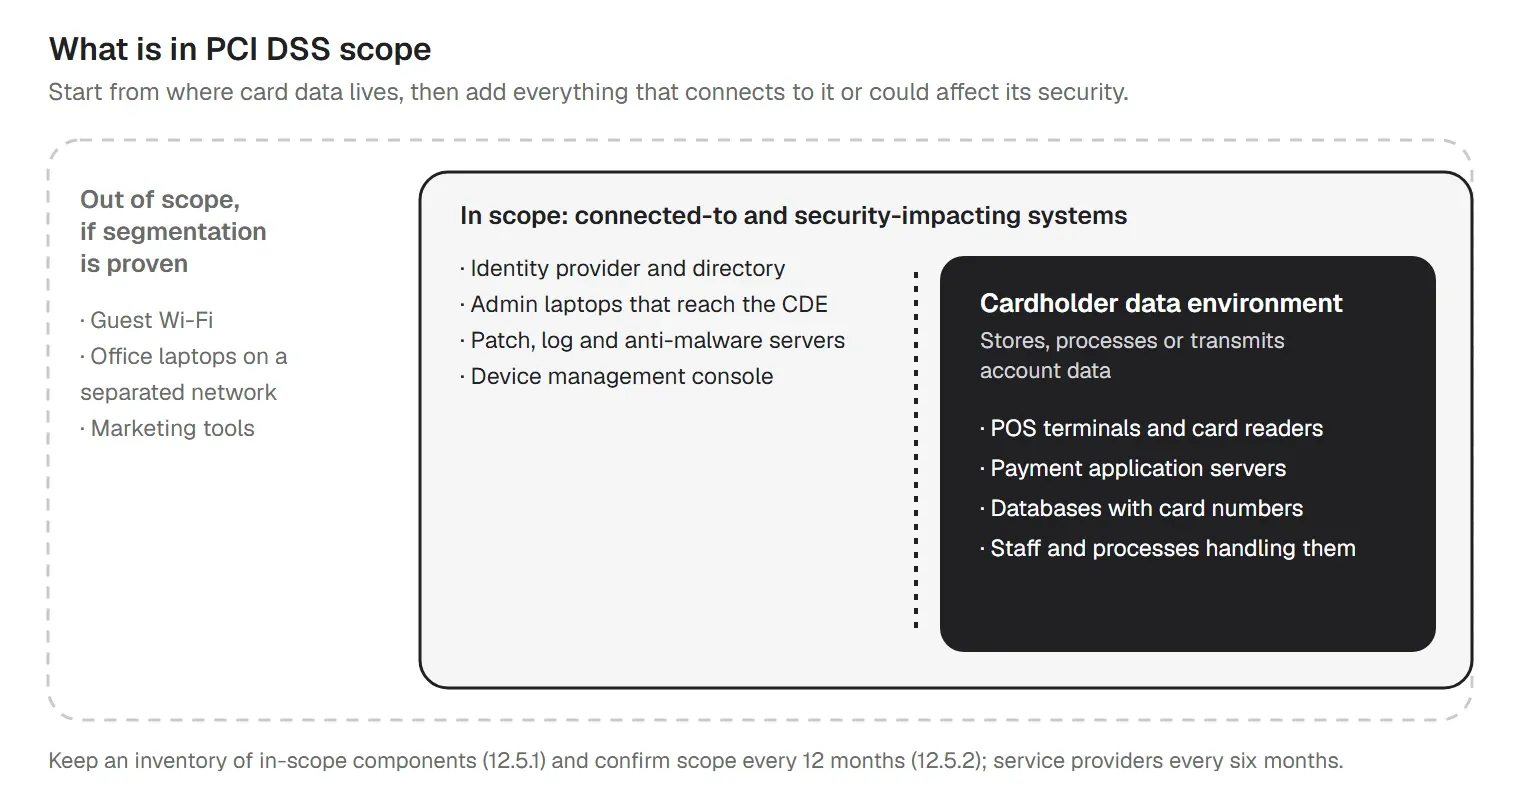
Segmentation can take a system out of scope, but only if you can show it works, and an assessor will test it. Three habits keep scope honest:
The cheapest scope reduction is not keeping card data at all. Tokenization, a hosted payment page or a validated point-to-point encryption (P2PE) solution can shrink scope a lot.
PCI DSS groups its 12 principal requirements under six goals. Each requirement splits into X.Y sections (63 in all), and in v4.x the first section of every requirement asks for written policies, procedures and assigned roles. The requirement titles below are PCI SSC's; the checks are our summary, not the standard's text.
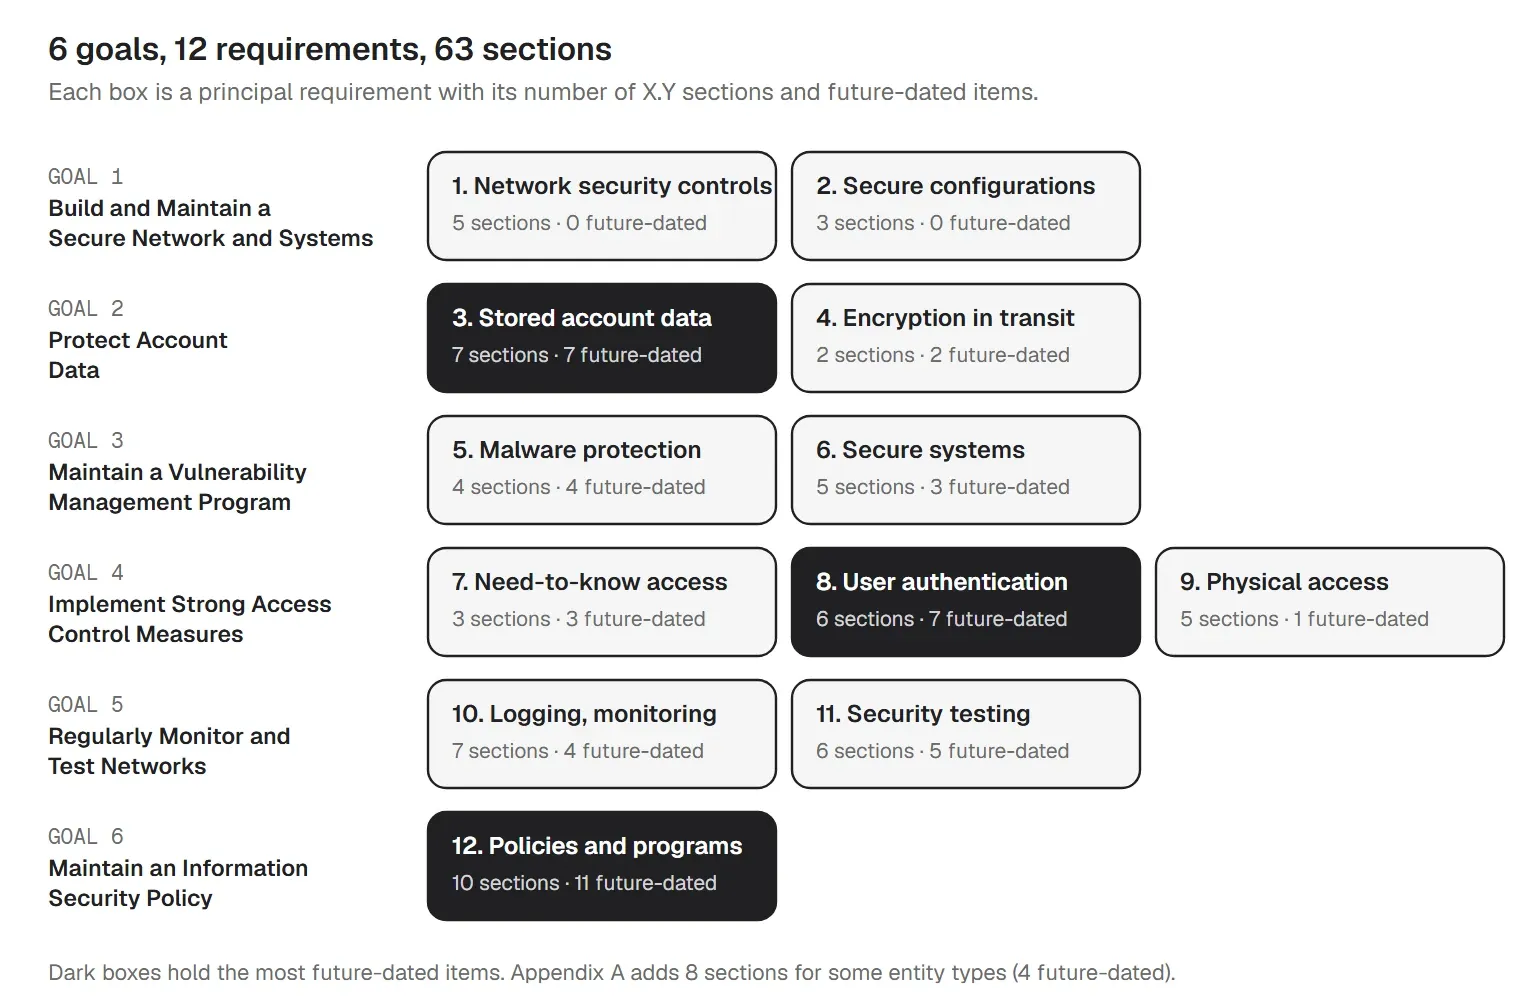
| # | Requirement | What to check |
|---|---|---|
| 1 | Install and Maintain Network Security Controls Goal 1: Build and Maintain a Secure Network and Systems | Network security controls (firewalls and similar) are configured and reviewed; CDE traffic is limited to what is needed; laptops that also reach the internet run controls users can't turn off. |
| 2 | Apply Secure Configurations to All System Components Goal 1: Build and Maintain a Secure Network and Systems | Every system type has a written hardening standard; vendor default passwords are changed or accounts disabled; unneeded services are off; Wi-Fi in scope is set up securely. |
| 3 | Protect Stored Account Data Goal 2: Protect Account Data | You keep as little account data as possible; no sensitive authentication data after authorization; card numbers are masked on screen and unreadable where stored; keys are managed. |
| 4 | Protect Cardholder Data with Strong Cryptography During Transmission Over Open, Public Networks Goal 2: Protect Account Data | Card numbers sent over open, public networks use strong cryptography with valid certificates; you keep an inventory of trusted keys and certificates. |
| 5 | Protect All Systems and Networks from Malicious Software Goal 3: Maintain a Vulnerability Management Program | Anti-malware runs and updates itself on systems at risk; removable media is scanned; staff are protected against phishing. |
| 6 | Develop and Maintain Secure Systems and Software Goal 3: Maintain a Vulnerability Management Program | Vulnerabilities are ranked; critical patches go on within one month; custom software is inventoried and built securely; payment-page scripts are controlled. |
| 7 | Restrict Access to System Components and Cardholder Data by Business Need to Know Goal 4: Implement Strong Access Control Measures | Access follows job need; all user accounts and privileges are reviewed every six months; system and application accounts get least privilege. |
| 8 | Identify Users and Authenticate Access to System Components Goal 4: Implement Strong Access Control Measures | Unique IDs; idle sessions re-authenticate after 15 minutes; lockout after 10 failed attempts; 12-character passwords; MFA for all non-console access into the CDE. |
| 9 | Restrict Physical Access to Cardholder Data Goal 4: Implement Strong Access Control Measures | Physical access to the CDE is controlled; media with card data is tracked and destroyed properly; card-reading devices are listed and inspected for tampering. |
| 10 | Log and Monitor All Access to System Components and Cardholder Data Goal 5: Regularly Monitor and Test Networks | Audit logs capture the right events, are protected, reviewed daily (with automated tools) and kept 12 months; control failures raise alerts. |
| 11 | Test Security of Systems and Networks Regularly Goal 5: Regularly Monitor and Test Networks | Rogue Wi-Fi checks; internal and external scans every three months; yearly penetration tests; intrusion detection; payment pages watched for changes. |
| 12 | Support Information Security with Organizational Policies and Programs Goal 6: Maintain an Information Security Policy | Security policy, acceptable-use rules, targeted risk analyses, scope confirmed yearly, awareness training, vendor management and an incident response plan. |
The Excel tracker breaks each row down into its sections, with an owner, a due date, a status and the evidence to keep. For the official wording, download the standard free from the PCI SSC Document Library.
Give the 51 future-dated requirements their own pass, because gap analyses done before 2025 often marked them as future work. Requirement 12 holds 11 of them; Requirements 3 and 8 hold 7 each.
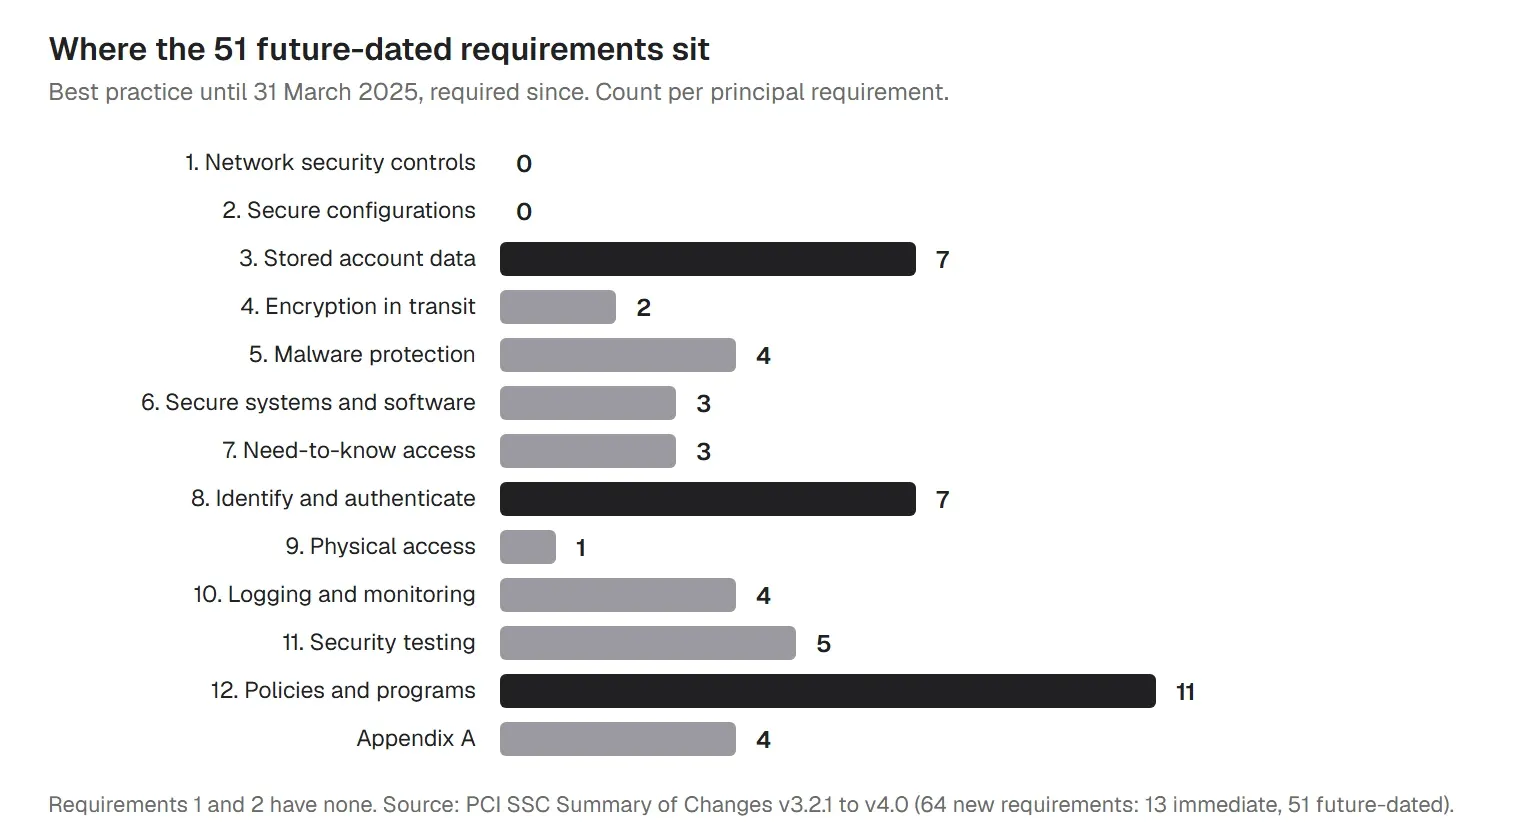
The tracker has a separate tab for all 51, each with our short label, who it applies to and a status column.
Validation is how you show your acquirer or customers where you stand. There are two routes:
Either way you sign an Attestation of Compliance (AOC) and send it, with any Approved Scanning Vendor (ASV) scan reports, to your acquirer. Merchant levels decide which route you take, and each card brand sets its own. On Visa's scale, Level 1 is over 6 million Visa transactions a year and needs an annual ROC by a QSA; Levels 2 and 3 complete an annual SAQ, and for Level 4 the acquirer sets the requirements. Ask your acquirer which level and SAQ apply to you; the workbook's SAQ selector only gives a first guess.
Two more points come up in planning. Entities that self-assess with an SAQ cannot use the customized approach, which needs a QSA or ISA. And PCI SSC's free Prioritized Approach tool sorts the requirements into six milestones, starting with "don't store data you don't need"; download it from the Document Library and use it alongside this checklist. Our PCI compliance audit guide walks through the assessment itself.
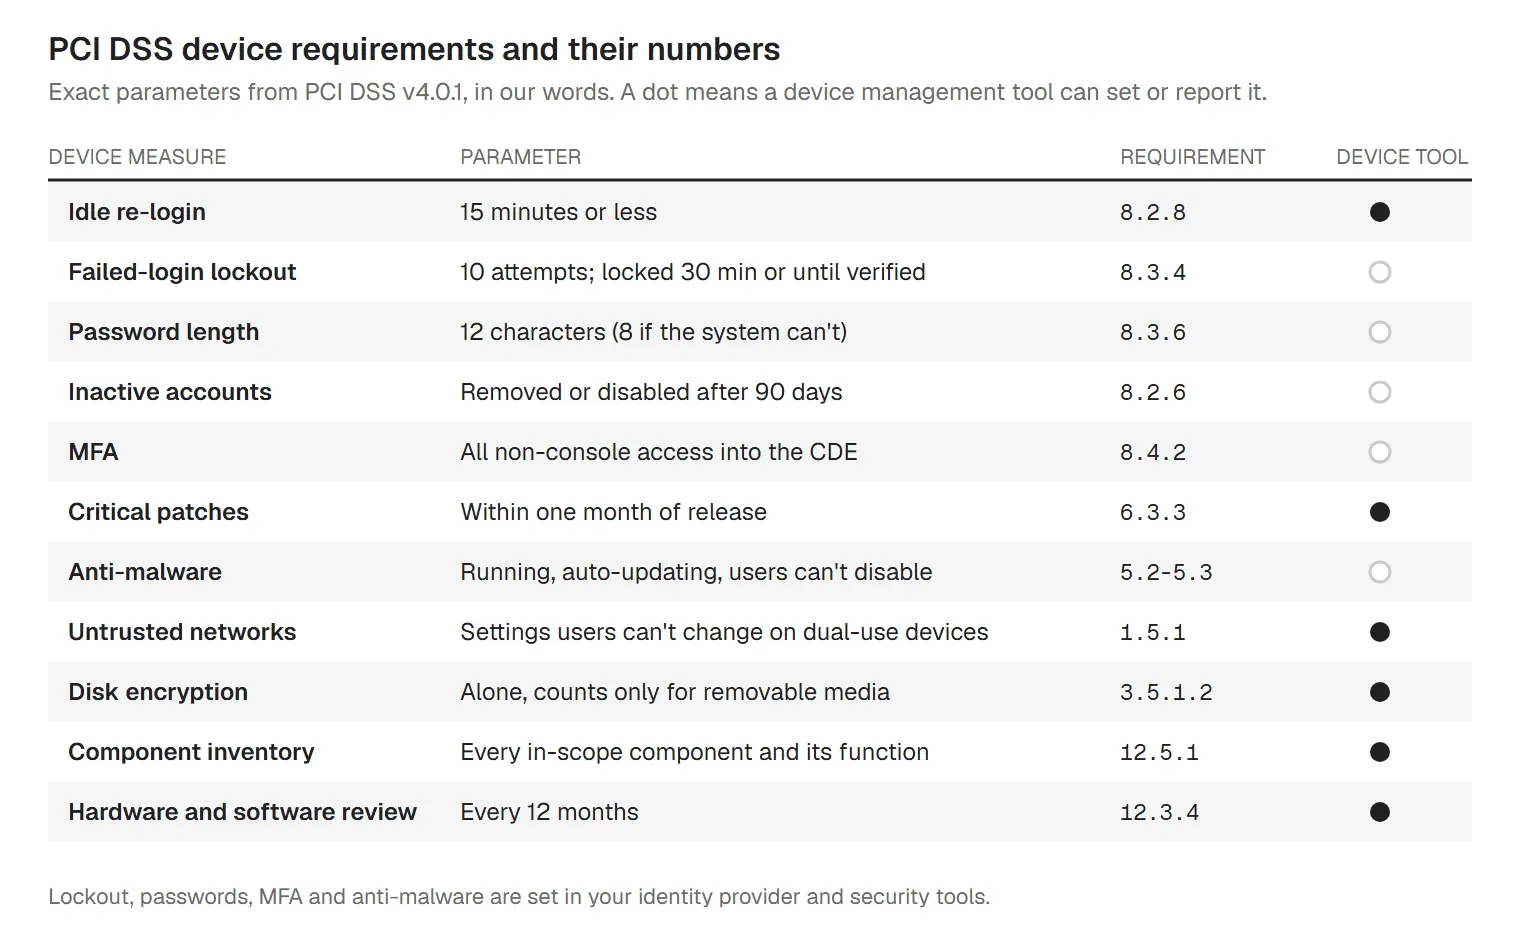
PCI DSS never mentions MDM, but a good part of it lands on the laptops, desktops, phones and payment terminals in scope. These are the parameters assessors check, from v4.0.1:
A PCI DSS gap analysis compares what you do today with each requirement and turns the difference into a plan. With the tracker it takes these steps:
Automation helps with the evidence part. Our guide to automated tools for PCI DSS compliance compares the tool types.
If you work across several frameworks, our NIST compliance checklist, ISO 27001 checklist, CIS Controls checklist and HIPAA compliance checklist come with similar trackers.
More PCI DSS guides for IT teams
Most of PCI DSS is network security, logging, testing, physical security and policy, and trio.so does none of that. It handles the device settings behind several requirements, from one console across Windows, Mac, iOS and Android:
See how trio.so handles the device side of PCI DSS, area by area, with the evidence you can show your assessor.
trio.so does not assess or validate PCI DSS compliance, and using it does not make you PCI DSS compliant. Your QSA or your SAQ does the validating, and account lockout, MFA, anti-malware, logging, scanning and payment-page requirements need other tools. Learn more about compliance automation. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed October 2026. PCI DSS is a standard of the PCI Security Standards Council. trio.so is not affiliated with or endorsed by PCI SSC. Requirement summaries here are paraphrased; get the official text from the PCI SSC Document Library. This article is guidance, not legal advice or an assessment. The device mapping is ours.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
PCI compliance for small business under PCI DSS v4.0.1: merchant levels, which SAQ you need, what drives the cost, and how PCI fines work for merchants.
Complete POS security guide covering threats, malware protection, mobile vulnerabilities, PCI DSS compliance, and implementation best practices.
PCI compliance audit guide for PCI DSS v4.0.1: QSA, ISA or SAQ, ROC vs AOC, ASV scans, pen tests, the evidence auditors ask for and how to prepare.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients