



Explained
POS Security: Complete Guide to Point-of-Sale System Protection
Complete POS security guide covering threats, malware protection, mobile vulnerabilities, PCI DSS compliance, and implementation best practices.
PCI compliance for small business under PCI DSS v4.0.1: merchant levels, which SAQ you need, what drives the cost, and how PCI fines work for merchants.

Content writer, trio.so
For most small businesses, PCI compliance means a yearly Self-Assessment Questionnaire (SAQ), not an outside audit. PCI DSS applies to every business that accepts payment cards, whatever its size (PCI SSC). Size changes how you prove it: the card brands sort merchants into levels, most small businesses land in the lowest one, and your acquiring bank tells you which SAQ to fill in.
This guide explains the PCI compliance levels, helps you pick your SAQ and walks through completing it. It also covers what drives the cost and how fines work. Everything here follows PCI DSS v4.0.1, the current version.
In short
Yes. PCI DSS applies to every merchant that stores, processes or transmits cardholder data, or could affect its security, regardless of size or transaction volume. The card brands decide whether and how small merchants have to validate (PCI SSC).
The PCI Security Standards Council (PCI SSC) writes the standard but doesn't enforce it. The obligation comes from the card brands' rules, which reach you through the merchant agreement with your acquirer, the bank or processor that handles your card payments (PCI SSC FAQ 1212). Where a law asks for more, or conflicts with the standard, the law applies.
Outsourcing card handling shortens the work, though some always stays with you. If a payment provider handles every step, your SAQ is short, but you still complete it, keep a list of the service providers that touch card data and check their compliance status every year (Requirement 12.8).
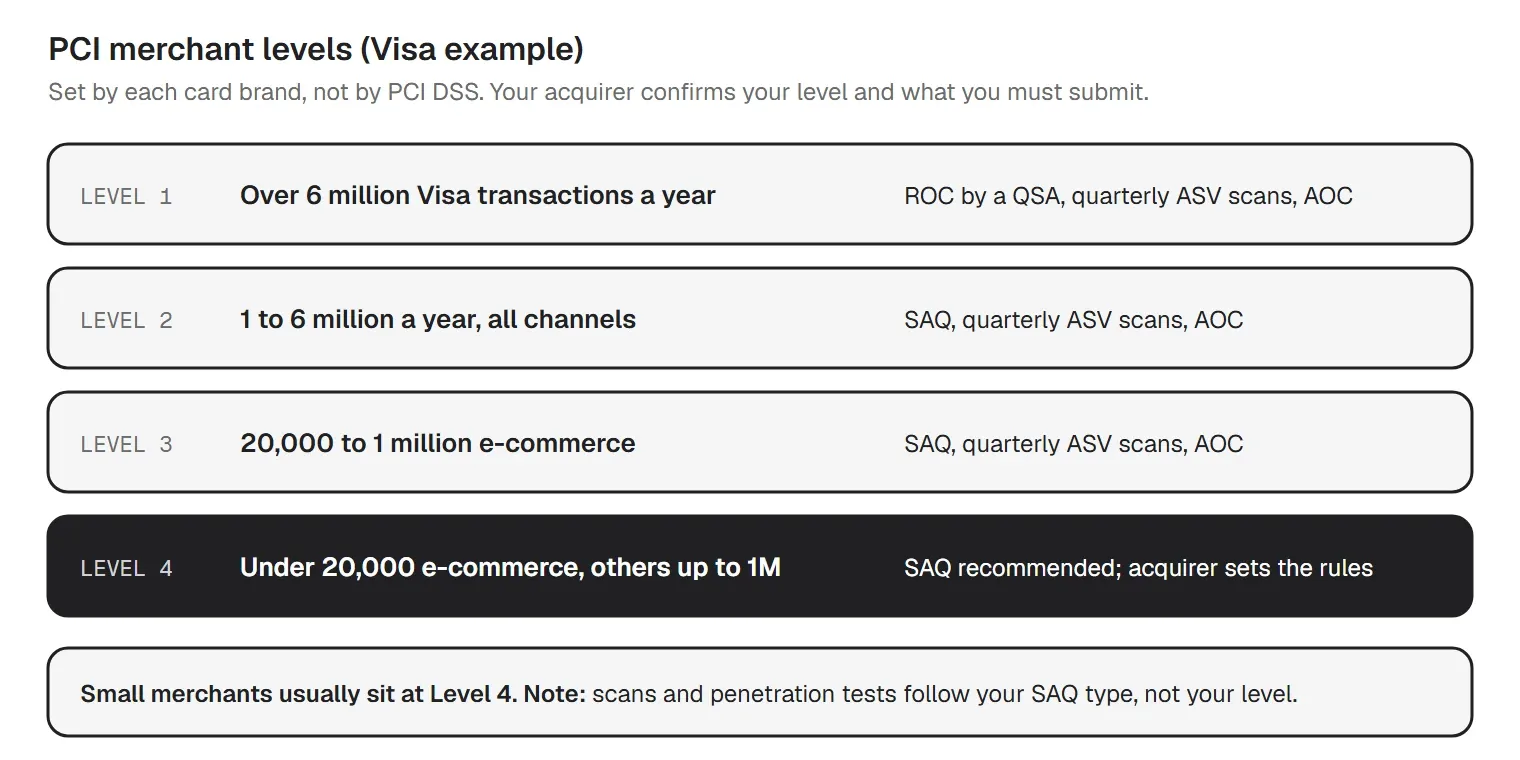
PCI merchant levels are set by each card brand, not by PCI DSS, and they decide how you validate. Visa's levels (Visa):
| Visa level | Visa transactions a year | How you validate |
|---|---|---|
| Level 1 | Over 6 million Visa transactions a year, all channels | Annual Report on Compliance (ROC) by a QSA, quarterly ASV scans, Attestation of Compliance (AOC) |
| Level 2 | 1 million to 6 million, all channels | Annual SAQ, quarterly ASV scans, AOC |
| Level 3 | 20,000 to 1 million e-commerce | Annual SAQ, quarterly ASV scans, AOC |
| Level 4 | Under 20,000 e-commerce, and all other merchants up to 1 million | SAQ recommended; quarterly ASV scans if applicable; your acquirer sets the requirements |
Mastercard uses similar transaction bands with its own rules, and American Express, Discover and JCB run their own programs. Your acquirer decides how its program applies to you, so confirm your level with it in writing. For a small business, two points matter more than the level number:
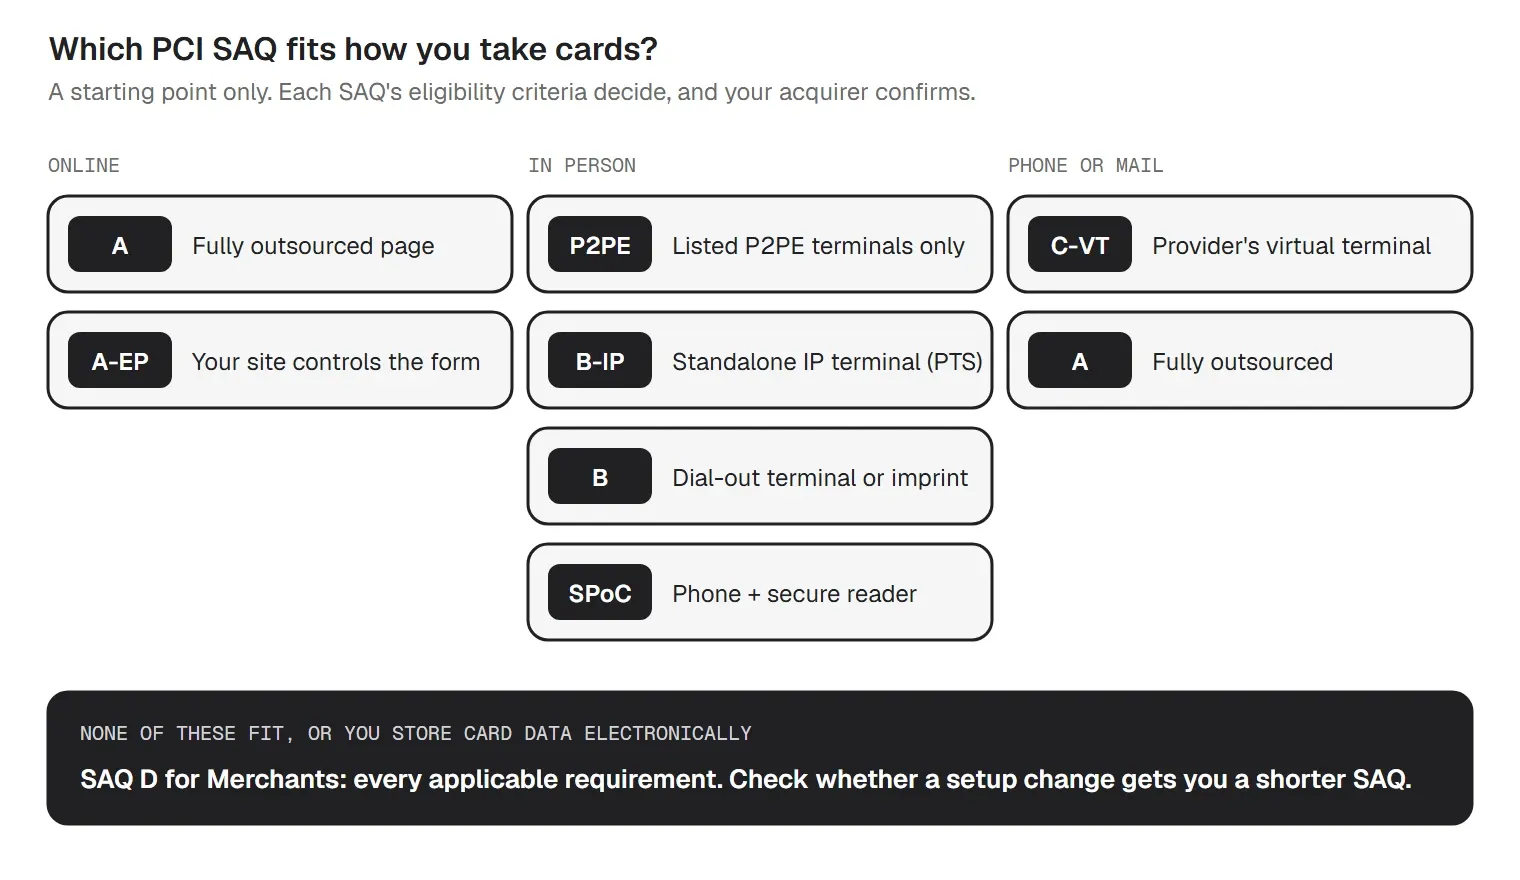
A PCI self-assessment questionnaire covers the parts of PCI DSS that apply to one payment setup. Each SAQ starts with eligibility criteria, and you can use it only if your business matches all of them. Your acquirer tells you which one to use (PCI SSC). The v4.0.1 SAQs were published in October 2024 and are free in the PCI SSC Document Library (Document Library).
| SAQ | Typical setup (our summary; the SAQ's own eligibility criteria decide) |
|---|---|
| A | Online, mail or phone orders where every card data function is outsourced to PCI DSS compliant providers. Online, the payment page is a redirect or the provider's embedded page or iframe. No electronic storage of card data. |
| A-EP | Online stores whose own website controls how card data reaches the payment provider, for example a direct post or JavaScript form, without storing, processing or transmitting card data themselves. |
| B | Imprint machines or standalone dial-out terminals, with no electronic storage of card data. |
| B-IP | Standalone PTS-approved payment terminals with an IP connection to the processor, kept apart from other devices on the network. |
| C | Payment application systems connected to the internet, with no electronic storage of card data. |
| C-VT | Keying one transaction at a time into a provider's web-based virtual terminal on a standalone computer. |
| P2PE | In-person payments taken only on hardware terminals from a point-to-point encryption (P2PE) solution on PCI SSC's list. |
| SPoC | Payments on an ordinary phone or tablet with a secure card reader, as part of a solution on PCI SSC's SPoC list. |
| D for Merchants | Every merchant not eligible for another SAQ. It covers all applicable PCI DSS requirements. |
Service providers that can self-assess use SAQ D for Service Providers, the only SAQ written for them. If you take payments more than one way, for example in a shop and online, ask your acquirer how to validate each channel.
SAQ A is the shortest questionnaire and the one most small online stores aim for. On 30 January 2025, PCI SSC revised it. Requirements 6.4.3 and 11.6.1 on payment-page scripts, and the risk analysis behind 11.6.1, came out of SAQ A, and a new eligibility criterion went in: you confirm that your site is not susceptible to attacks from scripts that could affect your e-commerce system (PCI SSC).
A PCI SSC FAQ from February 2025 explains that the criterion applies when your page embeds the provider's payment form, for example in an iframe, and not when you redirect customers to the provider. You can confirm it by protecting your page against script attacks yourself, or with written confirmation from your PCI DSS compliant payment provider that its embedded form, set up as instructed, includes that protection (PCI SSC).
Storing card data electronically, running your own payment software on an internet-connected network, or a mix of setups that no shorter SAQ covers will usually put you on SAQ D. It covers every applicable requirement, which is a lot for a small team. Before you start, ask whether a different payment setup would move you to a shorter SAQ. A hosted payment page or P2PE terminals can cost less than working through SAQ D's full scope every year.
Our PCI compliance checklist covers all 12 PCI DSS requirements in v4.0.1, so you can see what sits behind each SAQ question.
PCI SSC's Guide to Safe Payments, written by its Small Merchant Task Force, lists 12 security basics, ordered from the easiest and cheapest to the hardest (Guide to Safe Payments). In our words:
Each basic maps to one or more of the 12 PCI DSS requirements. The guide is free, and PCI SSC's merchant pages add plain-language guides to common payment systems and questions to ask your vendors.
There is no official price list for PCI compliance, and quotes vary widely. What you pay depends on a handful of drivers you can predict:
| Cost driver | Why it moves the cost |
|---|---|
| Your SAQ type | SAQ A covers a small set of requirements; SAQ D covers all of them. The questionnaire you qualify for decides most of the work. |
| How much of your setup touches card data | Every system in scope needs secure settings, patching, access control and logging. Hosted payment pages, tokenization and P2PE terminals take systems out of scope. |
| ASV scans | Needed every three months when your SAQ includes external scanning. ASVs charge for scans and rescans. |
| Penetration tests | Needed every 12 months where Requirement 11.4 applies, as on SAQ D. The price depends on how much there is to test. |
| Outside help | Optional for most small merchants on an SAQ, though some hire a QSA to check their scope or answers. |
| Equipment | Replacing terminals that aren't PTS-approved, or moving to a P2PE solution, is a one-off cost that can shorten your SAQ. |
| Staff time | Policies, training, terminal inspections and the yearly SAQ itself. It rarely appears as a line item, so track the hours. |
| Not validating | Your merchant agreement may add fees if you don't validate on time, and a breach brings costs of its own (next section). |
The less card data your own systems handle, the less PCI compliance costs. Before you buy a security product, check whether a change in how you take payments would move you to a shorter SAQ.
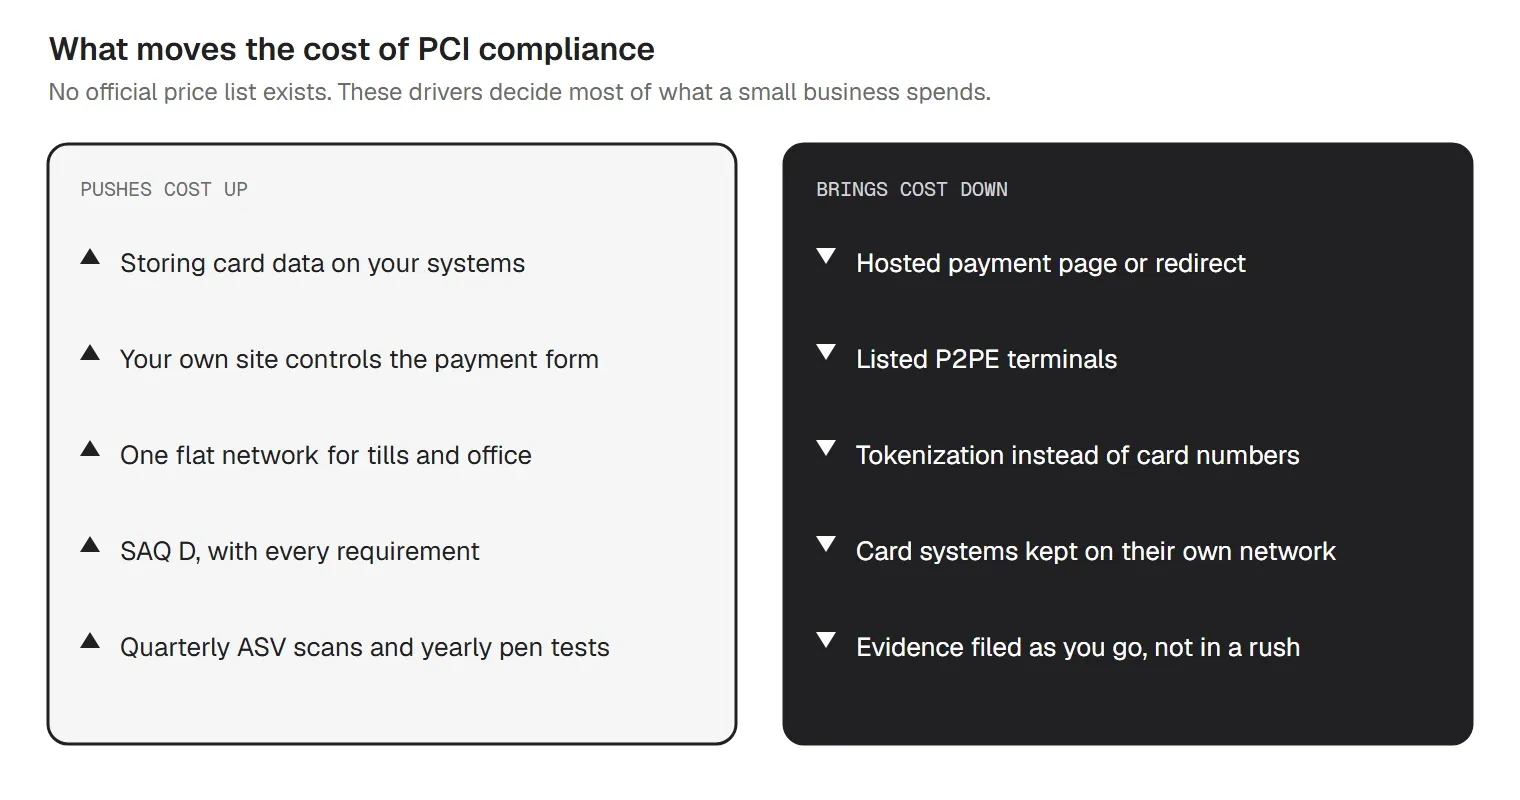
PCI SSC doesn't fine anyone. Fines and non-compliance fees come from the card brands, which apply them to acquirers under their rules, and your merchant agreement decides how they are passed on to you. PCI SSC publishes no fine amounts, and the figures quoted on vendor sites aren't official, so read your merchant agreement and ask your acquirer.
After a breach the stakes rise. PCI SSC's guide for small merchants lists financial penalties, lawsuits and the possible loss of the ability to accept cards (Guide to Safe Payments). Your merchant agreement is the document to read for what applies to you.
More PCI DSS guides for IT teams
Small businesses often take payments on ordinary laptops, tablets and phones, and those devices are in scope when they touch card data or the systems around it. trio.so is device management software that enforces and reports their settings on Windows, Mac, iOS and Android from one console:
See how trio.so handles the device side of PCI DSS, area by area, with the evidence you can show your assessor.
trio.so doesn't assess or validate PCI DSS compliance, and PCI SSC says no single product can make a business compliant (FAQ 1258). Your SAQ, signed and sent to your acquirer, does the validating. Terminal inspections, firewalls, ASV scans, MFA, anti-malware and your payment page need other tools, your payment provider or your own routines. Learn more about compliance automation.
Plans start at $5 per device.
14-day free trial. No credit card required.
For other rules small companies face, see SMB compliance.
Sources. Last reviewed October 2026, against PCI DSS v4.0.1 (June 2024), the current version on 26 October 2026. This article is guidance, not legal or assessment advice; your acquirer, card brand and assessor have the final word. PCI DSS is © PCI Security Standards Council, LLC. Requirement numbers and titles are used for reference; descriptions are our own paraphrase. trio.so is not affiliated with or endorsed by PCI SSC.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Complete POS security guide covering threats, malware protection, mobile vulnerabilities, PCI DSS compliance, and implementation best practices.
PCI compliance audit guide for PCI DSS v4.0.1: QSA, ISA or SAQ, ROC vs AOC, ASV scans, pen tests, the evidence auditors ask for and how to prepare.
PCI compliance checklist for PCI DSS v4.0.1: the 12 requirements, the 51 future-dated items, CDE scoping and SAQ vs ROC, with a free PDF and Excel tracker.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients