


Explained
How to Detect Shadow AI in Your Organization
Shadow AI breaches average $4.63M. Here is how to detect shadow AI using DNS logs, OAuth audits, and your endpoint inventory, step by step.
What is SIEM integration, and how does it improve threat detection? Learn practical steps, tools, and tips for SMBs in this concise guide.
For small and midsize businesses, staying ahead of cyber threats is a resource puzzle. With limited budgets, mixed device fleets, and overextended IT teams, maintaining visibility and control across the network can feel impossible.
Security Information and Event Management (SIEM) platforms offer a centralized way to collect, analyze, and respond to security events across your entire environment. But SIEMs don’t operate in isolation. Their effectiveness hinges on the quality and diversity of the data they ingest, from firewalls and cloud apps to laptops and mobile phones.
A robust MDM solution like Trio enhances SIEM by supplying rich, real-time data from endpoints: user identities, device health, app usage, compliance posture, and more. This insight is essential, especially in hybrid environments where personal devices and remote work introduce additional risks.
In this guide, we’ll break down what SIEM integration is, why it matters for SMBs, and how to approach it, covering data sources, integration workflows, key features, benefits, common challenges, and actionable best practices.
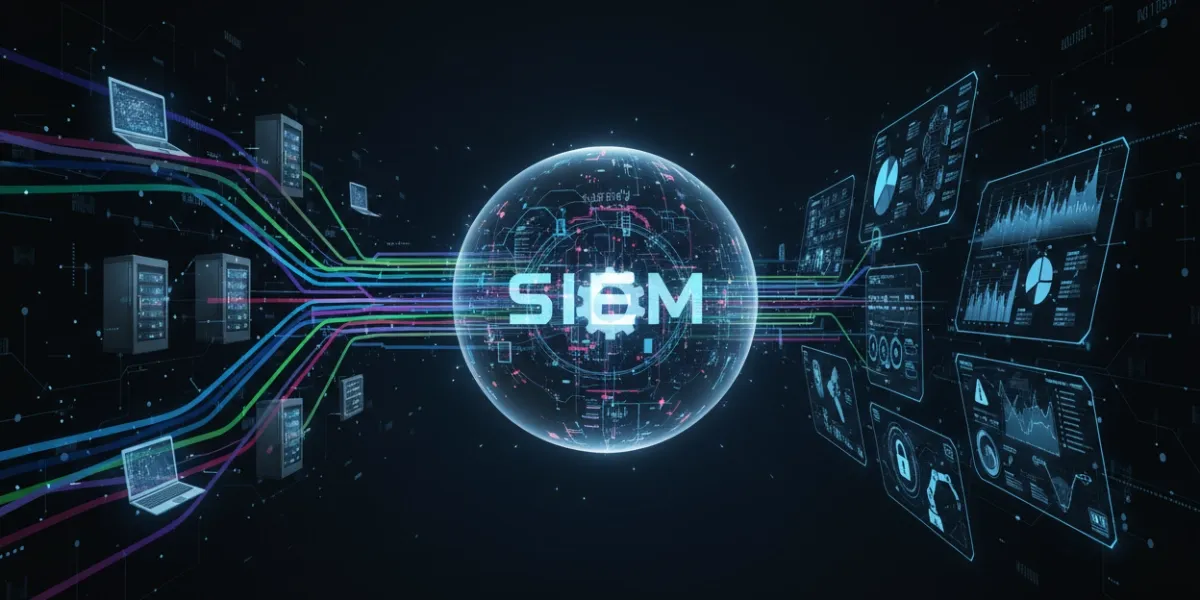
SIEM integration refers to the process of connecting various IT systems, endpoints, servers, apps, and security tools to a Security Information and Event Management (SIEM) platform so that their event data can be collected, normalized, and analyzed in one place. This enables organizations to detect threats, enforce compliance, and respond quickly to suspicious activity.
At its core, SIEM systems ingest log data from across the environment, correlate those logs to identify patterns or anomalies, and generate alerts based on predefined rules. Think of it as your IT security command center, but it only works if it can “see” what’s happening across your ecosystem.
This is where MDM integration becomes critical. Without it, your SIEM is flying blind. By integrating your mobile and desktop devices via a modern MDM solution like Trio, you add essential context to your security data: who’s using which device, whether it’s compliant, what apps are running, and whether it has been recently locked or wiped. That kind of real-time visibility is crucial for spotting threats before they spread.
A well-integrated SIEM setup can serve as a powerful force multiplier, reducing time spent on manual log reviews and enabling more automated, proactive defenses.
Effective SIEM integration starts with capturing data from the right sources. A SIEM system thrives on volume and variety; the more complete the picture, the better it can detect and correlate threats.
Core data sources typically include:
Proper connectivity means configuring these systems to securely forward events to your SIEM, often via agents, APIs, or syslog. Mobile devices and cloud platforms mustn’t be overlooked. For example, integrating Mobile Device Management (MDM) for Office 365 ensures that endpoint activity within your Microsoft environment is fully visible to your SIEM.
This broad connectivity ensures you're not operating with blind spots, a common issue in under-integrated environments.
A successful SIEM integration is about building a repeatable workflow that turns raw logs into actionable insights. Whether you’re starting fresh or expanding your current setup, these steps form the foundation of an effective integration process:
Following a clear SIEM deployment checklist helps keep the process structured and prevents common oversights, such as forgetting to configure log retention or failing to test correlation rules before going live.
A well-integrated SIEM platform transforms scattered events into structured, actionable insights. Here are the key features that define an effective SIEM deployment and how integration with related tools enhances each one:
Integrating tools like multi-factor authentication strengthens your ability to correlate risky access attempts, especially when login behavior deviates from norms. Similarly, Active Directory integration provides rich context for user actions, vital for detecting account compromise or privilege misuse.
Integrating your SIEM with tools across your IT stack transforms how your team responds to threats, manages compliance, and operates day to day. For SMBs working with lean teams, these benefits can be especially impactful.
Key benefits of SIEM integration include:
For example, when integrated with a DLP integration tool, your SIEM can detect and respond to sensitive data exfiltration in real time, not just logging it, but acting on it through connected systems.
SIEM integration offers powerful security advantages, but several common hurdles can slow progress or reduce effectiveness, especially for SMBs with limited time and resources. The table below outlines typical challenges and how to address them:
Solving these issues requires a phased rollout, tuned data pipelines, and thoughtful integration planning. Start with high-value sources and work toward full visibility over time.
A successful SIEM deployment refines how your systems communicate, how your alerts are prioritized, and how your team responds. The most effective strategies focus on simplicity, clarity, and incremental growth.
Best practices for SIEM integration include:
For SMBs using cloud-based tools, adopting a cloud SIEM integration approach offers scalability without the infrastructure burden. It also simplifies updates, supports remote work, and reduces deployment overhead.
Ready to simplify threat detection and improve visibility across your entire device fleet?
Whether you’re just starting out with SIEM or looking to strengthen existing integrations, Trio makes endpoint visibility easy, so your SIEM always has the data it needs to keep your business secure.
✅ Book a free demo to see how Trio integrates with your tools and security workflows
🚀 Start your free trial with no credit card and full platform access
Security doesn’t have to be overwhelming. With the right tools, it can just work.
Integrating your SIEM with the right data sources, including mobile devices, cloud platforms, and identity systems, turns your security operations from reactive to proactive. For small and midsize businesses, this integration can bridge the resource gap by automating threat detection, centralizing visibility, and enabling faster response.
MDM platforms play a vital role in this ecosystem. They feed your SIEM the endpoint context it needs to distinguish real threats from background noise. When properly configured, SIEM integration helps you stay compliant, reduce risks, and operate with confidence, even without a large security team.
By starting small, tuning your alerts, and automating where it matters most, you can build a security infrastructure that’s powerful, scalable, and aligned with your business goals.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. Trio MDM is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. Trio MDM is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





About Trio free trials.
Related
The related industry news, interviews, technologies, and resources.
Shadow AI breaches average $4.63M. Here is how to detect shadow AI using DNS logs, OAuth audits, and your endpoint inventory, step by step.
Declarative device management is Apple's answer to MDM polling delays and unreliable compliance data — here's how it works and how to start using it.
An APNS certificate is what lets your MDM platform send commands to iPhones, iPads, and Macs — here's how to create, renew, and protect it.
Device location history works differently on Android, iPhone, and MDM platforms. Here's what each one actually stores and how to access it.
Unlike full-device VPN, per-app VPN tunnels only the apps you choose — and without MDM enforcement, users can bypass it entirely on unmanaged devices.
A remote wipe on a Mac is only possible if the right tools are in place first — here is how MDM, Find My, and native macOS each handle device erasure.
Compare SOC 2 Type 1 and Type 2 audits. Discover key differences, audit scope, duration, and how to choose for compliance needs.
Compare managed and unmanaged devices - definitions, security differences, control levels, and how to choose the right approach for IT.