



Explained
How Secure Is Your Data Without Endpoint Encryption Software?
Endpoint encryption solutions are key for protecting data by converting it into an unreadable format that can only be decrypted by authorized individuals
Turn on BitLocker with Group Policy: policy path, TPM and PIN, recovery key backup to AD, and the fix for "require that a recovery password be specified".

Content writer, trio.so
To turn on BitLocker with Group Policy, create a GPO linked to your Windows computers and configure the settings under Computer Configuration > Policies > Administrative Templates > Windows Components > BitLocker Drive Encryption: the encryption method, startup authentication, and, most important, backup of recovery keys to Active Directory.
Group Policy sets how BitLocker behaves; it does not by itself start encryption on every PC. This guide covers the settings, the AD backup, TPM and PIN options, how to check the result and the fix for the "recovery password" error.
It applies to domain-joined Windows 11 and Windows 10 Pro, Enterprise and Education. Windows Home has device encryption but cannot be managed with BitLocker policy.
gpmc.msc).BitLocker - Workstations.Computer Configuration > Policies > Administrative Templates > Windows Components > BitLocker Drive Encryption.Under BitLocker Drive Encryption, enable Choose drive encryption method and cipher strength (Windows 10 [Version 1511] and later). Pick XTS-AES 256-bit for operating system drives and fixed data drives unless you need compatibility with older systems. Set this before encryption starts: changing it later means decrypting and re-encrypting.
Go to BitLocker Drive Encryption > Operating System Drives and enable Require additional authentication at startup. The options:
| Option | What the user sees | Use it when |
|---|---|---|
| TPM only | Nothing; the PC starts as normal | Standard laptops and desktops; best usability |
| TPM and startup PIN | A PIN at every boot | Higher risk devices, or travelling executives |
| TPM and startup key (USB) | A USB key at boot | Rare, and hard to manage across many PCs |
| Password only, no TPM | A password at boot | Old hardware without a TPM; tick Allow BitLocker without a compatible TPM |
For a TPM and PIN setup, also enable Configure minimum PIN length for startup and set a length of at least 6. Longer is safer.
This is the setting that saves you when a user forgets a PIN or a TPM changes. In the same Operating System Drives folder, enable Choose how BitLocker-protected operating system drives can be recovered, then:
Set the matching policies for fixed data drives and removable drives if you encrypt those. Make sure computers can write to AD: the BitLocker recovery attributes need the right schema (present by default from Windows Server 2012) and the computer account needs permission on its own object.
Back up keys of PCs that were already encrypted before the policy:
manage-bde -protectors -get C:
manage-bde -protectors -adbackup C: -id {KEY-PROTECTOR-ID}
Replace the placeholder with the ID of the Numerical Password protector from the first command.
The GPO configures policy. To start encryption, a user can turn on BitLocker from Settings (the wizard follows your policy), or you run it with PowerShell or a script on each PC:
Add-BitLockerKeyProtector -MountPoint "C:" -RecoveryPasswordProtector
Enable-BitLocker -MountPoint "C:" -EncryptionMethod XtsAes256 -TpmProtector -UsedSpaceOnly
Then check the state of any PC:
manage-bde -status C:
Volume C: [OS]
[OS Volume]

    Size:                 475.37 GB
    BitLocker Version:    2.0
    Conversion Status:    Used Space Only Encrypted
    Percentage Encrypted: 100.0%
    Encryption Method:    XTS-AES 256
    Protection Status:    Protection On
    Lock Status:          Unlocked
    Key Protectors:
        TPM
        Numerical Password
This is example output: sizes and protectors depend on the device. You want Protection On, the method you chose and a Numerical Password protector (the recovery key). Run gpupdate /force and gpresult /h C:\Temp\gpresult.html if the policy does not seem to apply.
You see this error when BitLocker is turned on in a way that does not create a recovery password, and policy requires one. Typical reasons:
Fix it by creating the recovery password protector first, then enabling:
manage-bde -protectors -add C: -RecoveryPassword
manage-bde -on C:
Then check the policy: allow the 48-digit recovery password, and make sure the PC is on the domain network or VPN when it encrypts.
Group Policy is the right tool for domain-joined PCs that stay on the corporate network. For devices that are not domain joined, work remotely or are enrolled in an MDM, the same BitLocker settings are delivered through the BitLocker configuration service provider, and keys are stored in Microsoft Entra ID or your MDM instead of AD. Pick one source of truth per device; two policies that disagree make the "recovery password" error above more likely.
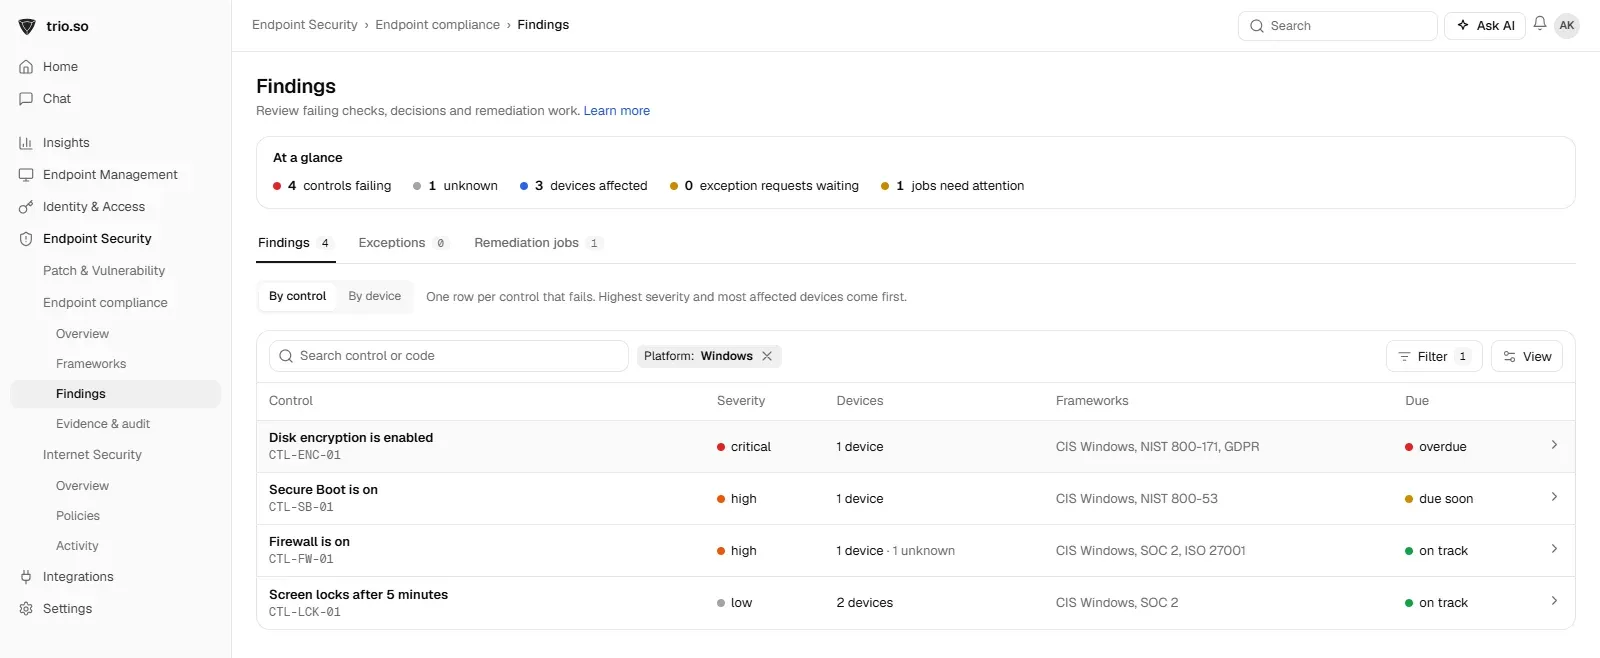
trio.so shows the encryption status of Windows devices. See policy management.
Related reading: BitLocker drive encryption, BitLocker vs VeraCrypt, full disk encryption and should I use FileVault?.
trio.so enforces disk encryption on managed Windows devices by policy and shows which ones are encrypted. Start a 14-day free trial.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Enable-BitLocker through a script or let users start it, and check with manage-bde -status.Related
The related industry news, interviews, technologies, and resources.
Endpoint encryption solutions are key for protecting data by converting it into an unreadable format that can only be decrypted by authorized individuals
Wondering about hardware vs software encryption? Learn the key differences to secure your business's sensitive data.
What full disk encryption is, how it works on Windows, Mac, Linux, iPhone and Android, how it differs from file encryption, and how to roll it out.
Sichere Geräteverschlüsselung: Erfahren Sie, wie MDM Datenpannen verhindert und Ihre Compliance einfach aufrechterhält.
Turn off or suspend BitLocker on Windows 10 and 11, check if it is on, and handle a fleet without losing recovery keys or failing compliance.
BitLocker vs VeraCrypt: Which is best for enterprise encryption? Compare features, security, and management to choose the right fit.
What BitLocker drive encryption is, how TPM, PIN and recovery keys work, Windows 11 Home vs Pro, and how IT turns it on and keeps keys safe at scale.
How full disk encryption works on Linux with LUKS, how to turn it on at install or on an existing Ubuntu system, TPM unlock, recovery keys and performance.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients