



Explained
3 Key Differences Comparing Patches vs Updates
Compare patches vs updates in this blog post and discover why they are both crucial for your business.
How Windows patch management works: update types, a monthly process, Microsoft's tools, patching third-party apps, Windows Server, and compliance needs.

Content writer, trio.so
Patch management for Windows is the ongoing process of finding, prioritizing, testing and installing updates on Windows PCs and servers: the security and cumulative updates Microsoft releases on Patch Tuesday, feature updates, drivers, and the third-party apps that run on Windows. In practice it is a monthly cycle (inventory, scan, prioritize by risk, test, deploy in stages, verify, document), run with Microsoft's tools for the operating system and a separate tool for third-party apps, because none of Microsoft's update tools patches apps like Chrome, Adobe Acrobat or Zoom. WSUS, the update server many teams relied on, has been deprecated since September 2024, so a lot of teams are choosing new tooling right now.
If you keep a few dozen to a few hundred Windows PCs up to date and are working out what replaces WSUS or how to cover third-party apps, the process steps, the tools table and the server and compliance sections below are the parts to use.
If you already know what patch management is and you're here for the tools and server specifics, skip ahead to Types of Windows Updates.
Patch management for Windows is the process of identifying, acquiring, testing, and applying software updates to Windows operating systems and applications across an organization's device fleet. The scope is broader than most people assume: it covers OS-level security patches, cumulative updates, feature updates, driver and firmware updates, and third-party application updates running on Windows devices.
The stakes are not abstract. In Verizon's 2025 Data Breach Investigations Report, exploitation of vulnerabilities was the way in for 20% of breaches, a 34% rise on the previous year. IBM's Cost of a Data Breach Report 2026 puts the average breach at $4.99 million, a record high. Unpatched systems are where that exposure lives.
WannaCry made this concrete: Microsoft had issued the patch for the exploited vulnerability 59 days before the attack hit. Organizations that had applied it were unaffected. Those that hadn't paid for it. The process has specific steps, and the tools available to execute those steps have changed significantly in the last year.
Windows distributes updates in several distinct categories. Knowing the difference matters for prioritization, scheduling, and documentation in compliance audits.
A structured patch management for Windows process applies to both workstations and servers, but Windows Server patch management introduces additional constraints around uptime requirements, change control, and reboot risk that workstation patching does not carry. Platforms like trio.so centralize this process across mixed Windows fleets, connecting device inventory, policy enforcement, and compliance reporting in one console. You can read more about what that looks like in practice on trio.so's patch management product page.
You cannot patch what you don't know about. Maintain a current list of all endpoints, servers, OS versions, and installed software. Practitioners note that asset discovery is the step organizations most often skip, and the one that creates the most audit failures when gaps surface.
Regularly scan all devices against current CVE databases to identify unpatched vulnerabilities. Verizon's 2025 report found that organizations took a median of 32 days to fix vulnerabilities in edge devices such as VPNs and firewalls, and fully fixed only about 54% of them during the year. The scan is what starts that clock: you can't reduce a number you're not measuring.
Do not apply patches in the order Microsoft releases them. Prioritize by CVSS severity score, whether the CVE appears on the CISA Known Exploited Vulnerabilities (KEV) catalog, system criticality, and network exposure. Organizations that patch against audit deadlines rather than actual risk are optimizing for the wrong outcome.
The organizational barrier here is usually a risk-tolerance conversation with leadership that hasn't happened yet. Name it, and don't try to solve it in your patch policy alone.
Deploy to a canary ring of 5 to 10 devices first. For servers, the canary ring should be non-critical systems only, never a production server that is a single point of failure. If a patch breaks something in your canary ring, check whether the issue is listed in Microsoft's known issues list on the Windows release health dashboard before rolling back entirely.
Stage deployment in sequence: Canary (5 to 10 devices) → Early Adopter (~10 to 15% of fleet) → Broad Deployment (remaining workstations) → Production Servers (last, with the longest dwell time and change-controlled maintenance windows). A common approach in admin communities such as r/sysadmin is to wait about two weeks after Patch Tuesday before broad deployment, so community-reported issues can surface first.
Ring-based deployment is the professional answer to the "patch now vs. wait" dilemma. It is not a reason to delay indefinitely; it lets you move quickly on non-critical systems while giving production workloads a safer buffer. Since April 2025, Windows Autopatch has also been available with Microsoft 365 Business Premium and A3 or higher licenses, and it can deliver hotpatch updates to Windows 11 devices, which brings managed update rings within reach of more Intune shops.
One second-order effect worth planning for: when you first introduce ring-based deployment, helpdesk ticket volume will temporarily increase from the Early Adopter ring. Plan support capacity for the first two cycles before you roll it out broadly.
After deployment, confirm installation via compliance reports, not just deployment status. A patch can show as "installed" while the device hasn't rebooted to complete the installation. If your reporting shows a device as compliant but you're not seeing the expected security baseline, check whether a pending reboot is blocking the patch from activating.
Plan rollback before you deploy, not after something breaks. For Windows cumulative updates, rollback is possible but time-limited. For servers, rollback should be documented in the change management ticket before the maintenance window opens, not decided on the fly at 2am.
Maintain timestamped records of what was patched, when, on which devices, and by whom. PCI DSS, SOC 2, and ISO 27001 all require this documentation, and it also helps you trace the timeline faster when an incident occurs. Windows Server patch management specifically requires server-level documentation that workstation tooling doesn't always generate automatically.
Microsoft's native tool ecosystem has shifted significantly. WSUS was deprecated in September 2024, and the replacement picture is intentionally distributed across multiple products depending on your environment. No single Microsoft native tool covers everything WSUS covered. The r/sysadmin community has been actively working through this, and the frustration is real, because there is no clean one-to-one replacement. These are the Windows patching tools Microsoft currently offers.
WSUS is Microsoft's legacy on-premises update management server. As of September 20, 2024, WSUS is officially deprecated: no new features will be added. The role remains available in Windows Server 2025 and still publishes updates, and Microsoft has not announced an end date. WSUS still works. You have time to plan the migration. But the clock is running, and Microsoft's investment is going elsewhere.
WUfB is a cloud policy-based update management service integrated with Microsoft Intune. It uses Deployment Rings natively and requires no on-premises infrastructure. Microsoft has been folding the Windows Update for Business deployment service into Windows Autopatch, so newer Intune screens and documentation often use the Autopatch name for the same kind of update policies.
Autopatch is a service layered on Intune that automates update ring management without requiring manual admin scheduling each month.
MECM is Microsoft's on-premises and hybrid update management platform. With a third-party catalog integration like Patch My PC, it can extend to third-party application patching.
Azure Update Manager is Microsoft's cloud-based service for managing Windows and Linux updates across Azure VMs and on-premises systems connected via Azure Arc.
Which Microsoft native tool should you use?
Intune-managed workstations → Windows Update for Business or Windows Autopatch
On-premises servers with existing SCCM/AD infrastructure → MECM with Intune co-management, or Azure Update Manager with Azure Arc
Still on WSUS and not ready to migrate → Stay on WSUS for now, but start evaluating Azure Update Manager or a third-party tool; plan migration within 12 to 18 months
Not sure? → If your environment is mixed (some cloud, some on-prem, some remote workers), no single Microsoft native tool covers everything. This is where third-party patch management platforms fill the gap.
None of the native tools above natively patches third-party applications like Chrome, Firefox, or Adobe Acrobat. Organizations managing a full Windows device fleet, beyond OS-level updates alone, often look beyond native tools to a comprehensive Windows device management platform.
| Tool | Covers | Server Support | Third-Party Apps | Requires | Cost |
|---|---|---|---|---|---|
| WSUS | Windows OS + Microsoft products | Yes (on-prem) | No | On-prem Windows Server | Free (included) |
| Windows Update for Business | Quality + feature updates, drivers | Limited | No | Intune / Microsoft 365 | Free with Windows Pro/Ent |
| Windows Autopatch | Quality + feature updates, Edge, Teams | No | No | Intune + license tier | Included in qualifying M365 licenses |
| MECM / SCCM | Windows OS + 3rd party (via catalog) | Yes (on-prem/hybrid) | Yes (with catalog) | On-prem infrastructure (WSUS for on-prem SUP; not required in cloud-connected mode) | Included in M365 E3/E5 or separate |
| Azure Update Manager | Windows + Linux across Azure, Arc | Yes (cloud + Arc) | No | Azure Arc for on-prem | Free (Azure VMs); $5/server/month (Arc) |
Microsoft's native tools (WSUS, Windows Update for Business and Windows Autopatch) are scoped for OS and Microsoft product updates. They do not natively patch third-party applications. That means Chrome, Firefox, Adobe Acrobat, Java, 7-Zip, VLC, Zoom, Slack, and every other non-Microsoft application on your Windows fleet is outside their scope.
There are three realistic paths for closing that gap: MECM/SCCM with a third-party catalog integration (such as Patch My PC), a standalone third-party patch management tool, or a full UEM/MDM/RMM platform that includes software deployment. This is where dedicated Windows patch management software fills a role that Microsoft's native stack cannot. One second-order effect worth flagging: if you add a third-party patch catalog to MECM/SCCM, your update approval workflow doubles in complexity, so plan for that admin overhead before committing to that path.
The quality of third-party patching support varies significantly across tools: wrong versions, silent failures, and unreliable rollback are the failure modes practitioners consistently report. It is the first thing to probe in any tool evaluation. Unpatched third-party apps carry the same compliance liability as unpatched OS vulnerabilities, and auditors are increasingly aware of the distinction.
Patching a workstation and patching a production database server are not the same conversation. Servers have uptime requirements that workstations don't. A patch that forces an unplanned reboot on a domain controller or SQL Server can cause more disruption than the vulnerability it was meant to fix.
A few server-specific practices that are non-negotiable in mid-market environments: critical servers (domain controllers, SQL servers and other single points of failure) should only receive patches during change-controlled maintenance windows. Server rings must be separate from workstation rings, with non-critical servers going first and production servers last. A common rule of thumb in admin communities: security patches that don't require a reboot can install immediately on non-critical systems; critical production servers install only during scheduled maintenance.
Windows Server 2025 on-premises hotpatching via Azure Arc is now a paid option at $1.50/CPU core/month (since July 2025), and it allows security patches to be applied without a system reboot. Baseline months still require a reboot quarterly, but the reduction in unplanned maintenance windows is real: Microsoft's own GM described it as potentially letting sysadmins "see their families on weekends." The second-order effect to plan for: enabling hotpatching brings your servers under Azure Arc management, which expands your monitoring and configuration management scope. Understand that scope before committing.
Windows 10 support ended October 14, 2025. Workstations still running Windows 10 after that date receive no security patches unless they are enrolled in Extended Security Updates (ESU). Organizations pay $61 per device for the first year, the price doubles each year, and coverage runs for up to three years. The consumer ESU program, free with PC settings sync or 1,000 Microsoft Rewards points or a one-time $30, covers personal PCs to October 12, 2027 and is not meant for business fleets. ESU buys time; migration planning is overdue. Automated patch management software for Windows has become standard practice in mid-market environments precisely because scheduling, ring management, and server-specific maintenance windows need to be configured once and enforced consistently.
Your patch management for Windows process needs documented deadlines, but deadlines alone don't make you secure. Some frameworks set specific patching timelines; others leave the timeline to you but expect a documented process and records. Here is what they actually say.
Organizations that optimize for audit deadlines rather than actual risk leave a gap between documented compliance and real security exposure, and that gap is where exposure concentrates. Risk-based prioritization using CVSS scores, KEV catalog status, and system criticality closes that gap. Meeting the deadline is necessary. Meeting the deadline on the highest-risk vulnerabilities first is the goal.
More patch management guides for IT teams
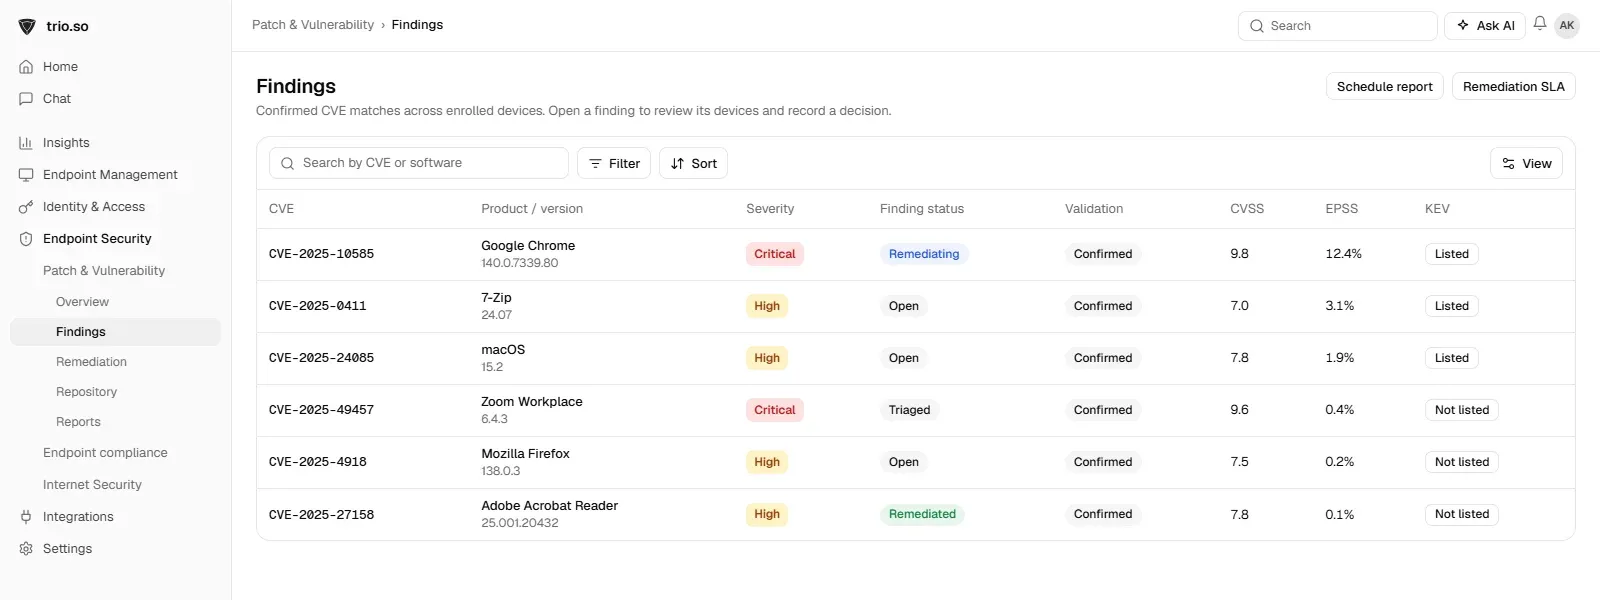
trio.so handles OS updates through Auto Patch policies and third-party fixes through remediation plans, and shows the result for each device. Its patch findings list every CVE found on your Windows PCs with its severity, CVSS and EPSS scores and whether it is in the CISA KEV catalog, so you can work through the riskiest fixes first, and each device gets a risk score from 0 to 100 based on its open findings.
The same console keeps an inventory of OS versions and installed apps for every device, deploys apps from its catalog or as MSI packages, controls which apps users may install with allow and block lists, and runs PowerShell scripts on enrolled Windows PCs, for example to apply a vendor workaround while a patch is in testing. Patch audit trails and compliance evidence export cover the records auditors ask for. Windows PCs sit next to macOS, iOS/iPadOS, Android and Linux devices in one console. Plans start at $5 per device. See patch management.
The ongoing process of finding, prioritizing, testing and installing updates for Windows and the apps that run on it, across all of an organization's PCs and servers, and keeping a record of what was patched and when.
At least monthly, in step with Patch Tuesday, with out-of-band fixes for actively exploited vulnerabilities as soon as they are tested. Critical fixes on internet-facing systems should go out within days, not weeks.
The second Tuesday of every month, when Microsoft releases its scheduled security and quality updates for Windows and other Microsoft products.
Yes. Microsoft deprecated WSUS in September 2024. It still works and still ships in Windows Server 2025, but it gets no new features, so plan a move to Windows Autopatch, Azure Update Manager or a third-party tool.
Microsoft's update tools do not patch them, so use Configuration Manager with a third-party catalog, a standalone patching tool, or an endpoint management platform that finds vulnerable app versions and deploys the fixes.
Related reading: patch management, how to disable Windows Update and software distribution strategy.
trio.so handles OS updates through Auto Patch policies and third-party fixes through remediation plans, and shows the result for each device.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Compare patches vs updates in this blog post and discover why they are both crucial for your business.
What software distribution is, the main types, and how to build a software distribution strategy for company devices, with real examples.
How macOS patch management works: enforcing updates with Declarative Device Management, patching third-party Mac apps and checking every Mac is current.
The blog explores the significance of security patches, their various forms, and their crucial role in fortifying digital defenses against cyber threats.
Patch management strengthens IT by creating an up-to-date environment. Solving system vulnerabilities to prevent catastrophic data breaches.
Automated patching for managed devices: how it cuts patch delays and manual work, which deadlines frameworks set, and how trio.so schedules and enforces OS updates.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients