



Explained
RMM vs MDM: Which One Does Your Business Need?
RMM vs MDM: What’s the difference? RMM manages IT infrastructure, while MDM secures and controls mobile devices.
Six ways to lock a Windows PC remotely, why Intune Remote lock is greyed out for Windows, and what to do instead when a company laptop goes missing.

Content writer, trio.so
You can lock a Windows PC remotely with Find my device at account.microsoft.com/devices, if the PC is signed in with a Microsoft account and Find my device was turned on beforehand. For company PCs there is a catch: Microsoft Intune's Remote lock action supports Android, iPhone, iPad and Mac but not Windows, which is why the button is greyed out for Windows devices. On Windows you use other tools instead: disconnect the user's session from the network, push a script through your MDM, force BitLocker recovery for a laptop that must not be used again, or wipe it. Whichever you use, the PC has to be online to receive it, and BitLocker encryption is what protects the data while it is not.
If a company laptop just went missing or someone left with one, find your situation in the six methods below; if you are planning ahead, the policies section covers what to set up now.
If you already know the difference between a lock, a wipe and disabling an account, skip to the methods.
Locking a PC remotely sends it back to the lock or sign-in screen, so someone has to enter the password or PIN to continue. It does not shut the PC down, erase it or disable the account. Those are different actions:
Every method below needs the PC to be on and reachable. If it is off or offline, the command waits or never arrives. BitLocker full-disk encryption is what protects the data in that time, so lock and encryption belong together.
Three questions decide the method: is the PC signed in with a Microsoft account, is it on your network or VPN, and is it enrolled in an MDM? Pick the method that matches; you do not need all six.
The fastest option for a PC signed in with a Microsoft account and connected to the internet.
Setup (before anything goes missing):
To lock it:
Limits: it needs a Microsoft account that is an administrator on the PC, it must be turned on before the loss, and location services must be on. It does not work for local or domain-only accounts, and many company setups leave it off.
Since December 2025, Microsoft's Link to Windows app for Android can lock a paired Windows 11 PC.
Limits: it needs a phone paired with the PC beforehand, it is meant for a person locking their own PC, and locking also disconnects the phone until the PC is signed in again. It is not an admin tool for a fleet.
When the PC is on your network or VPN and you have admin rights on it, you can disconnect the signed-in user's session. A disconnected console session goes back to the lock screen, and the user's apps keep running.
query session /server:TARGETPC
tsdiscon <SessionID> /server:TARGETPC
The first command lists the sessions on the PC; use the ID of the active console session in the second. To end the session instead, which closes the user's apps, use logoff <SessionID> /server:TARGETPC.
A common mistake: calling the Windows lock function (LockWorkStation, or rundll32.exe user32.dll,LockWorkStation) through Invoke-Command or PsExec. Those run in a separate, non-interactive session, so the command reports success but the user's desktop does not lock. The lock function only works when it runs in the signed-in user's own session, for example from a scheduled task that runs as that user.
Limits: it needs network or VPN access to the PC, admin rights, and remote administration allowed through the PC's firewall. It does not reach laptops that are off the network.
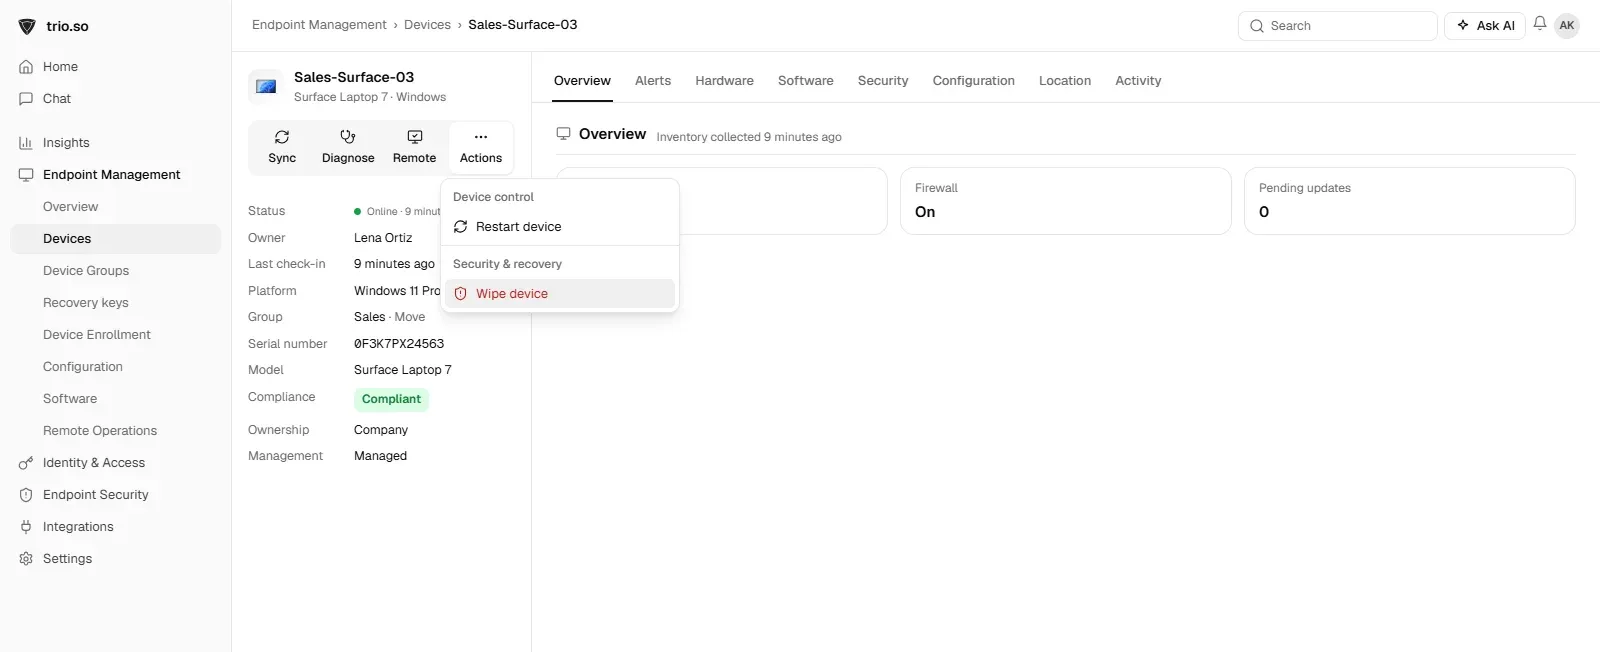
Intune's Remote lock is greyed out for Windows because it does not support Windows. Microsoft lists Remote lock for Android Enterprise company-owned devices, Android Open Source Project devices, iOS and iPadOS, macOS and visionOS, and not for Windows 10 or 11. It is a platform limit, not a missing permission or a licence issue.
What Intune admins do instead:
All of these need the PC to check in with Intune to receive the command.
A screen lock is the wrong tool when someone has left the company with a laptop and still knows the password. Forcing BitLocker recovery restarts the PC to the BitLocker recovery screen, which asks for the 48-digit recovery key. Without that key, which IT holds, the PC cannot start Windows.
manage-bde -forcerecovery C:
shutdown /r /t 0
Run it remotely through your MDM's script tool, or over the network with an admin session. Pair it with disabling the user's account in your directory.
Limits: BitLocker must already be on, the PC restarts, and it can only be undone with the recovery key. Make sure the key is stored before you run it, in your MDM, Microsoft Entra ID or Active Directory.
Methods 3 and 5 work for one PC on the network. For a fleet of laptops that rarely come to the office, you need the same actions from a central console, over the internet. An MDM that runs scripts on enrolled Windows PCs can send the BitLocker recovery script, sign the user out or run your own lock script in the user's session, without a VPN.
Limits: the PCs must be enrolled before anything goes missing, the PC must be online to receive the script, and an MDM subscription is needed. Check that your MDM can run scripts on demand, not only on a schedule.
| Method | Works off the network? | Needs setup in advance? | Cost | Best for |
|---|---|---|---|---|
| Find my device | Yes, over the internet | Yes: turned on, Microsoft account | Free | A PC signed in with a Microsoft account |
| Link to Windows Lock PC | Yes, through the phone | Yes: phone paired, remote PC controls on | Free | A person locking their own PC |
| Disconnect the session (tsdiscon) | No, needs network or VPN | Yes: admin rights, remote administration allowed | Free | Domain PCs in the office |
| Intune: account disable and scripts | Yes | Yes: enrolled, scripts ready | Intune licence | Intune-managed fleets |
| BitLocker recovery | Yes, through an MDM script | Yes: BitLocker on, key stored | Free | A leaver's laptop that must not be used again |
| MDM script | Yes | Yes: enrolled | MDM subscription | Fleets of remote laptops |
Remote lock only happens after someone notices a problem. An inactivity lock happens every time, with nobody involved. PCI DSS v4.0 requirement 8.2.8 asks for users to re-authenticate after 15 minutes of inactivity, and NIST SP 800-171 and CMMC require a session lock after a set period of inactivity; 15 minutes is the common choice.
With Group Policy: Computer Configuration > Windows Settings > Security Settings > Local Policies > Security Options > "Interactive logon: Machine inactivity limit", set to 900 seconds. For laptops that never reach the office network, apply the same setting through your MDM.
If a screen saver lock is set to a shorter time than the machine inactivity limit, the PC locks at the shorter time. That is fine for security; just do not assume the 15-minute setting is the one in control.
Every method here needs the PC to be reachable. A stolen laptop that is switched off may never receive anything. What protects it then is what was set up before: BitLocker encryption with the recovery key stored by IT, a strong sign-in, and accounts you can disable centrally. IBM's 2026 Cost of a Data Breach report put the average breach at $4.99 million worldwide; encrypting every company laptop is the control that keeps a lost device from becoming one.
So when a PC goes missing: disable the user's account and sessions, send a lock or BitLocker recovery if the PC is online, and wipe it if it will not come back.
For phones, the approach is different; see how to remote lock a device.
trio.so does not lock Windows PCs remotely; its lock action covers Android, Apple and Linux devices. On Windows, it enforces BitLocker and shows the encryption status of each PC, keeps BitLocker recovery keys in the console, runs scripts on enrolled Windows PCs, and wipes company-owned Windows PCs that will not come back. See Windows device management.
Related reading: remote wipe on Windows, BitLocker vs VeraCrypt, IT offboarding checklist and terminated employee email policy.
trio.so enforces BitLocker, keeps recovery keys in the console and wipes company-owned Windows PCs that will not come back.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Related
The related industry news, interviews, technologies, and resources.
RMM vs MDM: What’s the difference? RMM manages IT infrastructure, while MDM secures and controls mobile devices.
Lock a lost iPhone remotely with Find My and Lost Mode: what it does, whether it can be unlocked, how to turn it off, and how IT locks company iPhones.
Lock a lost Android phone remotely with Find Hub, and how IT admins lock company phones with MDM. Steps, limits, and next steps.
How to control an iPhone remotely with FaceTime or screen sharing, what "This iPhone is managed remotely" means, and the remote actions MDM allows.
What is remote control for Android and how can it help your business? Discover tools, benefits, and setup tips in this guide.
Are you applying remote disk management best practices? Find out how to transform your IT infrastructure with proactive storage solutions.
Shut down or restart a Mac remotely with Terminal and SSH, Screen Sharing or your iPhone, and what to check before you restart a Mac you cannot reach.
Run a command prompt on a remote computer with PsExec, Enter-PSSession and Invoke-Command. Setup, fixes for access denied, and the security risks to watch.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients