



How-Tos
Remote Wipe Windows 10 and 11: How to Erase a Lost Laptop
How to remotely wipe a Windows 10 or 11 laptop: the MDM wipe options, Intune Wipe vs Retire, what happens offline, and why BitLocker matters first.
How IT installs, updates and controls apps on Windows PCs: deployment methods, Microsoft's tools, app control and patching third-party apps.

Content writer, trio.so
Windows application management is how IT installs, updates, controls and removes the apps on a fleet of Windows PCs from one place, instead of setting up each machine by hand. It covers four jobs: deploying apps (MSI, MSIX, Microsoft Store and installer packages), keeping them patched, controlling which apps may run, and keeping an inventory of what is installed where. For a handful of PCs, the Settings app and winget are enough; for a fleet, teams use a device management (MDM or UEM) tool, Microsoft Intune or Configuration Manager.
If you manage the apps on a few dozen to a few hundred Windows laptops and want to know which methods and tools fit, this guide covers the components, Microsoft's own tools, best practices and how to control what runs.
Windows application management (sometimes called a Windows application manager or app manager for Windows) is the process and tooling IT uses to look after software on company PCs: which apps each role gets, how they arrive, how they stay current, and how they come off when someone leaves. On a single PC, you manage apps in Settings > Apps > Installed apps. Across a fleet, the same jobs move to a central console so every PC in a role ends up with the same set of apps.
Windows 10 reached end of support on 14 October 2025, so new work should target Windows 11. The components are the same on both.
Installing apps without a technician at each desk. Common package types are MSI (the classic Windows Installer format), EXE installers with silent switches, MSIX (Microsoft's modern package format with clean install and removal), and Microsoft Store apps.
Keeping apps current. Store apps update themselves; desktop apps such as browsers, PDF readers and remote access tools need a patching process, because Windows Update only covers Windows and Microsoft products. See patch management for Windows.
A current list of every app and version on every PC, so you can answer "who still runs the old version?" in a minute. This is inventory, not application performance monitoring.
Matching installs to the licences you pay for, and reclaiming licences when people leave or stop using an app.
Deciding which apps may run, removing local admin rights, and keeping records of what is installed for audits.
Microsoft's cloud MDM deploys Win32 apps (packaged with its content prep tool), MSI line-of-business apps, Microsoft 365 Apps and Microsoft Store apps through its "Microsoft Store app (new)" type, which keeps Store apps updated automatically. Enterprise App Management, an add-on sold on its own or in the Intune Suite, adds a catalog of prepared third-party Win32 apps with optional auto-update.
Group Policy software installation can assign MSI packages to domain-joined PCs on the office network. Configuration Manager is Microsoft's on-premises tool for large fleets, with application models, detection rules and distribution points. Both work best for PCs that regularly reach the corporate network.
Cross-platform MDM and UEM tools deploy and patch Windows apps from the cloud, alongside Macs and phones, so PCs at home are covered without a VPN.
winget is Microsoft's command-line package manager, built into Windows 11. winget install, winget upgrade --all and winget list cover install, update and inventory for apps in its repository. It is handy for scripts and small fleets; it is not a full management console.
Scripts fill gaps: silent installs with custom options, cleanup of old versions, or a workaround while a patch is tested. Keep scripts in version control and sign them.
Microsoft retired the Microsoft Store for Business and Education. Store apps are now deployed through the Microsoft Store integration in Intune or another MDM, and winget can install Store apps from the command line.
App-V runs apps in a virtual bubble. The App-V client in Windows has a fixed extended support lifecycle, so treat it as a legacy option and prefer MSIX or standard installers for new packages.
| Method | Best for | Reaches remote PCs | Patches third-party apps |
|---|---|---|---|
| Settings and winget | A few PCs, scripting | Only with your own scripts | Partly, through winget upgrade |
| Group Policy | Domain PCs on the office network | No | No |
| Configuration Manager | Large on-premises fleets | With extra infrastructure | With a third-party catalog |
| Microsoft Intune | Microsoft 365 shops | Yes | With Enterprise App Management (add-on) |
| Cross-platform MDM | Mixed Windows, Mac and mobile fleets | Yes | Depends on the tool |
Use one format per app type, prefer MSI or MSIX with silent install switches, and record the install and uninstall commands for each package.
Release new apps and versions to IT and a pilot group first, then to everyone, so a broken update hits five PCs instead of five hundred.
Let your management tool collect installed apps and versions from every PC automatically, and review it monthly for unapproved software.
Patch browsers, PDF readers and other common targets automatically, ranked by severity and whether the flaw is being exploited.
Offer optional apps in a company portal so people can install approved tools without a ticket.
Check how many PCs installed each app and why the rest failed, and follow up weekly.
Match installed app versions against known vulnerabilities, so you know which apps need patching first.
Record each package, who owns it, which groups get it and why, so the next admin can maintain it.
Apps only reach PCs that are enrolled. Use Windows Autopilot or automatic enrollment when PCs join Microsoft Entra ID, so new PCs arrive managed. See Windows device enrollment.
Give admins only the console permissions they need, so not everyone who can see devices can push software to them.
Deployment decides what you install; application control decides what may run. On Windows, Microsoft offers App Control for Business (formerly Windows Defender Application Control), which enforces allow lists at the operating system level, and AppLocker, which sets rules by publisher, path or hash. MDM tools add their own allow and block lists. Combine application control with removing local admin rights, so users cannot simply install around it. See application whitelisting, application blacklisting and how to stop employees from installing software on Windows.
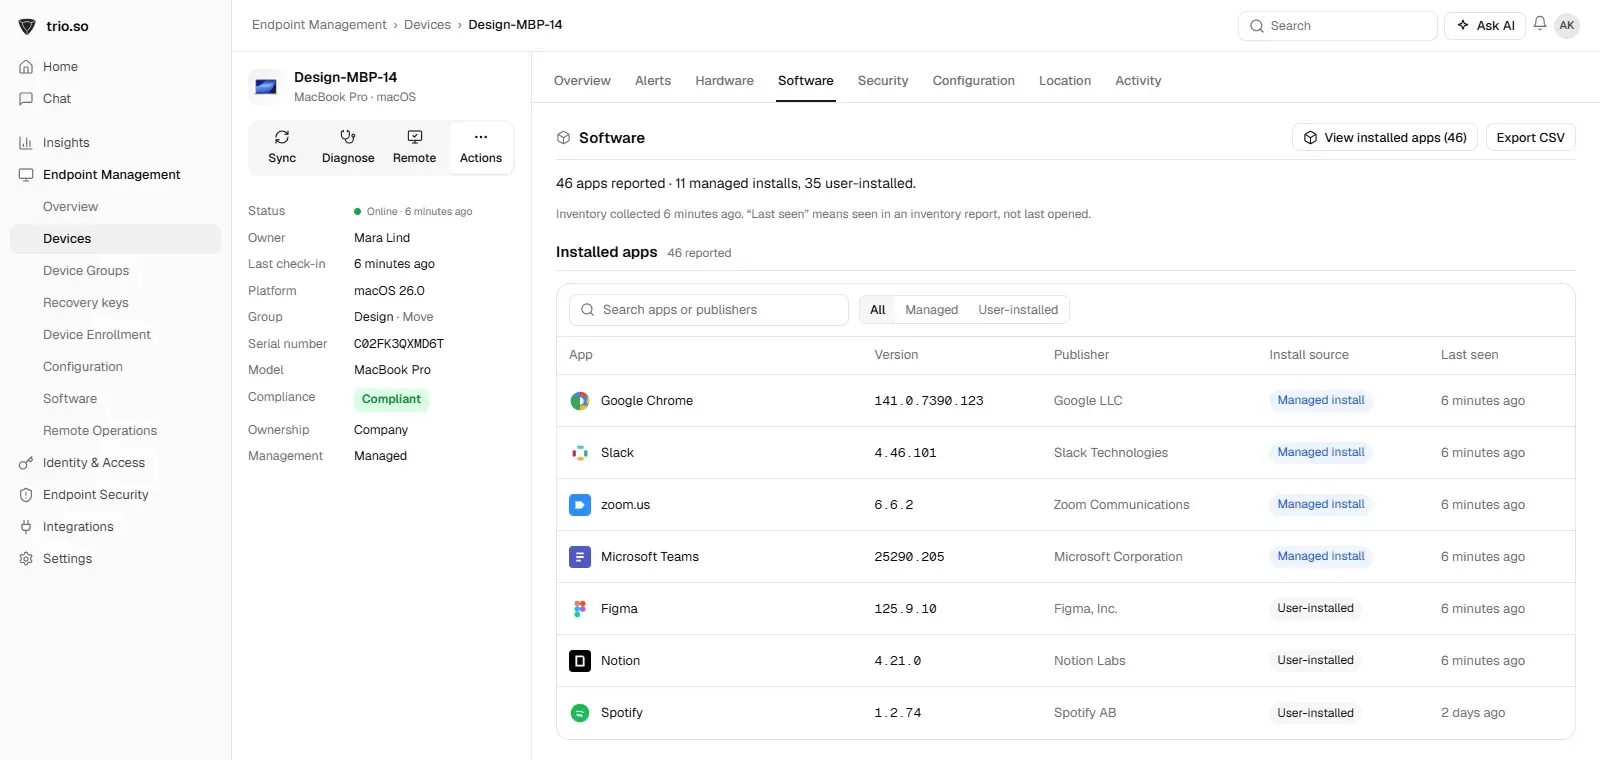
trio.so lists the installed apps on every Windows PC, deploys apps from its catalog or as MSI packages, and controls which apps may run with allow and block lists and an App Control for Business policy. Windows updates run through Auto Patch policies and third-party apps are fixed through remediation plans, PowerShell scripts run on enrolled PCs, and IT can open a remote desktop session to help a user. Plans start at $5 per device.
Installing, updating, controlling and removing apps across many Windows PCs from a central tool, with an inventory of what is installed where.
On one PC, use Settings > Apps > Installed apps or winget. Across a fleet, use an MDM, Intune or Configuration Manager to deploy, update and inventory apps centrally.
Package apps as MSI, MSIX or Store apps, deploy them from a management console to groups of PCs, and pilot each new version before releasing it to everyone.
Use App Control for Business or AppLocker policies, an MDM's block list, and remove local admin rights so users cannot install around the rules.
Microsoft retired the Microsoft Store for Business and Education. Store apps are now deployed through the Microsoft Store integration in Intune or another MDM, or with winget.
Related reading: software distribution strategy, patch management for Windows, how to deploy an application and application whitelisting.
trio.so deploys MSI and catalog apps, patches third-party software and blocks apps you do not allow. Plans start at $5 per device.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
How to remotely wipe a Windows 10 or 11 laptop: the MDM wipe options, Intune Wipe vs Retire, what happens offline, and why BitLocker matters first.

Fix "The Group Policy Client service failed the sign-in" and "Windows couldn't connect to the Group Policy Client service": service, permissions, repair.
What each PowerShell execution policy does, how to check and set it with Set-ExecutionPolicy, and how to fix "running scripts is disabled".
Tired of intrusive ads on Windows 10? Discover effective methods for how to block ads on Windows 10 and enhance your browsing experience.
Curious about patch management challenges? WSUS vs SCCM offers unique solutions for efficient updates and robust system security in your firm.
How to pause, delay or disable Windows Update on Windows 11 and 10 with Settings, Group Policy, the registry and services, and why IT should defer instead.
Intune vs SCCM compared: cloud vs on-premises, co-management, Configuration Manager's future, and which fits a small, mid-size or hybrid fleet.
How to delete a Windows service with sc delete or PowerShell, fix "marked for deletion", and what to check first. One PC or many.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients