



Explained
ISO 27001 Certification Cost: A Small Business Guide (2026)
What ISO 27001 certification costs a small business: the audit, preparation, tools and staff time, what drives each one, and how to keep the bill down.
ISO 27001 compliance software explained: what each tool type automates, what stays with your team, how to choose one, and where device management fits.

Content writer, trio.so
ISO 27001 compliance software is any tool that takes routine work out of running an information security management system (ISMS): collecting evidence, tracking tasks and policy reviews, keeping the risk register and Statement of Applicability in one place, and enforcing technical controls such as encryption and updates on company devices. It speeds up the mechanical work. It does not make the decisions the standard leaves to you, and no tool certifies you.
This guide sorts the tools into types, shows what each one automates and what stays with your team, explains how the 2022 version of the standard affects your choice, and covers the endpoint controls where automation pays off fastest.
In short
ISO/IEC 27001:2022 asks you to run a management system: set the scope, assess and treat risks, choose controls, monitor them, audit yourself and improve. Most of the effort is repeated work: chasing evidence, reminding control owners, keeping records current. That is what software is good at.
Vendors use the labels loosely, so it helps to sort products by the job they do:
| Tool type | What it automates | What stays a decision |
|---|---|---|
| ISMS and GRC platforms | Risk register, Statement of Applicability, control owners, tasks, internal audit and management review records | What is in scope, which risks you accept, which controls you exclude and why |
| Evidence integrations | Pulling settings and logs from cloud services, identity providers, HR and ticketing tools on a schedule | Whether the evidence actually shows the control works |
| Policy and training tools | Policy versions, approvals, acknowledgements, awareness training records | What the policies say and whether people follow them |
| Device management | Encryption, passcode and screen lock, OS updates, app rules, inventory, lost-device lock and company-device wipe, compliance evidence exports | Which device rules fit your risks, and how you handle personal devices |
| Security operations tools | Vulnerability scanning, logging, backup and malware protection for the controls they cover | How you respond to what they find |
Small teams don't always need a full platform. A shared drive for documents, a ticket queue for tasks and a device management tool for endpoint controls can carry a first certification. Larger or multi-framework programs get more from a platform that maps one control to several frameworks. Our broader guide to automated compliance software compares tools across frameworks.
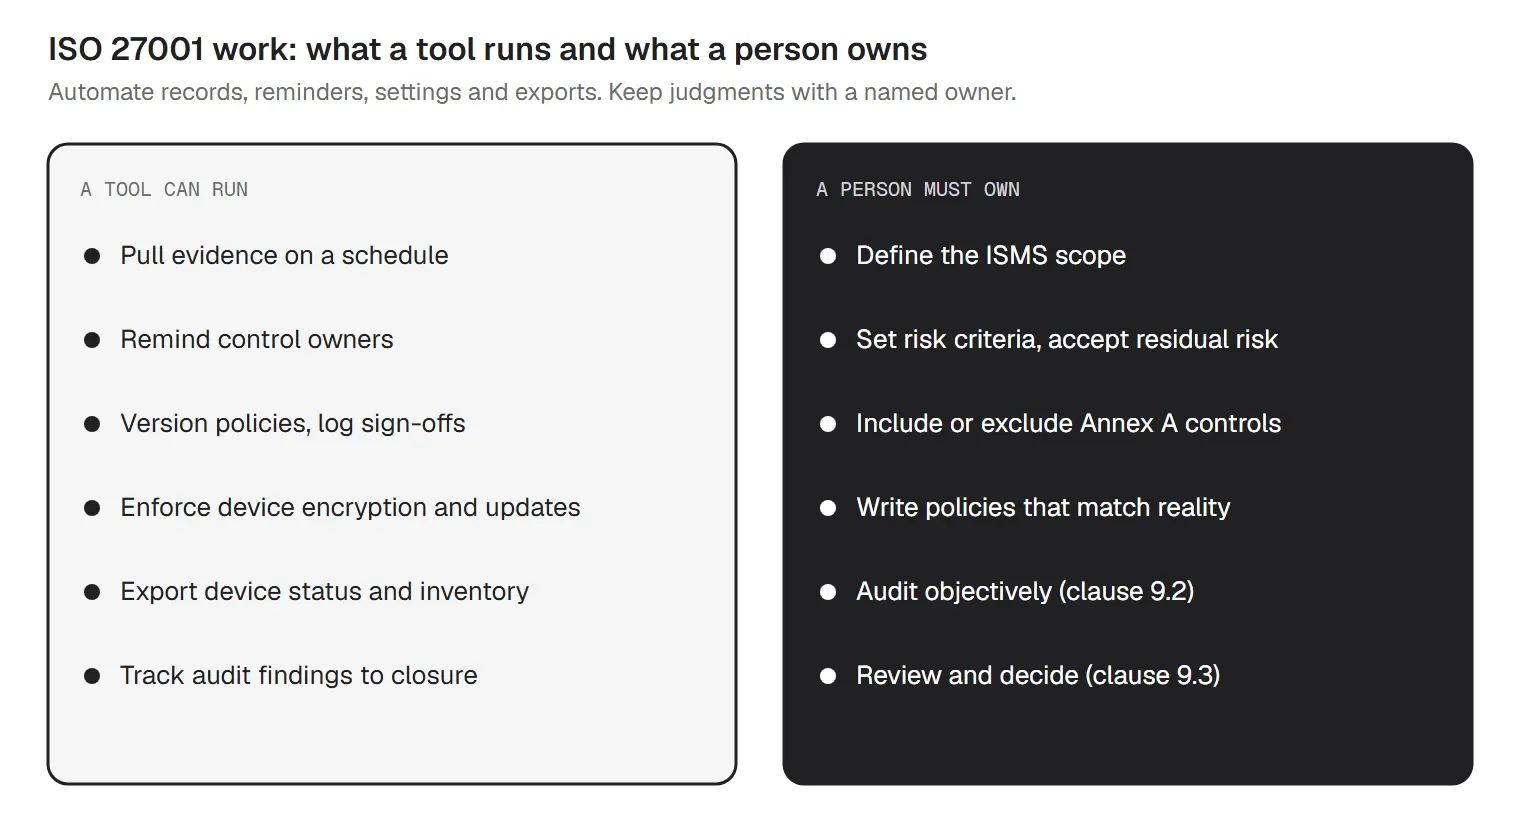
A useful rule: automate anything that is a record, a reminder, a setting or an export. Keep anything that is a judgment with a named person. Auditors interview people; a dashboard that says a clause is "complete" proves nothing on its own.
| Area | Automate | Keep with a person |
|---|---|---|
| Evidence collection | Scheduled pulls of settings, logs and reports | Deciding whether the evidence is enough |
| Risk register | Scoring, reminders, review dates | Risk criteria, risk owners, accepting residual risk |
| Statement of Applicability | Keeping it versioned and linked to controls | Including or excluding each Annex A control, with reasons |
| Policies | Versions, approvals, staff acknowledgements | Writing policies that match how you work |
| Internal audit | Scheduling, checklists, finding tracking | An objective, impartial auditor and their conclusions |
| Management review | Collecting inputs into one pack | Top management's decisions on changes and improvement |
| Device controls | Enforcing encryption, screen lock, updates and app rules; exporting status | Which device rules apply, and the rules for personal devices |
Be careful with automation percentages. Vendors measure different things, such as the share of evidence steps automated in a cloud-only company, and no independent source puts a reliable number on a whole ISMS. Judge a tool by the specific evidence it produces for your controls.
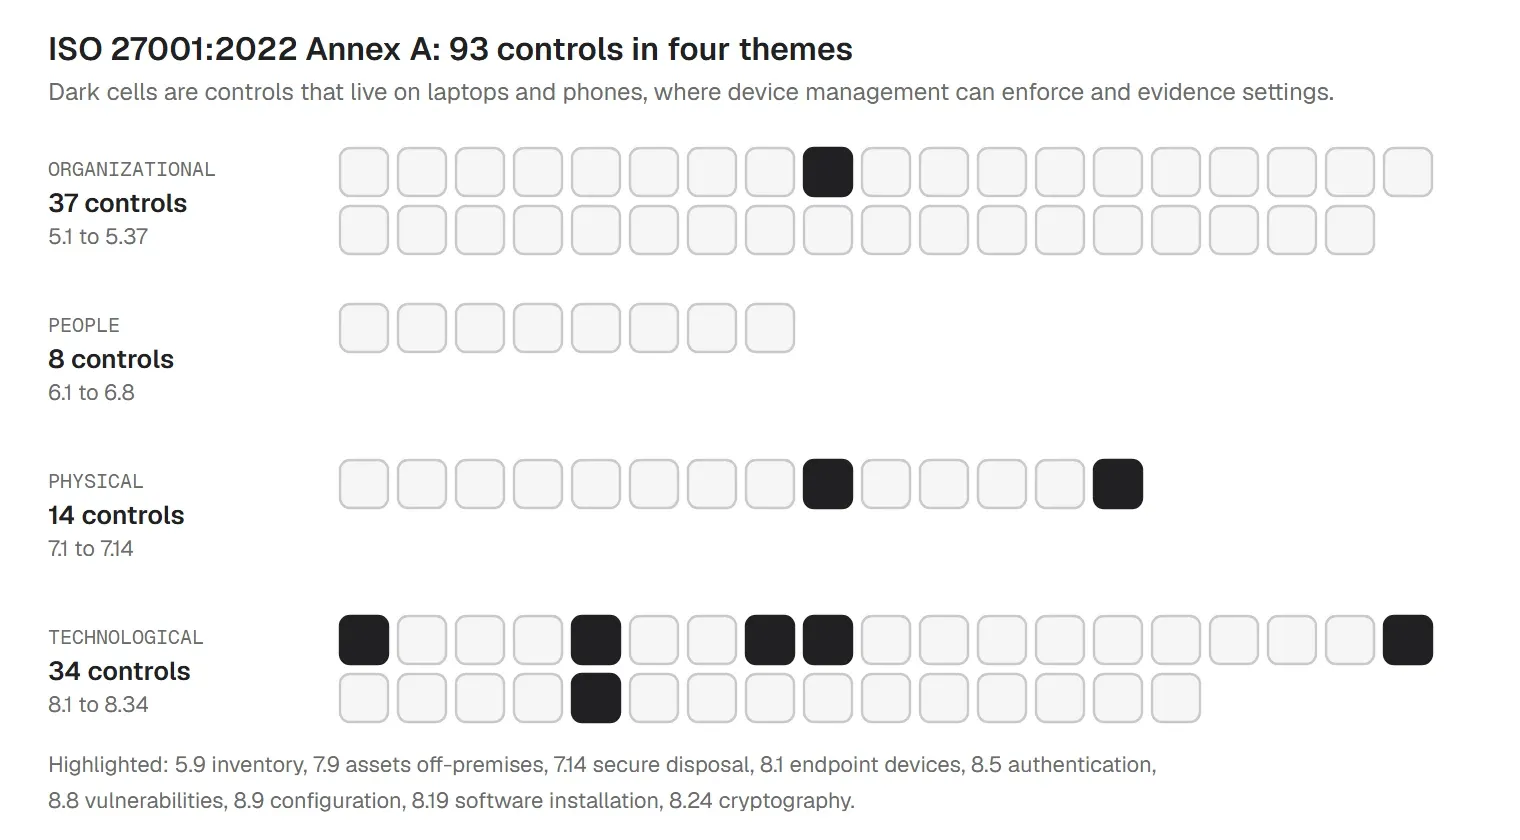
ISO/IEC 27001:2022 was published on 25 October 2022. Its Annex A has 93 controls in four themes, down from 114 controls in 14 clauses in the 2013 version: 11 controls are new, 24 were merged and 58 updated (IAF MD 26). The transition ended on 31 October 2025, when all 2013 certificates expired or were withdrawn. A 2024 amendment also asks you to decide whether climate change is relevant to your ISMS (Amd 1:2024); it adds no controls.
New controls that most often show up in tool evaluations:
Two checks for any tool: does its control library use the 2022 numbering, and are the new controls mapped and visible? If a tool still shows 14 control domains, it is running the 2013 structure.
Annex A 8.1 User endpoint devices is about protecting the information on the laptops, phones and tablets people use for work. The control does not list products. The organization picks its measures through risk treatment, and ISO/IEC 27002:2022 gives implementation guidance. Common measures for company laptops and phones include encryption, screen lock, OS updates, control over software installation, remote wipe of lost company devices and rules for personal devices. Malware protection (8.7) and vulnerability management (8.8) are separate controls.
Endpoint controls automate well because a device management tool applies the setting and records the result at the same time. Instead of collecting screenshots from each laptop, you export a report that shows which devices are encrypted, updated and locked down, and which are not.
| Annex A control | What trio.so can support |
|---|---|
| 5.9 Inventory of information and other associated assets | Hardware and software inventory for every enrolled device, exportable as evidence |
| 7.9 Security of assets off-premises | Encryption enforced wherever the device goes; lock for lost Macs, iPhones and Android devices |
| 7.14 Secure disposal or re-use of equipment | Remote wipe of company-owned devices before re-use or disposal |
| 8.1 User endpoint devices | Encryption, passcode and screen lock, OS updates and app rules applied by policy at enrollment |
| 8.5 Secure authentication | Passcode and screen-lock rules for unlocking the device (not app or system sign-in) |
| 8.8 Management of technical vulnerabilities | OS update management on Windows, macOS, iOS and Android |
| 8.9 Configuration management | Device settings enforced by policy and checked by the compliance engine's ISO 27001 framework |
| 8.19 Installation of software on operational systems | App allow and block lists |
| 8.24 Use of cryptography | BitLocker and FileVault (with FileVault recovery key escrow), plus phone encryption, with status per device |
For the full list of controls and how to plan them, use our ISO 27001 checklist.
| Check | Question to ask the vendor |
|---|---|
| 2022 control mapping | Show me the 2022 Annex A numbering and the new controls in your control library. |
| Your actual stack | Which of our systems do you connect to today, and what evidence does each connection produce? |
| Evidence format | Can an auditor read your exports without a login? Are they dated and attributable? |
| Multi-framework | If we also need SOC 2 or GDPR evidence, do you map a control once and reuse it? |
| Effort to run | Who on our side has to maintain the tool, and for how many hours a week? |
| Your data | Where do you store our data, which sub-processors do you use, and what security assurance can you show? |
More ISO 27001 guides for IT teams
trio.so is device management software. It supports the device-related Annex A controls you select: the ones that live on laptops and phones. Across Windows, Mac, iOS and Android, from one console, it lets you:
trio.so's compliance engine includes ISO 27001 among its frameworks and checks the device controls a management tool can enforce. It does not write your Statement of Applicability, risk register or policies, and it does not certify you: certification comes from a certification body, ideally an accredited one. Learn more about ISO 27001 compliance in trio.so and compliance automation.
14-day free trial. No credit card required.
More ISO 27001 guides: the ISO 27001 checklist, ISO 27001 certification cost for small businesses, ISO 27001 vs SOC 2, NIST vs ISO 27001 and the ISO 27701 checklist. For the encryption side, see full-disk encryption.
Sources. Last reviewed October 2026. This article is guidance, not legal or audit advice. ISO/IEC standards are copyrighted; control titles are cited, not quoted.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
What ISO 27001 certification costs a small business: the audit, preparation, tools and staff time, what drives each one, and how to keep the bill down.
An ISO 27701 checklist for the 2025 edition: what changed, who it is for, how it relates to ISO 27001 and GDPR, and the tasks a privacy program needs.
An ISO 27001 checklist for IT teams: clauses 4 to 10, all 93 Annex A controls with an SoA template, risk register and device controls. Free PDF and Excel.
SOC 2 compliance automation replaces manual evidence collection with continuous monitoring, cutting audit prep from 500 hours to roughly 170.
GDPR compliance software explained: the six main tool types, what each automates, what stays with people, and how Article 32 device controls fit in.
SOC 2 compliance risks for small businesses are real: audits fail, deals stall, and budgets blow. Learn what goes wrong and how to stay on track.
PCI compliance for small business under PCI DSS v4.0.1: merchant levels, which SAQ you need, what drives the cost, and how PCI fines work for merchants.
GDPR requirements for small and US businesses: who the law covers, the duties that apply, deadlines, fines and what you can skip. Free checklist.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients