



Explained
HIPAA Compliance & Cell Phones: PHI Security Rules
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
What ISO 27001 certification costs a small business: the audit, preparation, tools and staff time, what drives each one, and how to keep the bill down.

Content writer, trio.so
ISO 27001 certification cost for a small business comes down to four things: the certification body's audit, the work to build your information security management system (ISMS), any tools or outside help you buy, and your own team's time. The standard sets no price. What you pay depends mostly on how many people and sites fall inside your ISMS scope, how much of the security work you already do, and how much of the preparation you do yourself.
This guide explains each cost, what makes it go up or down, how the certification process runs over three years, and where small teams usually overspend. If you sell to larger customers, you have probably met the question in a security questionnaire: "Are you ISO 27001 certified?" This is what answering yes involves.
In short
ISO/IEC 27001:2022 sets requirements for an information security management system: a repeatable way to find your information security risks, decide how to treat them, and show that the measures work. Clauses 4 to 10 contain the requirements every certified organization must follow. Annex A lists 93 reference controls in four themes: 37 organizational, 8 people, 14 physical and 34 technological. You choose the controls you need through your risk assessment and record the decision in a Statement of Applicability.
Three facts matter for budgeting:
Certification is voluntary. ISO itself notes that some organizations use the standard without certifying. Small businesses often certify because customers ask for it.
We don't publish a price range here, because no primary source gives one and quotes vary widely by scope. What we can do is show what you are paying for, so you can compare quotes and plan a budget that holds up.
| Cost | What it covers | What drives it |
|---|---|---|
| Certification body audit | Stage 1 and Stage 2 audit days, plus surveillance and recertification audits later | Headcount in scope, number of sites, complexity of your systems |
| Preparation | Gap analysis, risk assessment, Statement of Applicability, policies, internal audit | How much security practice you already document; whether you hire a consultant |
| Tools | Compliance software, device management, backup, password manager, training platform | Which controls you need and what you already pay for |
| Internal time | A project lead, control owners, management review, staff training | Scope, how many gaps you find, how organized your evidence is |
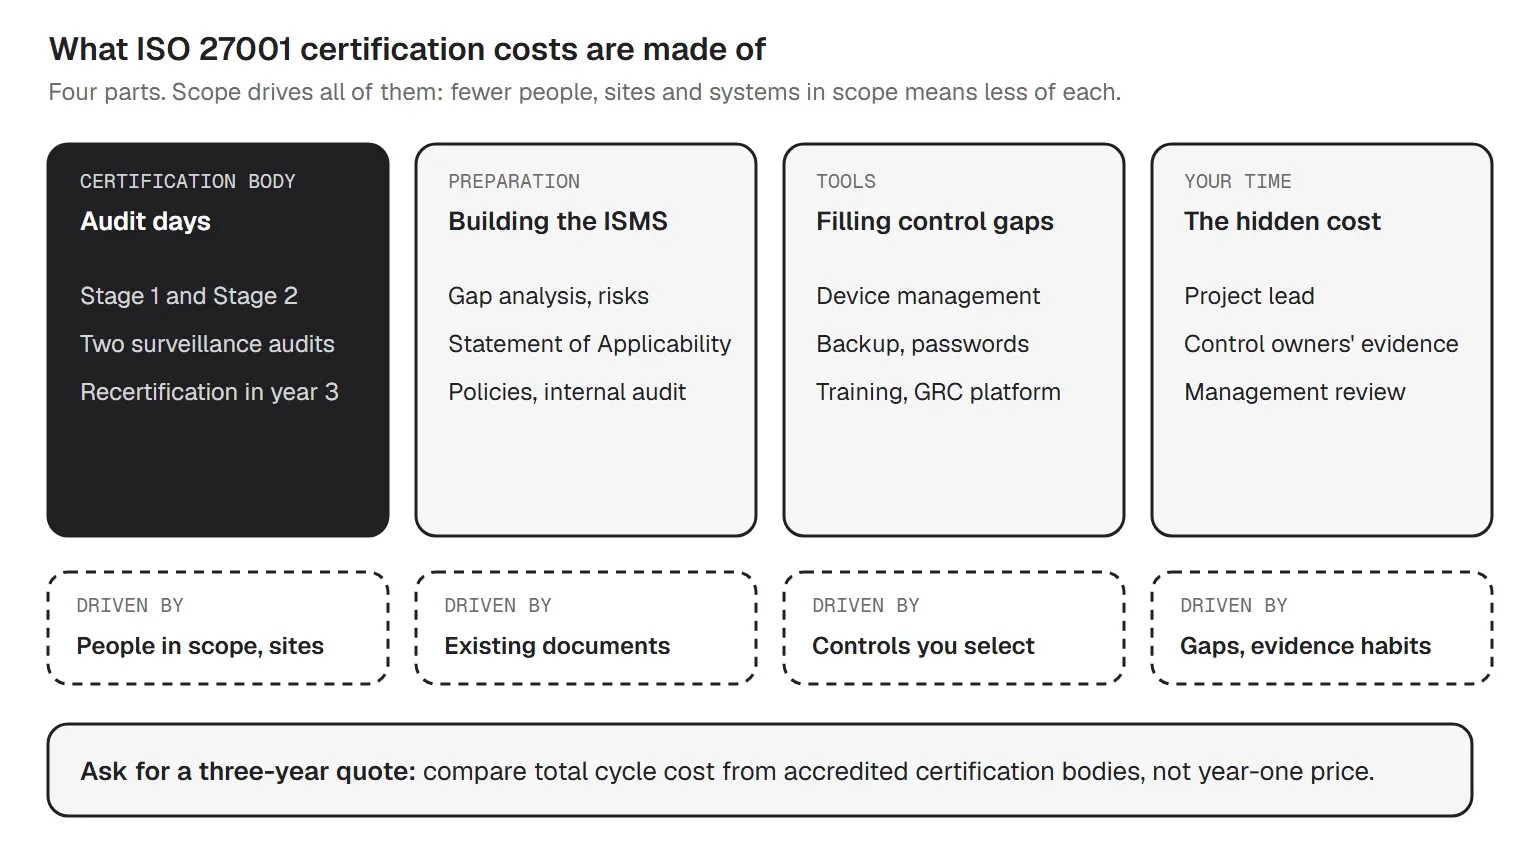
Certification bodies price the audit in auditor days. The minimum number of days is set by the rules certification bodies follow, ISO/IEC 27006-1:2024, and it depends mainly on the number of people working within your ISMS scope. A 15-person company with one office needs far fewer audit days than a 200-person company with three sites. Travel, the number of sites visited and how complex your systems are also change the quote.
Ask each certification body for a written quote that covers the whole three-year cycle: Stage 1, Stage 2, both surveillance audits and the recertification audit. A low first-year price can hide higher surveillance fees.
This is usually the largest part. You need a defined scope, a risk assessment and treatment process, a Statement of Applicability, an information security policy, objectives, evidence of competence, an internal audit and a management review. If your team already writes things down and runs regular access reviews, preparation is mostly documentation. If not, it means changing how work is done.
A consultant shortens the learning curve but costs more. Templates and a compliance platform cost less but need more of your own time. Many small teams mix the two: they do the work themselves and pay for a review before Stage 1.
You may not need new tools at all. Check what you already have against the controls you select. The gaps small companies most often fill are device management (encryption, updates, screen lock and inventory on laptops and phones), backup, a password manager and security awareness training. Our ISO 27001 compliance software guide covers what tools can and cannot do.
Someone has to own the project, and control owners have to produce evidence. This cost doesn't show up on an invoice, so it is easy to underestimate. Name the project lead early and protect time in their week for it.
The process follows the same path in every company. For the detailed task list, use our ISO 27001 checklist.
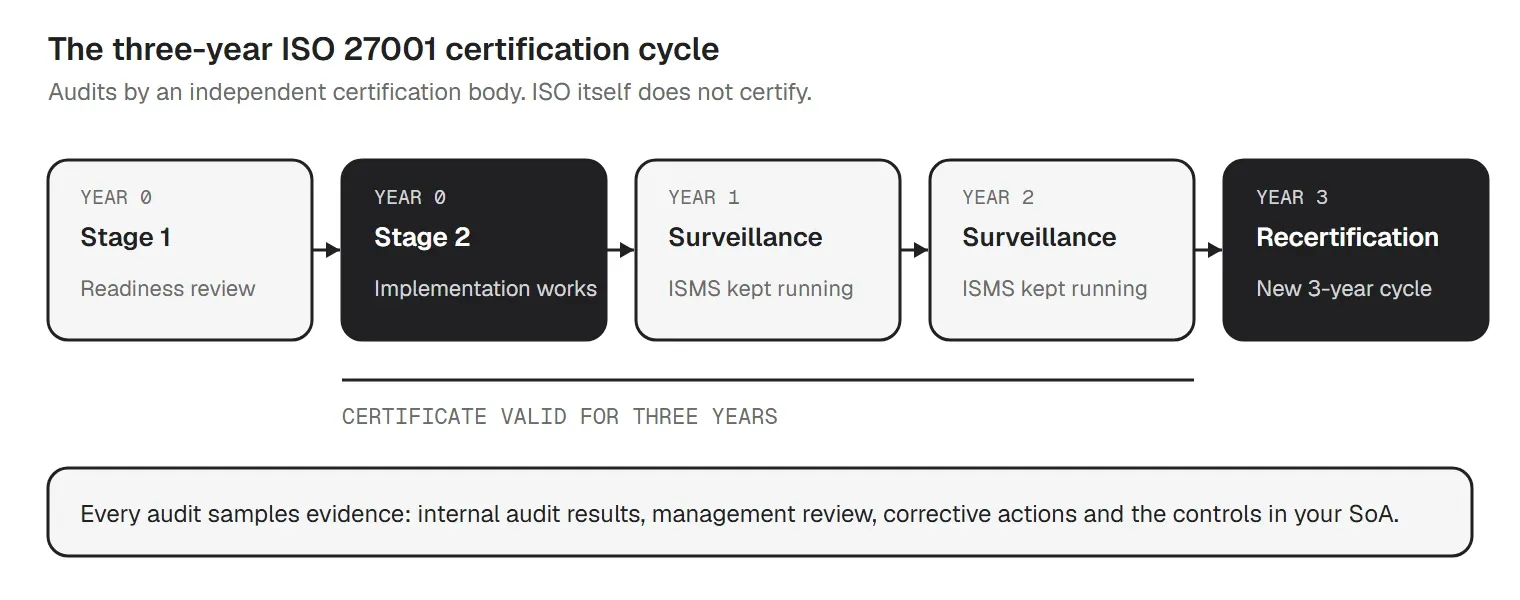
A certificate is valid for three years. Surveillance audits follow in each of the next two years, and a recertification audit takes place before the certificate expires. How long the first certification takes depends on your starting point; we don't quote a number because it varies too much to be useful.
ISO 27001 itself carries no fines: it is voluntary. The cost of not having it is commercial, in lost deals and longer security reviews. If you also handle personal data of people in the EU, much of the same work can be reused for GDPR (see the GDPR compliance checklist), though the two are separate obligations.
More ISO 27001 guides for IT teams
Device controls produce a lot of repeat evidence work. trio.so is device management software that supports the device-related Annex A controls you select. Across Windows, Mac, iOS and Android, from one console, it lets you:
| Annex A control | What trio.so can support |
|---|---|
| 5.9 Inventory of information and other associated assets | Hardware and software inventory for every enrolled device, exportable as evidence |
| 7.9 Security of assets off-premises | Encryption enforced wherever the device goes; lock for lost Macs, iPhones and Android devices |
| 7.14 Secure disposal or re-use of equipment | Remote wipe of company-owned devices before re-use or disposal |
| 8.1 User endpoint devices | Encryption, passcode and screen lock, OS updates and app rules applied by policy at enrollment |
| 8.5 Secure authentication | Passcode and screen-lock rules for unlocking the device (not app or system sign-in) |
| 8.8 Management of technical vulnerabilities | OS update management on Windows, macOS, iOS and Android |
| 8.9 Configuration management | Device settings enforced by policy and checked by the compliance engine's ISO 27001 framework |
| 8.19 Installation of software on operational systems | App allow and block lists |
| 8.24 Use of cryptography | BitLocker and FileVault (with FileVault recovery key escrow), plus phone encryption, with status per device |
trio.so's compliance engine includes ISO 27001 among its frameworks and checks the device controls a management tool can enforce. It does not write your Statement of Applicability, risk register or policies, and it does not certify you: certification comes from a certification body, ideally an accredited one. Learn more about compliance automation.
14-day free trial. No credit card required.
More ISO 27001 guides: the ISO 27001 checklist, ISO 27001 compliance software, ISO 27001 vs SOC 2, NIST vs ISO 27001 and the ISO 27701 checklist for privacy. For wider context, see compliance for SMBs.
Sources. Last reviewed October 2026. This article is guidance, not legal or audit advice. ISO/IEC standards are copyrighted; control titles are cited, not quoted.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
Which NCA ECC-2:2024 controls you can automate, which need people, how small teams should sequence tools, and where device management fits in the stack.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
NIST compliance automation tools by type: GRC platforms, NIST and CISA tools, scanners and device management. What each covers and what it can't.
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
ISO 27001 compliance software explained: what each tool type automates, what stays with your team, how to choose one, and where device management fits.
Explore HIPAA compliance automation capabilities, limitations, and implementation steps. Learn what you can automate and what needs human oversight.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients