



Explained
HIPAA Compliance & Cell Phones: PHI Security Rules
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
Which NCA ECC-2:2024 controls you can automate, which need people, how small teams should sequence tools, and where device management fits in the stack.

Content writer, trio.so
NCA's control sets have grown. ECC-2:2024 is the current version of the Essential Cybersecurity Controls for government entities and CNI operators, and since late 2025 NCNICC-1:2025 sets controls for private companies outside CNI. For IT teams already stretched thin, tracking 108 main controls across 4 domains by hand in spreadsheets is hard to keep up.
NCA compliance automation means using software to check, enforce and evidence ECC-2:2024 controls on a schedule, so the evidence is ready before the assessment instead of assembled under deadline. Most of that work sits in Domain 2, Cybersecurity Defense, which holds 61 of the 108 controls. That is where the bulk of your automatable effort lives, and where tooling returns the most.
Automation covers the repetitive technical work: configuration checks, policy enforcement, access reviews and evidence collection. Governance controls such as the strategy, the risk method, the committee charter and independent audits need human decisions. Tools can track those obligations and flag deadlines, but they cannot replace them.
This guide covers the ECC-2:2024 structure, which controls you can automate, how SMEs and startups should sequence their approach, what the tool landscape looks like, and how trio.so handles the endpoint layer.
In short
If you already know ECC-2:2024's domain structure, skip ahead to Which ECC-2:2024 Controls You Can (and Cannot) Automate.
ECC-2:2024 is built on 4 domains, 28 subdomains, 108 main controls and 92 subcontrols. That is a restructure of ECC-1:2018, which had 5 domains, 29 subdomains and 114 controls; its industrial control systems domain moved to NCA's OTCC. If your team or GRC tool was mapped to the old version, re-map it, because the controls did not carry over one to one. The Saudi staffing rule also widened: all cybersecurity positions, not just the head and critical roles, must be held by full-time, qualified Saudis.
ECC is not a certifiable standard. There is no badge or certificate at the end of an assessment; NCA checks compliance through self-assessment, reports from its compliance tool and field audit visits. Build your program around keeping controls in place and evidenced, not around a certificate.
Two NCA sets define who has which obligations. ECC-2:2024 applies to government agencies, their affiliated companies and entities inside and outside Saudi Arabia, and private entities that own, operate or host critical national infrastructure. The ECC itself states no penalty amounts; it rests on NCA's Statute and a High Order that require ongoing compliance.
NCNICC-1:2025 covers private companies outside CNI, as notified by NCA. Large entities (more than 250 staff or over SAR 200 million revenue) have 65 controls; small and medium entities (6 to 249 staff or SAR 3 to 200 million) have 26. For the full picture of who falls under which set, see our guide to NCA compliance.
Working through 108 controls is hard without a structured approach. Going domain by domain, starting with Domain 2 where automation carries the most weight, is where NCA compliance automation becomes the practical path.
Domain 2 holds 61 of ECC-2:2024's 108 controls, and many of them map to technical settings that software can enforce, check and evidence on a schedule. The aim is to cut manual work on the technical side so your team spends its time where judgment is needed. Choosing the right automated compliance software for your ECC program starts with knowing which controls are machine-friendly and which are not.
These seven areas are where automation tools do well across Domain 2.
1. Configuration Checks and Baseline Enforcement
2. Patch Management and Vulnerability Remediation
3. Evidence Collection and Audit Trails
4. Compliance Status Tracking
5. Identity and Access Policy Enforcement
6. Encryption and Device Security Policy Enforcement
7. Reporting and Compliance Dashboards
Which automation approach fits your organization?
Large organization (dedicated security team): a full GRC platform mapped to ECC-2:2024, with a SIEM and audit management.
Mid-size organization (small IT team): a stacked approach, with device management for the endpoint controls in Domain 2 plus a light GRC tool for evidence and governance tracking. trio.so's compliance engine includes an NCA ECC template that checks the device settings behind several Domain 2 controls in this model.
SME or startup (no dedicated security staff): start with device management for the technical controls and a self-assessment tool or spreadsheet for the procedural ones; move to a GRC platform as the program matures.
Not sure? Start with device management for the device controls in Domain 2. It gives you a baseline for those settings before you invest in broader GRC tooling.
Automation cannot replace governance, and mixing the two up leads to real gaps.
The right frame is not "automation is limited". Automation handles the large technical domain so your team's time goes to the decisions that need judgment. The tool does the checking; you make the calls.
| Tool type | ECC domains | What it automates | Best for | Limits |
|---|---|---|---|---|
| Device management (MDM/UEM) | Domain 2 (device controls) | Device inventory, encryption and screen-lock enforcement, OS update status, configuration checks, device evidence | Organizations with mixed laptop and mobile fleets | Does not cover governance documents, third-party risk or non-device controls |
| Dedicated GRC platform | All 4 domains (tracking) | Evidence collection, control mapping, audit trail, scoring, reporting | Large organizations that need full-framework tracking | Higher cost and setup; check that it is mapped to ECC-2:2024 |
| Vulnerability management tool | Domain 2 (2-10, part of 2-3) | Scanning, severity ratings, patch tracking | Teams prioritizing technical hygiene | No governance; evidence limited to vulnerability data |
| SIEM and log management | Domain 2 (2-12, 2-13) | Log collection, 12-month retention, event correlation | Organizations with an existing SOC | Not built for compliance tracking; evidence export needs extra work |
| IAM and PAM platform | Domain 2 (2-2) | Least privilege, MFA, privileged access, access reviews | Complex access requirements | Single-domain focus; no endpoint or evidence management |
| Self-assessment or light GRC tool | Domains 1 and 4 | Self-assessment records, procedural control tracking | SMEs that need a light governance layer | No technical automation; used alongside technical tools |
| AI-assisted compliance platform | All 4 domains | Gap analysis, policy drafting, vendor risk questionnaires | Teams wanting one platform | Newer category; maturity and claims vary, so check the control mappings |
| Stacked approach (device management + GRC) | All 4 domains | Device evidence plus governance evidence management | Mid-size organizations balancing coverage and cost | Two vendors and some integration work |
NCNICC-1:2025 brought small and medium private companies (6 to 249 staff, or SAR 3 to 200 million revenue) into NCA's scope, as notified by NCA. NCA compliance automation for a 40-person company looks different from a 500-person enterprise, and the approach should reflect that. You don't need to build every control on day one.
Start with an NCA compliance checklist to see your current gap before you buy any tool. The gap assessment tells you which controls are in place, which are missing and where your highest audit risk sits. That output drives the tool choice, not the other way round.
The small and medium tier has a reduced set: 26 controls in 13 sub-components, against 65 for large entities and 108 main controls in the ECC. Law-firm summaries say some of the small and medium controls are recommended rather than mandatory, so read the NCNICC text (Arabic is binding) and mark each control before you plan. The risk for smaller organizations is over-engineering: building the full ECC before the NCNICC controls that apply to you are solid.
Smaller teams run lean compliance programs, which is why sequencing tools by impact, not by framework order, matters. The real bottleneck is often internal sign-off on the budget before the first assessment date.
NCA compliance automation for startups works best in order of impact. With a small team and a limited budget:
A stacked approach, device management plus a light GRC or self-assessment tool, usually costs an SME less than a full enterprise GRC suite at this stage. If device results look inconsistent after you start, check whether all devices were enrolled before the first check ran; devices added later show gaps that may not be real failures.
The market for NCA compliance software has grown since ECC-2:2024 was published. Four tool categories serve most organizations, and knowing the differences helps you avoid buying the wrong layer first.
If you are moving from ECC-1:2018 tools, check whether your current tool has an ECC-2:2024 module. A tool still mapped to the old 5-domain framework will give you a misleading baseline, so re-run your gap assessment against the right version before you trust any automated score. The ECC is one part of a broader IT compliance program, and tools are best judged in that wider context. Banks that also follow SAMA's framework can read our SAMA compliance automation guide for the SAMA side.
trio.so supports NCA compliance automation at the device and endpoint layer: the Domain 2 controls that land on laptops, desktops, phones and tablets. It manages Windows, macOS, Linux, iOS, iPadOS and Android devices from one console, which suits the mixed fleets common in Saudi organizations, and the console is available in Arabic as well as English.
Here is what that covers in practice:
The same engine has templates for other frameworks, including ISO 27001, SOC 2, PCI DSS and NIST. In each case it checks device controls, not the governance layers of the framework.
The template checks device settings only. It does not cover the governance, network, logging, testing, physical, continuity or third-party controls, and trio.so does not assess or certify ECC compliance. For the governance side, pair it with a light GRC or self-assessment tool.
One expectation to set up front: the first time the compliance engine checks a fleet, it often shows configuration failures nobody knew about. Plan a fix-up sprint before you export your first evidence; that first check reflects your actual state, which may differ from what was assumed.
Per-device pricing suits small and medium companies starting under NCNICC-1:2025 without an enterprise budget. Plans start at $5 per device. Learn more about trio.so's approach to compliance automation.
14-day free trial. No credit card required.
More NCA and Saudi compliance guides for IT teams
Sources. Last reviewed October 2026 against ECC-2:2024, the current version on 27 October 2026. Control IDs and names are NCA's; every description is our own paraphrase, and the Arabic ECC text is binding. This article is guidance, not legal advice or an assessment. trio.so is not affiliated with or endorsed by NCA.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
NIST compliance automation tools by type: GRC platforms, NIST and CISA tools, scanners and device management. What each covers and what it can't.
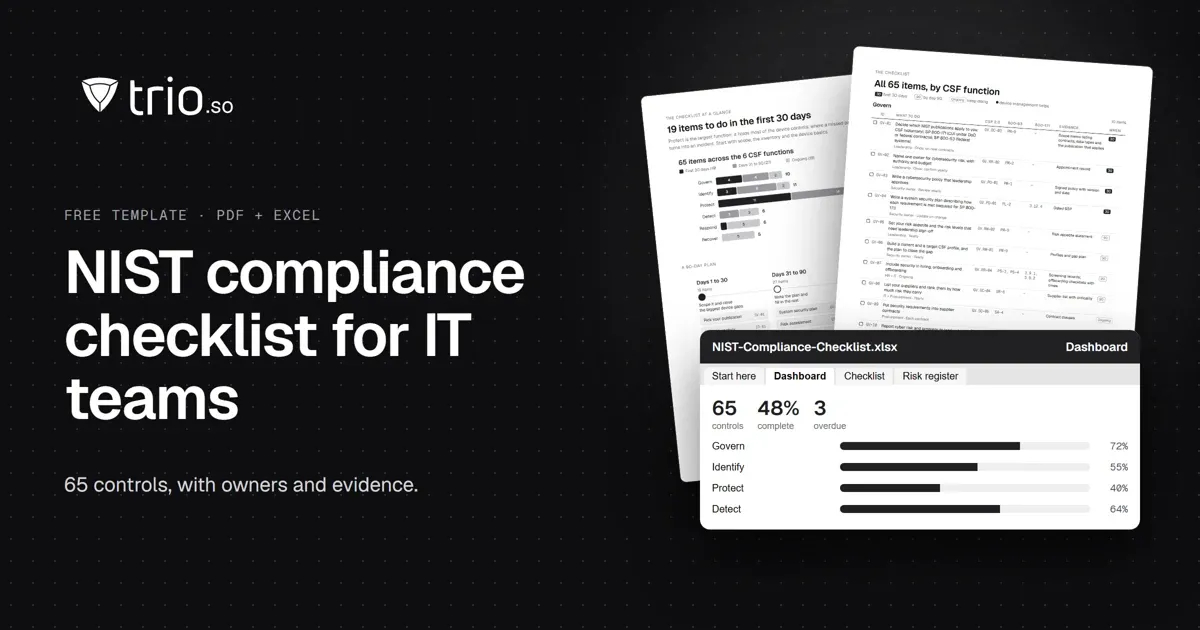
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
ISO 27001 compliance software explained: what each tool type automates, what stays with your team, how to choose one, and where device management fits.
Explore HIPAA compliance automation capabilities, limitations, and implementation steps. Learn what you can automate and what needs human oversight.
What ISO 27001 certification costs a small business: the audit, preparation, tools and staff time, what drives each one, and how to keep the bill down.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients