



Explained
HIPAA Compliance & Cell Phones: PHI Security Rules
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
NCA compliance explained: who must follow ECC-2:2024, the NCA framework family, NCNICC-1:2025, how NCA checks compliance and why there is no certificate.

Content writer, trio.so
NCA compliance means following the cybersecurity controls issued by Saudi Arabia's National Cybersecurity Authority (NCA). The core set is the Essential Cybersecurity Controls, ECC-2:2024, which binds government entities, their affiliated companies and private operators of critical national infrastructure (CNI). Private companies outside CNI have their own set, NCNICC-1:2025, and extra NCA sets cover cloud, telework, operational technology, critical systems, data and social media accounts.
This guide explains who must comply with which NCA requirements, how the framework family fits together, how NCA checks compliance and why there is no NCA certificate. It is written for IT and security leads at Saudi government bodies, banks and CNI operators.
In short
The National Cybersecurity Authority was set up by Royal Order No. 6801 in 1439H as the Kingdom's cybersecurity regulator. It issues binding control sets, policies and guidelines, and it checks that the entities in scope follow them. Article 10(3) of its Statute and High Order No. 57231 require those entities to keep "ongoing and continuous compliance", which is why NCA compliance is an ongoing program, not a one-off project.
NCA's documents are published in Arabic and English, and the Arabic version is binding. Everything lives on NCA's regulatory documents page; always check there for the latest version before you plan work.
Which NCA framework applies depends first on what your organization is, then on what it runs.
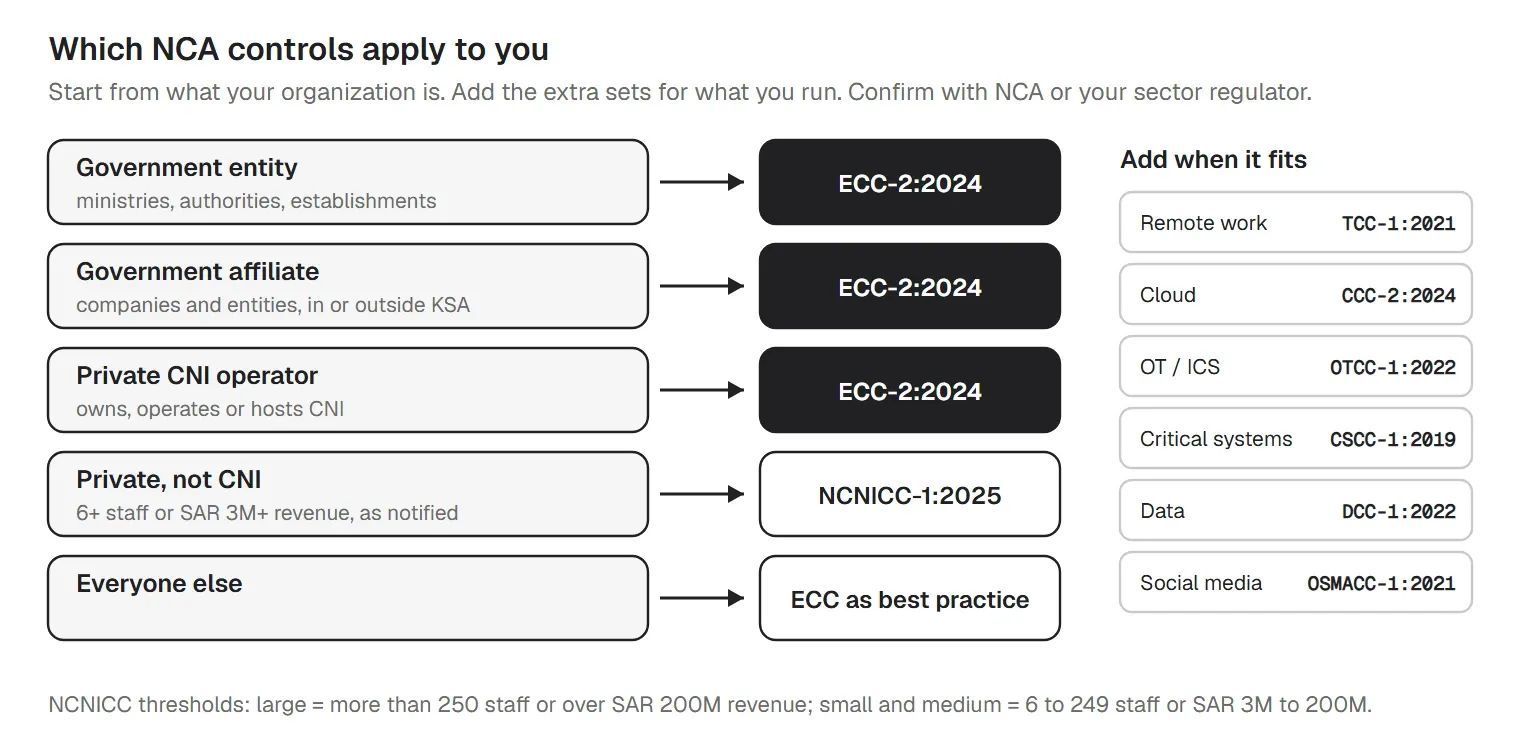
| Organization | Main NCA set | Notes |
|---|---|---|
| Government agency (ministry, authority, establishment) | ECC-2:2024 | Plus the extra sets for what it runs |
| Company or entity affiliated with a government agency | ECC-2:2024 | Inside or outside Saudi Arabia |
| Private entity that owns, operates or hosts CNI | ECC-2:2024 | Banks and other financial firms may also answer to SAMA |
| Private company outside CNI | NCNICC-1:2025 | Large or small and medium tier, as notified by NCA |
| Any other organization in the Kingdom | None mandatory | NCA strongly encourages the ECC as best practice |
Within ECC scope, you apply every control that is applicable to you. Cloud subdomain 4-2, for example, applies only if you use or plan to use cloud or hosting services.
NCA describes most of its control sets as extensions of the ECC: you put the ECC in place first, then add the set for the technology or situation you have. Current versions as of October 2026:
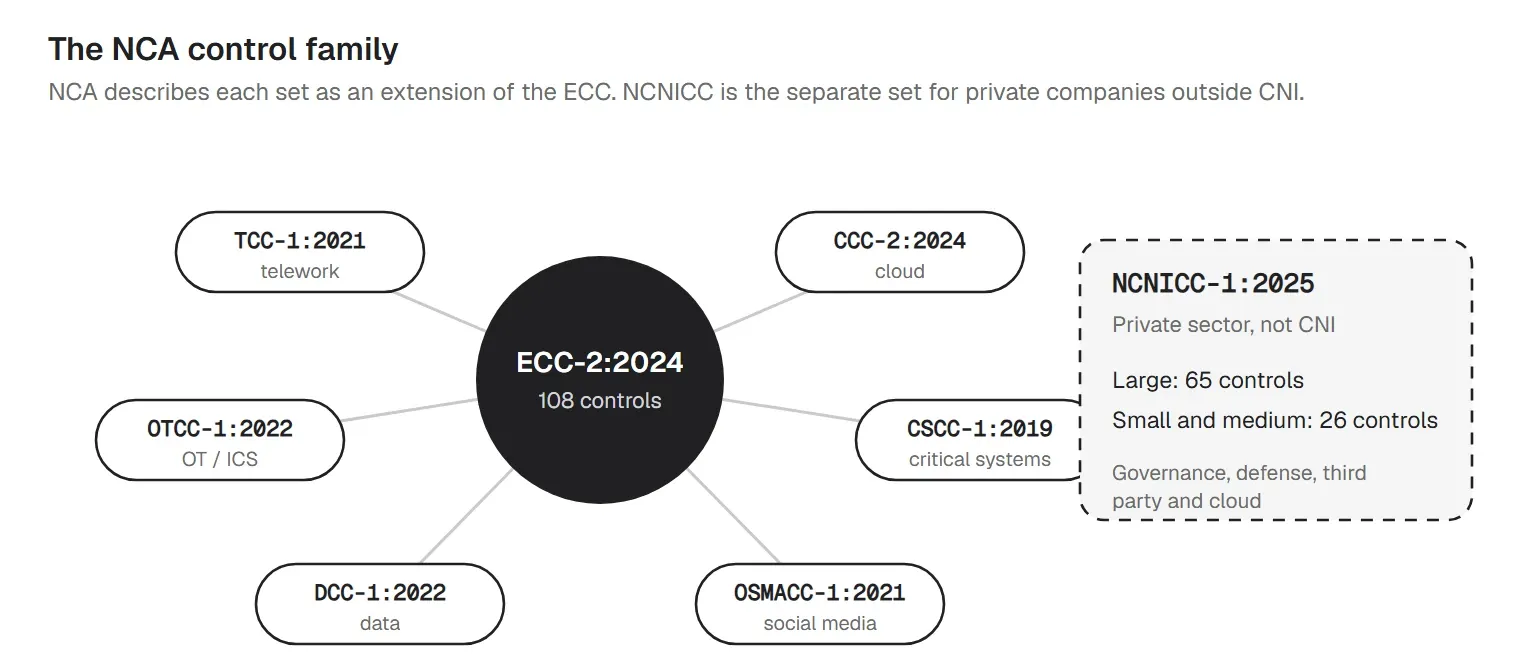
| Set | Version | What it covers (our words) |
|---|---|---|
| Essential Cybersecurity Controls | ECC-2:2024 | Government entities and their affiliated companies (inside and outside Saudi Arabia), and private entities that own, operate or host CNI |
| Non-CNI Private Sector Entities Cybersecurity Controls | NCNICC-1:2025 | Private-sector entities that are not CNI operators, in two size tiers (large; small and medium), as notified by NCA |
| Cloud Cybersecurity Controls | CCC-2:2024 | Cloud service providers and cloud service tenants |
| Telework Cybersecurity Controls | TCC-1:2021 | The same entities as ECC, for remote work |
| Operational Technology Cybersecurity Controls | OTCC-1:2022 | Industrial control systems and OT (took over ECC-1's old domain 5) |
| Critical Systems Cybersecurity Controls | CSCC-1:2019 | Extra controls for national critical systems |
| Data Cybersecurity Controls | DCC-1:2022 | Protecting data across its lifecycle |
| Organizations' Social Media Accounts Cybersecurity Controls | OSMACC-1:2021 | Securing an organization's official social media accounts |
The Telework Cybersecurity Controls matter to most IT teams: they apply to the same entities as the ECC and set concrete numbers, such as patches on mobile devices at least every month, telework systems patched at least every three months and backup restore tests at least every six months.
ECC-2:2024 has 4 main domains (Governance, Defense, Resilience, Third-Party and Cloud), 28 subdomains, 108 main controls and 92 subcontrols. It replaced ECC-1:2018, which had 5 domains and 114 controls; the industrial control systems domain moved to OTCC. Several requirements are specific enough to plan around:
Our NCA ECC compliance checklist lists all 108 controls with the evidence to keep, in a free PDF and Excel tracker.
The Non-CNI Private Sector Entities Cybersecurity Controls (NCNICC-1:2025) fill the gap the ECC left: private companies that are not CNI operators. The set has three components (Cybersecurity Governance, Cybersecurity Defense, and Third-Party and Cloud Computing Cybersecurity) and two tiers:
| Tier | Size (staff or annual revenue) | Controls |
|---|---|---|
| Large entities | More than 250 full-time staff, or revenue over SAR 200 million | 65 controls in 22 sub-components |
| Small and medium entities | 6 to 249 staff, or revenue of SAR 3 to 200 million | 26 controls in 13 sub-components |
Law-firm summaries say the controls apply to these categories as notified by NCA, and that some small and medium controls are recommended rather than mandatory. Secondary sources date the adoption to 28 December 2025. We found no published compliance deadline as of October 2026. If you are a private company, don't assume the full ECC applies to you; check whether NCA has notified you under NCNICC.
The ECC says NCA evaluates compliance through multiple means, such as self-assessment by the entity, periodic reports from NCA's compliance tool and field audit visits, as NCA sees fit. External evaluations run through NCA's Haseen e-service.
Inside your organization, control 1-8 asks for three things: the cybersecurity department reviews the controls periodically, parties outside that department audit them independently, and the results go to the cybersecurity supervisory committee and the head of the entity. That cycle produces most of what NCA will ask to see.
ECC-2:2024 says NCA will issue an assessment and compliance tool for it. In October 2026 the ECC page listed the document and an implementation guide but no tool, while the TCC, DCC and OTCC pages offer xlsx tools.
No. Nothing in the ECC describes a certificate, seal or badge, and NCA does not certify companies the way an ISO 27001 certification body does. Compliance is shown through the self-assessments, tool reports and audits above, and it has to be kept up, not earned once.
So treat "NCA certified" products and services with care. A vendor can say its product supports some controls; it cannot do your compliance work for you, and NCA does not endorse it. The same goes for trio.so: TrioSoft holds no NCA attestation of any kind.
ECC-2:2024 states the duty to comply and its legal basis, but no penalties or fine amounts. We found no official NCA penalty schedule for ECC non-compliance, so treat any specific figure you see quoted with caution and ask NCA or your legal counsel. What is clear from the Statute is that no entity is relieved of responsibility for its own cybersecurity.
Banks, finance companies and payment providers regulated by the Saudi Central Bank follow SAMA's Cyber Security Framework. If NCA treats your institution as critical national infrastructure, the ECC applies as well. No NCA or SAMA document we found says how the two relate or which takes precedence, so plan for both and confirm with your regulators. Many controls overlap, such as asset inventory, MFA, encryption, patching and logging, so one set of evidence can often serve both. Our SAMA CSF checklist covers the SAMA side.
Tools can take over the repetitive evidence work on the technical side; our guide to NCA compliance automation covers what can and can't be automated.
Most of the ECC is governance, network, logging, testing, continuity and third-party work, and trio.so does none of that. It is device management software for Windows, macOS, Linux, iOS, iPadOS and Android, and it supplies device evidence for several controls, most of them in the Defense domain:
trio.so's compliance engine includes an NCA ECC (ECC-2:2024) template. It is off by default: you turn it on, see device results and export the evidence for your assessment.
The template checks device settings only. It does not cover the governance, network, logging, testing, physical, continuity or third-party controls, and trio.so does not assess or certify ECC compliance. Learn more about compliance automation. Plans start at $5 per device.
14-day free trial. No credit card required.
More NCA and Saudi compliance guides for IT teams
Sources. Last reviewed October 2026 against ECC-2:2024, the current version on 27 October 2026. Control IDs and names are NCA's; every description is our own paraphrase, and the Arabic ECC text is binding. This article is guidance, not legal advice or an assessment. trio.so is not affiliated with or endorsed by NCA.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
Which NCA ECC-2:2024 controls you can automate, which need people, how small teams should sequence tools, and where device management fits in the stack.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
NIST compliance automation tools by type: GRC platforms, NIST and CISA tools, scanners and device management. What each covers and what it can't.
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
ISO 27001 compliance software explained: what each tool type automates, what stays with your team, how to choose one, and where device management fits.
Explore HIPAA compliance automation capabilities, limitations, and implementation steps. Learn what you can automate and what needs human oversight.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients