



Explained
HIPAA Compliance & Cell Phones: PHI Security Rules
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.

Content writer, trio.so
This NCA ECC compliance checklist turns the National Cybersecurity Authority's Essential Cybersecurity Controls, ECC-2:2024, into tasks you can assign and prove. It covers all 4 domains, 28 subdomains and 108 main controls, with the 92 subcontrols under them, the evidence each one needs and a suggested owner.
It is for IT and cybersecurity leads at Saudi government entities, their affiliated companies and critical national infrastructure (CNI) operators, and for private companies that use the ECC as their baseline. The free download is a PDF checklist and an Excel tracker with a summary sheet, an evidence register, a device and endpoint tab and a review calendar.
In short
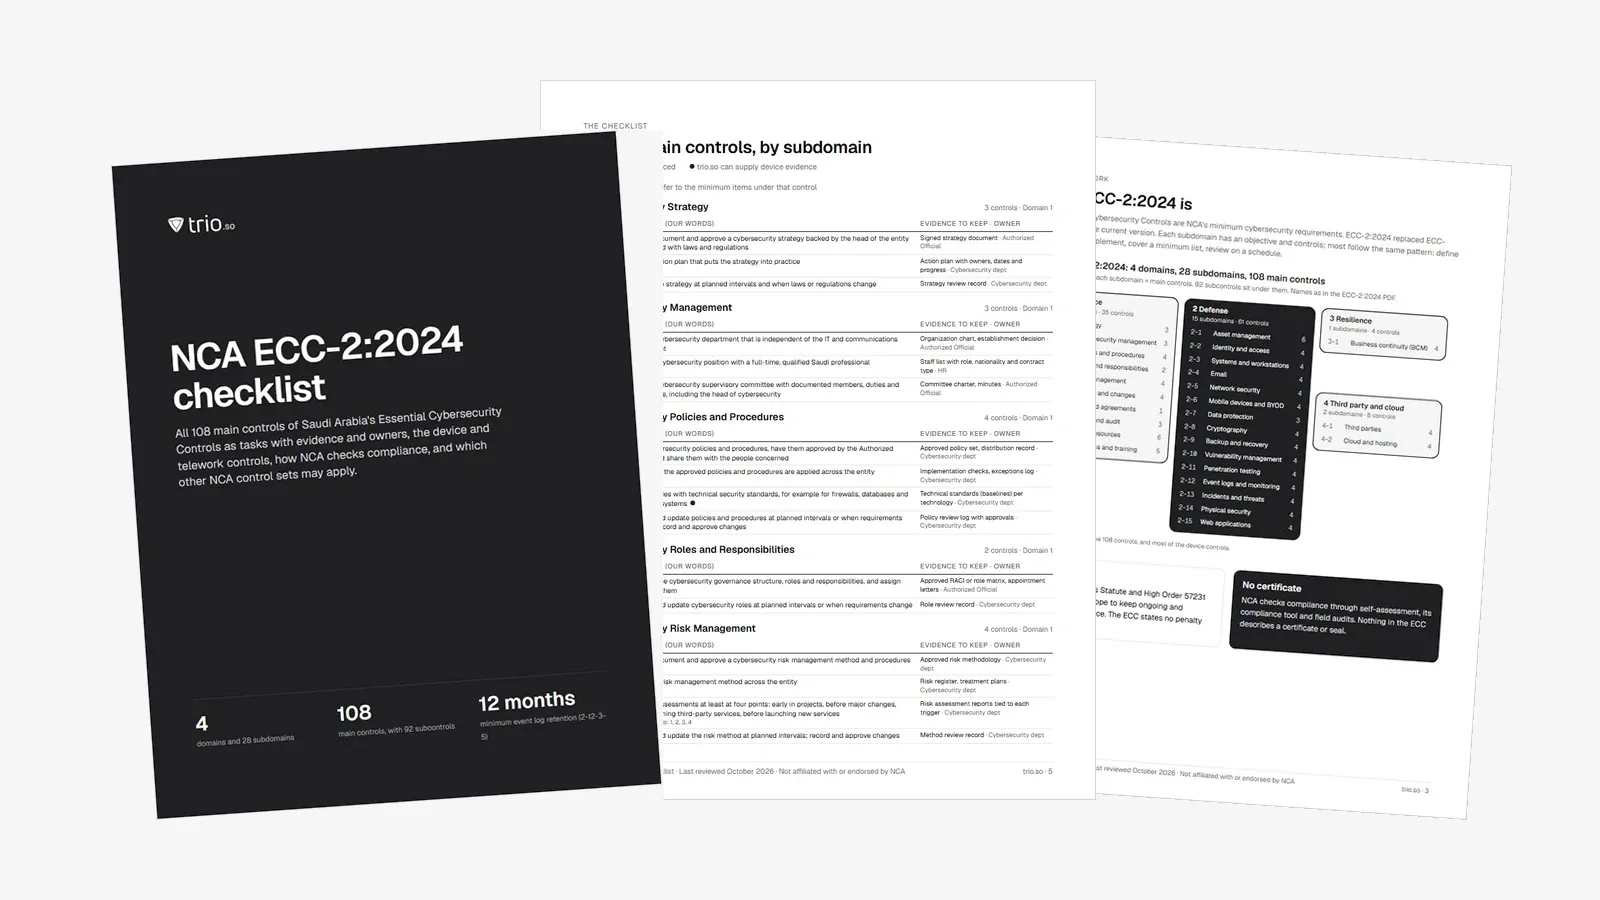
The Essential Cybersecurity Controls are NCA's minimum cybersecurity requirements. ECC-2:2024 is the current version: it updated ECC-1:2018, and NCA's ECC page still serves it as of October 2026. The Arabic text is the binding one.
Controls are coded by domain, subdomain and control, so 2-6-3 is Domain 2, subdomain 6 (Mobile Devices Security), control 3, and 2-6-3-1 is its first subcontrol. Each subdomain has an objective and a set of controls, and most follow the same four steps: define and approve the requirements, put them into practice, cover a minimum list, and review them on a schedule.
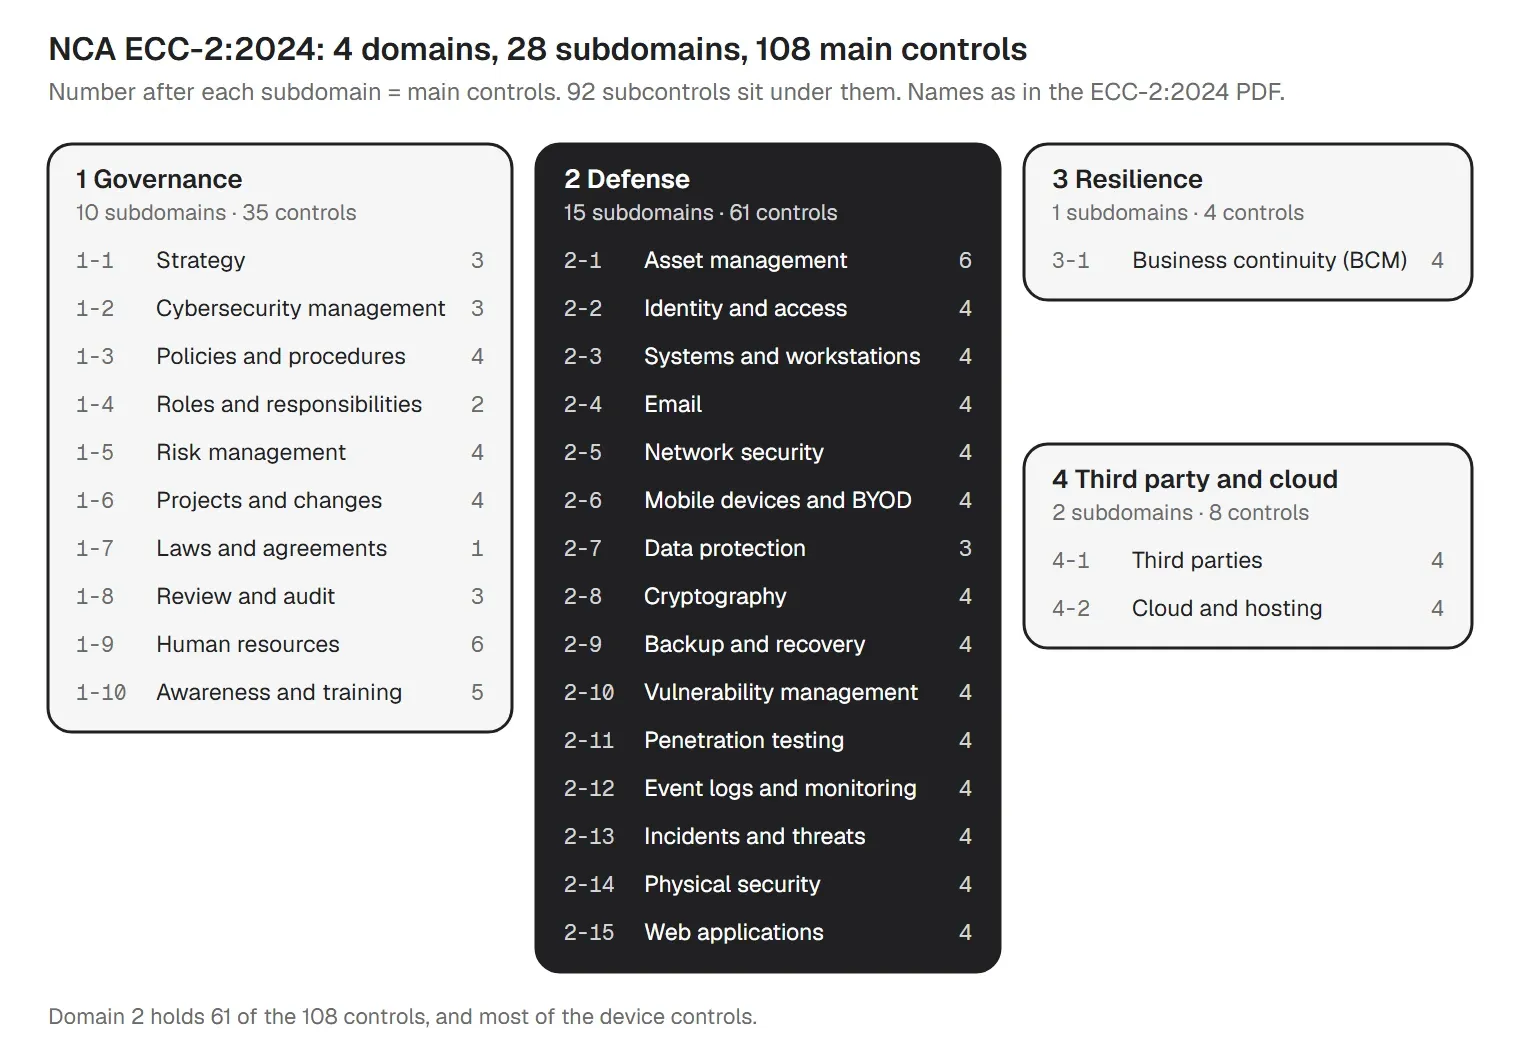
Domain 2, Cybersecurity Defense, holds 61 of the 108 controls and nearly all of the technical work. Domain 3 is a single subdomain on the cybersecurity side of business continuity. Domain 4 covers third parties and cloud services.
ECC-2:2024 applies to government agencies (ministries, authorities, establishments and others), their affiliated companies and entities inside and outside Saudi Arabia, and private-sector entities that own, operate or host CNI. NCA strongly encourages every other entity to use the controls as best practice.
Inside that scope, you apply every control that is applicable to you. The ECC's own example is cloud: subdomain 4-2 applies if you use or plan to use cloud or hosting services. Mark the controls that don't apply as Not applicable in the tracker and write down why.
Private companies that are not CNI operators now have their own NCA set, NCNICC-1:2025, with 65 controls for large entities and 26 for small and medium ones. Our guide to NCA compliance explains who falls under which set, including the telework, cloud and OT controls, and how banks fit next to SAMA.
Below is each subdomain with what an assessor will look for, in our words. The PDF and the Excel tracker break every row down into its main controls, each with the evidence to keep and a suggested owner, and list the 92 subcontrols separately.
| ID | Subdomain | What to check | Controls |
|---|---|---|---|
| 1-1 | Cybersecurity Strategy | An approved strategy, backed by the head of the entity, with an action plan you are running and a review date. | 3 |
| 1-2 | Cybersecurity Management | A cybersecurity department independent of IT, every cybersecurity post held by a full-time qualified Saudi professional, and a supervisory committee with a charter. | 3 |
| 1-3 | Cybersecurity Policies and Procedures | Approved policies and procedures, backed by technical standards (firewalls, databases, operating systems), communicated, in force and reviewed. | 4 |
| 1-4 | Cybersecurity Roles and Responsibilities | A governance structure and named roles approved by the Authorized Official, reviewed on a schedule. | 2 |
| 1-5 | Cybersecurity Risk Management | An approved risk method in use, with assessments early in projects, before major changes, before buying third-party services and before launching new services. | 4 |
| 1-6 | Cybersecurity in Information and Technology Project Management | Security requirements inside project and change management: vulnerability checks and a hardening review before go-live; secure coding for software. | 4 |
| 1-7 | Compliance with Cybersecurity Standards, Laws and Regulations | A list of nationally approved international agreements with cybersecurity terms that bind you, and how you follow them. | 1 |
| 1-8 | Periodical Cybersecurity Review and Audit | Your own periodic control reviews, an independent audit by people outside the cybersecurity department, and results sent to the committee. | 3 |
| 1-9 | Cybersecurity in Human Resources | Security and non-disclosure clauses in contracts, screening for sensitive roles, awareness for staff, and access removed at once when people leave. | 6 |
| 1-10 | Cybersecurity Awareness and Training Program | An approved awareness program (phishing, mobile devices and storage media, browsing, social media) and role-based training. | 5 |
| ID | Subdomain | What to check | Controls |
|---|---|---|---|
| 2-1 | Asset Management | A current inventory of all information and technology assets, an acceptable-use policy in force, and assets classified and labelled. | 6 |
| 2-2 | Identity and Access Management | MFA for remote access and privileged accounts, least privilege and segregation of duties, privileged access management and periodic access reviews. | 4 |
| 2-3 | Information System and Information Processing Facilities Protection | Centrally managed anti-malware on workstations and servers, strict control of external storage media, patch management and trusted time sync. | 4 |
| 2-4 | Email Protection | Phishing and spam filtering, MFA for remote and webmail access, archiving and backup, advanced-threat protection, and SPF, DKIM and DMARC. | 4 |
| 2-5 | Network Security Management | Segmentation, production separated from test, browsing restrictions, secure Wi-Fi, limited ports and services, IPS, DNS security and DDoS protection. | 4 |
| 2-6 | Mobile Devices Security | Rules for laptops, phones, tablets and BYOD: entity data kept separate and encrypted, use limited to business need, data deleted on loss or exit, user awareness. | 4 |
| 2-7 | Data and Information Protection | Data protection requirements approved and applied according to each data classification level. | 3 |
| 2-8 | Cryptography | A cryptography standard that includes NCA's National Cryptographic Standards, key lifecycle management, and encryption in transit and at rest by classification. | 4 |
| 2-9 | Backup and Recovery Management | Backups that cover critical assets, fast recovery after an incident and restore tests on a schedule. | 4 |
| 2-10 | Vulnerability Management | Periodic vulnerability assessment, severity ratings, risk-based fixes, patches tested outside production first, and trusted vulnerability feeds. | 4 |
| 2-11 | Penetration Testing | Penetration tests on a schedule covering every internet-facing service: infrastructure, websites, web and mobile apps, email and remote access. | 4 |
| 2-12 | Cybersecurity Event Logs and Monitoring Management | Logs on for critical assets, privileged accounts and remote access, a SIEM, continuous review and at least 12 months of retention. | 4 |
| 2-13 | Cybersecurity Incident and Threat Management | Incident response plans and escalation, incident classification, reporting to NCA, sharing with NCA and threat intelligence feeds. | 4 |
| 2-14 | Physical Security | Controlled access to critical areas, access and CCTV logs that are protected, secure disposal and re-use of media, and device security on and off site. | 4 |
| 2-15 | Web Application Security | For external web apps: a web application firewall, multi-tier design, HTTPS, a secure-use policy and authentication set by impact assessment. | 4 |
| ID | Subdomain | What to check | Controls |
|---|---|---|---|
| 3-1 | Cybersecurity Resilience Aspects of Business Continuity Management (BCM) | Business continuity plans that keep security systems running, include cyber incident response and include disaster recovery. | 4 |
| ID | Subdomain | What to check | Controls |
|---|---|---|---|
| 4-1 | Third-Party Cybersecurity | Contract clauses for confidentiality, data removal and incident contact; risk assessment before outsourcing; managed SOCs that use remote access based fully in Saudi Arabia. | 4 |
| 4-2 | Cloud Computing and Hosting Cybersecurity | Cloud requirements in force: data protected by classification and returned in a usable format at exit, and your environment separated from other tenants. | 4 |
Most gaps in an ECC self-assessment are not exotic. They are specific wording that a quick read skips:
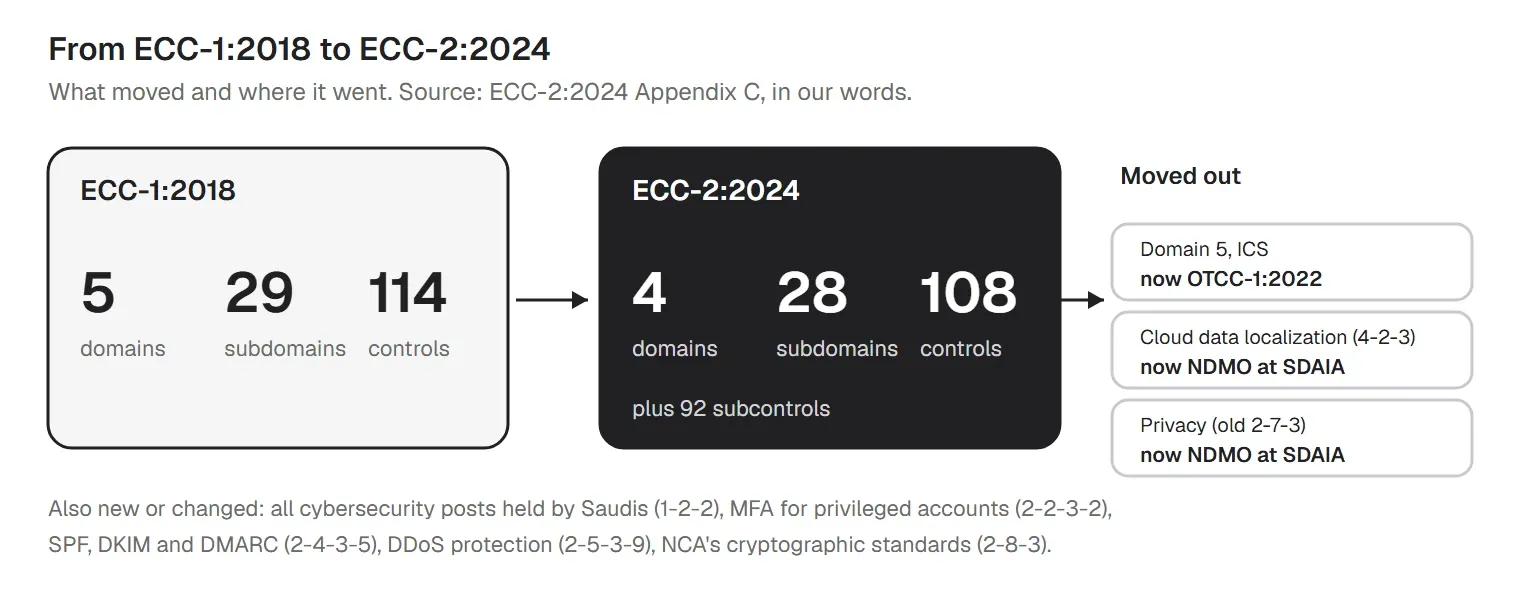
If your last gap analysis used ECC-1:2018, re-map it. The 2018 version had 5 domains, 29 subdomains and 114 controls. ECC-2:2024's Appendix C lists every change; the ones that move work are these:
| Area | Change |
|---|---|
| Structure | 5 domains, 29 subdomains and 114 controls became 4 domains, 28 subdomains and 108 controls (92 subcontrols). |
| Domain 5 removed | Industrial Control Systems moved out of the ECC into OTCC. |
| Scope | Now names government affiliates inside and outside Saudi Arabia. |
| 1-2-2 staffing | All cybersecurity positions, not just the head and critical roles, go to full-time qualified Saudis. |
| 2-2-3-2 MFA | MFA now covers privileged accounts as well as remote access, with factors set by impact assessment. |
| 2-4-3-5 email | Domain validation names SPF, DKIM and DMARC (SPF only before). |
| 2-5-3-9 DDoS | New subcontrol: protection against DDoS attacks. |
| 2-7 data | Protection by classification level; privacy moved to NDMO at SDAIA. |
| 2-8-3 crypto | Must include NCA's National Cryptographic Standards. |
| 4-2-3 cloud | The rule to host and store data inside the Kingdom was removed; localization now sits with NDMO (SDAIA). |
Two common claims are wrong. Web Application Security (2-15) is not new; ECC-1:2018 had it. And ECC-2:2024 no longer requires hosting and storage inside the Kingdom: that rule moved to the National Data Management Office (NDMO) at SDAIA, and NCA updated its cloud controls, CCC-2:2024, for localization.
The ECC doesn't name a product, but several Defense controls land on laptops, desktops, phones and tablets. NCA's Telework Cybersecurity Controls (TCC-1:2021), which apply to the same entities for remote work, go further and ask for central management of mobile devices and BYOD with an MDM (TCC 2-5-1-1) and monthly patches on mobile devices (TCC 2-5-1-2).
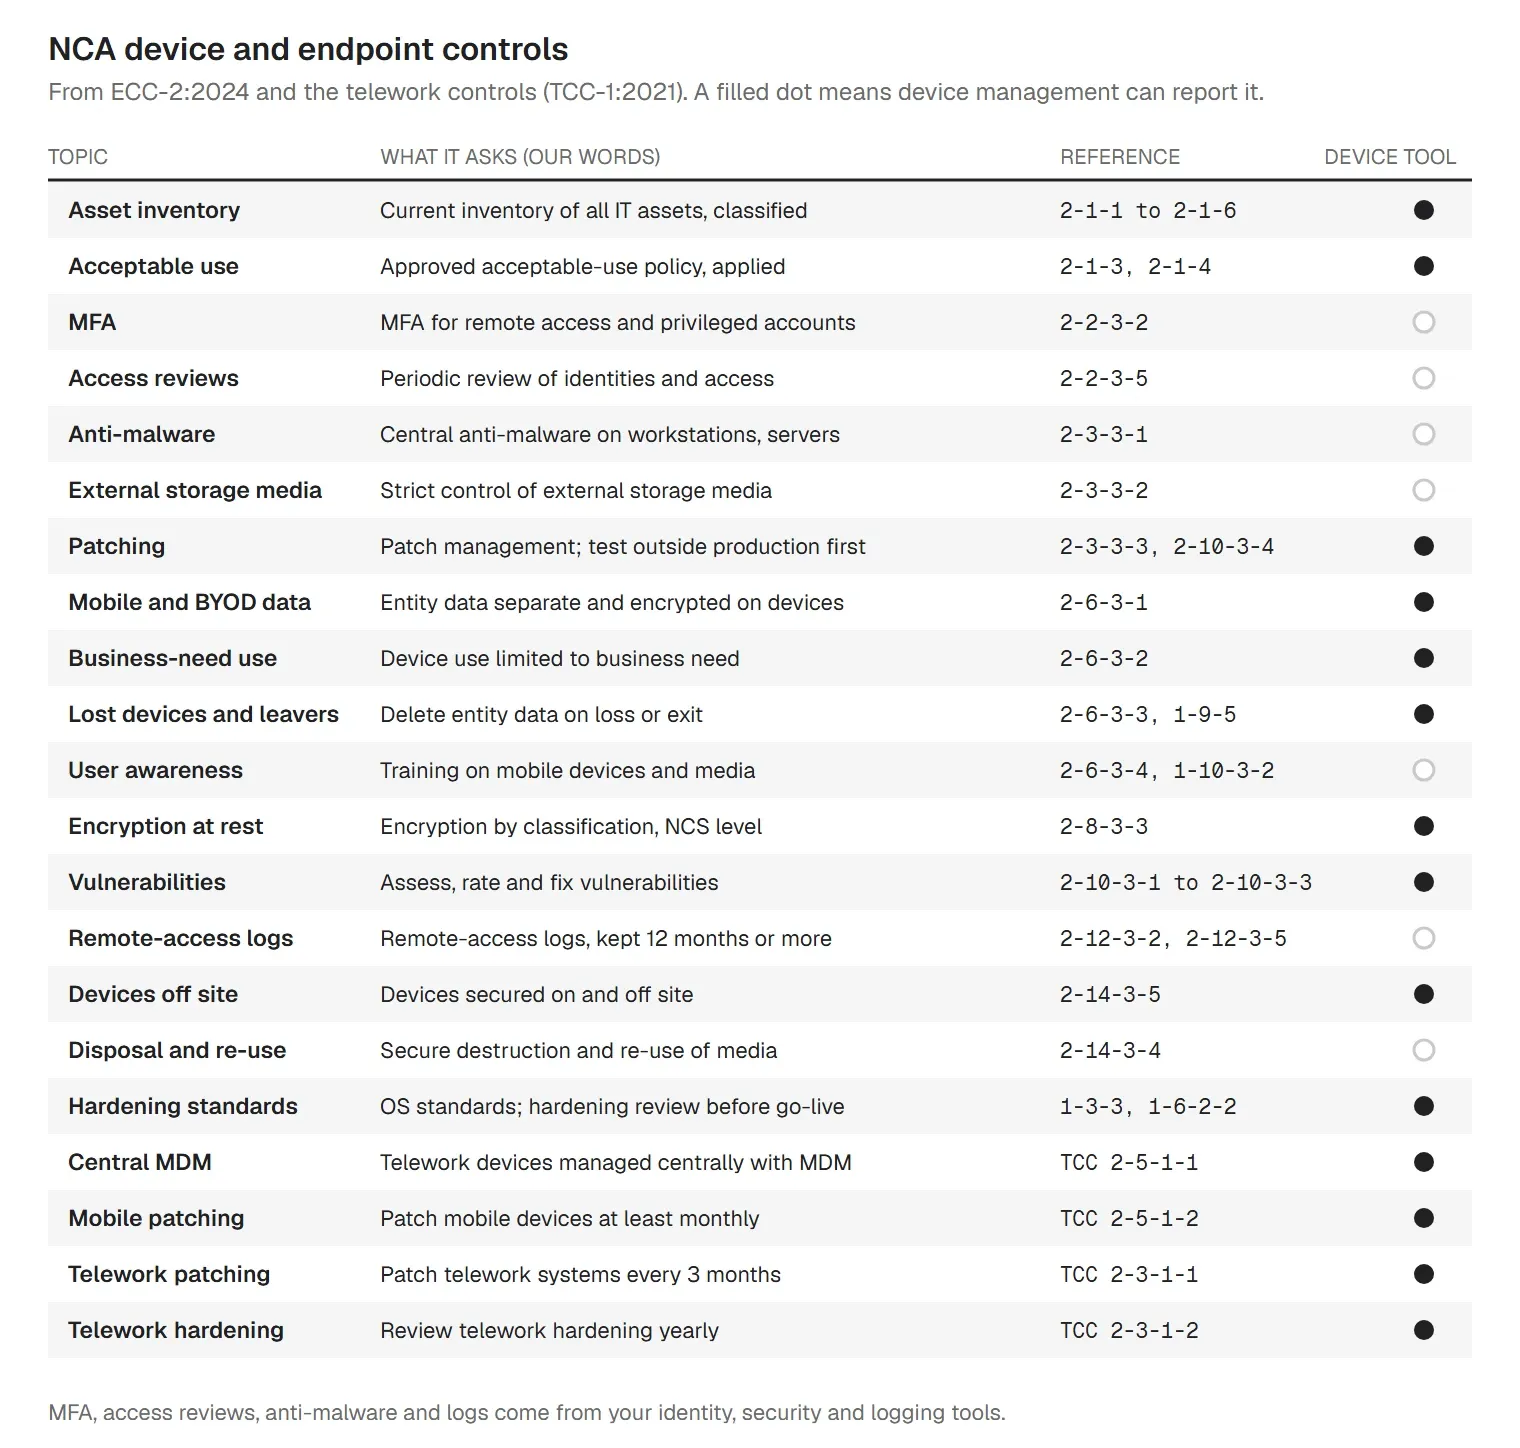
The tracker's Device and endpoint tab lists these with a column for laptops and desktops, one for phones and tablets, and an exceptions column.
NCA evaluates compliance "through multiple means", in the ECC's words: self-assessment by the entity, periodic reports from NCA's compliance tool, and field audit visits, as NCA sees fit. NCA's external evaluations run through its Haseen portal.
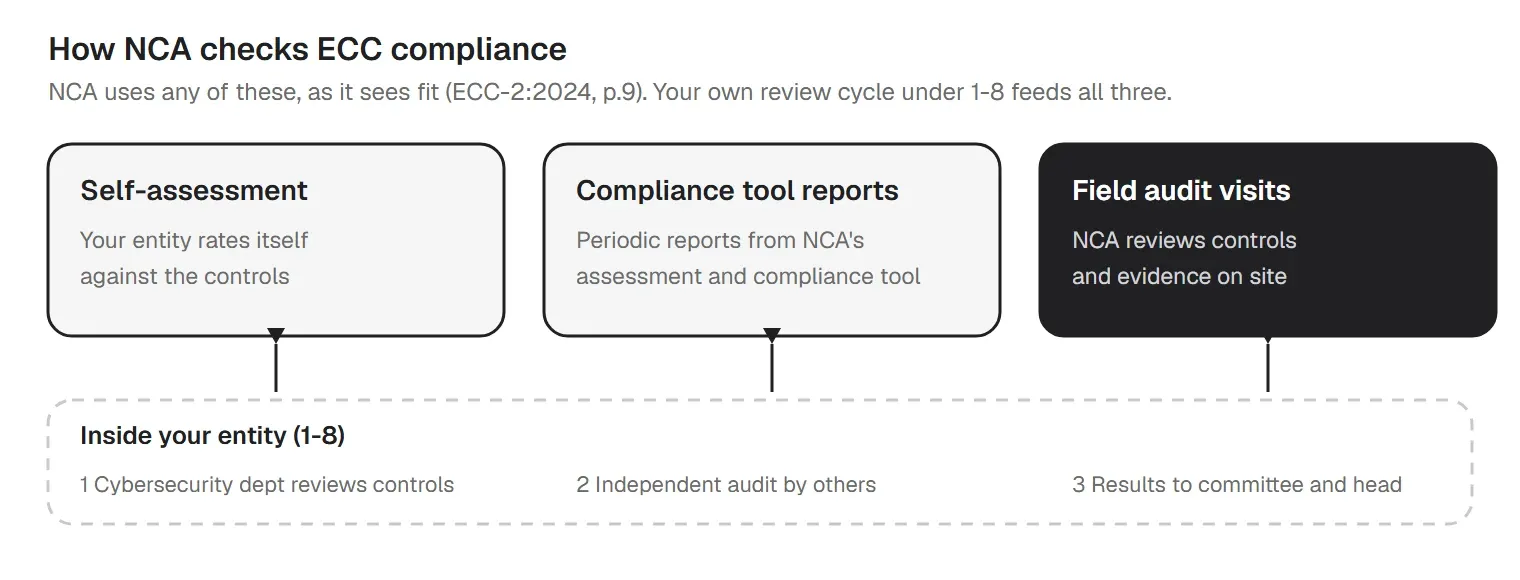
ECC-2:2024 says NCA will issue an ECC-2:2024 assessment and compliance tool. In October 2026 the ECC page listed the PDF and an implementation guide but no tool download, while the telework, data and OT pages do offer one. There is no ECC certificate, so be wary of anyone selling one.
Evidence that holds up is dated, approved and specific: the signed strategy and policies with review dates, the committee charter and minutes, the role matrix, the risk register, the asset inventory, MFA coverage and access review sign-offs, patch, scan and penetration test reports with the fixes, log retention settings, the incident plan and reports to NCA, continuity and recovery test results, and contracts with the required clauses.
For tools that take over the repetitive parts, see our guide to NCA compliance automation.
Most of the ECC is governance, network, logging, testing, continuity and third-party work, and trio.so does none of that. It is device management software for Windows, macOS, Linux, iOS, iPadOS and Android, and it supplies device evidence for several controls, most of them in the Defense domain:
trio.so's compliance engine includes an NCA ECC (ECC-2:2024) template. It is off by default: you turn it on, see device results and export the evidence for your assessment.
In the checklist, the controls marked with a dot are the ones where these device results can serve as part of the evidence: 1-3-3, 1-6-2, 1-8-1, 2-1-2, 2-1-4, 2-3-3, 2-6-2, 2-6-3, 2-8-3, 2-10-3 and 2-14-3. None of them is covered in full by a device tool.
The template checks device settings only. It does not cover the governance, network, logging, testing, physical, continuity or third-party controls, and trio.so does not assess or certify ECC compliance. Learn more about compliance automation. Plans start at $5 per device.
14-day free trial. No credit card required.
More NCA and Saudi compliance guides for IT teams
Sources. Last reviewed October 2026 against ECC-2:2024, the current version on 27 October 2026. Control IDs and names are NCA's; every description is our own paraphrase, and the Arabic ECC text is binding. This article is guidance, not legal advice or an assessment. trio.so is not affiliated with or endorsed by NCA.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
Which NCA ECC-2:2024 controls you can automate, which need people, how small teams should sequence tools, and where device management fits in the stack.
NIST compliance automation tools by type: GRC platforms, NIST and CISA tools, scanners and device management. What each covers and what it can't.
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
ISO 27001 compliance software explained: what each tool type automates, what stays with your team, how to choose one, and where device management fits.
Explore HIPAA compliance automation capabilities, limitations, and implementation steps. Learn what you can automate and what needs human oversight.
What ISO 27001 certification costs a small business: the audit, preparation, tools and staff time, what drives each one, and how to keep the bill down.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients