



Explained
HIPAA Compliance & Cell Phones: PHI Security Rules
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.

Content writer, trio.so
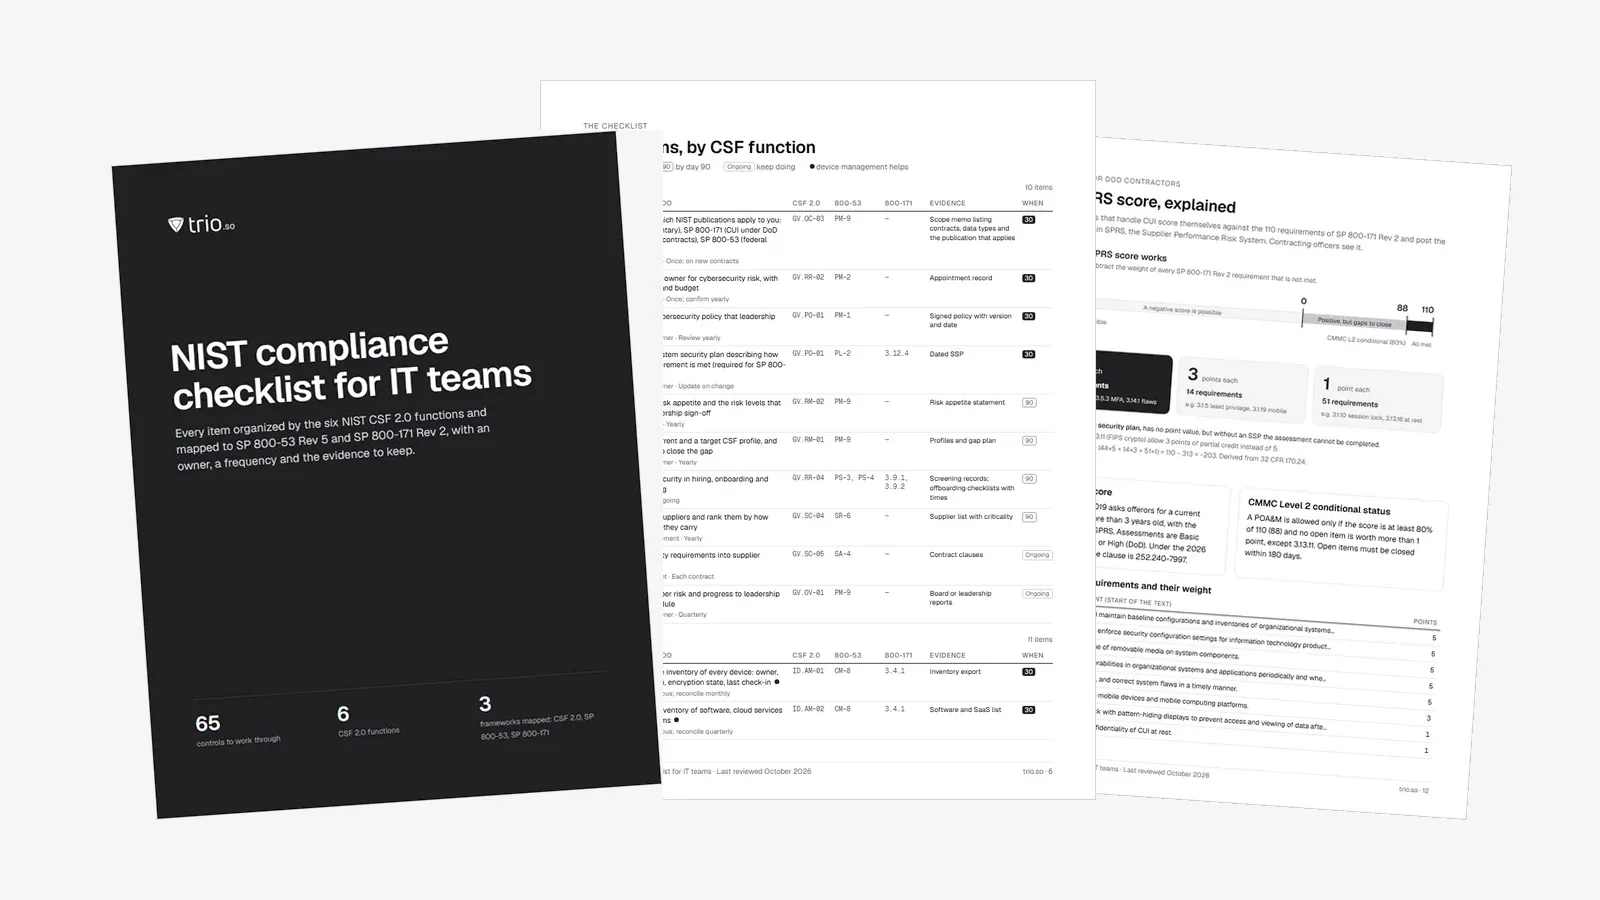
A NIST compliance checklist lists the security controls a NIST framework expects, and the proof that they run. This one has 65 controls organized by the six functions of the NIST Cybersecurity Framework (CSF) 2.0: Govern, Identify, Protect, Detect, Respond and Recover. Each item is mapped to the matching SP 800-53 control and SP 800-171 requirement, so one list works whichever NIST document applies to you.
It is written for the people doing the work: IT managers, sysadmins and MSPs at companies adopting the CSF, defense contractors handling CUI, and teams supporting federal systems. The device items go further than most checklists, because laptops and phones are where many controls actually live.
Download it as a printable PDF and an Excel tracker with a dashboard, a CSF 2.0 self-assessment, and an SP 800-171 sheet that calculates your SPRS score. Or work through it below.
In short
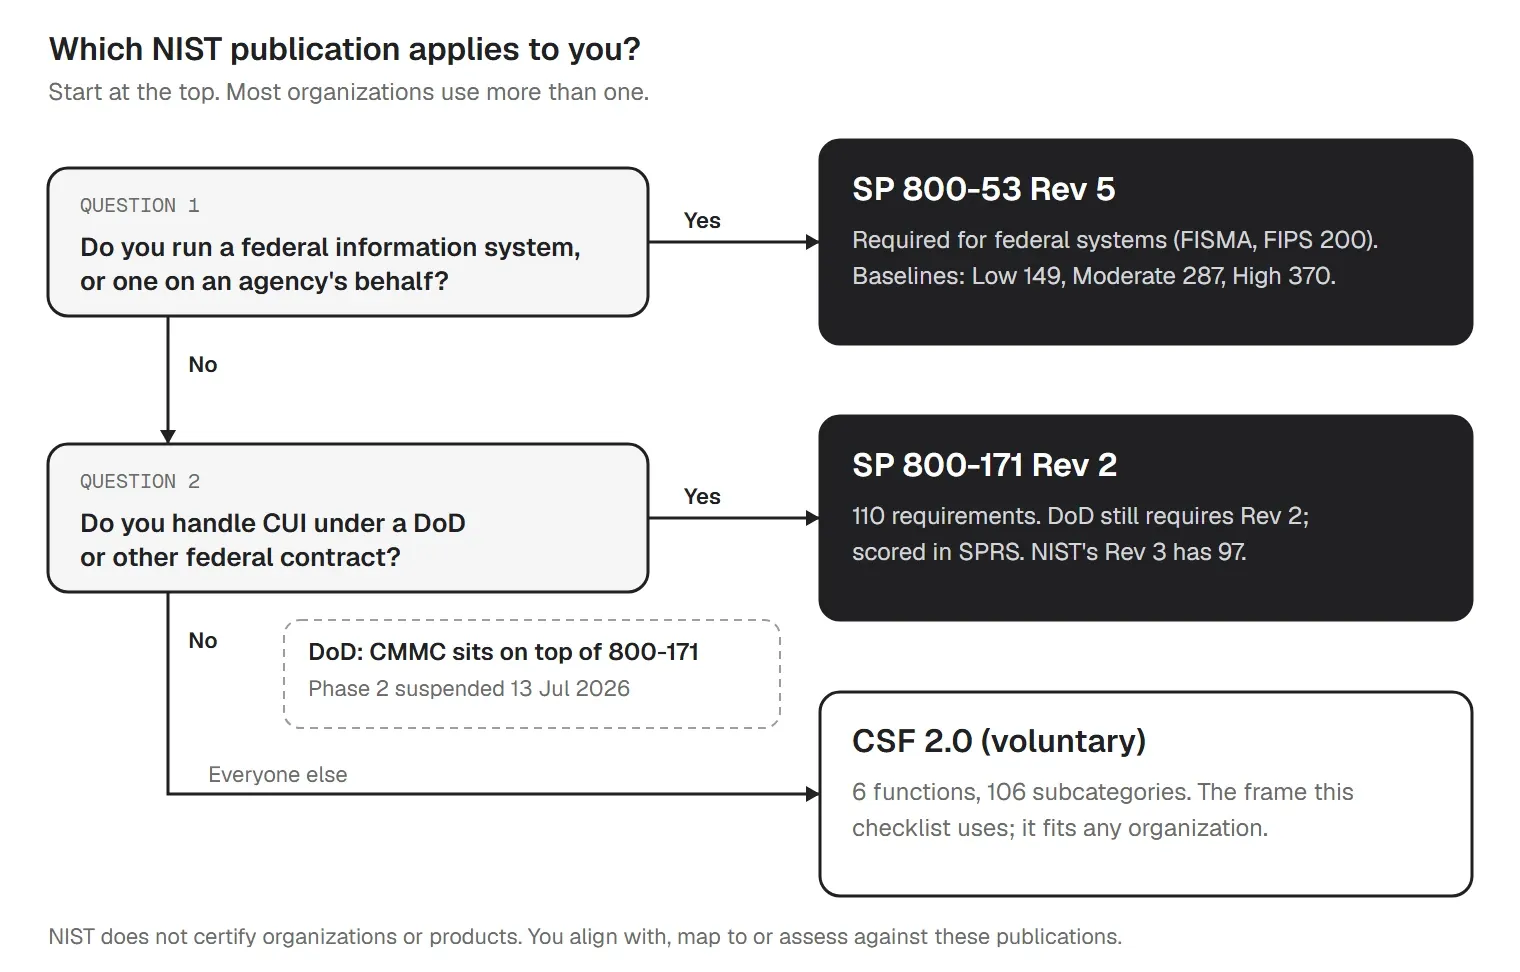
"NIST compliance" covers three different documents. NIST itself is non-regulatory and does not offer certifications, so the obligation comes from your contracts or your sector:
| Document | Who it applies to | Size |
|---|---|---|
| CSF 2.0 | Any organization, voluntarily. Many customers and insurers ask about it. | 6 functions, 22 categories, 106 subcategories |
| SP 800-171 Rev. 2 | Contractors that handle Controlled Unclassified Information (CUI) under DoD contracts (DFARS 252.204-7012) | 110 requirements in 14 families |
| SP 800-53 Rev. 5 | Federal information systems, and providers that run them | 20 families; baselines of 149, 287 and 370 controls |
If you are not sure, start with the CSF. The checklist below covers it fully and tags the 800-53 and 800-171 items alongside. Our guide to NIST compliance explains the background.
Put the basics in first. 19 items are marked "first 30 days": the ones that close the most common gaps and that any assessor asks about first.
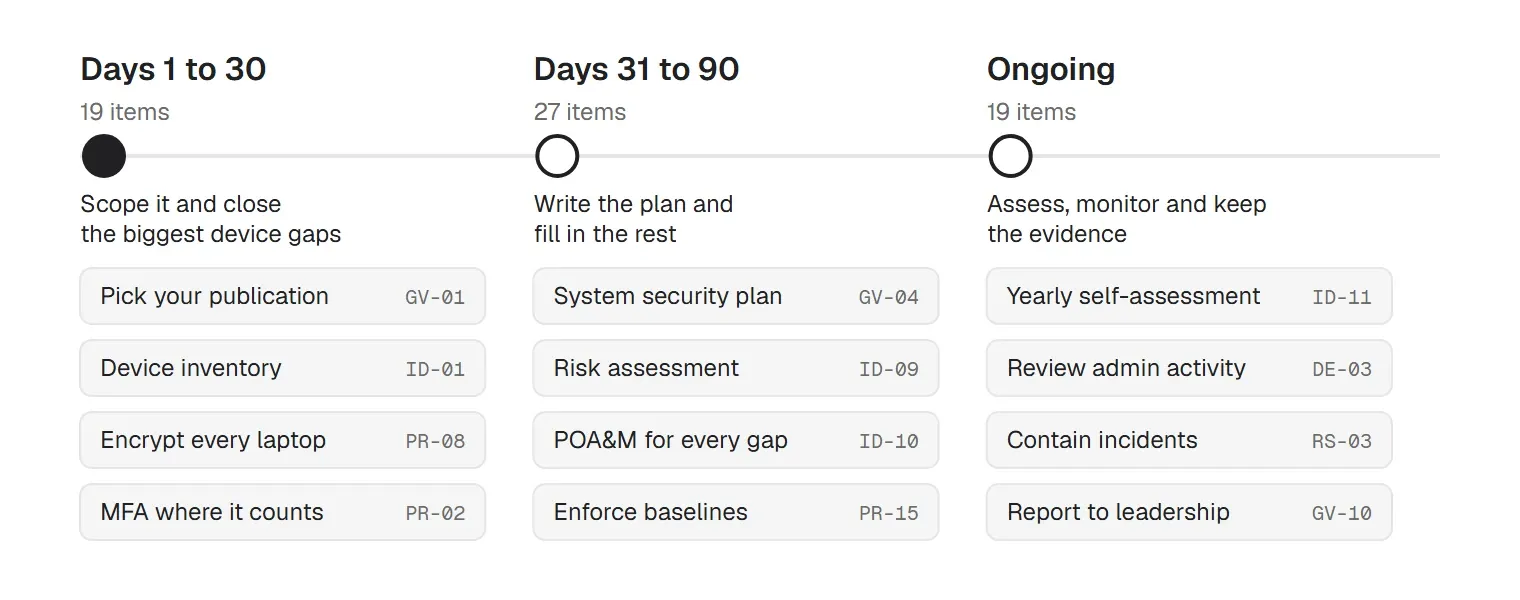
In the Excel tracker, filter the Phase column to see each list. Give every item an owner and a due date before you start.
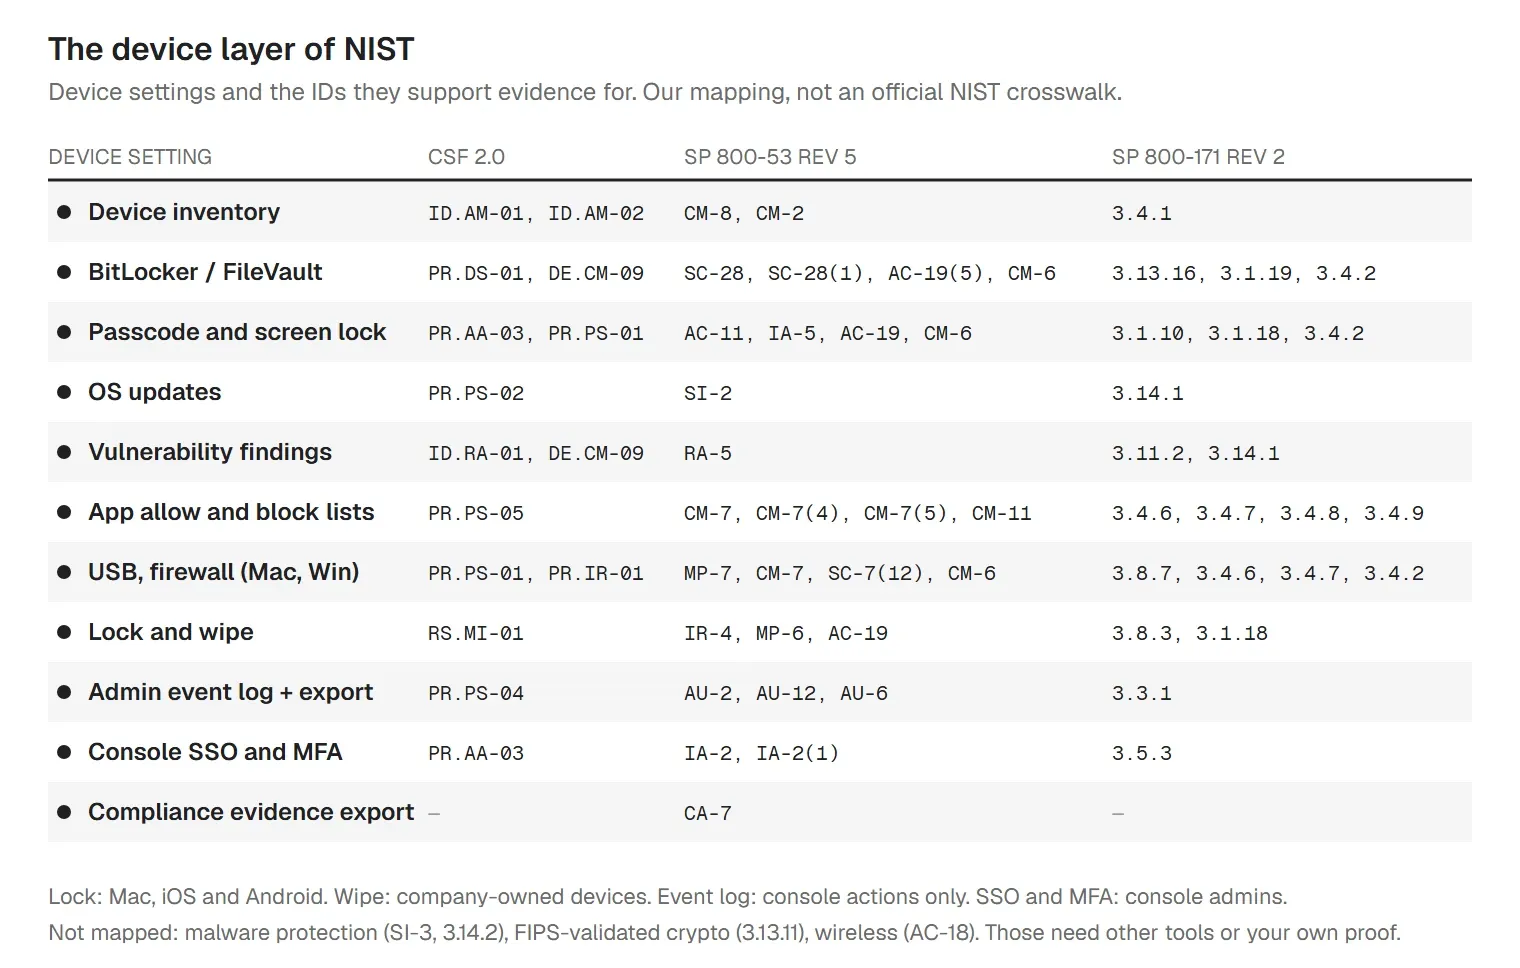
Each item lists the CSF 2.0 subcategory it supports, the closest SP 800-53 control and the SP 800-171 requirement, where one exists. These mappings are practical groupings, not an official NIST crosswalk.
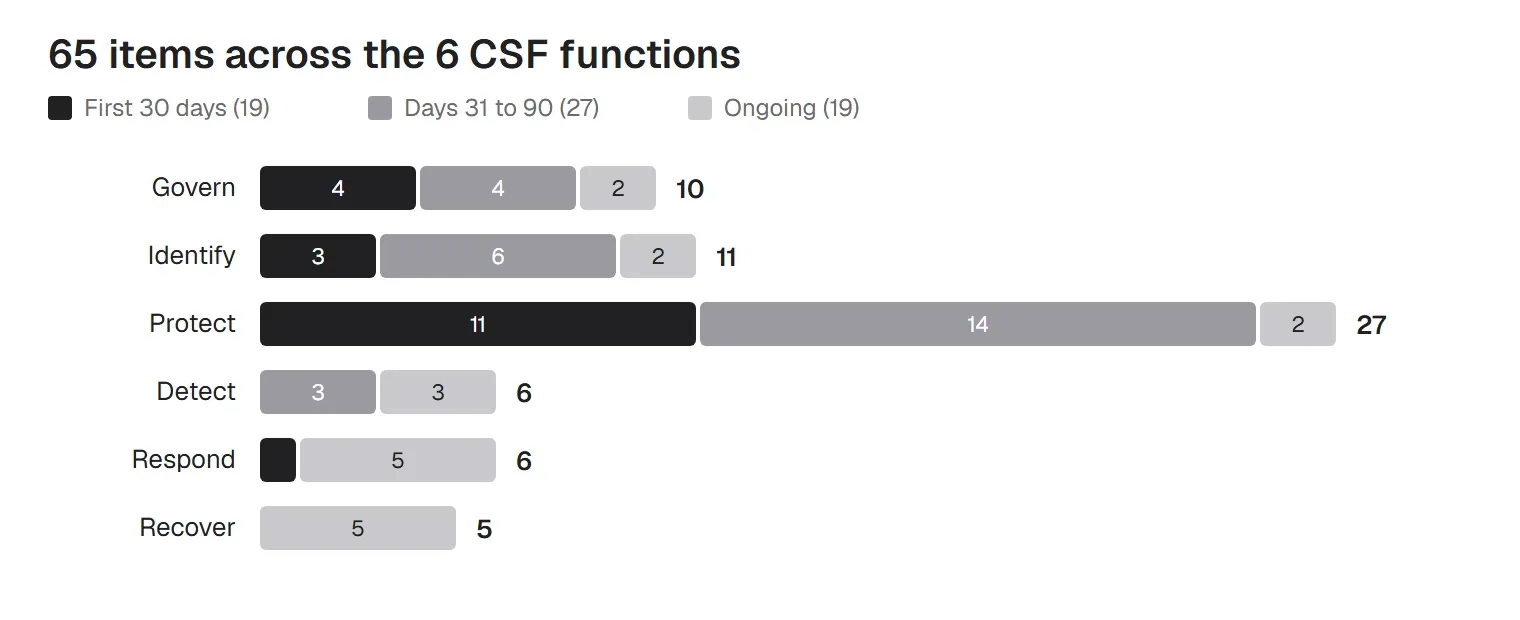
Govern is new in CSF 2.0. It covers who owns cybersecurity risk, the policy, and how suppliers are managed. For SP 800-171, the system security plan sits here too.
| ID | What to do | CSF 2.0 | 800-53 | 800-171 | Evidence to keep |
|---|---|---|---|---|---|
| GV-01 | Decide which NIST publications apply to you: CSF (voluntary), SP 800-171 (CUI under DoD or federal contracts), SP 800-53 (federal systems) (first 30 days) | GV.OC-03 | PM-9 | — | Scope memo listing contracts, data types and the publication that applies |
| GV-02 | Name one owner for cybersecurity risk, with authority and budget (first 30 days) | GV.RR-02 | PM-2 | — | Appointment record |
| GV-03 | Write a cybersecurity policy that leadership approves (first 30 days) | GV.PO-01 | PM-1 | — | Signed policy with version and date |
| GV-04 | Write a system security plan describing how each requirement is met (required for SP 800-171) (first 30 days) | GV.PO-01 | PL-2 | 3.12.4 | Dated SSP |
| GV-05 | Set your risk appetite and the risk levels that need leadership sign-off | GV.RM-02 | PM-9 | — | Risk appetite statement |
| GV-06 | Build a current and a target CSF profile, and the plan to close the gap | GV.RM-01 | PM-9 | — | Profiles and gap plan |
| GV-07 | Include security in hiring, onboarding and offboarding | GV.RR-04 | PS-3, PS-4 | 3.9.1, 3.9.2 | Screening records; offboarding checklists with times |
| GV-08 | List your suppliers and rank them by how much risk they carry | GV.SC-04 | SR-6 | — | Supplier list with criticality |
| GV-09 | Put security requirements into supplier contracts | GV.SC-05 | SA-4 | — | Contract clauses |
| GV-10 | Report cyber risk and progress to leadership on a schedule | GV.OV-01 | PM-9 | — | Board or leadership reports |
You can't protect what you haven't found. The inventory is the base of everything else, and NIST's documents all start with it. Vulnerability scanning lives here as well: see our guide to vulnerability management.
| ID | What to do | CSF 2.0 | 800-53 | 800-171 | Evidence to keep |
|---|---|---|---|---|---|
| ID-01 | Keep a live inventory of every device: owner, OS version, encryption state, last check-in (first 30 days) | ID.AM-01 | CM-8 | 3.4.1 | Inventory export |
| ID-02 | Keep an inventory of software, cloud services and systems (first 30 days) | ID.AM-02 | CM-8 | 3.4.1 | Software and SaaS list |
| ID-03 | Map how sensitive data and CUI move between systems and outside parties | ID.AM-03 | PL-8 | 3.1.3 | Data flow diagram |
| ID-04 | Find and label where sensitive data and CUI live | ID.AM-07 | RA-2 | — | Data inventory |
| ID-05 | Rank assets by how critical they are to the business | ID.AM-05 | RA-2 | — | Criticality ratings in the inventory |
| ID-06 | Track hardware and software through their whole life, including end of support | ID.AM-08 | SA-22 | — | End-of-life report from the inventory |
| ID-07 | Scan for vulnerabilities on a schedule and when new ones are announced (first 30 days) | ID.RA-01 | RA-5 | 3.11.2 | Scan reports |
| ID-08 | Watch threat and vulnerability alerts, including CISA's Known Exploited Vulnerabilities list | ID.RA-02 | SI-5 | 3.14.3 | Alert log with actions |
| ID-09 | Run a risk assessment: likelihood and impact for each threat to your systems | ID.RA-05 | RA-3 | 3.11.1 | Dated risk assessment |
| ID-10 | Track every fix in a plan of action and milestones (POA&M) with owner and date | ID.RA-06 | CA-5 | 3.12.2 | POA&M |
| ID-11 | Assess your controls against the framework, and record what to improve | ID.IM-01 | CA-2 | 3.12.1 | Self-assessment results |
Protect is the largest function and the one IT owns most directly: identities, encryption, configuration, patching and network controls. Pair it with our access control policy template.
| ID | What to do | CSF 2.0 | 800-53 | 800-171 | Evidence to keep |
|---|---|---|---|---|---|
| PR-01 | Give everyone a unique account; remove shared and generic logins (first 30 days) | PR.AA-01 | IA-2, AC-2 | 3.5.1, 3.5.2 | User list per system |
| PR-02 | Require MFA for remote access, privileged accounts, email and cloud apps (first 30 days) | PR.AA-03 | IA-2(1), IA-2(2) | 3.5.3 | MFA enrollment report |
| PR-03 | Grant least privilege; keep admin accounts separate from daily accounts (first 30 days) | PR.AA-05 | AC-6 | 3.1.5, 3.1.6 | Admin account list |
| PR-04 | Review access every quarter and remove leavers the same day | PR.AA-05 | AC-2 | 3.1.1 | Signed reviews; leaver records |
| PR-05 | Control physical access to offices, server rooms and equipment | PR.AA-06 | PE-2, PE-3 | 3.10.1 | Access lists and logs |
| PR-06 | Train everyone on security, including phishing, at hire and every year | PR.AT-01 | AT-2 | 3.2.1, 3.2.2 | Training records |
| PR-07 | Give admins and developers role-specific security training | PR.AT-02 | AT-3 | 3.2.2 | Training records |
| PR-08 | Encrypt every laptop and desktop (BitLocker, FileVault) and store recovery keys centrally (first 30 days) | PR.DS-01 | SC-28(1) | 3.13.16 | Encryption status report per device |
| PR-09 | Encrypt phones and tablets by requiring a passcode (first 30 days) | PR.DS-01 | AC-19(5) | 3.1.19 | Mobile compliance report |
| PR-10 | Encrypt data in transit: TLS for web and email, VPN for remote access | PR.DS-02 | SC-8(1) | 3.13.8 | TLS and VPN configuration |
| PR-11 | Back up critical data, protect the backups, and test restores (first 30 days) | PR.DS-11 | CP-9 | 3.8.9 | Backup reports; restore test results |
| PR-12 | Restrict USB and removable storage where it is not needed | PR.DS-01 | MP-7 | 3.8.7 | USB policy and settings report |
| PR-13 | Wipe or destroy devices and drives before disposal or reuse, and keep proof | ID.AM-08 | MP-6 | 3.8.3 | Wipe or destruction records |
| PR-14 | Document a secure configuration baseline for each operating system (first 30 days) | PR.PS-01 | CM-2 | 3.4.1 | Baseline documents |
| PR-15 | Enforce the baseline settings and detect drift | PR.PS-01 | CM-6 | 3.4.2 | Configuration compliance report |
| PR-16 | Lock screens automatically after a set idle time (first 30 days) | PR.PS-01 | AC-11 | 3.1.10 | Screen lock settings report |
| PR-17 | Patch operating systems and apps on a set timeline, fastest for critical and known-exploited flaws (first 30 days) | PR.PS-02 | SI-2 | 3.14.1 | Patch compliance report |
| PR-18 | Replace unsupported operating systems and software, or isolate them with a documented exception | PR.PS-02 | SA-22 | — | Exception register |
| PR-19 | Allow approved apps and block prohibited ones | PR.PS-05 | CM-7(5) | 3.4.8 | App allow and block lists |
| PR-20 | Turn off unneeded services and ports; turn on host firewalls | PR.IR-01 | CM-7, SC-7(12) | 3.4.7 | Firewall and service settings |
| PR-21 | Run anti-malware or EDR on every endpoint (first 30 days) | PR.PS-05 | SI-3 | 3.14.2 | Coverage report from the EDR tool |
| PR-22 | Turn on logging for systems that handle sensitive data, and keep the logs | PR.PS-04 | AU-2, AU-12 | 3.3.1 | Logging settings; retention policy |
| PR-23 | Require mobile devices to be enrolled before they reach company data; write BYOD rules | PR.PS-01 | AC-19 | 3.1.18 | Enrollment report; BYOD policy |
| PR-24 | Run changes to systems through an approval process | PR.PS-01 | CM-3 | 3.4.3 | Change tickets |
| PR-25 | Segment networks; keep guests and IoT away from sensitive systems | PR.IR-01 | SC-7 | 3.13.1, 3.13.5 | Network diagram; firewall rules |
| PR-26 | Secure remote access with a VPN or similar service plus MFA (first 30 days) | PR.IR-01 | AC-17 | 3.1.12 | Remote access configuration |
| PR-27 | Protect wireless access with strong encryption and authentication | PR.IR-01 | AC-18 | 3.1.16, 3.1.17 | Wi-Fi configuration |
Detection depends on knowing what normal looks like. Monitor networks, endpoints and admin activity, and decide in advance what counts as an incident.
| ID | What to do | CSF 2.0 | 800-53 | 800-171 | Evidence to keep |
|---|---|---|---|---|---|
| DE-01 | Monitor networks and network services for suspicious activity | DE.CM-01 | SI-4 | 3.14.6 | Monitoring tool and alert records |
| DE-02 | Monitor endpoints for encryption, patch and configuration status | DE.CM-09 | CA-7 | 3.12.3 | Monthly device status reports |
| DE-03 | Monitor admin and user activity for misuse | DE.CM-03 | AU-6 | 3.3.5 | Review records |
| DE-04 | Monitor what service providers do in your environment | DE.CM-06 | SA-9 | — | Provider access review |
| DE-05 | Analyze and correlate alerts to spot real incidents | DE.AE-03 | AU-6 | 3.3.5 | Triage records |
| DE-06 | Define what counts as an incident and who declares it | DE.AE-08 | IR-8 | 3.6.1 | Incident criteria in the IR plan |
Write the plan before you need it. DoD contracts require cyber incidents to be reported within 72 hours. Our data breach response plan is a starting point.
| ID | What to do | CSF 2.0 | 800-53 | 800-171 | Evidence to keep |
|---|---|---|---|---|---|
| RS-01 | Write an incident response plan with roles and contacts, and test it (first 30 days) | ID.IM-04 | IR-8, IR-3 | 3.6.1, 3.6.3 | IR plan; test report |
| RS-02 | Triage, categorize and prioritize incidents | RS.MA-03 | IR-4 | 3.6.1 | Incident tickets |
| RS-03 | Contain incidents: lock or wipe lost devices, disable compromised accounts | RS.MI-01 | IR-4 | 3.6.1 | Containment records |
| RS-04 | Preserve evidence and find the root cause | RS.AN-03 | IR-4 | 3.6.1 | Investigation notes |
| RS-05 | Report incidents to the parties that require it, such as DoD within 72 hours under DFARS 252.204-7012 | RS.CO-02 | IR-6 | 3.6.2 | Notifications sent |
| RS-06 | Eradicate the cause and record what was done | RS.MI-02 | IR-4 | 3.6.1 | Closure records |
Recovery is where backups prove themselves. Check that what you restore is clean, and record what you learned. See our disaster recovery plan template.
| ID | What to do | CSF 2.0 | 800-53 | 800-171 | Evidence to keep |
|---|---|---|---|---|---|
| RC-01 | Run the recovery plan and restore from clean backups | RC.RP-01 | CP-10 | — | Recovery log |
| RC-02 | Check backups and restored systems are clean before use | RC.RP-03 | CP-10 | — | Integrity check records |
| RC-03 | Verify restored systems work normally before handing them back | RC.RP-05 | CP-10 | — | Sign-off |
| RC-04 | Keep leadership and stakeholders informed during recovery | RC.CO-03 | CP-2 | — | Status updates |
| RC-05 | Close recovery formally and record lessons learned | RC.RP-06 | IR-4 | — | After-action report |
None of the NIST documents names a product, but all three expect you to know every device, configure it securely, keep it patched and encrypt the data on it. On a mixed fleet of Windows, Mac, iOS and Android, that is a lot of settings to keep consistent.
A CSF assessment compares where you are with where you want to be. CSF 2.0 calls these your current and target profiles: for each of the 106 subcategories, how far the outcome is achieved today, and how far it needs to be. Separately, the four Tiers describe how rigorous your program is as a whole:
| Tier | What it looks like |
|---|---|
| 1 Partial | Ad hoc. Done by individuals, not by policy. |
| 2 Risk Informed | Approved by management, but not applied everywhere. |
| 3 Repeatable | Formal policy, applied consistently and reviewed. |
| 4 Adaptive | Improved continuously based on lessons and threat information. |
If you handle CUI under a DoD contract, you assess yourself against SP 800-171's 110 requirements and post a score in the Supplier Performance Risk System (SPRS). The method is set out in 32 CFR 170.24:
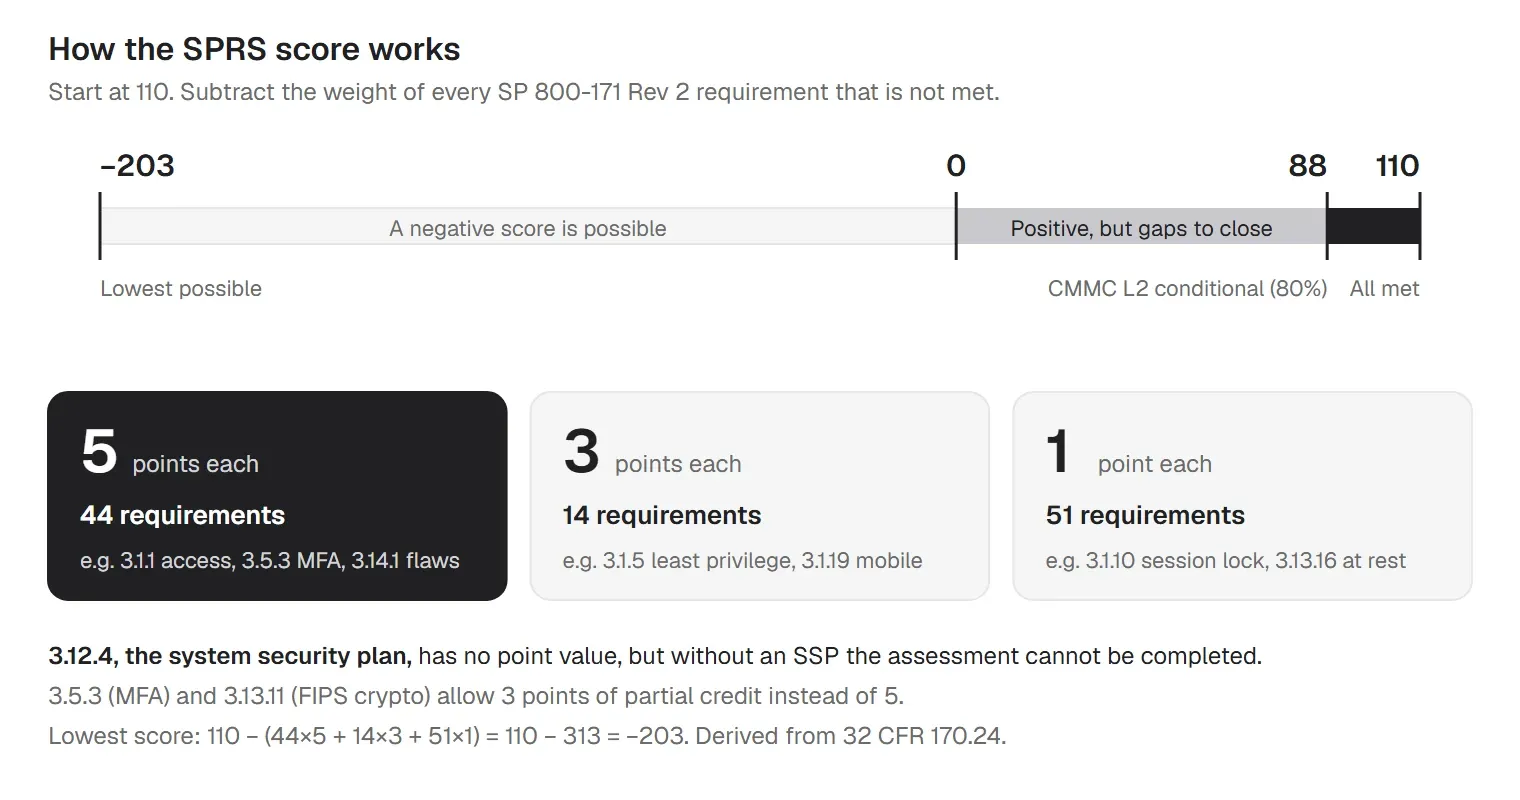
Revision 2 or 3? NIST published Revision 3 in May 2024, with 97 requirements in 17 families, and withdrew Revision 2. DoD contracts still require Revision 2's 110 requirements, and CMMC Level 2 is built on them. In July 2026, DoD suspended the planned November 2026 start of CMMC Phase 2, so contracts can require at most a Level 1 or Level 2 self-assessment for now. Check your contract for the clause that applies to you.
Our CMMC checklist covers the certification side for defense contractors.
SP 800-53 Rev. 5 is the full control catalog for federal systems: 20 families and over 1,000 active controls and enhancements. Release 5.2.0 (August 2025) added three items. You pick a baseline from SP 800-53B based on the system's impact level: Low (149 controls), Moderate (287) or High (370). Our NIST 800-53 checklist covers the families in detail, and the Excel tracker lists the baseline counts for each family.
Whether it is a customer review, an SPRS self-assessment or a federal assessor, the question is the same: can you show the control ran? Dated reports collected over time answer it. A screenshot taken the week before shows one moment.
| Control | Evidence | Refresh |
|---|---|---|
| Inventory | Device and software inventory export | Monthly |
| Encryption | Encryption status per device, keys escrowed | Monthly |
| Patching | Patch compliance by device and severity | Monthly |
| Access | Quarterly access review sign-offs; leaver records | Quarterly |
| MFA | Enrollment report for remote and privileged access | Quarterly |
| Vulnerabilities | Scan reports and the fixes that followed | Monthly |
| Incidents | IR plan, test report, incident log | Yearly and per incident |
| Backups | Backup reports and the last restore test | Quarterly |
| SP 800-171 | System security plan, POA&M, SPRS submission | Yearly and on change |
More NIST guides for IT teams
NIST compliance stays your program: the policies, the assessments and the decisions are yours. trio.so covers many of the device controls in this checklist from one console:
Learn more about compliance automation.
14-day free trial. No credit card required.
Sources. Last reviewed October 2026. This article is guidance, not legal advice. Mappings between frameworks are ours, not official NIST crosswalks.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.
Which NCA ECC-2:2024 controls you can automate, which need people, how small teams should sequence tools, and where device management fits in the stack.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
NIST compliance automation tools by type: GRC platforms, NIST and CISA tools, scanners and device management. What each covers and what it can't.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
ISO 27001 compliance software explained: what each tool type automates, what stays with your team, how to choose one, and where device management fits.
Explore HIPAA compliance automation capabilities, limitations, and implementation steps. Learn what you can automate and what needs human oversight.
What ISO 27001 certification costs a small business: the audit, preparation, tools and staff time, what drives each one, and how to keep the bill down.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients