



Explained
HIPAA Technical Safeguards Explained for IT Teams
HIPAA technical safeguards are the 5 standards in 45 CFR 164.312. What each one requires, required vs addressable, and the device settings that meet it.
What SOC 2 compliance means, who needs it, the Trust Services Criteria, Type 1 vs Type 2, the audit process, cost, and the device controls auditors test.

Content writer, trio.so
SOC 2 compliance means a licensed CPA firm has examined a service organization's controls and issued a SOC 2 report on them. The examination is set by the AICPA and measured against its Trust Services Criteria for security, availability, processing integrity, confidentiality and privacy.
Companies get SOC 2 reports because their customers ask for them. If you sell software or run systems that hold customer data, a large customer's security review will often start with "send us your SOC 2 report".
This guide explains what the report is, who needs one, what the criteria ask for, how the audit works, what it costs, and where IT teams carry most of the work: identities and devices. When you are ready to plan the work, our SOC 2 compliance checklist lists 69 controls with the evidence auditors sample.
In short
When a company says it is SOC 2 compliant, it usually means it has a recent SOC 2 report, ideally a Type 2, with a clean (unqualified) opinion. That is the accurate way to say it: "we have a SOC 2 Type 2 report covering January to December."
Is SOC 2 a certification? No, although many people call it one. There is no SOC 2 certificate and no certifying body. A CPA firm performs an attestation and writes a report. The report describes your system, lists your controls, and, for a Type 2, shows how each control was tested and whether exceptions were found. Customers read it, usually under an NDA.
The CPA firm performs the examination under the AICPA attestation standards (sections AT-C 105 and 205). You may also see "SOC 2.0" or "SOC II". They mean the same report. SOC stands for System and Organization Controls; the older name, Service Organization Control, is still common.
Is SOC 2 mandatory? No law requires it. It is a market requirement: enterprise buyers, regulated customers and procurement teams ask for it before they share data with you.
Any service organization that stores, processes or transmits customer data and sells to businesses that will ask. In practice:
If your customers are consumers, or you hold no customer data, you probably don't need one yet.
SOC 2 reports use the AICPA's 2017 Trust Services Criteria, with points of focus revised in 2022. The 2022 revision added and reworded points of focus, for example on patch management, but did not change the criteria themselves. The criteria are grouped into five categories:
| Category | In scope | What it covers |
|---|---|---|
| Security (common criteria) | Always | Protection against unauthorized access, use and change. 33 criteria. |
| Availability | Optional | Uptime, capacity, backup and recovery. 3 criteria. |
| Confidentiality | Optional | Protecting information you agreed to keep confidential. 2 criteria. |
| Processing integrity | Optional | Complete, accurate, timely processing. 5 criteria. |
| Privacy | Optional | Personal information under your privacy notice. 18 criteria. |
Many first reports cover Security alone, or Security plus Availability and Confidentiality. Add a category only when customers ask for it.
The 33 Security criteria sit in nine series, CC1 to CC9. CC1 to CC5 follow the COSO internal control framework. CC6 to CC9 are extra criteria the AICPA added on top of COSO, and they are where most IT work sits: access, devices, monitoring, change and vendors. The checklist post breaks down every series and the controls that meet it.
A Type 1 report tests whether your controls are designed well, as of a single date. A Type 2 report tests whether they operated effectively over a period, usually 3 to 12 months. Enterprise buyers generally want a Type 2. Some companies get a Type 1 first to answer customers sooner. Our comparison of SOC 2 Type 1 vs Type 2 covers the trade-offs.
The checklist post explains what happens during the audit in more detail, including sampling and the request list.
There are no official figures. Audit firms and compliance vendors publish estimates, and they vary widely with scope, company size and the firm you choose. Typical published ranges:
| Typical estimate | |
|---|---|
| Readiness work | Depends on how many controls you still need to put in place |
| Type 1 | About 3 to 4 months from kickoff |
| Type 2 | A 3 to 12 month period, then a few weeks of fieldwork before the report |
| Audit fee | Vendor estimates range from about $5,000 to $40,000 for a Type 1 and $7,000 to $75,000 for a Type 2 |
Your own staff time is often the larger cost. The checklist post keeps one table of vendor estimates with sources, so the numbers stay in one place.
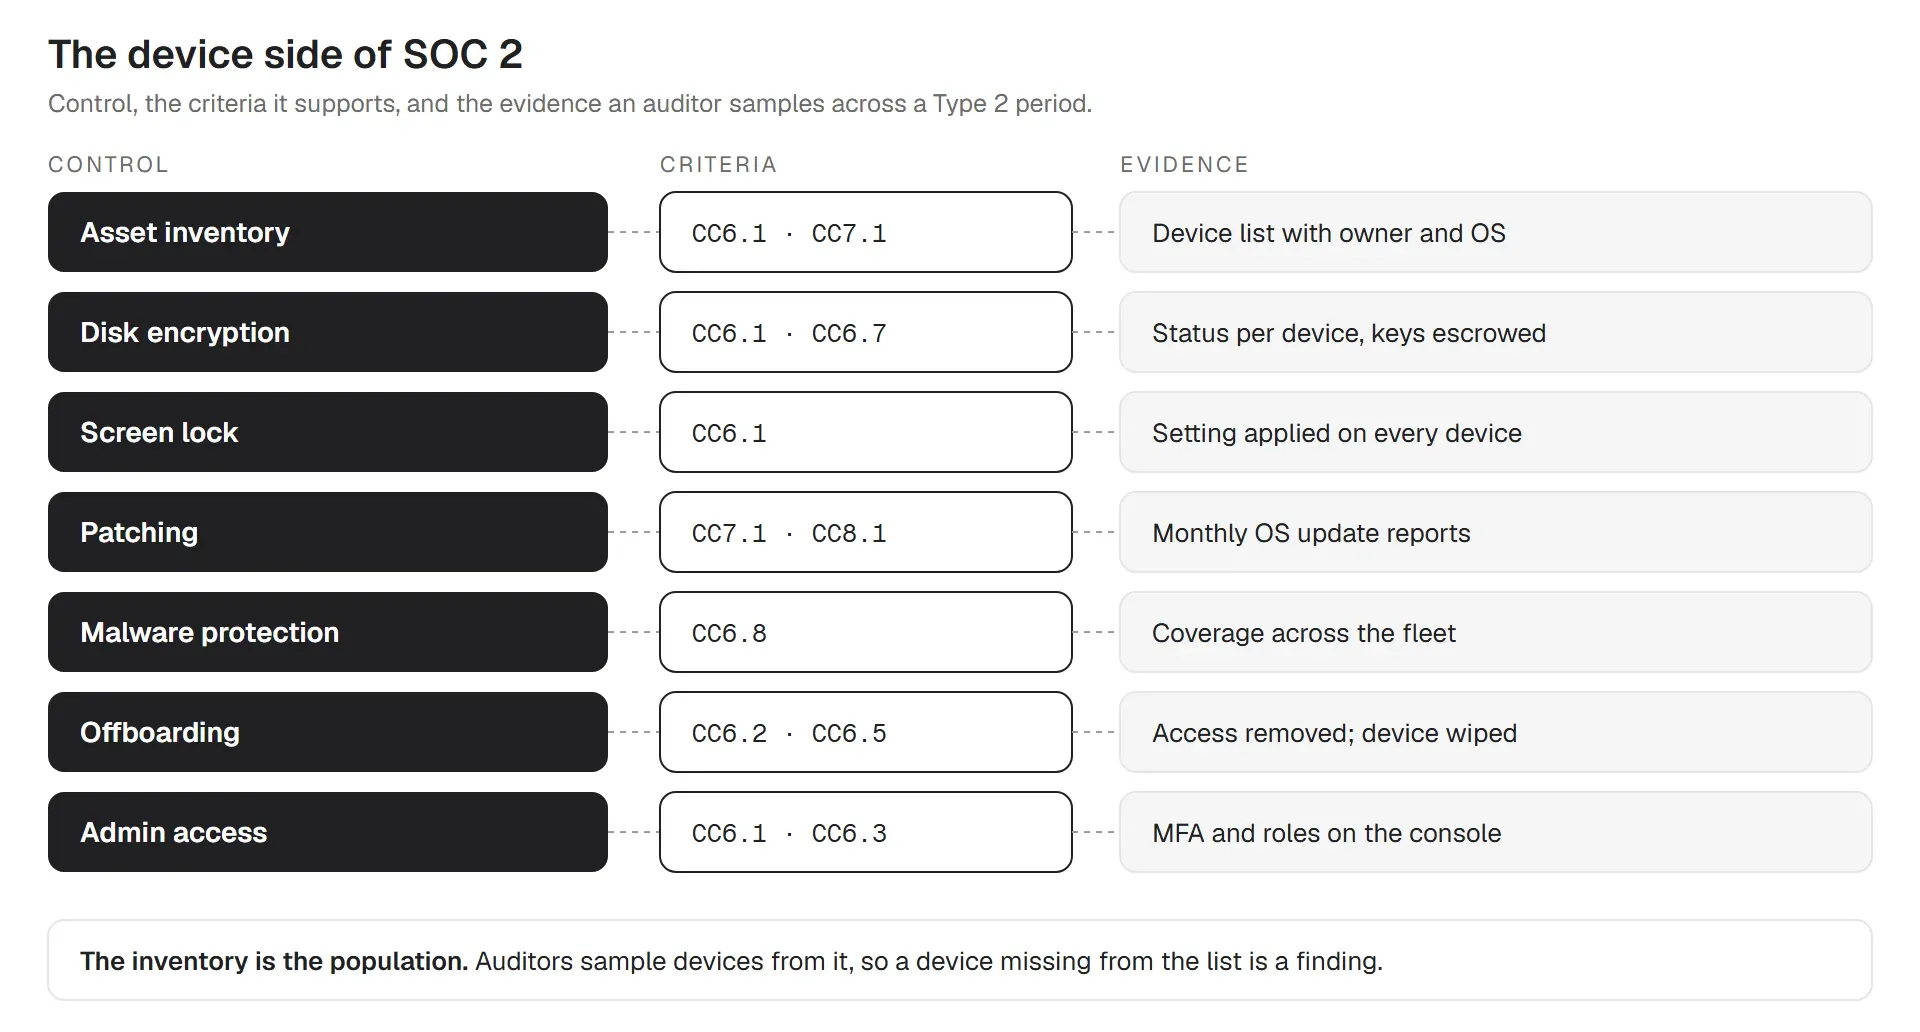
SOC 2 doesn't name products, and it doesn't require MDM by name. But the criteria ask you to inventory, protect and control the devices that reach customer data, and in a Type 2 the auditor checks that across the whole period. That makes laptops and phones a common source of exceptions.
| Control | Criteria | Evidence auditors look for |
|---|---|---|
| Asset inventory | CC6.1, CC7.1 | A complete list of devices with owner and OS. The auditor samples from it. |
| Disk encryption | CC6.1, CC6.7 | Encryption status per device, with recovery keys stored centrally |
| Screen lock and passwords | CC6.1 | The policy, and the setting applied on every device |
| Patching | CC7.1, CC8.1 | OS update reports showing devices current within your policy window |
| Malware protection | CC6.8 | Anti-malware or EDR coverage across the fleet |
| Offboarding | CC6.2, CC6.5 | Access removed on time; device returned, wiped or unenrolled |
| Lost devices | CC6.7, CC7.3 | Lock and wipe records, and the incident decision |
| Admin access | CC6.1, CC6.3 | MFA and roles on the tools that manage your devices |
For MSPs: if you manage devices for clients, each client will review you as a vendor under its own vendor-risk controls (CC9.2), and its auditor may ask to see that review. Keep each client's devices, admins and reports separate, so you can answer one client without exposing another. If you rely on an MSSP for EDR or monitoring, ask for its SOC 2 report, because your auditor will look at how you rely on it.
SOC 2 reports don't expire, but buyers expect a recent one. Buyers usually expect a new report every year, with periods that follow each other without a gap. Between reports, customers may ask for a bridge letter: a letter signed by your management, not the auditor, saying whether controls changed since the last period ended.
Treat SOC 2 as a set of routines, not a project: quarterly access reviews, monthly device reports, a yearly risk assessment and vendor review, and offboarding that removes access the same day.
If you are also weighing ISO 27001, many controls overlap. Our ISO 27001 vs SOC 2 comparison explains the differences, and SOC 2 for small businesses covers the risks of going without a report.
More SOC 2 guides for IT teams
SOC 2 stays your program: the policies, reviews, vendors and the audit are yours. trio.so manages many of the device controls above from one console:
See also our guide to SOC 2 compliance automation and compliance automation in trio.so.
14-day free trial. No credit card required.
Sources. Last reviewed October 2026. Time and cost figures are estimates from audit firms and vendors, not AICPA rules.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
HIPAA technical safeguards are the 5 standards in 45 CFR 164.312. What each one requires, required vs addressable, and the device settings that meet it.
Shadow AI breaches average $4.63M. Here is how to detect shadow AI using DNS logs, OAuth audits, and your endpoint inventory, step by step.
Declarative device management is Apple's answer to MDM polling delays and unreliable compliance data — here's how it works and how to start using it.
An APNS certificate is what lets your MDM platform send commands to iPhones, iPads, and Macs — here's how to create, renew, and protect it.
Device location history works differently on Android, iPhone, and MDM platforms. Here's what each one actually stores and how to access it.
Unlike full-device VPN, per-app VPN tunnels only the apps you choose — and without MDM enforcement, users can bypass it entirely on unmanaged devices.
A remote wipe on a Mac is only possible if the right tools are in place first — here is how MDM, Find My, and native macOS each handle device erasure.
Compare SOC 2 Type 1 and Type 2 audits. Discover key differences, audit scope, duration, and how to choose for compliance needs.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients