



Explained
SCIM Security: Strengthening Identity Management
Learn how SCIM security enhances identity management with encryption, authentication, and access control.
What excessive permissions are, how privilege creep builds them up, the risks, and how to find and remove them with access reviews and least privilege.

Content writer, trio.so
Excessive permissions are access rights that a user, administrator, app or service account holds beyond what its job needs: a sales rep who can open payroll files, an intern in the Domain Admins group, a laptop user who is a local administrator, an integration with write access to every mailbox. They build up quietly through privilege creep, and they turn one stolen password or one wrong click into a much bigger incident. You find them with an access review of admin groups, roles and shared data, and you fix them by removing what is not used, moving people onto roles, and making admin rights temporary.
If an audit finding or an admin group that keeps growing is why you are here, start with how to find excessive permissions; the risks section is there to help you make the case for the cleanup.
A permission is excessive when nobody can explain why the account needs it today. The access may have been right once, for a project or a previous role, but it stayed after the reason went away. Common examples:
The opposite of excessive permissions is the principle of least privilege: every account gets the minimum access its task needs, for as long as it needs it.
Privilege creep is the slow growth of access over time. Nobody decides to give a user too much; access is added for good reasons and rarely taken away. It usually happens in a few predictable ways:
Each step is small. Together they leave a directory where many accounts can do far more than the business intends, which is why reviews have to be regular rather than a one-off cleanup.
The original version of this post listed ten risks. They come down to these:
Excessive permissions detection is mostly an access review: list who has access, compare it with what their role needs, and check what has not been used. Start with the accounts that can do the most damage.
Begin with the groups and roles that grant administrative control, and count their members. On a Windows PC, list the local Administrators group:
Get-LocalGroupMember -Group "Administrators"
In Active Directory, list the members of the most powerful groups, including nested groups:
Get-ADGroupMember -Identity "Domain Admins" -Recursive | Select-Object Name, SamAccountName
Get-ADGroupMember -Identity "Enterprise Admins" -Recursive | Select-Object Name, SamAccountName
On a Mac, the admin group shows which local accounts are administrators:
dscl . -read /Groups/admin GroupMembership
On Linux, check who can use sudo (the group is sudo on Debian and Ubuntu, wheel on Fedora and RHEL):
getent group sudo wheel
In Microsoft Entra ID, open Roles & admins in the Microsoft Entra admin center and review who holds Global Administrator and the other privileged roles. Do the same for the admin roles in Google Workspace, your cloud provider and each important SaaS app.
For each person, ask their manager or the system owner a simple question: does this person need this access for the work they do now? Write the answer down. An access review template keeps the evidence in one place, which is also what an auditor will ask to see.
Unused permissions are the easiest to remove. Useful signals:
Review sharing on drives and sites that hold sensitive data, links shared with "anyone", and the third-party apps connected to Microsoft 365 or Google Workspace with broad scopes. These rarely show up in a group review but often hold the data that matters most.
Fixing excessive user permissions is a mix of cleanup and changing how access is granted, so the problem does not grow back.
Local admin rights deserve their own attention because they are the most widespread case. A user who is an administrator on their own laptop can install unapproved software, turn off disk encryption or antivirus, and give malware the same rights. The usual reason they keep admin rights is that they need to install or update apps. Deploying those apps centrally removes that reason. For Macs, see Mac administrator accounts and how to let standard users install programs on a Mac.
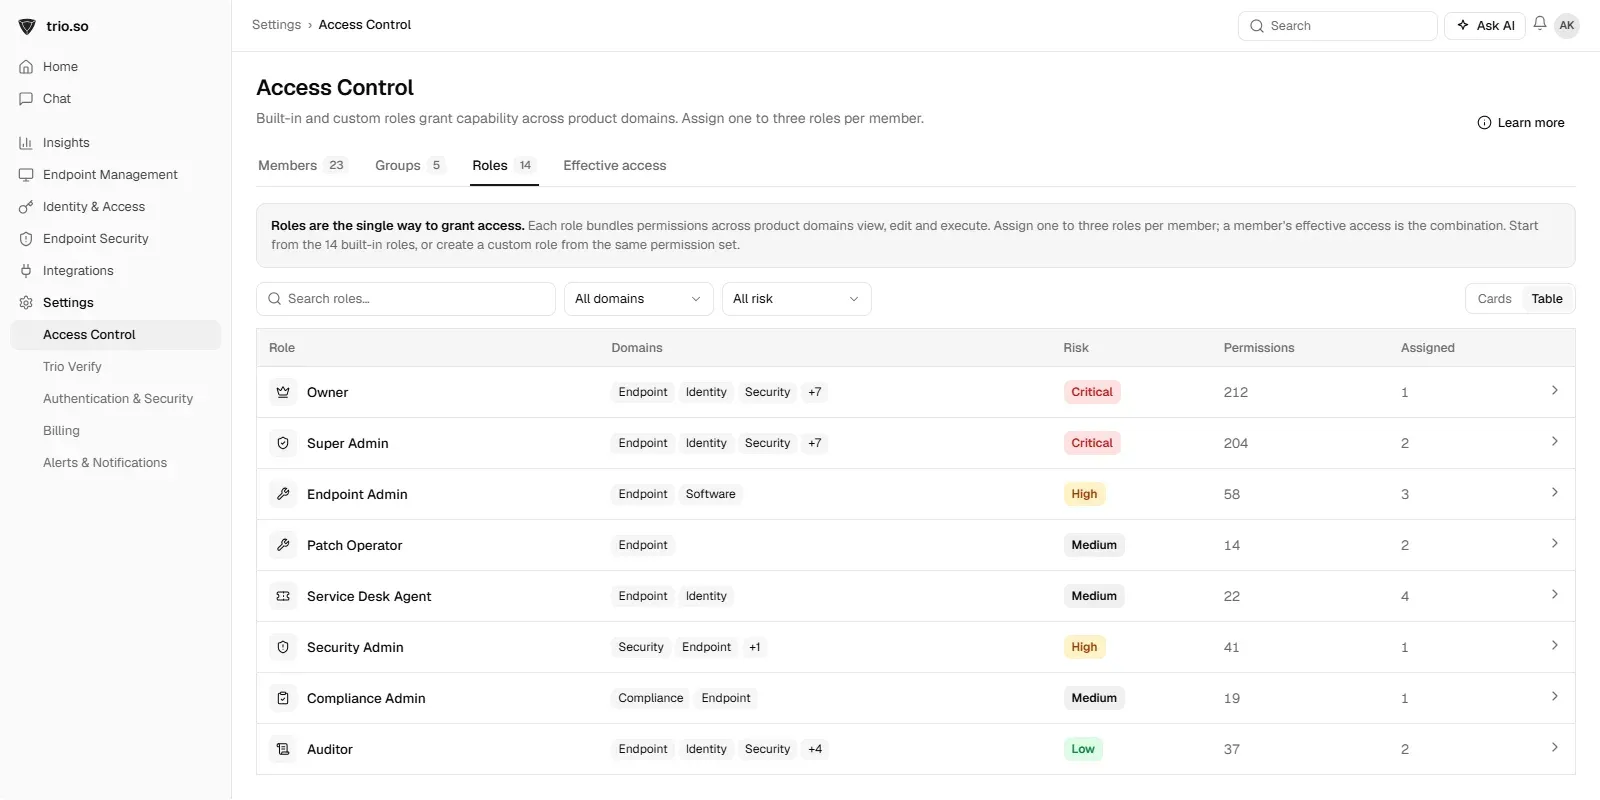
Least privilege applies to the IT team's own tools too. In trio.so, IT staff get console access through roles, with one to three roles per person: built-in roles such as Endpoint Admin, Patch Operator, Service Desk Agent or Auditor, or custom roles you define for your own team. And trio.so deploys apps to enrolled Macs: App Store apps through Apple MDM and uploaded installers, so users never need an admin password for them. See Apple device management.
Related reading: the least privilege access model and privileged access management best practices.
trio.so gives IT staff console access through built-in and custom roles, one to three per person.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Learn how SCIM security enhances identity management with encryption, authentication, and access control.
Discover Cloud Security Posture Management (CSPM) and how it helps businesses like yours protect their valuable cloud infrastructure.
Explore credential management software for IT managers. Learn key features, benefits, and how to choose the right solution for your organization.
Struggling with access governance in IT? Strong policies and best practices can protect sensitive information and boost your cybersecurity efforts.
Seven cybersecurity metrics every business should track, the difference between KPIs and KRIs, and how to measure security culture.
Discover how Digital Asset Management (DAM) improves business efficiency by centralizing digital content and enhancing collaboration.
Discover effective strategies for Defense Against BYOD Threats. Learn to safeguard your organization while embracing the benefits of personal devices.
What XProtect does on a Mac, whether it runs by itself, how to check its version and last update, and where it stops, with a fleet check for IT teams.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients