




School
Digital Literacy in Education: Its Importance & Strategies
This complete guide explores the importance of digital literacy in education and strategies for fostering these critical skills in both students and teachers.
The main student privacy concerns in schools today, the laws that protect student data (FERPA, COPPA, PPRA, state laws), and a checklist for schools.

Content writer, trio.so
The main student privacy concerns today are edtech apps that collect more data than they need and share it with third parties, AI tools that students feed personal information into, monitoring software on school devices, data breaches and ransomware at schools and their vendors, lost or stolen devices holding student records, and biometric systems such as face or fingerprint scanning. In the US, student data is protected mainly by FERPA (education records), COPPA (online services used by children under 13), PPRA (surveys on sensitive topics), CIPA (internet safety in schools that receive E-rate funding) and a growing number of state laws; in Europe, the GDPR applies. Schools protect student data best by collecting less, vetting every vendor, limiting who can see records, encrypting their devices, and having a breach plan ready.
If you run a school or its IT, the laws table and the checklist near the end are the practical parts; if you are a parent, the FERPA section explains what you are entitled to see and ask for.
Schools hold some of the most sensitive data anyone collects about children: grades, attendance, disciplinary records, special education plans, health information, family circumstances and, increasingly, a record of everything a student does online at school. That data follows students. A disciplinary note, a mental health flag or a learning disability record that leaks or is shared carelessly can affect how a student is treated for years, and children cannot meaningfully consent to how their data is used.
There is also a practical reason. Schools are a frequent target for ransomware and data theft because they hold valuable personal data and often have small IT teams. Keeping fewer records leaves less for an attacker to take.
Schools have real reasons to watch what happens on their networks: US schools that receive E-rate funding must filter harmful content, and staff want early warning of bullying or self-harm. But monitoring that reads every message, follows students home on school laptops or flags them by keyword can do harm of its own: it can chill what students search for and write, produce false alarms, and expose sensitive topics, such as a student researching their sexuality or health. Most privacy advocates argue for a balance: monitor what the law and student safety require, tell students and parents what is monitored, keep the data briefly, and limit who sees alerts.
Schools and their apps often collect data because they can, not because they need it: browsing histories, location, device details, behavior scores. Every extra field is something that can leak, be misused or be requested years later.
A typical school uses dozens or hundreds of apps, many adopted by individual teachers. Each one may collect student data, use it for analytics or advertising, or share it with other companies. Privacy policies change, and free tools are often paid for with data.
Students and teachers paste essays, questions and personal details into AI chatbots and AI features inside learning apps. Schools need to know which tools are approved, whether the vendor trains its models on student input, and how long that input is kept.
Software that scans student email, documents and browsing for signs of risk can help, but it collects a great deal of sensitive data and can flag students wrongly. Its scope, retention and who receives alerts should be written down and shared with families.
Attacks on schools and their software suppliers have exposed millions of student records. The breach at the student information system provider PowerSchool, disclosed in January 2025, showed how one vendor incident can affect students and staff across many districts at once.
A teacher's laptop left on a bus, or a stolen office PC, can hold spreadsheets of student names, grades and health notes. If the device is not encrypted, the loss can become a reportable data breach.
Fingerprint lunch systems, face recognition at doors and proctoring software that films students at home all collect biometric data, which some states regulate strictly (Illinois' Biometric Information Privacy Act, for example).
Parents often do not know what data is collected, which apps hold it or how long it is kept. That makes it hard for them to use the rights the law gives them.
Not all student data is equal. A useful way to review what you hold is to sort it into three groups.
| Type | Examples | Approach |
|---|---|---|
| Necessary | Name, date of birth, contact details, enrollment, attendance, grades, special education and health information needed for care | Collect, protect, limit access to staff who need it |
| Situational | Disciplinary records, counseling notes, free-meal eligibility, device and account logs | Collect only when there is a clear purpose; keep for a set time |
| Unnecessary or intrusive | Detailed browsing histories kept long-term, location tracking outside school, social media monitoring, biometrics where an ID card would do | Avoid, or collect only with a documented reason and parental notice |
Data minimization (collecting less and deleting it when it is no longer needed) is the single most effective privacy measure, because records that have been deleted cannot be exposed in a later breach.
This is a summary, not legal advice; check the primary sources linked by the US Department of Education's Student Privacy Policy Office and the Federal Trade Commission, and your own state's law.
| Law | Who it covers | What it requires |
|---|---|---|
| FERPA (1974) | Schools and colleges that receive US Department of Education funding | Parents (and students from age 18) can see and seek to correct education records; schools need consent to disclose them, with exceptions |
| COPPA (1998, FTC rule amended 2025) | Operators of online services directed to children under 13, or that know they collect from them | Verifiable parental consent before collecting children's personal information; schools may consent for purely educational use |
| PPRA (1978) | Surveys and evaluations funded by the US Department of Education, and some other school activities | Parental consent or notice before students answer questions on protected topics |
| CIPA (2000) | Schools and libraries receiving E-rate discounts | An internet safety policy, content filtering, monitoring minors' online activity, and teaching online safety |
| State laws | Schools and edtech vendors in each state | Limits on how vendors use student data, such as bans on targeted advertising and selling data |
| GDPR | Schools and services processing data of people in the EU (UK GDPR in the UK) | A lawful basis for processing, data minimization, security, and rights to access and erasure |
FERPA protects education records at schools that receive funding from US Department of Education programs, which covers nearly all public schools. Parents have the right to inspect and review their child's records, to ask for records they believe are wrong to be corrected, and to consent before personally identifiable information is disclosed. Exceptions include school officials with a legitimate educational interest, directory information (if parents were told and given the chance to opt out), and health and safety emergencies. When a student turns 18 or enters college, the rights pass to the student.
COPPA applies to companies, not schools: operators of websites, apps and online services aimed at children under 13 must get verifiable parental consent before collecting a child's personal information. FTC guidance lets a school give that consent on parents' behalf when the service is used only for the school's educational purpose and not for commercial ones. The FTC's amended COPPA Rule took effect in June 2025, with compliance required by April 22, 2026; among other changes, it requires separate parental consent before children's data is disclosed to third parties, for example for targeted advertising, a written data retention policy and a written information security program.
PPRA requires parental consent before students take part in surveys funded by the US Department of Education that ask about protected areas, such as political beliefs, mental health, sexual behavior, illegal behavior, religion or family income. Schools must also notify parents and let them opt out of certain other surveys and of some uses of student data for marketing.
Schools and libraries that receive E-rate discounts must adopt an internet safety policy, filter images that are obscene or harmful to minors, monitor minors' online activities, and teach students about appropriate online behavior. It is the reason most US schools run web filtering; see websites schools commonly block.
Most US states have passed student privacy laws since 2014, many modeled on California's Student Online Personal Information Protection Act (SOPIPA). They typically stop edtech vendors from using student data for targeted advertising, building profiles or selling it. Some go further: Illinois' Student Online Personal Protection Act (SOPPA) requires schools to publish the vendors they share student data with, and New York's Education Law 2-d requires a parents' bill of rights and data protection terms in vendor contracts. Check your state's law before signing with a new vendor.
In the EU, and under the UK GDPR in the UK, schools and their vendors must have a lawful basis for processing student data, collect only what they need, keep it secure, and honor access and erasure requests. In the UK, online services likely to be used by children also have to follow the Age Appropriate Design Code.
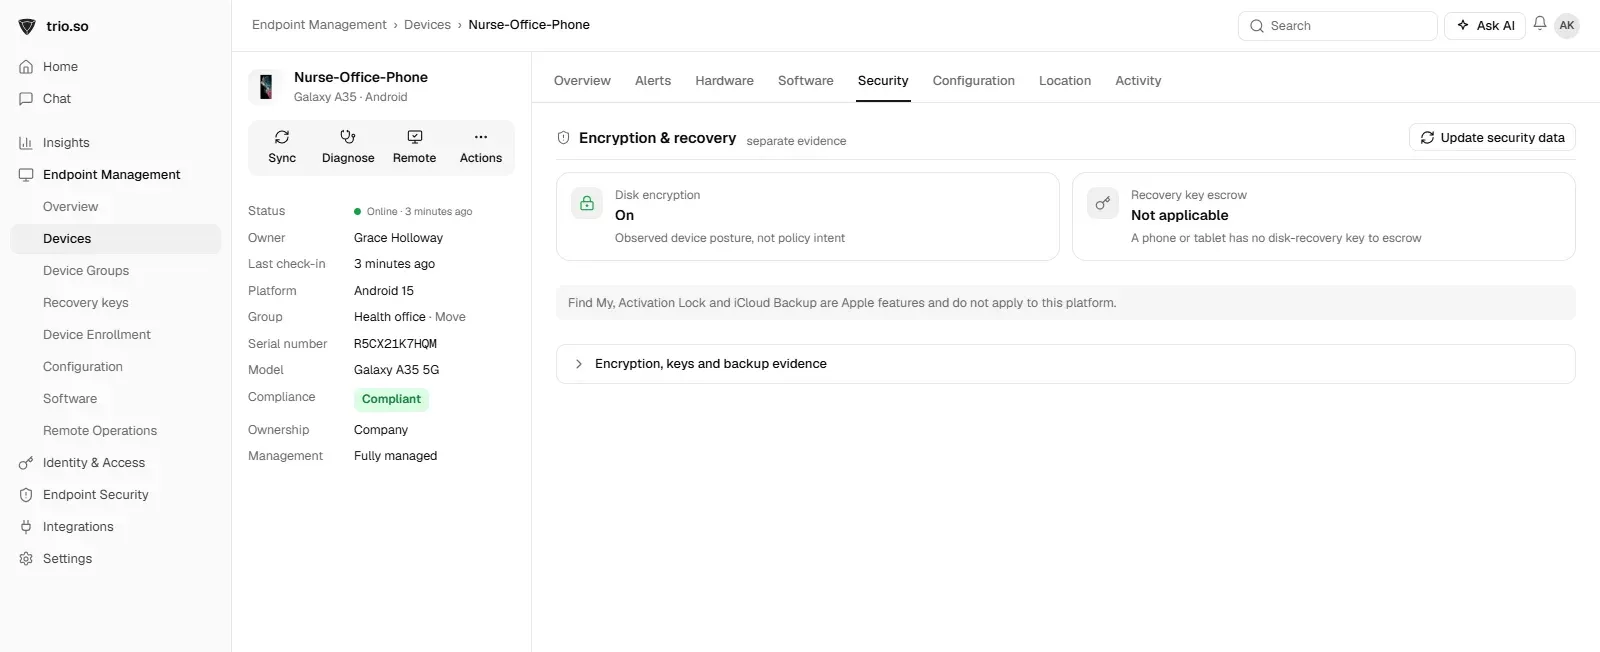
Laws and policies only hold if the devices that store student data are protected. trio.so shows whether school laptops, tablets and phones are encrypted, and can lock or wipe a lost school-owned device from the console. It covers the device part of protecting student data; it does not make a school compliant with FERPA, COPPA or any other law on its own. See school device management.
Related reading: BYOD in schools and screen time in schools.
trio.so shows which school devices are encrypted and can lock or wipe a lost one from the console.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
This complete guide explores the importance of digital literacy in education and strategies for fostering these critical skills in both students and teachers.

The transformative benefits of AI in education for students, from personalized learning to enhanced accessibility, while addressing potential challenges.
As screens permeate classrooms & virtual learning, it is crucial to understand the relationship between screen time in schools & academic performance.

The main dangers of the internet for students, from cyberbullying to scams, and what students, parents, teachers and schools can do about each.

This guide delves into the intricacies of cyberbullying in schools, shedding light on the multifaceted strategies required to combat it effectively.

Learn social media etiquette for students to build a positive online presence. Simple tips for students from trio.so.
Explore best practices for implementing effective and balanced school internet filtering to ensure both safety and access to educational resources.
Best classroom management software to help school administrators elevate educational experience & academic growth in the digital realm.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients