



Explained
How to Delete a Windows Service From the Command Line
How to delete a Windows service with sc delete or PowerShell, fix "marked for deletion", and what to check first. One PC or many.
Intune vs SCCM compared: cloud vs on-premises, co-management, Configuration Manager's future, and which fits a small, mid-size or hybrid fleet.

Content writer, trio.so
Intune is Microsoft's cloud service for managing devices. SCCM, now called Microsoft Configuration Manager, is software you install on your own servers to manage Windows PCs and servers. Choose Intune if your devices are mostly remote, mixed or cloud joined and you want no management servers. Choose Configuration Manager if you run a large on-premises Windows estate that needs OS imaging, distribution points and deep software deployment. Many companies run both through co-management and move one workload at a time.
No, SCCM is not deprecated. Microsoft still releases Configuration Manager current branch updates and now groups it with Intune in one product family. The facts in this post come from Microsoft Learn pages checked on 26 October 2026.
Microsoft Intune is a cloud-based service for managing devices and apps. You run it from the Intune admin center in a browser, with no servers of your own. Devices enroll through Microsoft Entra ID, and Intune pushes configuration profiles, compliance policies, apps and updates to them over the internet.
Per Microsoft's supported platforms page, Intune supports Windows, macOS, iOS and iPadOS, Android and Linux (Ubuntu Desktop and Red Hat Enterprise Linux). Windows devices are typically set up with Windows Autopilot instead of a custom image.
System Center Configuration Manager was renamed Microsoft Endpoint Configuration Manager and is now just Configuration Manager, part of the Microsoft Intune family of products. It is software you install and run yourself: site servers, a SQL Server database, distribution points that hold content, and a client on every managed PC.
Microsoft describes it as a tool to deploy applications, software updates and operating systems across many devices, run real-time actions, manage compliance settings and report on all of it. It integrates with Active Directory, WSUS, Group Policy, the Windows ADK and Windows Deployment Services. It is built around Windows.
| Area | Intune | Configuration Manager (SCCM) |
|---|---|---|
| Where it runs | Microsoft's cloud. No servers for you to run. | Your own servers (or VMs in your cloud): site server, SQL, distribution points. |
| Platforms | Windows, macOS, iOS and iPadOS, Android, Linux. | Windows clients and servers. Other platforms through Intune and co-management. |
| Best network fit | Remote and internet-connected devices. | Devices on the corporate network or reaching it through a cloud management gateway. |
| OS deployment | Windows Autopilot sets up a new device the first time it starts. | Task sequences with PXE, bare metal imaging and in-place upgrades. |
| App deployment | Apps from stores, MSI, Win32 packages and more, delivered from the cloud. | Applications and packages from distribution points, with fine-grained deployment rules and Software Center. |
| Patching | Windows Update policies and update rings. | Software update management through WSUS, with detailed scheduling and reporting. |
| Identity | Microsoft Entra ID. | Active Directory, with Entra ID for cloud features. |
| Infrastructure to maintain | None on your side. | Servers, SQL, content distribution, and updating the site on Microsoft's release cadence. |
| Licensing | Subscription. Check Microsoft's current licensing pages. | Licensed as part of the Microsoft Intune family. Check Microsoft's current licensing pages. |
The short version of the trade-off: Intune removes infrastructure and works anywhere the device has internet. Configuration Manager gives you more control and more depth for Windows on a network you own, and costs you servers and people to run them.
You do not have to pick one. Co-management lets a Windows device be managed by both Configuration Manager and Intune at once. You decide, workload by workload, which one is the authority. Per Microsoft, co-management supports these workloads: compliance policies, Windows Update policies, resource access policies, Endpoint Protection, device configuration, Office Click-to-Run apps and client apps. Configuration Manager keeps managing everything you do not switch.
The requirements Microsoft lists include a supported Configuration Manager current branch version, devices that are Microsoft Entra joined or Microsoft Entra hybrid joined, and Intune and Entra ID licensing. Entra-registered only devices are not supported. Internet-based devices need a cloud management gateway to reach Configuration Manager.
Co-management is also the usual migration path. Start with compliance policies and Windows Update, pilot on a collection of devices, then move the next workload. Devices that stay on Configuration Manager keep working throughout.
If you run Intune and Configuration Manager together, watch for conflicts when both try to set the same thing. Use the workload sliders to give each setting one owner.
As of 26 October 2026, Microsoft has not announced an end of life for Configuration Manager current branch. Microsoft Learn says it plans to release updates for current branch a few times per year, and each version is supported for 18 months from general availability. Only the newest version gets both security and critical updates.
What is true is that Microsoft's direction is cloud. Configuration Manager now lives under the Microsoft Intune documentation and brand, and co-management is the bridge it documents. That is a direction, not a retirement date. Do not plan around a date that Microsoft has not published, and check the current branch lifecycle page before you commit to a multi-year project.
For a small or mid-sized company, Intune is usually the simpler fit. There is no server to build or patch, new laptops can ship to employees and enroll themselves, and remote staff are managed the same way as people in the office. Configuration Manager asks for a site server, SQL, content distribution and someone who knows how to run them, which is hard to justify for a one-person IT team.
Configuration Manager still makes sense when you already own it, run hundreds or thousands of Windows PCs on a controlled network, image machines in bulk, or need its depth for software distribution and reporting. For those companies the question is rarely "which one" and more often "how fast do we attach Intune".
| Your situation | Start here |
|---|---|
| Under a few hundred devices, remote or mixed, no existing Configuration Manager | Intune |
| Mid-size, mostly Windows, mostly on the network, existing Active Directory | Configuration Manager, with Intune attached through co-management for compliance and Conditional Access |
| Large Windows estate with imaging and strict change control | Configuration Manager with a staged co-management plan |
| Hybrid: office PCs plus remote laptops plus phones | Intune for remote and mobile, Configuration Manager for the office fleet until workloads move |
| Macs, Linux and Android next to Windows from one team | Intune covers them, or a cross-platform UEM (next section) |
Intune and Configuration Manager are strongest for a Windows and Microsoft 365 company. If your fleet is a real mix of Windows, Macs, Linux, iPhones and Android phones, or you want one console without a Microsoft licensing stack, a cross-platform unified endpoint management (UEM) tool is a third route. See our comparison of Intune alternatives, the WSUS vs SCCM explainer, and the trio.so vs Microsoft Intune comparison.
If your devices are not all Windows, trio.so manages Windows, macOS, Linux, iOS and Android from one console. Windows PCs, Macs, iPhones, Android devices and Linux machines sit in the same device list. Read more about unified endpoint management.
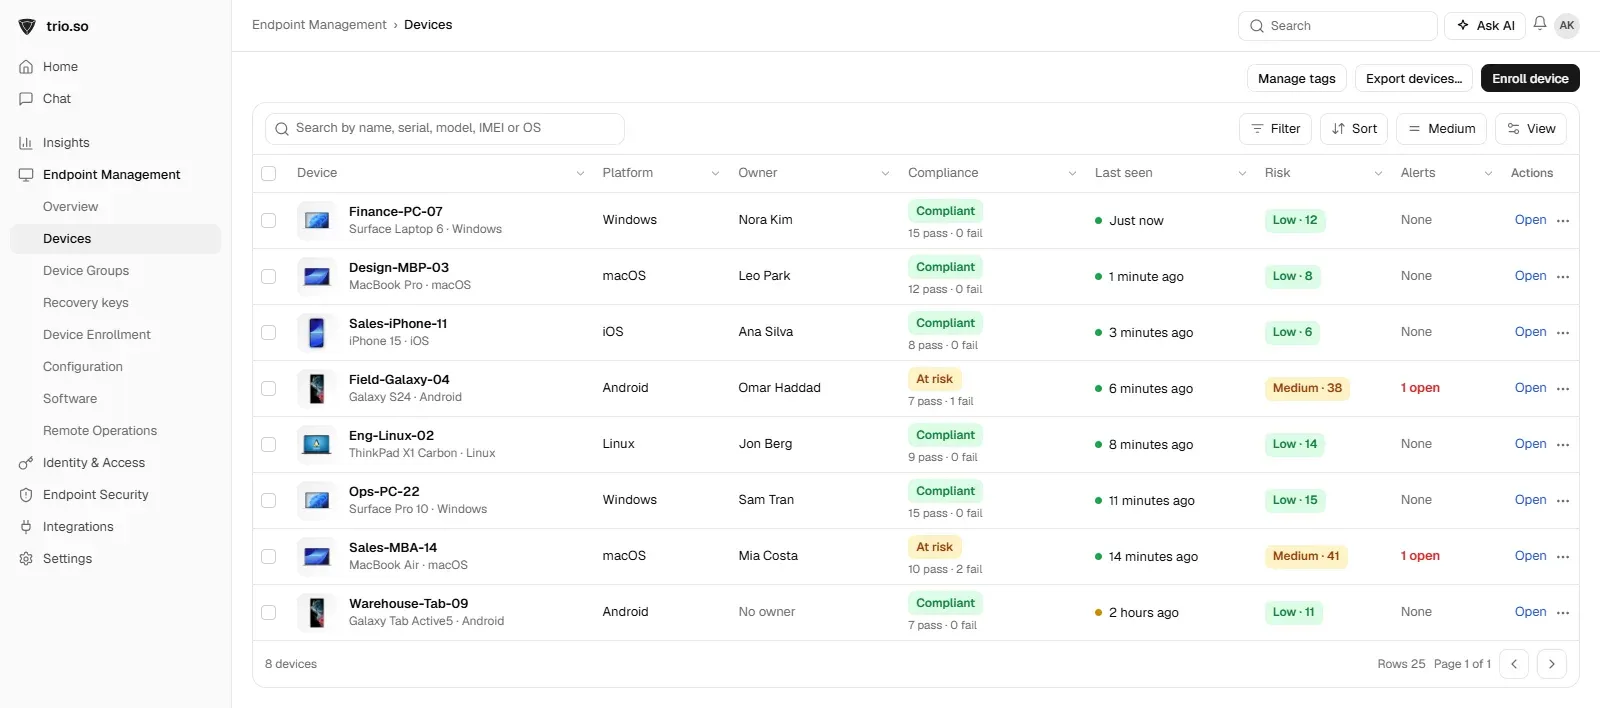
trio.so manages Windows, macOS, Linux, iOS and Android devices from one console.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
How to delete a Windows service with sc delete or PowerShell, fix "marked for deletion", and what to check first. One PC or many.
Disable Control Panel and Settings with Group Policy: the exact policy, its registry value, how to exempt admins and how to allow only some items.
Disable a GPO safely: disable the link, disable user or computer settings, or unlink it, and why to leave the Default Domain Controllers Policy alone.
Turn on Remote Desktop for Windows machines with Group Policy: the exact policy path, the firewall rule, NLA, and how to check it worked.
Windows 11 has no classic Guest account to switch on, but the hidden one can be disabled or deleted. Steps for one PC and for every PC by policy.
What is picture password in Windows 11? Read this blog to learn about its benefits, how to enable it, how to troubleshoot, and the best practices.
Get past "You must enable system protection on this drive". Turn on System Protection and run System Restore from the command prompt on Windows 10.

Back up files on Windows 10 and 11 from Command Prompt with robocopy, xcopy and wbadmin, plus a ready-to-use backup script you can schedule.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients