

Templates
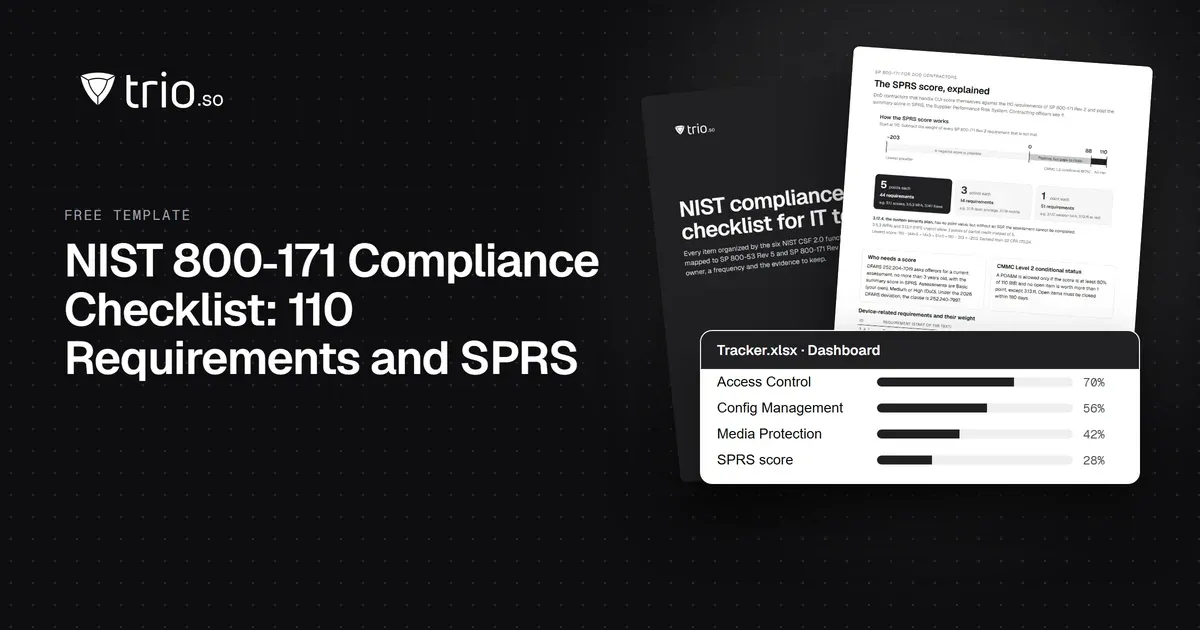
NIST 800-171 Compliance Checklist: 110 Requirements and SPRS
A NIST 800-171 compliance checklist with all 110 Rev. 2 requirements, their SPRS points, Rev. 3 changes, CMMC status and a self-assessment guide. Free Excel.
Secure your business with PCI DSS compliance. Explore our essential PCI DSS checklist and ensure you’re protecting sensitive payment data effectively.
Payment Card Industry Data Security Standards, or PCI DSS, play a critical role in protecting sensitive cardholder data and are essential for businesses that process, store, or transmit credit card information. This blog will walk you through what a PCI DSS checklist entails, why it’s essential, and a structured template of PCI DSS in its full form to streamline your compliance journey.
PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards designed to ensure that all companies that accept, process, store, or transmit credit card information maintain a secure environment. The goal is to protect cardholder data, prevent data breaches, and reduce fraud in card transactions. Created by the PCI Security Standards Council (SSC) — comprising major card brands like Visa, Mastercard, and American Express — PCI DSS compliance is mandatory for any business handling credit card transactions, regardless of size or transaction volume. The standards are comprehensive and cover multiple security aspects, from physical security to encryption, access controls, and monitoring. Non-compliance can result in hefty fines, reputational damage, and the potential loss of the ability to process card payments.
PCI DSS compliance is more than just meeting regulatory requirements. Compliance with these standards helps organizations:
PCI DSS compliance is divided into four levels, determined by the volume of transactions a business processes each year. Each compliance level has specific requirements:
The higher your level, the more rigorous the compliance requirements and audits. For example, Level 1 requires a yearly Report on Compliance (ROC) by a Qualified Security Assessor (QSA), while lower levels may only need to complete a Self-Assessment Questionnaire (SAQ). Each guarantees its own PCI DSS certification. 
Below is a structured PCI DSS compliance checklist that every organization handling payment card data should consider. This PCI DSS audit checklist includes the 12 primary PCI DSS requirements, with each broken down into actionable steps.
Here’s a PCI DSS checklist template to streamline your PCI DSS compliance process:
Once you’ve achieved PCI DSS compliance, it’s crucial to keep up with industry trends and security improvements. Here are some best practices:
Failing to comply with PCI DSS standards can be costly. Here are some common mistakes to avoid:
Failing to comply with PCI DSS can lead to substantial penalties, including:
PCI DSS compliance is essential for protecting your business and your customers from the risks associated with payment data breaches as part of your vulnerability management program. This checklist offers a practical roadmap for achieving and maintaining compliance, ensuring that your business adheres to stringent security and IT compliance standards. By taking the steps above and continuously monitoring your systems, you can avoid costly breaches, protect sensitive cardholder data, and maintain the trust of your customers. Interested in simplifying PCI DSS compliance for your organization? Try Trio’s comprehensive Mobile Device Management security solution with a free demo today and take the first step toward a secure, compliant payment environment.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
A NIST 800-171 compliance checklist with all 110 Rev. 2 requirements, their SPRS points, Rev. 3 changes, CMMC status and a self-assessment guide. Free Excel.
A SOC 2 compliance checklist for IT teams: 69 controls mapped to the Trust Services Criteria, with the evidence auditors sample. Free PDF and Excel.
Learn what each Conditional Access policy template does and when to use it. Download ready-to-use ACP templates for identity security.
Complete SAMA compliance checklist for Saudi financial institutions. Domain-by-domain requirements, obligations, and practical implementation steps.
The NCA compliance checklist your team actually needs: ECC-2:2024 domains, NCNICC-1:2025, and what auditors look for as evidence.
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Feeling overwhelmed by CCPA? Use this comprehensive CCPA Compliance Checklist to secure customer data on mobile devices. Discover how MDM simplifies compliance.
Need an MDM audit checklist? Our guide covers 7 key areas & compliance strategies to ensure your mobile device management is secure and efficient.