



Templates
NCA ECC Compliance Checklist for ECC-2:2024 (PDF + Excel)
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
SAMA compliance checklist for the SAMA CSF: 4 domains and 32 subdomains, maturity levels 0 to 5, evidence and owners, with a free PDF and Excel tracker.

Content writer, trio.so
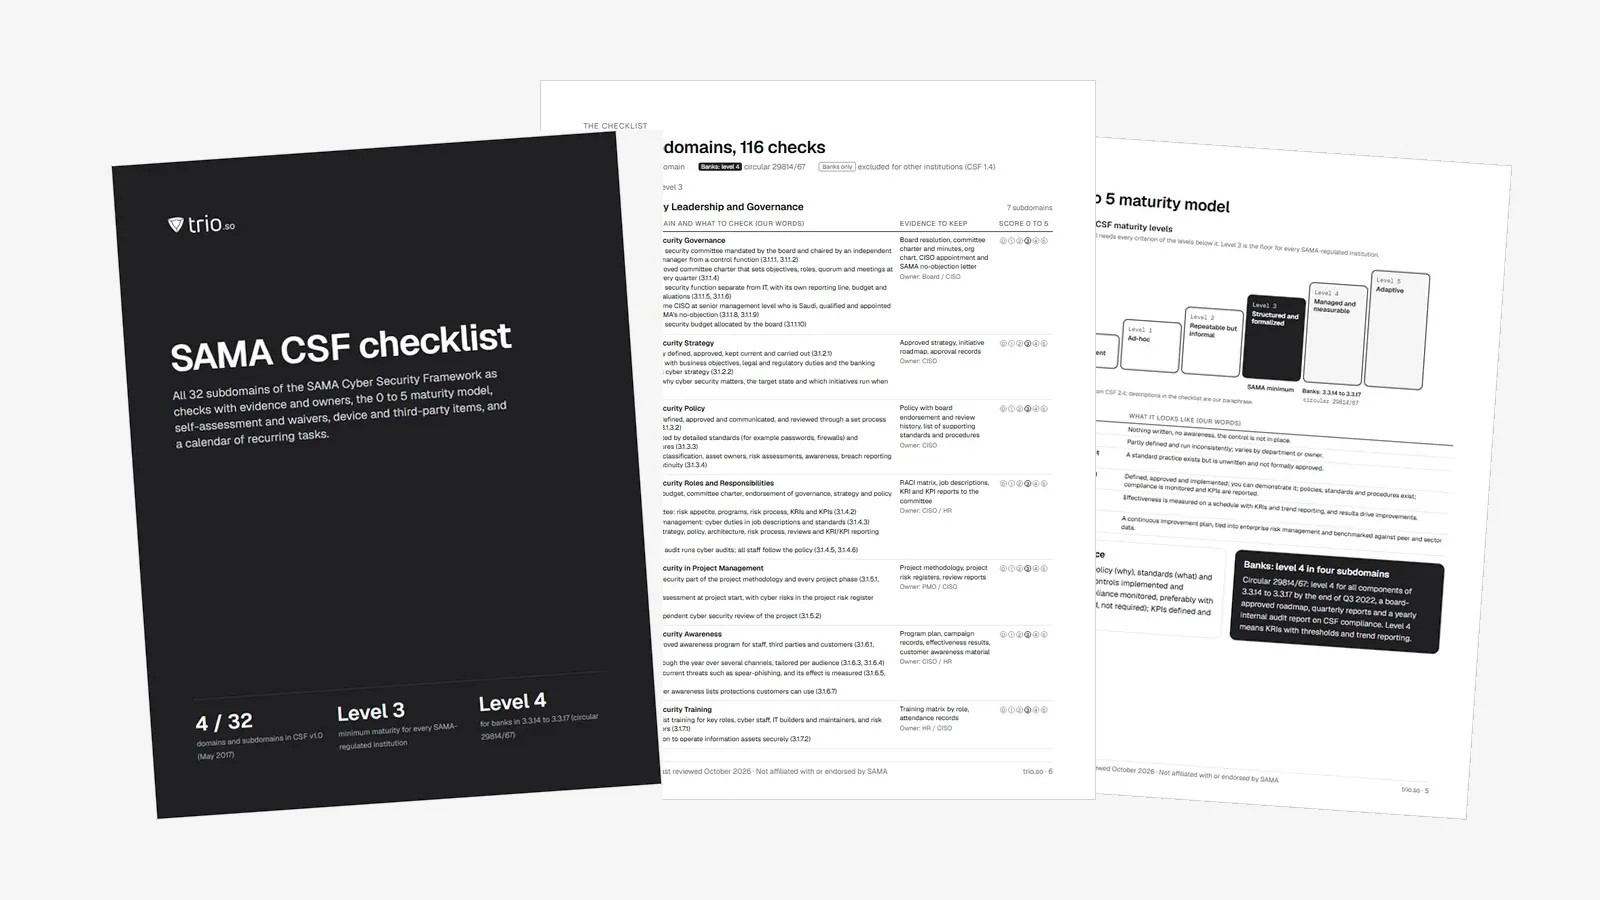
A SAMA compliance checklist turns the Saudi Central Bank's Cyber Security Framework (SAMA CSF) into tasks you can assign, score and prove. This one covers all 4 domains and 32 subdomains of CSF v1.0, broken into 116 checks with the evidence to keep and a suggested owner for each.
It is written for CISOs, IT managers and compliance leads at banks, finance companies, payment service providers and credit bureaus regulated by SAMA. Use it for a gap assessment, to score each subdomain on SAMA's 0 to 5 maturity scale, and to prepare the evidence behind your self-assessment.
The free download has a PDF guide and an Excel tracker with a maturity score per subdomain, targets that switch to level 4 where banks need it, an evidence register, a device tab, a third-party tracker, a task calendar and a dashboard.
In short
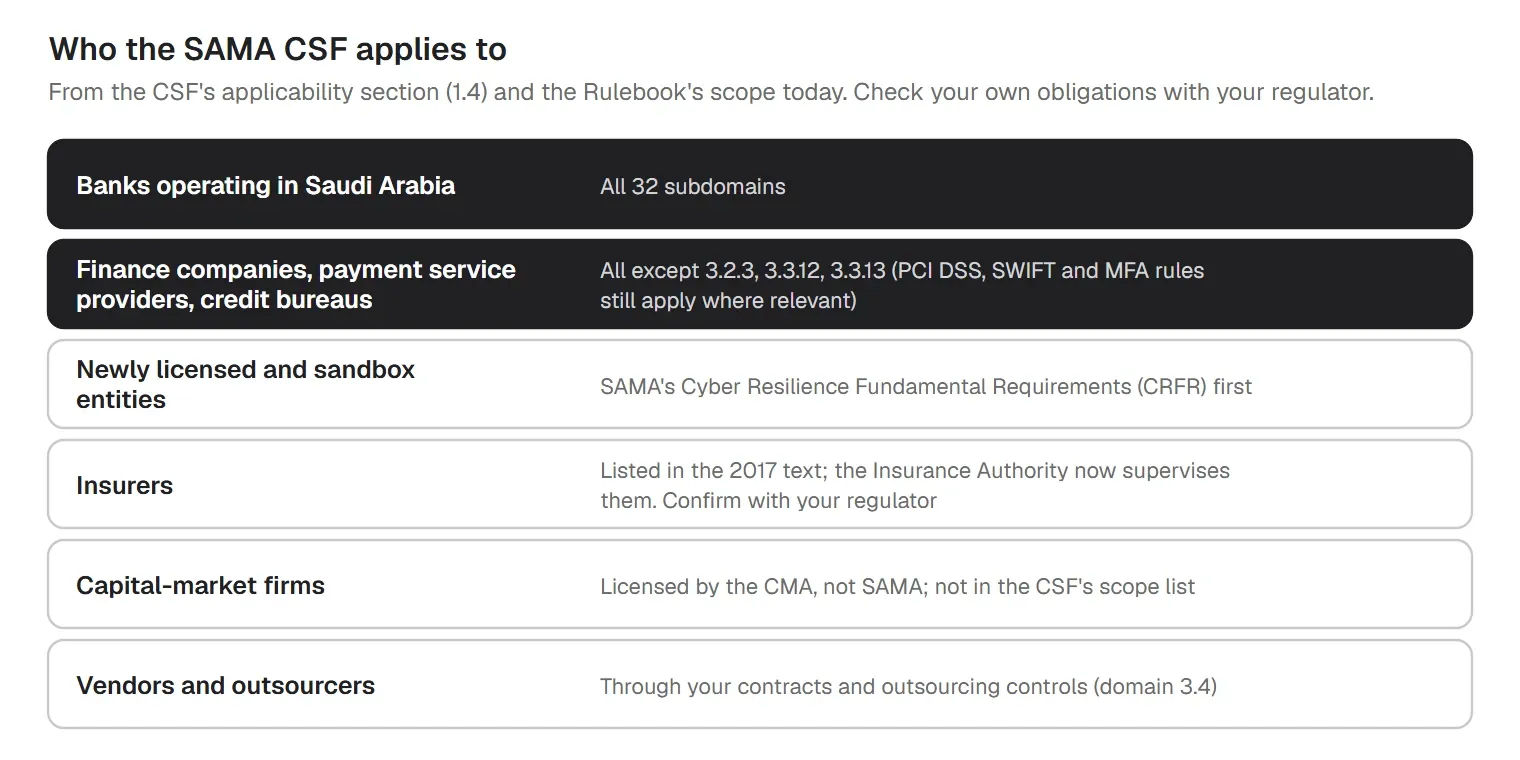
The CSF applies to the financial institutions SAMA regulates, which the framework calls Member Organizations. Today the Rulebook lists the banking sector, finance companies, payment systems and payment service providers, credit bureaus and the Regulatory Sandbox. Banks follow all 32 subdomains. Other institutions skip three of them and must align with the banking sector's cyber strategy (3.1.2) only where it applies:
The 2017 framework text also lists insurers and reinsurers. The Insurance Authority now supervises the insurance sector, so insurers should confirm with it which cyber rules apply to them. Capital-market firms are licensed by the Capital Market Authority, not SAMA, and are not in the CSF's scope list. Newly licensed and sandbox fintechs start with SAMA's Cyber Resilience Fundamental Requirements. Our guide to SAMA compliance covers scope, history and the related SAMA rules in more depth.
Each row below is one CSF subdomain. The subdomain names and the numbers in brackets are SAMA's; the checks are our short summary, not SAMA's wording. Read the full control considerations in the SAMA Rulebook before you score yourself.
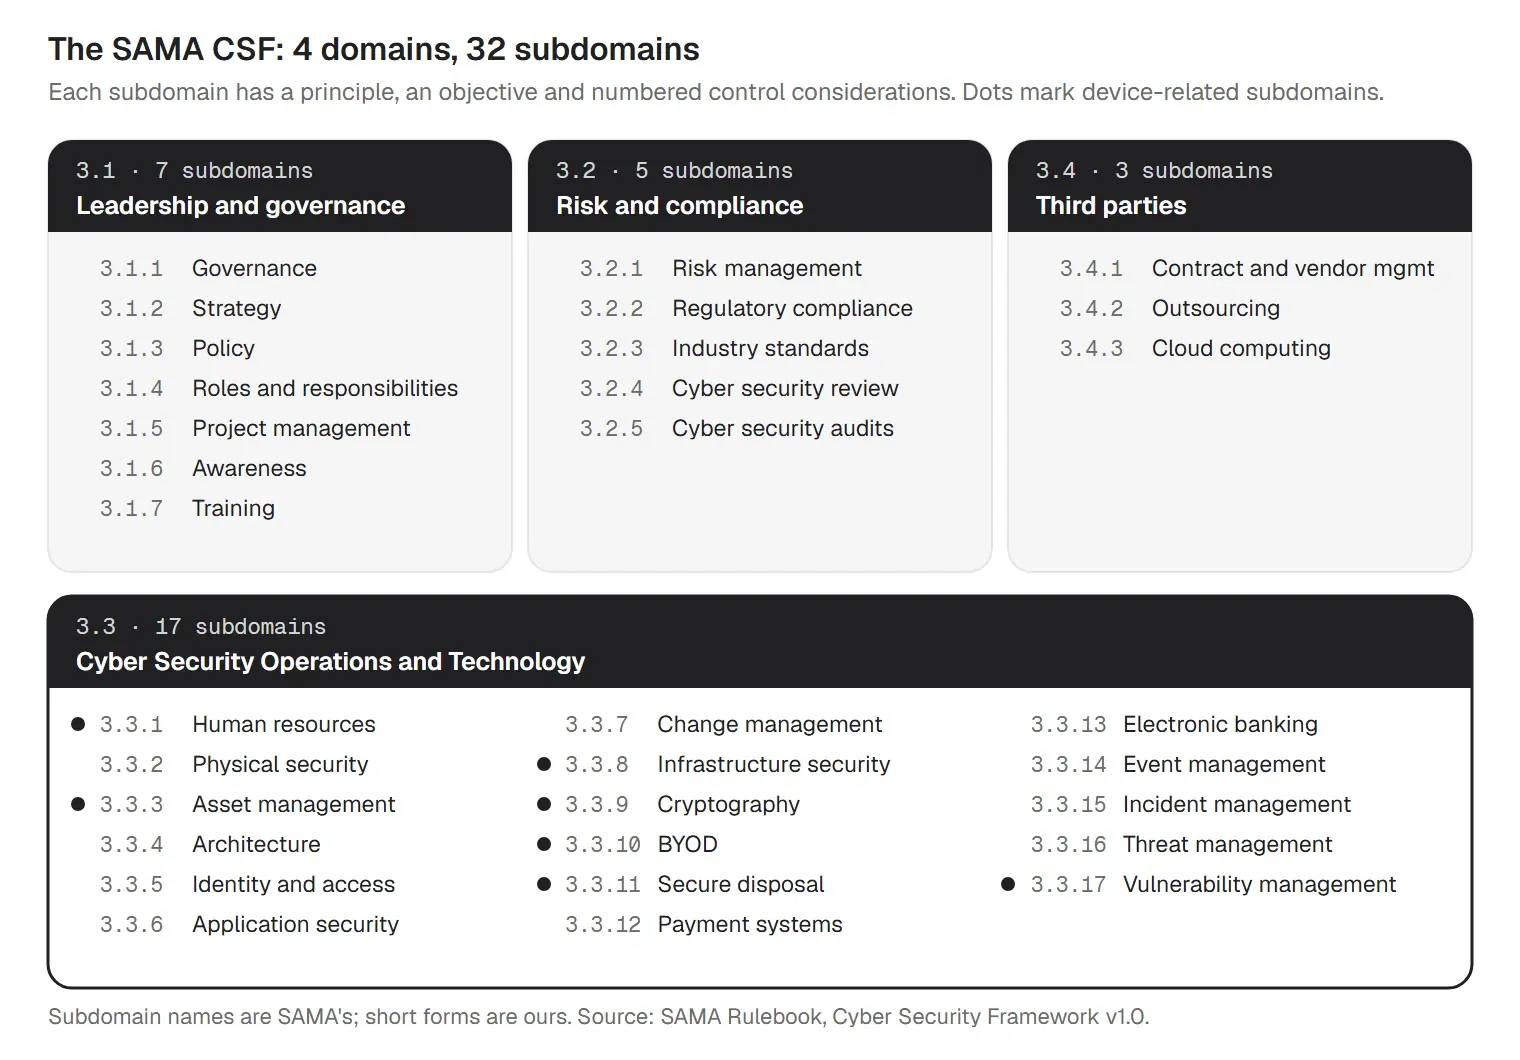
Seven subdomains about who owns cyber security. Expect SAMA to ask for board papers, the committee charter and the CISO's appointment first.
| ID | Subdomain | What to check (our words) | Evidence to keep |
|---|---|---|---|
| 3.1.1 | Cyber Security Governance |
| Board resolution, committee charter and minutes, org chart, CISO appointment and SAMA no-objection letter |
| 3.1.2 | Cyber Security Strategy |
| Approved strategy, initiative roadmap, approval records |
| 3.1.3 | Cyber Security Policy |
| Policy with board endorsement and review history, list of supporting standards and procedures |
| 3.1.4 | Cyber Security Roles and Responsibilities |
| RACI matrix, job descriptions, KRI and KPI reports to the committee |
| 3.1.5 | Cyber Security in Project Management |
| Project methodology, project risk registers, review reports |
| 3.1.6 | Cyber Security Awareness |
| Program plan, campaign records, effectiveness results, customer awareness material |
| 3.1.7 | Cyber Security Training |
| Training matrix by role, attendance records |
Five subdomains about how you find, treat and review cyber risk, and how you keep up with regulation and industry standards.
| ID | Subdomain | What to check (our words) | Evidence to keep |
|---|---|---|---|
| 3.2.1 | Cyber Security Risk Management |
| Risk register, risk treatment plans, risk acceptance sign-offs, approved risk appetite |
| 3.2.2 | Regulatory Compliance |
| Regulatory register, change log for policies and standards |
| 3.2.3 | Compliance with (Inter)national Industry Standards Banks only |
| PCI DSS Attestation of Compliance, SWIFT attestation, EMV records |
| 3.2.4 | Cyber Security Review |
| Review and penetration test reports, follow-up tracker |
| 3.2.5 | Cyber Security Audits |
| Audit plan, audit reports, management responses |
Seventeen subdomains, the largest share of the work. Most device and endpoint items sit here: asset management, infrastructure security, cryptography, BYOD, secure disposal and vulnerability management.
| ID | Subdomain | What to check (our words) | Evidence to keep |
|---|---|---|---|
| 3.3.1 | Human Resources |
| Signed agreements, screening records, leaver checklists with returned devices |
| 3.3.2 | Physical Security |
| Access logs, visitor records, data centre controls, transport and disposal records |
| 3.3.3 | Asset Management |
| Asset register export, ownership list, discovery reports |
| 3.3.4 | Cyber Security Architecture |
| Architecture documents, design principles, review records |
| 3.3.5 | Identity and Access Management |
| IAM policy, access review sign-offs, MFA coverage report, privileged account list |
| 3.3.6 | Application Security |
| Application standards, SDLC, code review records |
| 3.3.7 | Change Management |
| Change tickets with approvals and test results |
| 3.3.8 | Infrastructure Security |
| Hardening standards per platform, configuration reports, compliance review results |
| 3.3.9 | Cryptography |
| Cryptographic standard, key management procedure, encryption status reports |
| 3.3.10 | Bring Your Own Device (BYOD) |
| BYOD standard, signed user agreements, enrollment records, encryption and passcode reports |
| 3.3.11 | Secure Disposal of Information Assets |
| Disposal records, wipe or destruction certificates, provider contracts |
| 3.3.12 | Payment Systems Banks only |
| Payment systems standard, SARIE and mada compliance records |
| 3.3.13 | Electronic Banking Services Banks only |
| E-banking security standard, MFA design, SMS rules, SAMA approvals |
| 3.3.14 | Cyber Security Event Management Banks: level 4 |
| Monitoring standard, SOC procedures and rota, SIEM use cases, SOC test reports |
| 3.3.15 | Cyber Security Incident Management Banks: level 4 |
| Incident procedure, incident register, SAMA notifications and reports |
| 3.3.16 | Threat Management Banks: level 4 |
| Threat intelligence procedure, source list, intelligence reports |
| 3.3.17 | Vulnerability Management Banks: level 4 |
| Scan reports, remediation deadlines per class, patch reports |
Three subdomains about vendors, outsourcing and cloud. Two of them need SAMA's approval before you act.
| ID | Subdomain | What to check (our words) | Evidence to keep |
|---|---|---|---|
| 3.4.1 | Contract and Vendor Management |
| Vendor risk assessments, contract clauses, SLA reports |
| 3.4.2 | Outsourcing |
| Outsourcing register, SAMA approvals, cyber review records |
| 3.4.3 | Cloud Computing |
| Cloud register, SAMA approvals, provider due diligence, contract clauses |
In the Excel tracker every row has a current maturity score, a target, the gap, a status, an owner, a due date and an evidence link.
SAMA measures maturity on a six-level scale, and you reach a level only when every criterion of the levels below it is in place. Every Member Organization should operate at level 3 or higher.
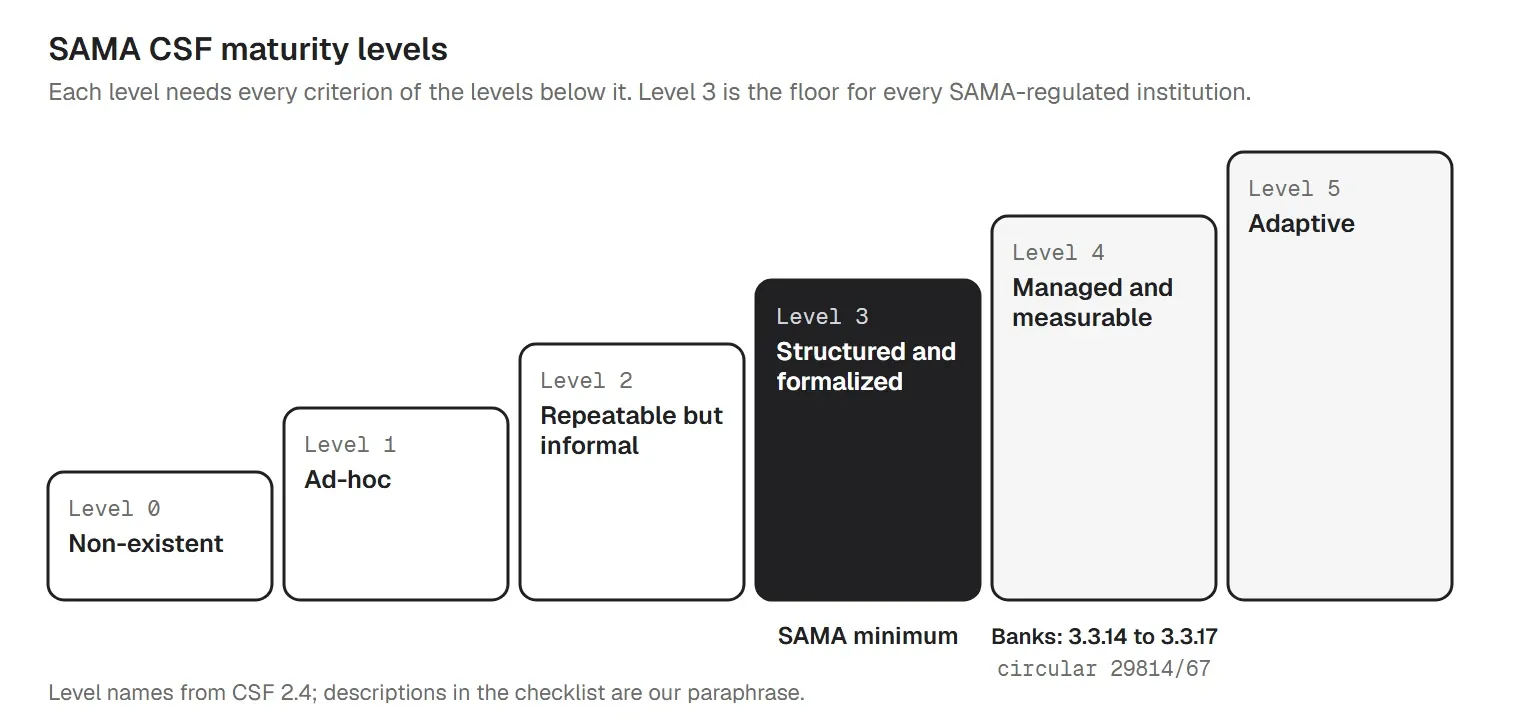
| Level | Name (SAMA) | What it looks like (our words) |
|---|---|---|
| 0 | Non-existent | Nothing written, no awareness, the control is not in place. |
| 1 | Ad-hoc | Partly defined and run inconsistently; varies by department or owner. |
| 2 | Repeatable but informal | A standard practice exists but is unwritten and not formally approved. |
| 3 | Structured and formalized | Defined, approved and implemented; you can demonstrate it; policies, standards and procedures exist; compliance is monitored and KPIs are reported. |
| 4 | Managed and measurable | Effectiveness is measured on a schedule with KRIs and trend reporting, and results drive improvements. |
| 5 | Adaptive | A continuous improvement plan, tied into enterprise risk management and benchmarked against peer and sector data. |
In practice, level 3 for a subdomain means four things you can show:
Banks have a higher bar in four subdomains. SAMA's circular 29814/67 asked banks to reach level 4 for all components of 3.3.14 Event Management, 3.3.15 Incident Management, 3.3.16 Threat Management and 3.3.17 Vulnerability Management, with a target of the end of Q3 2022. Level 4 adds key risk indicators (KRIs) with thresholds, measured on a schedule and used for trend reporting. The same circular asks for a yearly internal audit report on CSF compliance against the required maturity. The tracker sets these targets for you when you pick "Bank" as your institution type.
The CSF is checked through a periodic self-assessment that you complete with SAMA's questionnaire. SAMA then reviews and audits it to set your compliance level and maturity level, and its inspection visits check that the assessment is accurate. The CSF does not state how often the questionnaire runs or its format, so follow the instructions SAMA sends you.
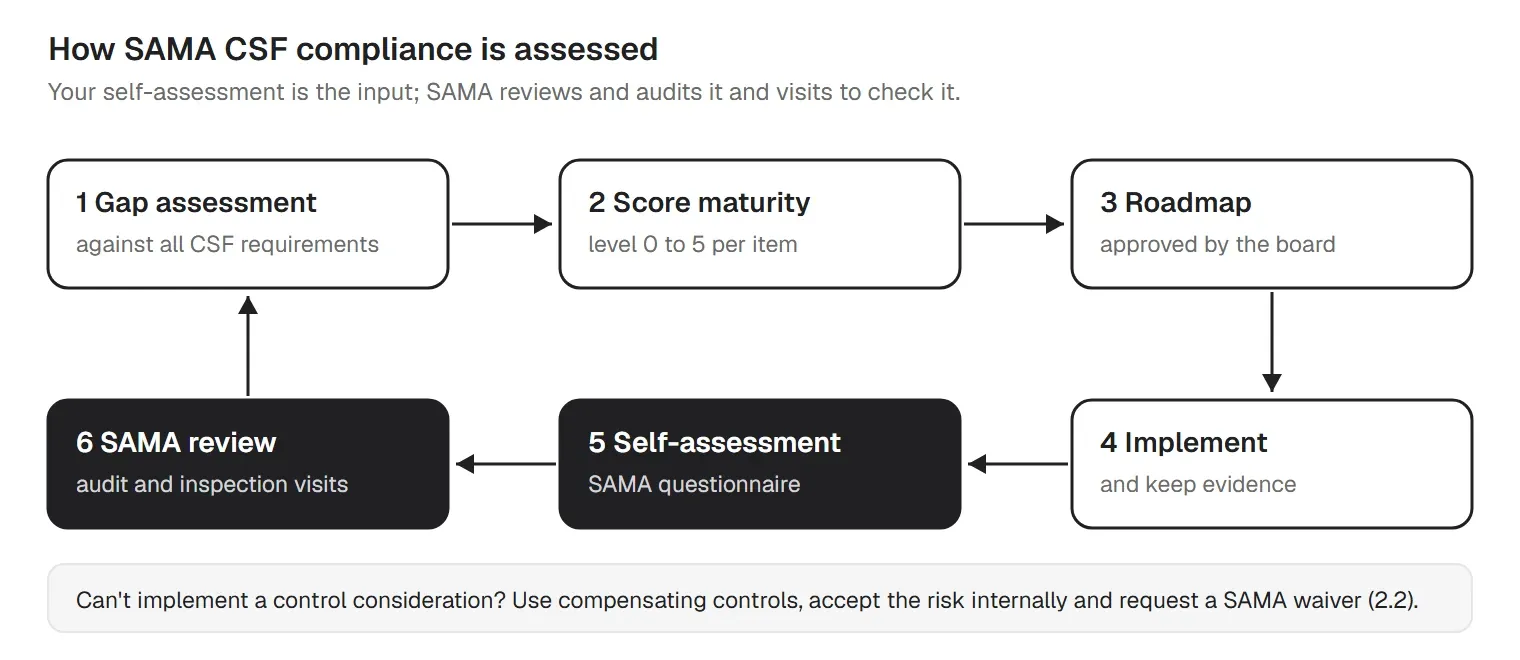
The framework is principle based. When a control consideration cannot be implemented as written, the CSF expects three things: compensating controls, an internal risk acceptance, and a formal waiver request to SAMA (section 2.2 and its Appendix D). Record each one in the tracker, because an exception without a waiver reads as a gap.
The original 2017 circular gave banks a sequence that still works as a project plan: a gap assessment against every requirement, a roadmap to at least level 3 approved by the board, regular progress reports, and follow-up by the cyber security committee.
Laptops, desktops, phones and tablets appear in more places than the BYOD subdomain. The infrastructure security standards in 3.3.8 must cover workstations, laptops, tablets and mobile devices in offices, not only servers in the data centre. This is also where the CSF names mobile device management (MDM): 3.3.10 expects it on personal devices that staff use for work.
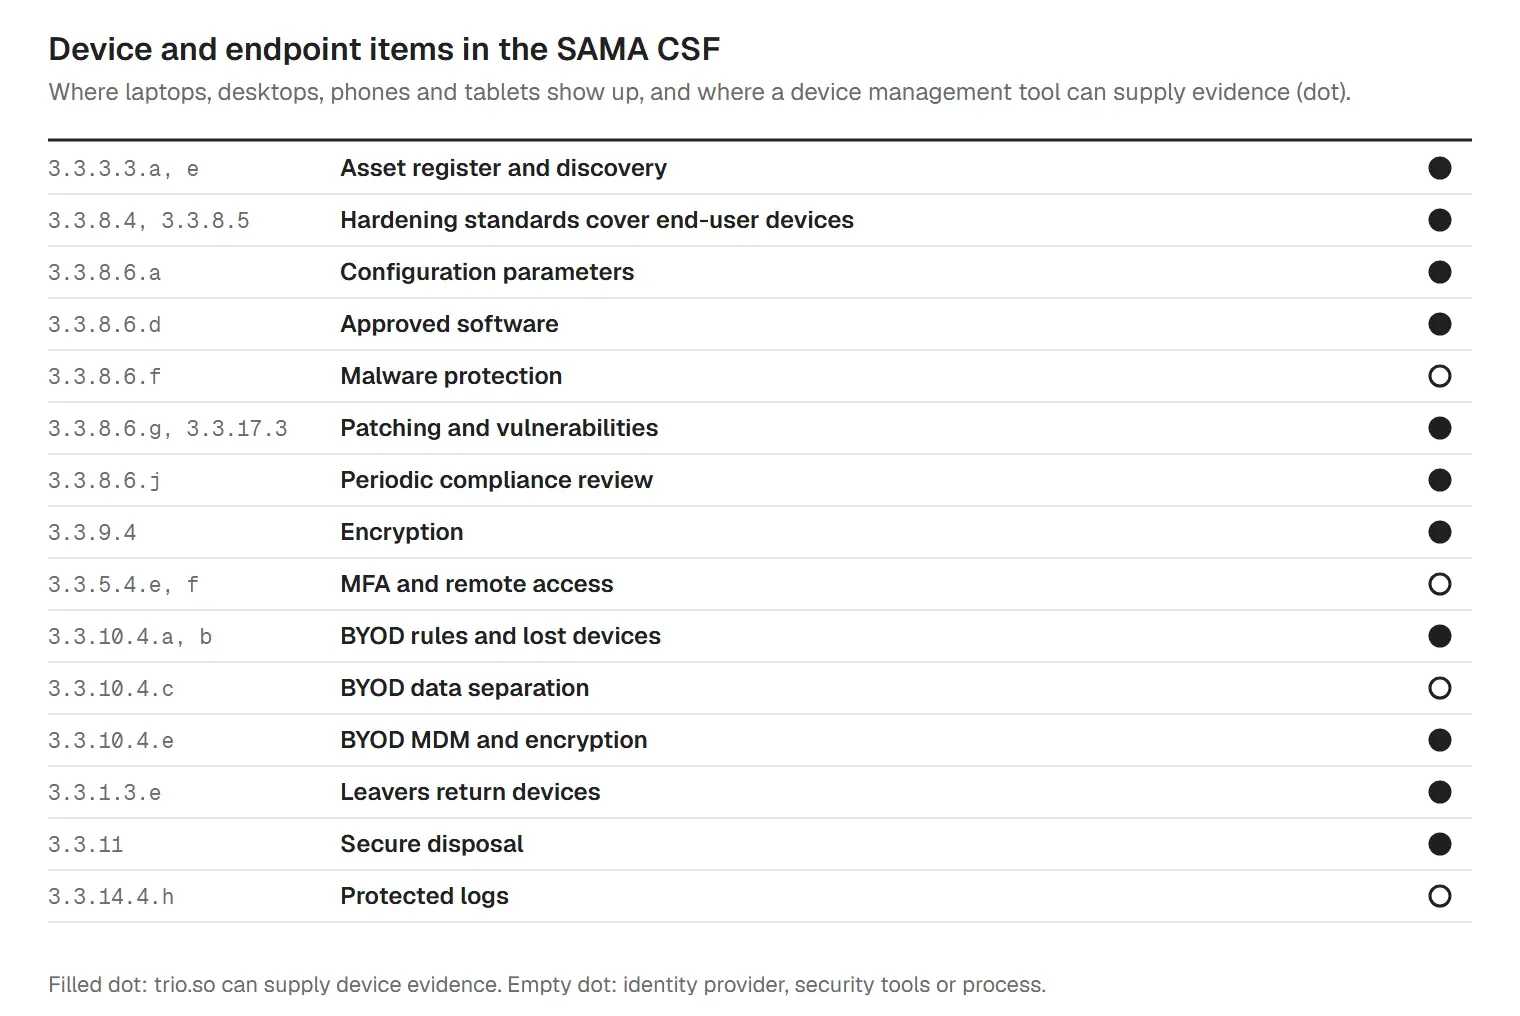
| CSF reference | Topic | What the CSF expects (our words) |
|---|---|---|
| 3.3.3.3.a, e | Asset register and discovery | Every laptop, desktop, phone and tablet sits in one register with an owner; new devices are found, not only typed in |
| 3.3.8.4, 3.3.8.5 | Hardening standards cover end-user devices | Your infrastructure standards name workstations, laptops, tablets and mobile devices in offices as well as data centres |
| 3.3.8.6.a | Configuration parameters | Standards set the configuration each device type must carry |
| 3.3.8.6.d | Approved software | Only approved software runs on devices |
| 3.3.8.6.f | Malware protection | Anti-malware with application allow-listing and APT protection |
| 3.3.8.6.g, 3.3.17.3 | Patching and vulnerabilities | Risk-based scans, fix deadlines per class, a set patch deployment method |
| 3.3.8.6.j | Periodic compliance review | Device standards are checked for compliance on a schedule |
| 3.3.9.4 | Encryption | Approved encryption, when to use it, and key lifecycle management |
| 3.3.5.4.e, f | MFA and remote access | MFA for sensitive and critical systems and all remote access |
| 3.3.10.4.a, b | BYOD rules and lost devices | User duties, training and consequences for tampered, lost or stolen devices and leavers |
| 3.3.10.4.c | BYOD data separation | Business data kept apart from personal data, for example a container |
| 3.3.10.4.e | BYOD MDM and encryption | MDM, device access controls and encryption on personal devices used for work |
| 3.3.1.3.e | Leavers return devices | Access revoked and devices returned when staff leave |
| 3.3.11 | Secure disposal | Data on retired devices made non-retrievable, for example by secure wiping |
| 3.3.14.4.h | Protected logs | Security logs protected from change and loss |
The CSF sets no numbers here: no screen-lock timeout, no patch deadline. You set them in your own standards, and SAMA checks that you follow them. Write the values into your infrastructure and BYOD standards, then keep device reports that show the values are in force. Our BYOD policy template and IT asset management policy template give you a starting text.
Domain 3.4 is short but has two hard gates. Material outsourcing needs SAMA's approval first (3.4.2), and banks also follow SAMA's Rules on Outsourcing. For hybrid and public cloud, you need a risk assessment and due diligence on the provider, SAMA's approval before you use the service or sign, and a contract with cyber terms (3.4.3). Cloud services should in principle be located in Saudi Arabia; using one outside the Kingdom needs SAMA's explicit approval.
For every vendor, check that the contract gives you the right to review and audit, sets an incident escalation route, covers exit and data return, and includes mutual confidentiality (3.4.1). The workbook's third-party tab flags vendors that need a SAMA approval you have not recorded, and cloud services outside Saudi Arabia without one.
Two other rule sets often land on the same team. SAMA's PDPL circular of December 2021 tells SAMA-supervised institutions to align with the Personal Data Protection Law through a gap analysis and a board-approved plan. And banks that NCA treats as critical national infrastructure may need NCA's Essential Cybersecurity Controls (ECC-2:2024) as well as the CSF. No SAMA or NCA document maps one onto the other or says which takes precedence, so check your obligations with both regulators.
If you run both, keep one evidence register and tag each item with the CSF subdomain and the ECC control it supports. The Excel evidence register has a column for the ECC reference. Our NCA ECC checklist has a matching tracker.
Most of the SAMA CSF is governance, risk, operations and third-party work that no device tool does for you. trio.so handles one slice: the laptops, desktops, phones and tablets your staff use, from one console on Windows, macOS, iOS and Android.
In the Excel tracker, the "trio.so can supply" column shows which rows device evidence from trio.so can support, such as the asset register, the infrastructure standards for end-user devices, cryptography and vulnerability management. Our SAMA compliance automation guide explains what else you can automate and what you can't.
trio.so does not assess or certify anything, and it does not do the governance, risk, continuity or third-party parts of the CSF. Your self-assessment and SAMA's review decide your maturity level. Learn more about SAMA CSF compliance in trio.so and compliance automation. Plans start at $5 per device.
14-day free trial. No credit card required.
More SAMA and Saudi compliance guides for IT teams
Sources. Last reviewed October 2026 against the SAMA Cyber Security Framework v1.0 (May 2017), the version in force in the SAMA Rulebook on 27 October 2026. Control-consideration numbers are SAMA's; every description here is our own paraphrase, not SAMA text. The Rulebook's English is a translation and the Arabic text governs. This article is guidance, not legal advice or an assessment. The SAMA Cyber Security Framework is published by the Saudi Central Bank (SAMA). trio.so is not affiliated with or endorsed by SAMA.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
Free MDM audit checklist in Word and PDF: 36 controls with how to test each one, the evidence to collect, a device sample sheet and an Excel tracker.
Free MDM rollout checklist in Word and PDF: requirements, APNs and platform prerequisites, a policy baseline, pilot and go-live forms, plus a tracker.

What J-SOX is, how it differs from US SOX, and a checklist of J-SOX requirements from scoping to the internal control report.
Free TISAX audit checklist in Word and PDF: assessment levels, labels, VDA ISA areas and the evidence to prepare, plus an Excel self-assessment tracker.
Learn how you can improve your resource allocation strategy & download the IT Resource Allocation Template to optimize your IT resource management.
Free IT audit checklist template in Excel, PDF and Word: 66 checks in 8 areas, an audit questionnaire, a findings tracker and a filled-in example.
Free IT contingency plan template in Word and Excel, with a filled-in example: BIA with MTD, RTO and RPO, call tree, recovery steps and test forms.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients