



Templates
Why Every IT Team Needs an IT Resource Allocation Template
Learn how you can improve your resource allocation strategy & download the IT Resource Allocation Template to optimize your IT resource management.
Free TISAX audit checklist in Word and PDF: assessment levels, labels, VDA ISA areas and the evidence to prepare, plus an Excel self-assessment tracker.

Content writer, trio.so
A TISAX audit checklist helps you prepare for the assessment an automotive customer asks for before it shares confidential designs, prototype parts or personal data with you. TISAX (Trusted Information Security Assessment Exchange) is run by the ENX Association. An approved audit provider assesses your company against the VDA ISA catalogue, and you receive labels that your customers can check in the ENX portal.
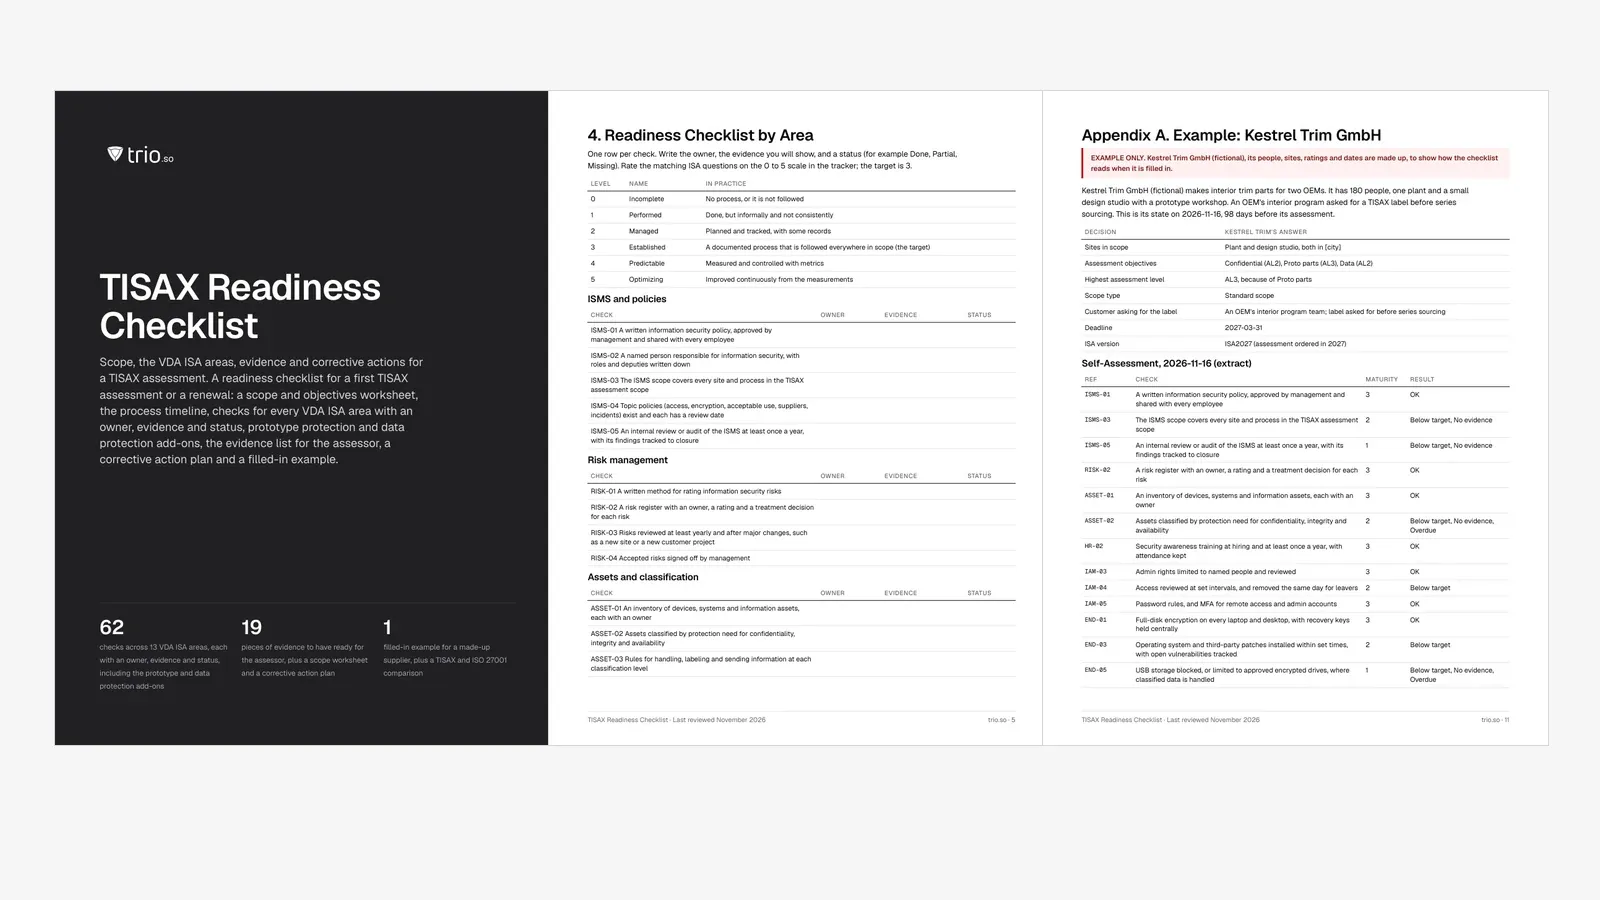
This guide is for IT and security leads at suppliers and service providers with 20 to 1,000 people, facing a first assessment or a renewal. It explains how the process runs, which assessment level and labels apply to you and what the VDA ISA asks, then gives a checklist by area. The download has the checklist in Word and PDF with a filled-in example, and an Excel tracker for your self-assessment, corrective actions and evidence.
In short
TISAX is the automotive industry's shared scheme for information security assessments. The ENX Association governs it, and carmakers, suppliers and audit providers develop it together. The German Association of the Automotive Industry (VDA) publishes the catalogue the assessment uses, the VDA ISA (Information Security Assessment).
You are assessed once, and every customer you choose can see the result in the ENX portal. Results are not public, and you decide who sees them. The ENX handbook notes that TISAX issues no certificate to hang on a wall. You get a set of labels instead, so when a buyer asks for "TISAX certification", they mean the right TISAX labels.
The VDA ISA has three catalogues: information security, prototype protection and data protection. Which of them you face depends on what your customer shares with you.
A customer usually decides. An OEM or a tier-1 supplier asks for a label before it shares information or prototypes, and often names the objectives it wants, such as Confidential or Proto parts. That covers parts suppliers, engineering and design firms, logistics companies that move prototypes, and IT and cloud providers that hold automotive data.
If a customer has asked, find out which objectives they want and by when before you do anything else. That answer sets your scope, your assessment level and your timeline. If NIS2 also applies to you, ENX has published a paper on how TISAX results relate to NIS2 duties; read it next to our NIS2 compliance checklist.
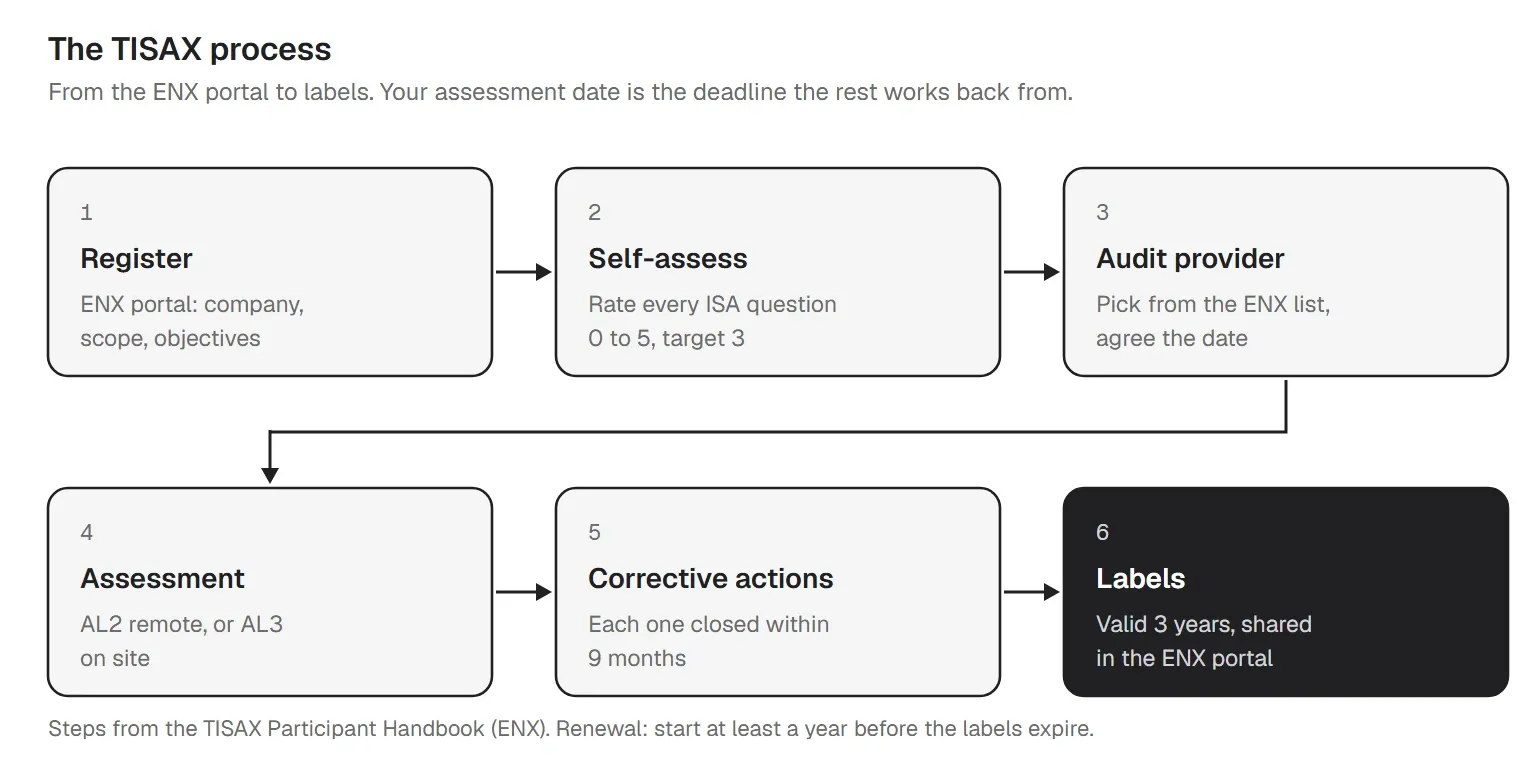
These steps follow the TISAX Participant Handbook. Registering as a participant is free; registering an assessment scope costs a fee, and the audit provider charges for the assessment itself. Book the provider early, because the date you agree with them is the deadline every other task works back from.
If the assessment finds major gaps, you write a corrective action plan with the root cause, the fix and a date for each finding. Every date must fall within nine months, and the audit provider asks for reasons when an action runs longer than three. With only minor gaps you can receive temporary labels while you close them. Follow-up assessments confirm the fixes, and if findings are still open after nine months, no labels are issued and you start a new assessment.
| Level | What the auditor does | Format |
|---|---|---|
| AL1 | Checks only that a self-assessment exists. ENX does not use it for TISAX labels. | No label |
| AL2 | Plausibility check of your self-assessment, a check of your evidence, and an interview with the person in charge of information security, usually by video call. | Remote |
| AL3 | Full check: document review, planned and unplanned interviews, and watching processes on site. The auditor has to visit. | On site |
You don't pick the level. Each assessment objective requires AL2 or AL3, and the highest one in your scope decides. A scope with Confidential and Data is assessed at AL2; add Proto parts and the auditor comes on site.
AL1 has no external check, so it never leads to a label. Everyone writes the self-assessment anyway, because both AL2 and AL3 start from it.
You receive a label for each objective you pass. The current objectives and the level each one needs:
| Objective | Area | Level | What it covers |
|---|---|---|---|
| Confidential | Information security | AL2 | Information with a high protection need for confidentiality |
| Strictly confidential | Information security | AL3 | Information with a very high protection need for confidentiality |
| High availability | Information security | AL2 | Information and systems with a high availability need |
| Very high availability | Information security | AL3 | Information and systems with a very high availability need |
| Proto parts | Prototype protection | AL3 | Prototype parts and components on your premises |
| Proto vehicles | Prototype protection | AL3 | Prototype vehicles on your premises |
| Test vehicles | Prototype protection | AL2 | Prototype vehicles used on public roads and test tracks |
| Proto events | Prototype protection | AL2 | Events, presentations and shoots with prototypes |
| Data | Data protection | AL2 | Personal data you process for a customer under GDPR Art. 28 |
| Special data | Data protection | AL3 | Special categories of personal data under GDPR Art. 9 |
Confidential and Strictly confidential replaced the older Info high and Info very high in April 2024. If a customer still asks for "Info high", it wants Confidential.
ISA2027 changes the prototype labels. The audit providers DQS and SGS report that the four prototype objectives become two: Prototype Protection Basic (AL2), for processes and trained staff, and Prototype Protection Facilities (AL3), which adds the physical protection at your sites. Labels you already hold keep their validity, and ENX will publish the transition details, so check the current list on enx.com before you register a scope.
The VDA ISA is the TISAX questionnaire: an Excel workbook of control questions, each with its requirements and a column for your rating. It is free to download from the ENX website. Version 6.0.3 applies to assessments ordered in 2026. ISA2027 is the basis for assessments ordered from 2027, and from now on the catalogue gets a yearly release named after its year. Audit providers count 43 revised controls in its information security part, most of them reworded so that companies and auditors read them the same way.
You rate each question on this scale:
| Level | Name | In practice |
|---|---|---|
| 0 | Incomplete | No process, or it is not followed |
| 1 | Performed | Done, but informally and not consistently |
| 2 | Managed | Planned and tracked, with some records |
| 3 | Established | A documented process that is followed everywhere in scope (the target) |
| 4 | Predictable | Measured and controlled with metrics |
| 5 | Optimizing | Improved continuously from the measurements |
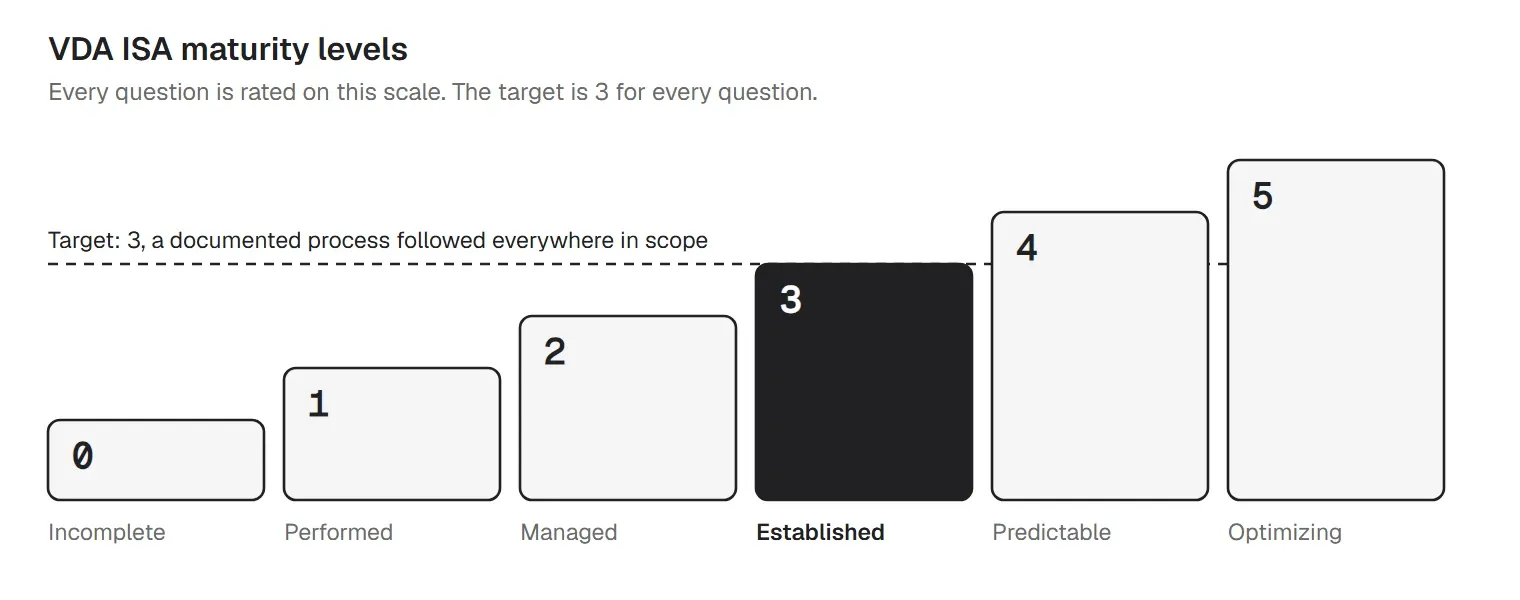
The target is level 3 for every question: a documented process that people follow everywhere in your scope. A written policy nobody follows rates low, and so does a good habit that nobody wrote down. Your TISAX self-assessment is this rating, question by question, with a note on the evidence. It is also the first thing the auditor reads, so rate what you can show and give every shortfall a fix date.
These checks follow the VDA ISA's areas in our own words, not the catalogue's. Use them to find gaps before you open the official questions, then rate the questions themselves. Below is a selection per area; the download has all 62, each with columns for an owner, the evidence and a status.
An ISO 27001 ISMS covers most of this; see our ISO 27001 checklist.
Our guide to IT risk management walks through a rating method.
The IT asset management policy template sets owners and the inventory rules.
Write the rules down in an access control policy, then keep the review records.
The data encryption policy template sets the encryption rules, the patch management policy template sets patch times, and our guide on how to disable USB ports covers removable storage. Personal phones that reach company data follow the BYOD policy.
The vendor management policy template gives you the contract and review rules, and our guide to third-party risk management covers how to rate suppliers.
The data breach response plan and the incident report template cover the process and the record.
The physical facility access policy sets zones, badges and visitor rules.
The prototype objectives cover physical parts and vehicles at your sites, test vehicles on roads and tracks, and events or shoots with prototypes. Design data on your servers falls under information security instead. Proto parts and Proto vehicles are assessed on site at AL3, so the auditor will walk through the workshop.
The data protection objectives apply when you process personal data on a customer's behalf, for example driver data from a test fleet or employee data for an HR service. The ISA's questions here follow the processor duties in GDPR Art. 28. Special data, which covers health and other special categories, is assessed at AL3.
Our GDPR compliance checklist covers the rest of the regulation.
Collect these before the assessment, current and approved. The download lists 19 items, including:
At AL2 you share documents for a remote review, and the auditor interviews the person in charge of information security. At AL3 the auditor also checks on site that what is written matches what people do, so records such as the visitor log and access reviews count as much as the policies.
| TISAX | ISO/IEC 27001 | |
|---|---|---|
| Who runs it | ENX Association; the VDA publishes the ISA catalogue | ISO and IEC publish the standard; accredited certification bodies certify |
| What you get | TISAX labels, one per assessment objective | A certificate for your ISMS |
| What is checked | The VDA ISA: information security, plus prototype protection and data protection where your objectives need them | Clauses 4 to 10 and the Annex A controls in your Statement of Applicability |
| Scoring | Maturity 0 to 5 per question, target 3 | Conformity or nonconformity per requirement |
| Scope | Sites and objectives you register; may be smaller than your ISMS but must sit inside it | The ISMS scope you define |
| Who sees the result | Partners you share it with in the ENX portal | Anyone you show the certificate to |
| Validity | Three years from the end of the assessment process | Set by the certification body's cycle |
The ISA was tailored from existing ISMS standards, and TISAX expects you to run an ISMS, so an ISO 27001 program covers much of the information security work. ISO 27001 doesn't cover prototype protection, the GDPR processor questions or the maturity scoring, and your customer checks the label in the ENX portal, so an ISO certificate doesn't stand in for it. The download maps each checklist area to the ISO/IEC 27001:2022 controls to look at first.
ENX gives no typical duration, because it depends on how mature your ISMS already is. A company with a working ISO 27001 ISMS has less to build than one starting from scattered policies. Plan back from the customer's deadline: the assessment date, the corrective action window of up to nine months after it, and your self-assessment and fixes before it. For a renewal, ENX recommends starting at least a year before your labels expire.
The cost has three parts: the ENX fee for registering the scope (in ENX's price list), the audit provider's fee, and your own team's time. Providers set their own prices. As a rough guide, the handbook estimates 3.5 to 4 auditor days at AL2 and 5 to 6 at AL3 for a small company with one site. More sites and more objectives add days.
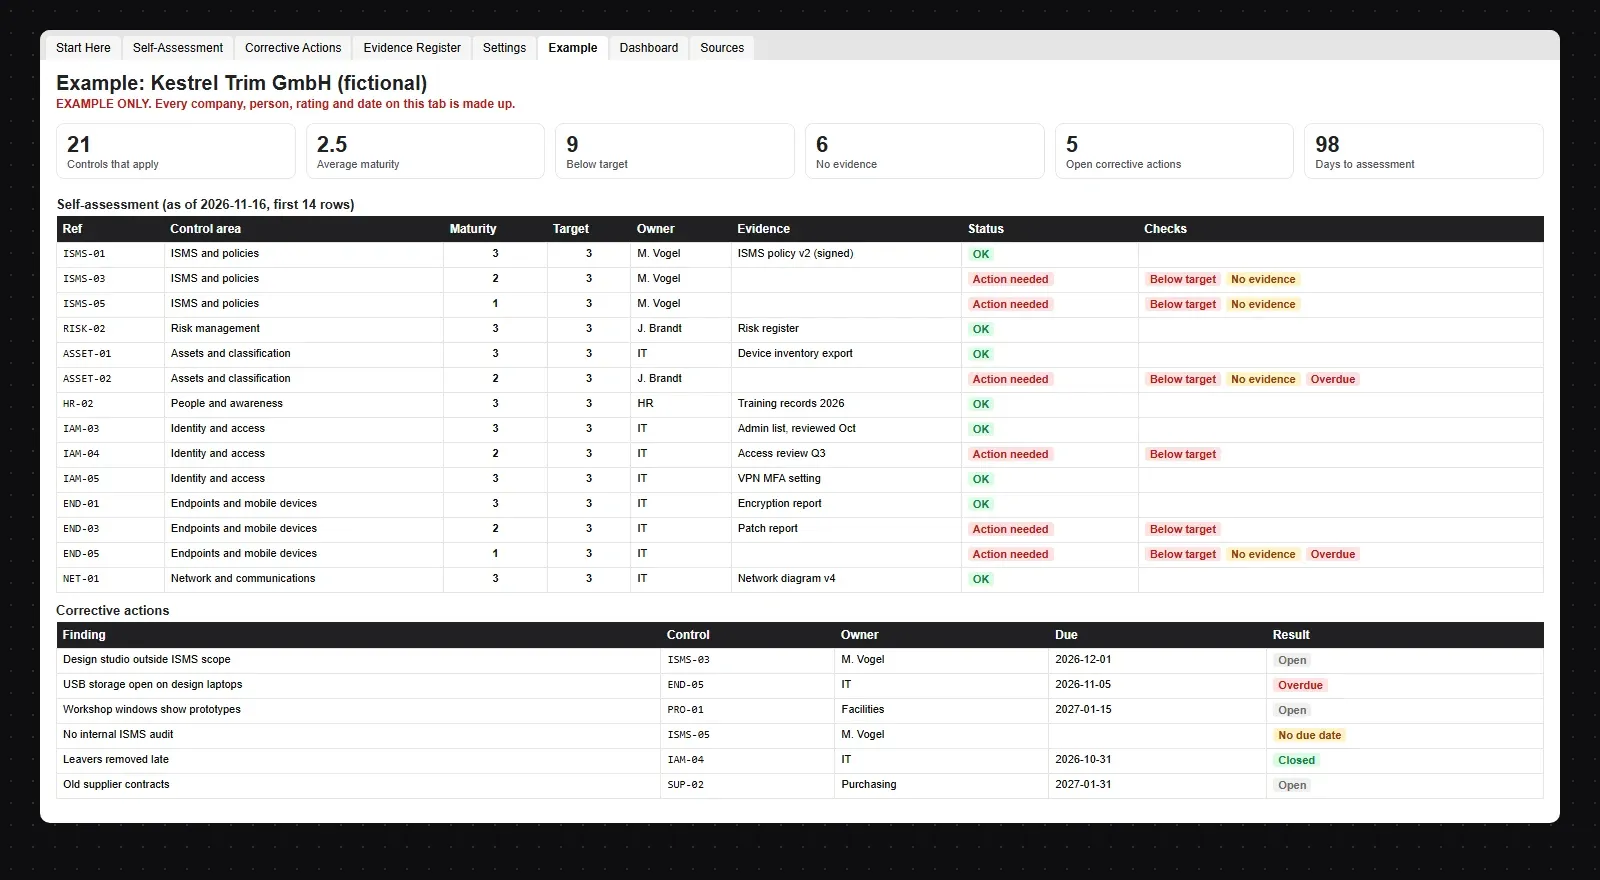
The download includes the checklist filled in for Kestrel Trim GmbH, a made-up maker of interior trim parts with 180 people, one plant and a design studio with a prototype workshop. An OEM asked for Confidential, Proto parts and Data, so the assessment is AL3. Part of its tracker on 16 November, 98 days before the assessment:
| Ref | Check | Maturity | Result |
|---|---|---|---|
| ISMS-03 | The ISMS scope covers every site and process in the TISAX assessment scope | 2 | Below target, No evidence |
| ASSET-02 | Assets classified by protection need for confidentiality, integrity and availability | 2 | Below target, No evidence, Overdue |
| END-05 | USB storage blocked, or limited to approved encrypted drives, where classified data is handled | 1 | Below target, No evidence, Overdue |
| PRO-01 | Prototype areas with physical barriers that stop outsiders seeing in | 2 | Below target, No evidence |
21 checks apply and 20 are rated, at an average maturity of 2.5. Nine are below the target, six have no evidence yet, and two fixes are past their date: USB storage on the design laptops and the rollout of the classification scheme. The design studio still sits outside the ISMS scope, which has to change before an auditor visits its prototype workshop.
The workbook sits next to the official ISA catalogue. It holds the 62 checks and a column for the matching ISA question number, not the ISA questions themselves. Self-Assessment flags checks below your target maturity, not yet rated, without evidence, or past their fix-by date. Corrective Actions flags overdue actions, and the Evidence Register flags documents due for review. The Dashboard shows average maturity per area and the days left to your assessment. Formulas only, no macros.
trio.so does not run your ISMS or your assessment, and it has no prototype protection features. What it covers is the endpoint part of the ISA: knowing which devices you have, setting and checking their security settings, and exporting the records an assessor asks for. For that part, trio.so gives you:
It manages Windows, macOS, Linux, iOS/iPadOS and Android from one console. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026. TISAX is a registered trademark of the ENX Association. The VDA ISA catalogue is published by the VDA and ENX; this template does not reproduce its text. The wording of every item is ours. trio.so is not affiliated with or endorsed by the ENX Association or the VDA.
trio.so keeps a device inventory with owners and serial numbers, sets BitLocker and FileVault, blocks USB storage on Windows, Linux and Android, shows patch status per device and exports evidence.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Learn how you can improve your resource allocation strategy & download the IT Resource Allocation Template to optimize your IT resource management.
Free IT audit checklist template in Excel, PDF and Word: 66 checks in 8 areas, an audit questionnaire, a findings tracker and a filled-in example.
Free IT contingency plan template in Word and Excel, with a filled-in example: BIA with MTD, RTO and RPO, call tree, recovery steps and test forms.
Free SDLC policy template with security work for every phase, release gates, a checklist, sign-off form, framework mapping and an Excel tracker.
Free NIS2 checklist in Excel, PDF and Word: check who is in scope, work through the ten Article 21 measures, supplier security and 24h/72h reporting.
Learn how to create a comprehensive Request for Information (RFI) template tailored for IT admins.
A server hardening checklist template for Windows and Linux with verification commands, plus a free Excel tracker, Word checklist and policy template.
Learn how to create an effective data masking policy to protect sensitive data, comply with regulations, and enhance trust + free template to get started!
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients