



Templates
IT Contingency Plan Template (Free Word + Excel + Example)
Free IT contingency plan template in Word and Excel, with a filled-in example: BIA with MTD, RTO and RPO, call tree, recovery steps and test forms.
Free IT audit checklist template in Excel, PDF and Word: 66 checks in 8 areas, an audit questionnaire, a findings tracker and a filled-in example.

Content writer, trio.so
An IT audit asks a simple question: do the controls you say you have actually work? Answering it takes more than a list of good intentions. You need to know what to check, what evidence to ask for and how to write up what you find so it gets fixed.
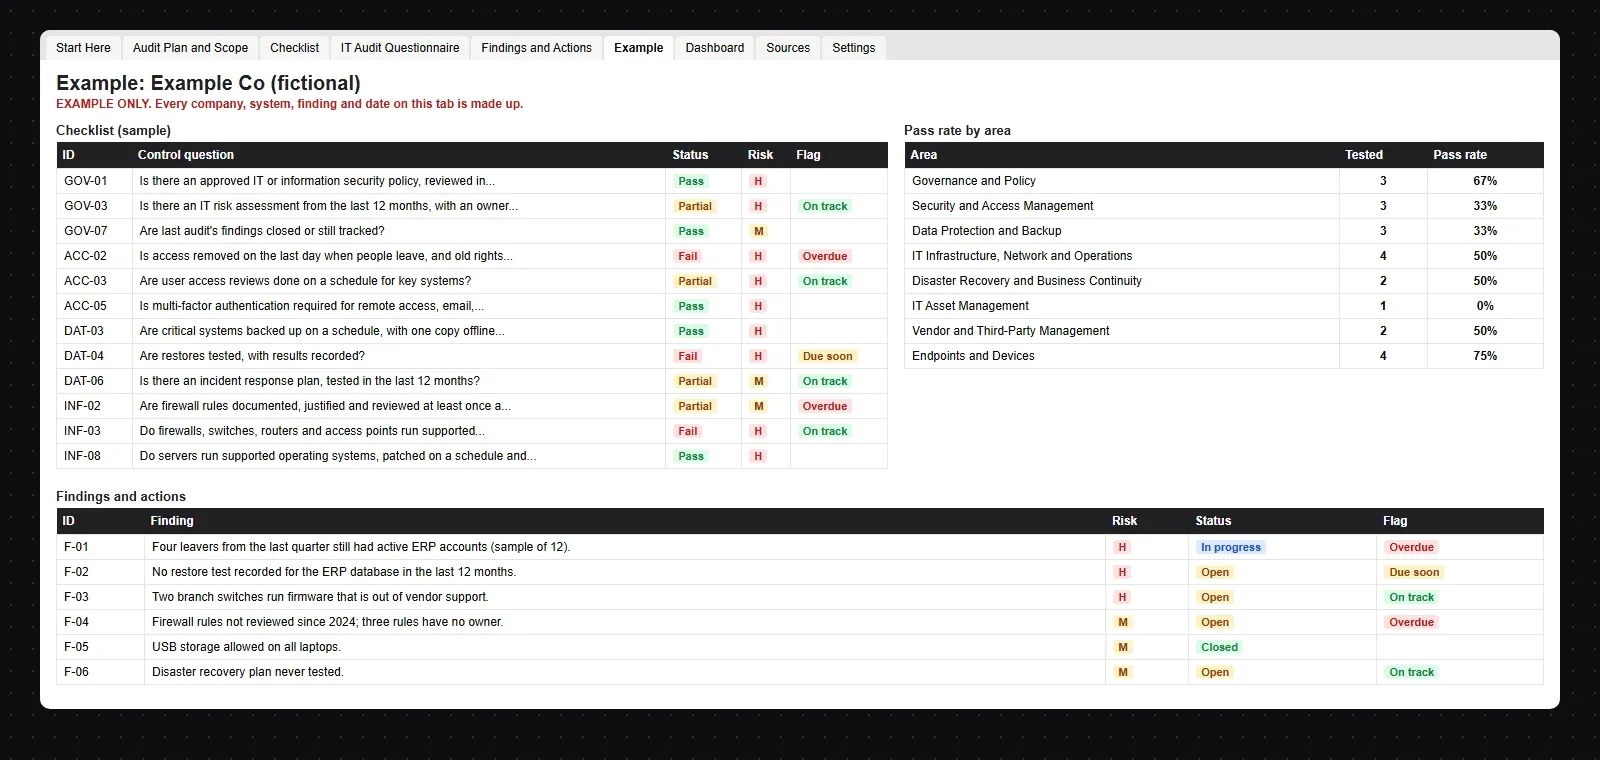
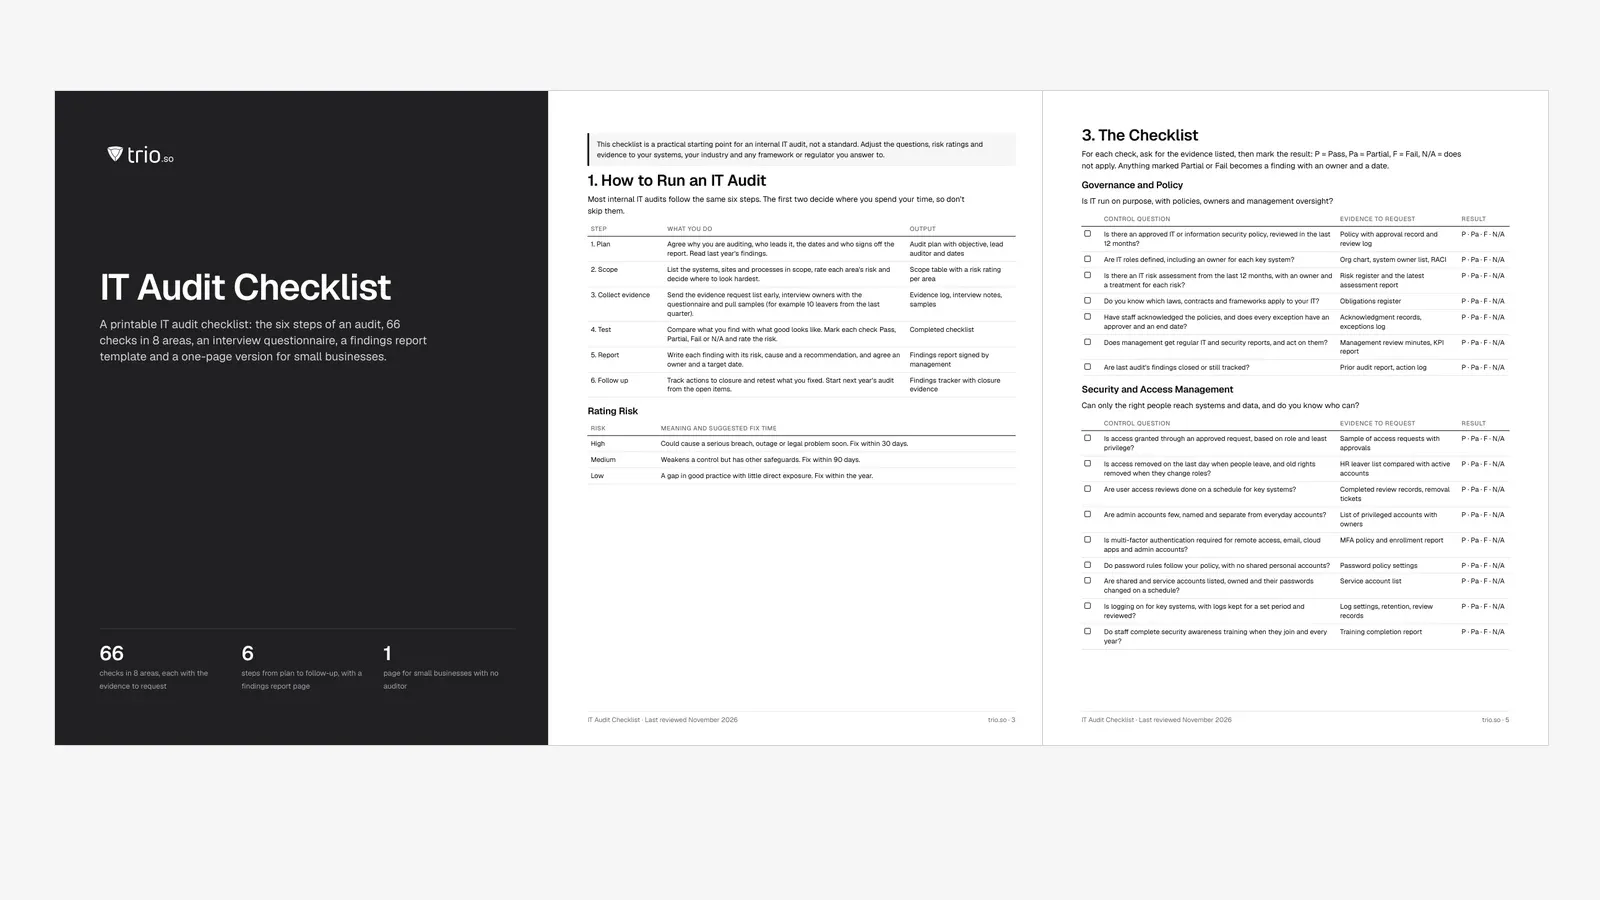
This free IT audit template gives you all three. The Excel tracker holds 66 checks in 8 areas, each with a control question, what good looks like and the evidence to request, plus an audit plan, an interview questionnaire, a findings tracker and a dashboard. The PDF and Word versions add a findings report page and a one-page small-business version.
In short
An IT audit is a structured review of how your organization runs and protects its technology. The auditor compares what is in place with what should be in place, tests a sample of the controls, and reports the gaps with a risk rating. The point is an honest view of where IT could fail, and a list of fixes in order of risk.
A checklist keeps the audit consistent: the same questions every year, so results can be compared area by area.
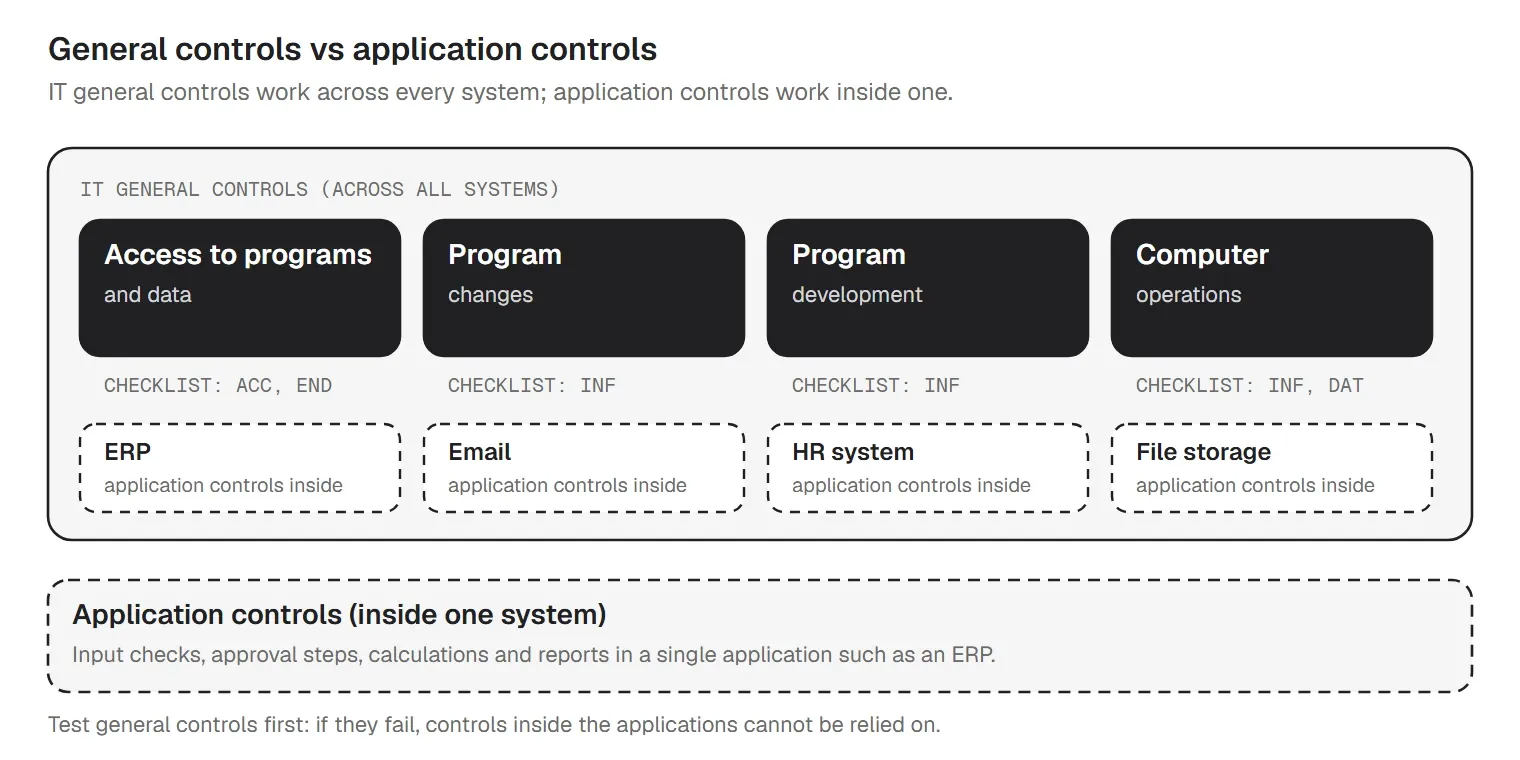
Audit teams commonly describe IT general controls in four areas: access to programs and data, program changes, program development and computer operations. The checklist covers all four, mostly in the access and infrastructure areas, so the same file works whether your auditor talks in ITGC terms or in plain IT language.
| Step | What you do | What you end up with |
|---|---|---|
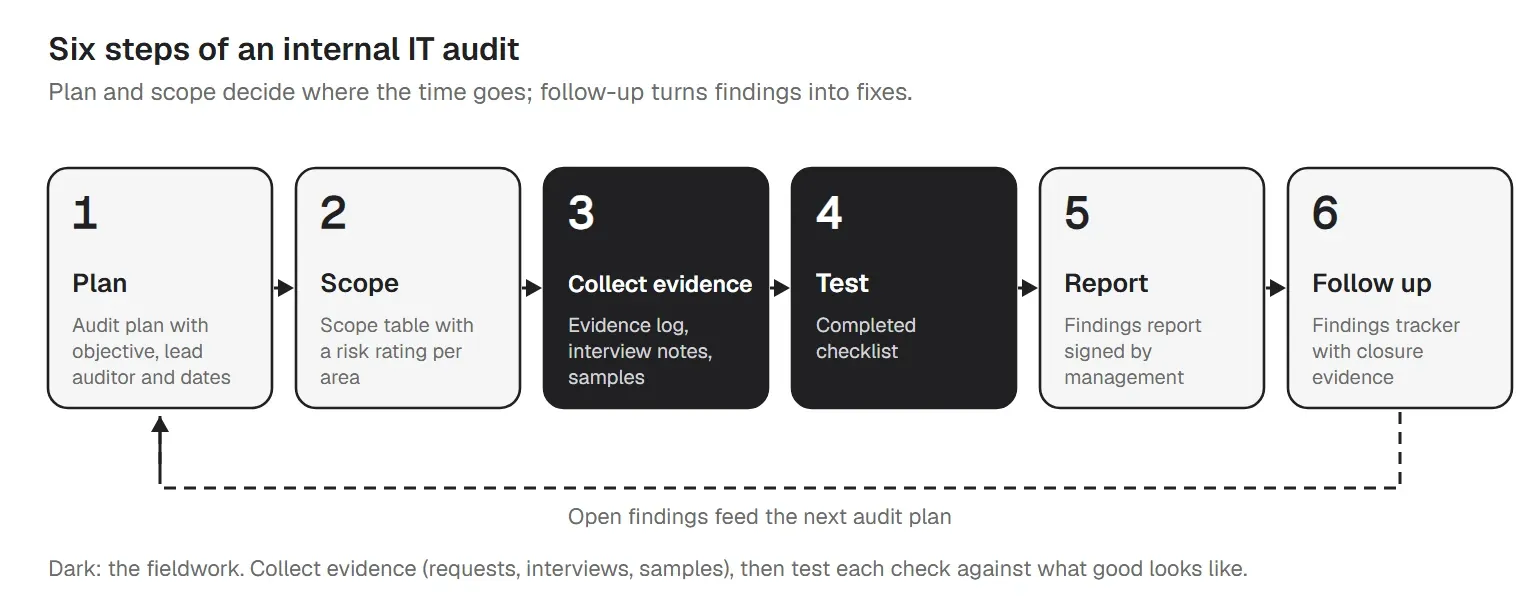
| 1. Plan | Agree why you are auditing, who leads it, the dates and who signs off the report. Read last year's findings. | Audit plan with objective, lead auditor and dates |
| 2. Scope | List the systems, sites and processes in scope, rate each area's risk and decide where to look hardest. | Scope table with a risk rating per area |
| 3. Collect evidence | Send the evidence request list early, interview owners with the questionnaire and pull samples (for example 10 leavers from the last quarter). | Evidence log, interview notes, samples |
| 4. Test | Compare what you find with what good looks like. Mark each check Pass, Partial, Fail or N/A and rate the risk. | Completed checklist |
| 5. Report | Write each finding with its risk, cause and a recommendation, and agree an owner and a target date. | Findings report signed by management |
| 6. Follow up | Track actions to closure and retest what you fixed. Start next year's audit from the open items. | Findings tracker with closure evidence |
Planning and scoping decide where your time goes. Rate each area's risk on the Audit Plan and Scope tab before you start: high-risk areas get more samples and more interviews, low-risk areas can carry forward last year's result if nothing has changed. Send the evidence requests a week or two before fieldwork.
Testing means comparing evidence with the "what good looks like" column. A policy not reviewed in three years is a Partial. A leaver account still active after a month is a Fail, whatever the policy says. That gap between paper and practice is what an audit is for.
The checklist keeps the seven classic audit areas and adds an eighth for endpoints. Each check below is written as a control question. In the workbook, each one also has what good looks like, the evidence to request, a framework reference and columns for owner, status, risk and due date.
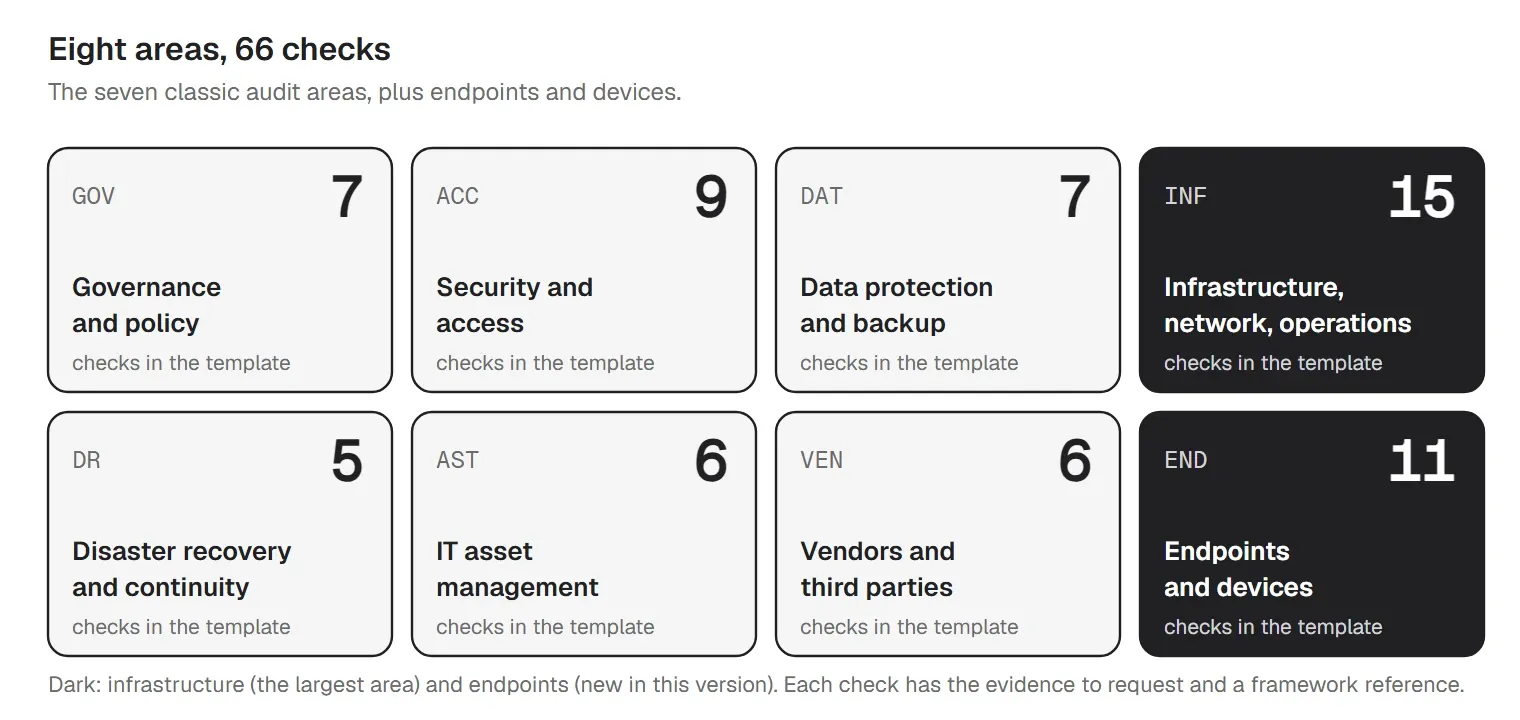
Is IT run on purpose, with policies, owners and management oversight? Start here, because every other area depends on policies, owners and a current risk assessment. Our IT governance policy template covers roles and oversight.
Can only the right people reach systems and data, and do you know who can? Access is where ITGC testing usually starts, and where gaps between policy and practice show up fastest. Pull a sample of joiners and leavers and trace each one. Our user access review template and access control policy template help with both.
Is data handled by its sensitivity, backed up, and recoverable? A backup that has never been restored is a hope, not a control. Ask for restore test records, not the backup schedule. See the data backup and recovery policy template.
Are servers, networks and cloud services documented, supported, secured and run under control?
Infrastructure is the biggest area in the checklist. It covers three layers, plus the operations around them:
| Layer | What to look at | Evidence that settles it |
|---|---|---|
| Network | Diagram, firewall rules, network device firmware, admin access, segmentation, Wi-Fi, remote access | Firewall rule export with review sign-off; device list with firmware versions |
| Servers and cloud | Supported operating systems, patching, hardening baseline, cloud admin roles and settings | Server list with OS versions and patch dates; cloud admin role list |
| Facilities | Locked server rooms and network closets, entry records, power and cooling | Access list, entry log, UPS test record |
| Operations | Change control, go-live testing, job and backup failure handling, availability alerts | Sample of change records; failed job tickets |
Change control and job monitoring are the ITGC areas of program changes, program development and computer operations in practical form. For server settings, our server hardening checklist goes deeper, and the configuration management policy template sets the baseline you audit against.
Can the business keep going, and recover IT, after a serious outage? The question is not whether a plan exists but whether it has been tested and whether the recovery targets were reached. Our disaster recovery plan template gives you a format.
Do you know what you own, who has it and when it retires? You can't protect, patch or retire what you don't know you have. Compare the register with what your device management, network scans and cloud consoles actually see. Our IT asset management policy template sets the rules.
Are the companies that run or reach your IT chosen, contracted and watched with care? Vendors run more of your IT every year, so their controls are part of yours. Check the contract terms and the access, not just the questionnaire. See the vendor management policy template.
Are the laptops, desktops and phones your staff use known, encrypted, patched and configured? Many checklists stop at servers and networks, but much of your data lives on laptops and phones. These checks make the device fleet its own area. For a deeper review of your device management setup, use the MDM audit checklist.
Interviews tell you how things are supposed to work and where to look. The questionnaire tab has 30 questions across the eight areas. A few that tend to surface real gaps:
Treat every answer as a lead, not as evidence. If the owner says leavers are removed on the last day, the next step is to compare the HR leaver list with active accounts.
A check passes on evidence, not on a yes in an interview. Most evidence falls into five kinds:
| Kind | Examples | Tip |
|---|---|---|
| Exports and reports | Device inventory, user lists, admin role lists, patch status per device, MFA enrollment | Ask for the export with a date, not a screenshot of a dashboard |
| Samples | Joiners and leavers, change records, access requests, incidents | Pick the sample yourself from the full population, for example 10 to 25 items |
| Signed records | Access reviews, policy approvals, firewall rule reviews, restore tests | Look for a name, a date and what was decided |
| Configuration | Password and MFA settings, encryption, backup jobs, firewall rules | See it in the system, or ask for a configuration export |
| Walkthroughs | Server rooms, a live change, a restore | Watch it happen and write down what you saw |
Record where each piece of evidence is kept in the Evidence reference column. Next year you'll know exactly what to pull again.
A finding that just says "access reviews not done" rarely gets fixed. Write each one in five parts so the owner understands what went wrong and why it matters:
| Part | What to write |
|---|---|
| Condition | What you found (the fact, with evidence) |
| Criteria | What good looks like (your policy, a framework or a contract) |
| Cause | Why it happened |
| Effect | What could go wrong, which sets the risk rating |
| Recommendation | What to do, with an owner and a target date |
Then rate the risk. The template uses three levels with suggested fix times: High (fix within 30 days), Medium (within 90 days) and Low (within the year). Agree them with management before the audit, not after. The Findings and Actions tab flags overdue actions and counts days open, and the Dashboard rolls it up for your report.
Many organizations run a full internal IT audit once a year, with lighter checks in between on the areas that change fastest, such as access, patching and backups. Audit again after a major change, such as a merger, a new core system or a serious incident. If a regulator, customer contract or framework sets a frequency, that comes first.
Who runs it depends on your size:
Between full audits, our IT health check template is a shorter, quarterly look at the same areas.
A 20-person company doesn't need 66 checks and a findings committee. It needs the basic controls that prevent common problems. The PDF and Word files include a one-page short version; here it is:
Move to the full checklist when you grow or a customer asks for evidence.
The checklist isn't tied to one framework, but each check carries a general reference so you can see where it fits. The reference names an ISO/IEC 27001:2022 Annex A theme, a NIST CSF 2.0 function and, where one fits, a CIS Controls v8.1 Control number.
| Framework | What it is |
|---|---|
| COBIT 2019 (ISACA) | A governance and management framework for enterprise IT: 40 governance and management objectives in five domains (Evaluate, Direct and Monitor; Align, Plan and Organize; Build, Acquire and Implement; Deliver, Service and Support; Monitor, Evaluate and Assess). |
| IT general controls (ITGC) | As audit teams commonly describe them: access to programs and data, program changes, program development, and computer operations. |
| NIST Cybersecurity Framework 2.0 | Published 26 February 2024, with six functions: Govern, Identify, Protect, Detect, Respond and Recover. |
| ISO/IEC 27001:2022 Annex A | 93 controls in four themes: organizational (37), people (8), physical (14) and technological (34). |
| CIS Controls v8.1 | Released June 2024: 18 Controls, from inventory of enterprise assets (1) to penetration testing (18). |
These are pointers, not a mapping: a framework-focused audit needs the framework's own requirements. Read the publisher's text at NIST, ISO, CIS and ISACA. Our ISO 27001 checklist walks through that standard, and the compliance checklist template tracks any framework you report against.
trio.so does not run the audit, assess vendors, test disaster recovery, audit networks or firewalls, or issue certifications. Those stay with your auditors, your IT team and your other tools.
What it gives you is evidence for the endpoint part of the audit: the laptops, desktops and phones your staff use every day. trio.so is device management for Windows, macOS, Linux, iOS/iPadOS and Android, from one console. For the endpoint and asset checks in this list, it gives you:
See how the device inventory and patch management work, or how compliance automation exports evidence. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026. Framework references are general pointers to ISO/IEC 27001:2022 Annex A themes, NIST Cybersecurity Framework 2.0 functions and CIS Controls v8.1 Control numbers; the wording of every check is ours. trio.so is not affiliated with or endorsed by ISO, NIST, the Center for Internet Security or ISACA.
trio.so keeps a device inventory with owners and serial numbers, shows encryption, patch and policy status for each device, and exports compliance evidence for your auditor.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Free IT contingency plan template in Word and Excel, with a filled-in example: BIA with MTD, RTO and RPO, call tree, recovery steps and test forms.
Free SDLC policy template with security work for every phase, release gates, a checklist, sign-off form, framework mapping and an Excel tracker.
Free NIS2 checklist in Excel, PDF and Word: check who is in scope, work through the ten Article 21 measures, supplier security and 24h/72h reporting.
Learn how to create a comprehensive Request for Information (RFI) template tailored for IT admins.
A server hardening checklist template for Windows and Linux with verification commands, plus a free Excel tracker, Word checklist and policy template.
Learn how to create an effective data masking policy to protect sensitive data, comply with regulations, and enhance trust + free template to get started!
Learn how to effectively use a Technology Risk Assessment Template with this guide. Simplify risk management and protect your business today!
Free IT risk management plan in Word and PDF with scoring scales, a treatment plan and sign-off form, plus an Excel risk register with a live risk matrix.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients