



Templates
Firewall Configuration Policy Template (Word, Excel + PDF)
Free firewall configuration policy (Word, PDF) and an Excel rule register that flags any-any, unowned, expired and unused rules. Plus how to plan rules.
A free compliance checklist template for IT teams: ten areas with owners, status and evidence, plus an Excel workbook, framework crosswalk and Word guide.

Content writer, trio.so
A compliance checklist template is a list of the controls, documents and routines an organization needs in place to follow the laws, regulations and contracts that apply to it, grouped by area, with an owner, a status and the evidence for each line. For IT, a framework-neutral checklist covers ten areas: scope and the frameworks that apply, written policies, an asset inventory, access control, device security, data protection, vendors, training, monitoring and evidence, and audit readiness. Work through it once to find the gaps, then keep it up to date and map each line to the specific framework you are audited against. The full checklist and a free template download, with an Excel workbook and a Word and PDF guide, are below.
If a first audit or a customer's security questionnaire is coming up and you do not know where to start, work through the checklist area by area; the sections after it show how to adapt it to your framework and keep the evidence ready.
Compliance requirements are spread across laws, contracts and standards, and most of them ask for the same basics in different words: know your systems and data, control who can reach them, protect devices and data, train people, and prove all of it. A checklist turns those requirements into concrete tasks with owners, so nothing depends on one person's memory. It also shows auditors and customers that the work is organized and repeatable.
A checklist does not make an organization compliant by itself. Compliance comes from doing the work and keeping the evidence; the checklist is how you see what is done and what is not.
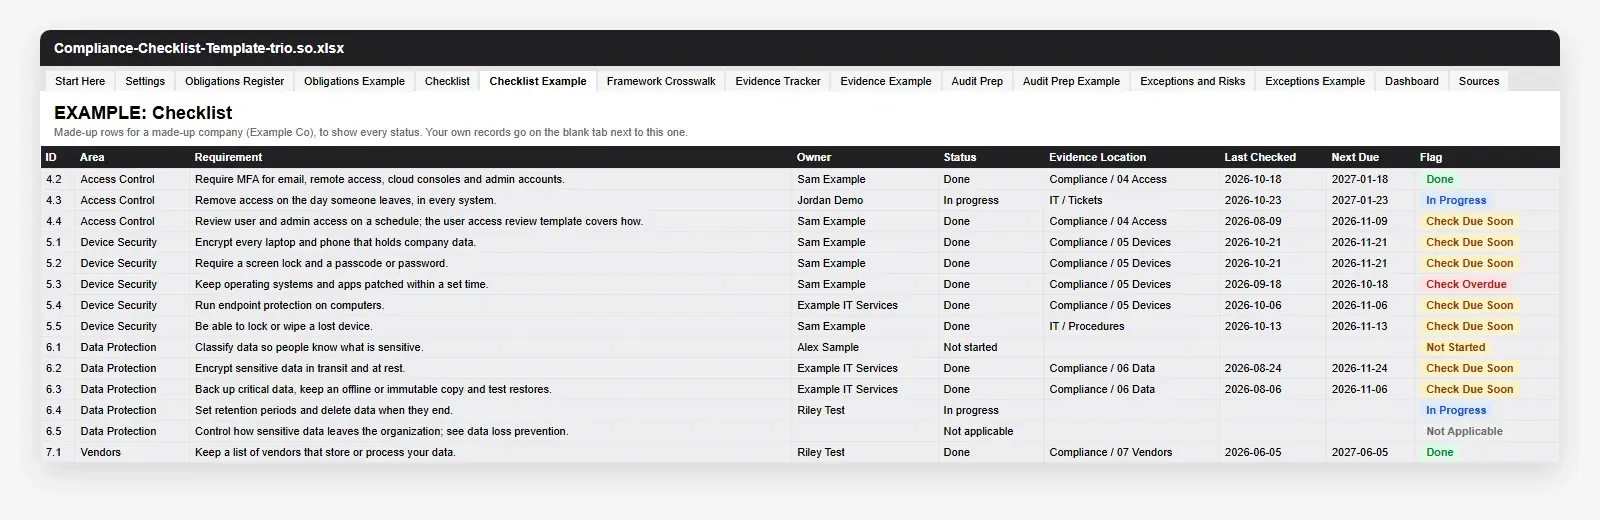
Copy the lines that apply to you. For each one, record an owner, a status (done, in progress, not started) and where the evidence lives.
The download has three files. The Excel workbook holds every line above with an owner, a status, the evidence and where it lives, the date it was last checked and the next due date, plus an obligations register, a framework crosswalk, an evidence tracker, audit preparation with a document request list, an exceptions and risks register and a dashboard. Each tab has a filled-in example beside it. The Word and PDF guide has the checklist area by area, how to adapt it to a framework, a short compliance program outline, an audit preparation checklist, a document request list and a sign-off page. Add your own owners, statuses and evidence locations for each line.
The areas above are common to most frameworks. Each framework then adds its own wording, scope and specific controls, so map your checklist to the one you are audited against:
Keep one master checklist and add a column for each framework that applies. Where frameworks overlap, one piece of evidence can cover several requirements.
Our framework checklists list each framework's own requirements:
The download's Framework Crosswalk tab maps the lines above to HIPAA, SOC 2, ISO 27001, NIST CSF 2.0, PCI DSS, GDPR and CIS Controls IDs where the fit is clear, and the checklist shows the IDs for the frameworks you mark in scope.
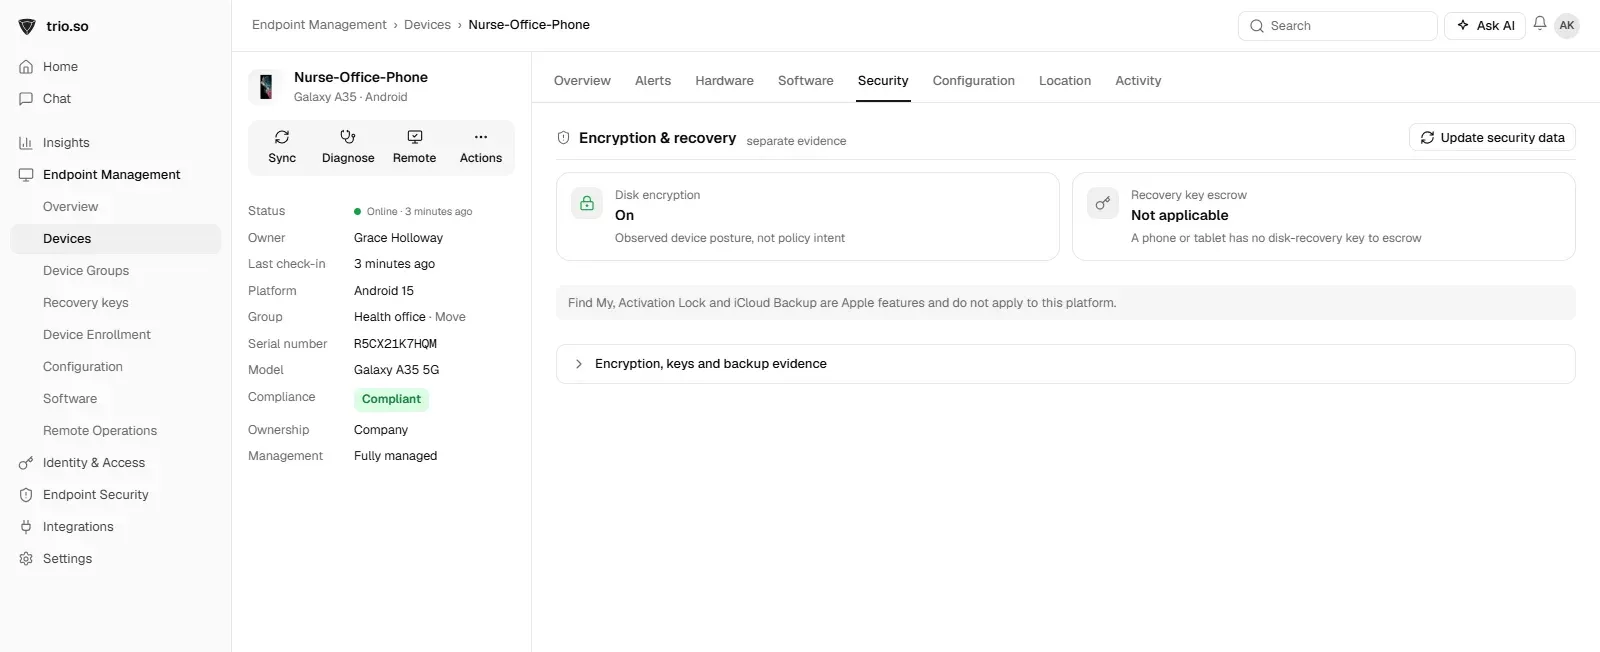
Most of this checklist is policy, people, vendors and process. To be clear, trio.so does not make anyone compliant and does not run your compliance program. It covers the device lines in areas 3 and 5: a device inventory with owner, serial number and installed apps; encryption and screen lock policies, with each device's encryption status; OS update policies, vulnerability findings and a risk score from 0 to 100 for each device, based on its open vulnerability findings; and whether each policy applied, failed or is still pending on each device. Its compliance templates for frameworks such as SOC 2, ISO 27001, PCI DSS, NIST SP 800-53, the CIS Benchmarks, NCA ECC and SAMA CSF check enrolled devices against device controls, and you can export the results as evidence for your audits. See compliance automation.
Plans start at $5 per device. 14-day free trial. No credit card required. Start a free trial or book a demo.
A compliance checklist template turns scattered requirements into owned, trackable tasks. Start with the ten areas above, map them to the frameworks that apply to you, assign an owner to every line, collect evidence as you go, and review the checklist regularly rather than only before an audit.
Related reading: IT audit checklist, user access review template, ISO 27001 checklist and data loss prevention.
trio.so shows each device's encryption status and exports compliance evidence from one console.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Free firewall configuration policy (Word, PDF) and an Excel rule register that flags any-any, unowned, expired and unused rules. Plus how to plan rules.
A free database security policy template, with the key components of a strong policy and best practices for protecting stored data.
Free IT asset disposal policy template with a disposal form, checklist and Excel log. NIST SP 800-88 Rev. 2 methods, ITAD vendor checks and process flow.
Using a proper transition plan template can help organizations manage projects and employees better. Read on to learn more about transition plans.
Free IT incident report template in Word and PDF with an Excel incident log: severity levels, timeline, root cause, postmortem and a filled-in example.
How to create a data center access policy, with the key components to cover and a template you can download.
Free VPN policy template in Word and PDF: who gets access, approved protocols, MFA, split tunneling and logging, plus an Excel VPN access register.
Free IT offboarding checklist with an Excel tracker: access removal, device return and wipe, admin and BYOD steps, plus sample offboarding emails.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients