



Templates
MDM Implementation Checklist (Free Word + Excel Tracker)
Free MDM rollout checklist in Word and PDF: requirements, APNs and platform prerequisites, a policy baseline, pilot and go-live forms, plus a tracker.
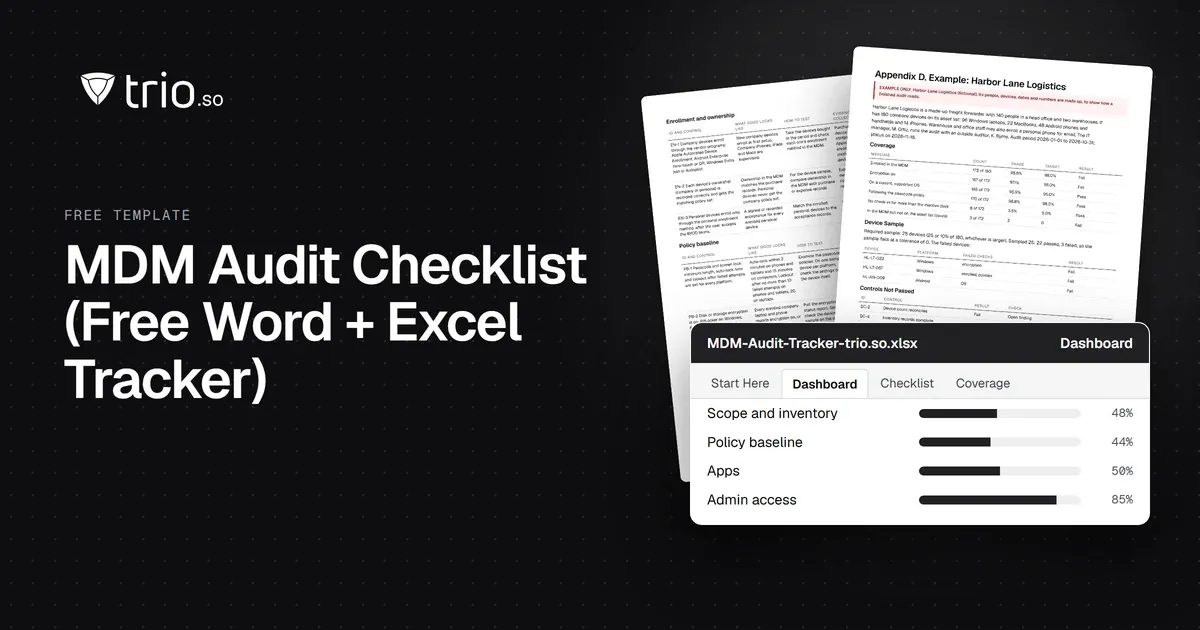
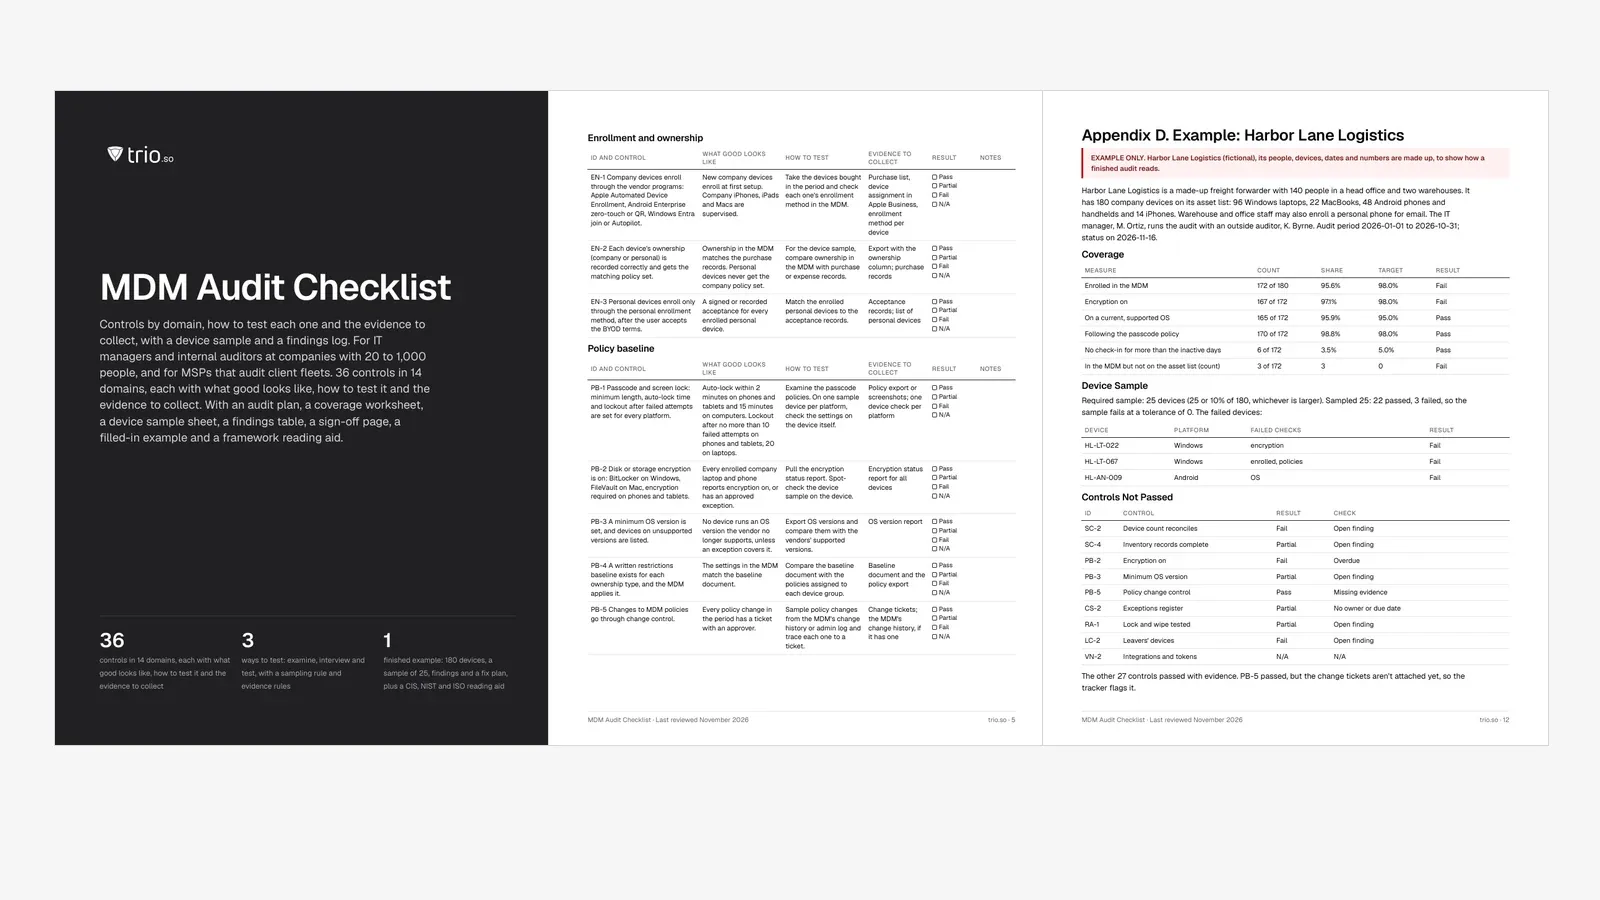
Free MDM audit checklist in Word and PDF: 36 controls with how to test each one, the evidence to collect, a device sample sheet and an Excel tracker.

Content writer, trio.so
An MDM audit checks two things: that the settings in your mobile device management tool match what your policy promises, and that they work on the laptops and phones people carry every day. This guide follows the audit in the order you would run it, from scope and the device count to sampling, testing, findings and the fix plan, with the evidence an auditor asks for at each step.
It's written for IT managers and internal auditors at companies of 20 to 1,000 people, and for MSPs that audit client fleets. The download has the full checklist in Word and PDF, plus an Excel tracker that works out coverage, the sample result and which fixes are overdue.
Free download
Your MDM holds the device inventory, the security settings and the record of what happened to each device, so most of an audit's evidence comes out of it. An MDM audit asks whether that record is complete and whether the settings hold up when someone checks a real device. It covers company laptops, phones and tablets on every platform you manage, plus the personal phones you allow to reach company email and apps.
A mobile device audit program repeats the work: a full audit every year, coverage numbers every quarter, and a retest of every finding before it closes. The checklist groups the controls into 14 domains:
Your mobile device management policy sets the rules; the audit tests them. If you're still rolling the MDM out, the MDM implementation checklist covers setup. This one is for a fleet that already runs.
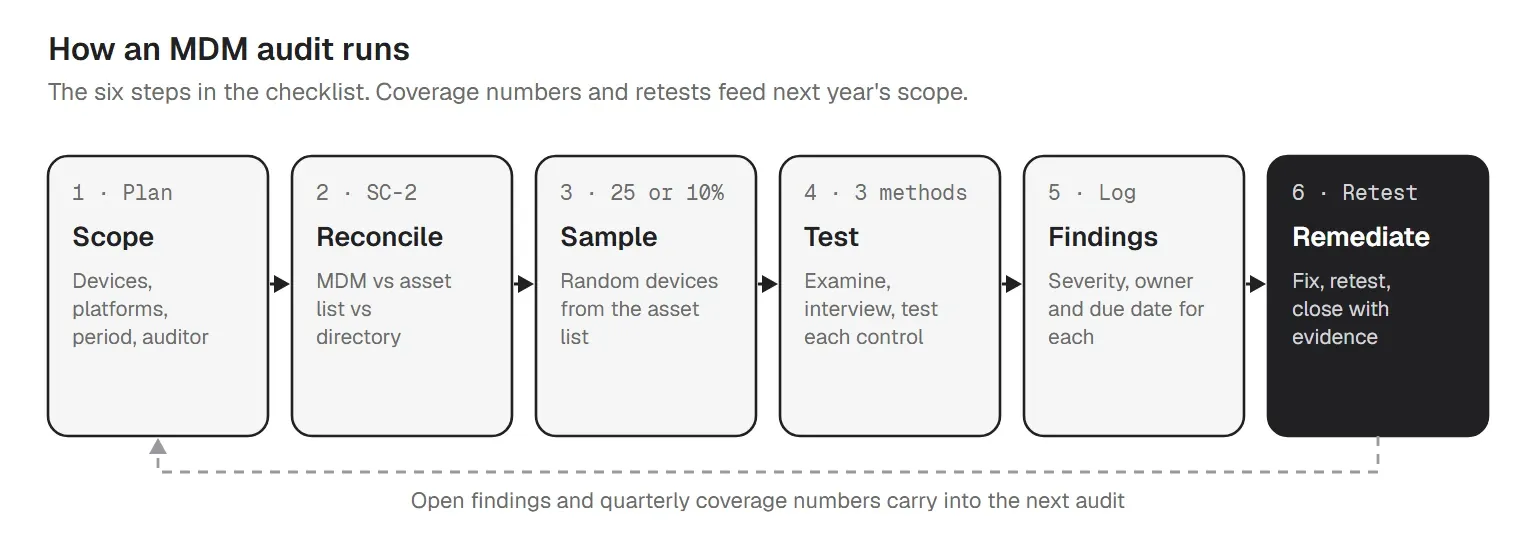
Agree the scope with the auditor before fieldwork starts: which devices, which platforms, which locations, company devices only or personal ones too, and the audit period. The period matters because only exports, tickets and screenshots dated inside it count as evidence. The checklist's audit plan page records all of it, along with the sample size and where the evidence will be kept.
Export three lists on the same day: the MDM inventory, the asset list and the active users in your directory. Match them on serial number and count the gaps in both directions. A device on the asset list but missing from the MDM is unmanaged. A device in the MDM but missing from the asset list is a hole in asset management. A device assigned to someone who left is an offboarding miss. Start here: the reconciliation shows which devices the rest of the audit can't see. Our guide to device inventory management covers keeping the asset list itself in shape.
Pick devices at random from the asset list, not from the MDM. A sample drawn from the MDM can only show devices that are already managed. The template's default is 25 devices or 10% of the asset list, whichever is larger. The section on sampling below explains the rule.
Work through the checklist domain by domain. For each control, read the setting, ask the person who runs it, and check that it works, then record a result: Pass, Partial, Fail or N/A. Write down where the evidence is kept.
Every Fail or Partial becomes a finding with a severity, an owner and a due date. A finding without an owner tends to stay open until the next audit, which is why the tracker flags it.
Fix each finding, then test it again the same way and keep the retest evidence before you close it. Expect a returning auditor to ask how last year's findings were closed.
The download lists 36 controls, each with what good looks like, how to test it and the evidence to collect. This is the short version:
| Domain | What to check | Evidence |
|---|---|---|
| Scope and inventory | Written policy; MDM count vs asset list vs directory; unmanaged devices reaching email; blank owner or serial fields | Three dated exports and the reconciliation sheet |
| Enrollment and ownership | Company devices enroll through Apple Automated Device Enrollment, Android Enterprise zero-touch or QR, or Windows Entra join or Autopilot; ownership recorded correctly; BYOD terms accepted | Enrollment method per device; purchase records; acceptance records |
| Policy baseline | Passcode, auto-lock and failed-attempt lockout; encryption; minimum OS version; restrictions; policy changes through change control | Policy exports; encryption report; one on-device check per platform |
| Compliance status and exceptions | Per-device policy status reviewed on a schedule; an exceptions register with approvers and expiry dates | Status report; review notes; exceptions register |
| Patching and OS versions | OS updates inside the patch window; third-party app vulnerabilities fixed by severity | Patch report; vulnerability report; fix dates |
| Apps | App inventory per device; an allow or block list; business apps deployed through the MDM | App inventory export; block list; approvals |
| Remote lock and wipe | A dated lock and wipe test on each platform; only named roles can wipe | Test record with screenshots; role export |
| Lost, stolen and offboarded devices | Lost devices locked or wiped within the target time; leavers' devices returned and wiped; retired devices removed | Tickets; HR leaver list traced to devices; disposal records |
| Admin access | Least-privilege console roles; MFA on every console account; quarterly access review; leavers removed on their last day | Members export with roles and last-active dates; review records |
| Logging and evidence | Admin actions and remote sessions logged where the tool allows; reports kept for the whole period | Log excerpts traced to tickets; evidence index |
| Wi-Fi, VPN and certificates | Wi-Fi through WPA2 or WPA3 profiles; VPN profiles and certificates deployed by the MDM, expiry dates watched | Profile exports; certificate list |
| Personal devices (BYOD) | The BYOD terms match what IT can actually see and do; no full wipe of a personal device | Screenshots from a personal test device; wipe history |
| Vendor and integrations | A dated review of the MDM vendor; integrations listed with owners; unused tokens removed | Vendor review; integration register |
| Audit program | Yearly audit, quarterly coverage review, retest before closing a finding | Last report; findings log with retest evidence |
The CIS Controls v8 give exact numbers for three of these settings. They set session lock at no more than 2 minutes of inactivity on phones and tablets and 15 minutes on computers (safeguard 4.3). They also set device lockout after no more than 10 failed attempts on phones and tablets and 20 on laptops (safeguard 4.10). And they ask for remote wipe on company-owned portable devices (safeguard 4.11), which an auditor will want to see tested, not only switched on. Encryption policy belongs in your data encryption policy and update windows in your patch management policy.
MDM testing means checking that a control works on real devices, beyond reading its settings. NIST SP 800-53A, NIST's guide to assessing security controls, names three ways an assessor gathers evidence, and most MDM controls need at least two of them:
| Method | What you do | MDM example |
|---|---|---|
| Examine | Read documents, settings, reports and records. | The passcode policy in the console; the encryption report; a disposal record |
| Interview | Ask the people who run the control how it works and what happens when it fails. | Ask the IT manager what happens when a leaver's phone isn't returned |
| Test | Watch the control work, or do it yourself (re-performance). | Lock and wipe a test device; time the auto-lock on a sample phone |
Two techniques do most of the work. In a walkthrough, the person who runs a control shows it from start to finish, for example how a lost phone gets reported, locked and recorded. In re-performance, you or the auditor run the control yourselves, for example by sending a lock and a wipe to a spare test device of each platform and timing the response. Teams often skip this test because nobody wants to wipe a working device, so keep one spare device per platform for it.
For the evidence itself:
No framework sets one sample size for MDM audits, so agree it with your auditor. The template's default is 25 devices or 10% of the asset list, whichever is larger, up to the whole list. A 90-device company samples 25; a 400-device company samples 40. Spread the sample across platforms and ownership types in roughly the same proportion as the fleet, and add any device the reconciliation flagged.
For each sampled device, check six things in the MDM: is it on the asset list, is it enrolled, is encryption on, does it follow the passcode policy, is the OS current, and were its policies applied. Check two or three devices by hand as well. The Device Sample tab marks a device Fail on any No, or when it hasn't checked in within the inactive-days limit (30 by default). With the default tolerance of zero, one failed device fails the sample, and each failure becomes a finding.
A sample shows whether the controls work on the devices you picked. Coverage numbers show how far they reach across the whole fleet. Take these counts on the same day and compare each one with a target:
| Measure | Share of | Template target |
|---|---|---|
| Enrolled in the MDM | Company devices on the asset list | 98% or more |
| Encryption on | Enrolled devices | 98% or more |
| On a current, supported OS | Enrolled devices | 95% or more |
| Following the passcode policy | Enrolled devices | 98% or more |
| No check-in for more than 30 days | Enrolled devices | 5% or less |
| In the MDM but not on the asset list | A count | 0 |
The targets are defaults, not a standard. Set your own in the tracker's Settings tab, and review the numbers every quarter between audits.
Most of these are process gaps. Leavers' phones, for example, stay assigned when IT isn't on the HR leaver list. The IT offboarding checklist closes that gap, and a user access review covers the console admins.
If staff enroll their own phones, the audit checks two things that pull in opposite directions: the company data on the phone is protected, and IT doesn't reach further into the phone than the BYOD terms say. Enroll a personal test device, compare what the console shows and allows with what the terms promise, and check the wipe history for any full wipe of a personal device. What IT can do depends on the platform. On Android a work profile keeps work apps in their own profile. Apple's personal enrollment covers the whole device, so the terms should spell out what IT can and can't do. The BYOD policy template and the remote work policy template cover the employee side.
Once a year for the full audit is the usual rhythm, and the timing often follows a SOC 2, ISO 27001 or customer audit that asks for device evidence. Between audits, review the coverage numbers every quarter, review console access every quarter, and retest each finding before you close it. Audit again sooner after a big change, such as a move to a new MDM, a merger or a new platform. For the rest of the IT estate, use the IT audit checklist.
No framework has a section called MDM, but several have controls an MDM carries out. This reading aid shows where each domain sits. It isn't an official mapping.
| Checklist domain | CIS Controls v8 | NIST SP 800-53 | ISO 27001:2022 Annex A |
|---|---|---|---|
| Scope and inventory | 1.1, 1.2 | CM-8 | A.5.9 |
| Enrollment and ownership | 4.1, 4.12 | AC-19 | A.8.1 |
| Policy baseline | 3.6, 4.1, 4.3, 4.10 | AC-19, AC-19(5) | A.8.1 |
| Compliance status and exceptions | 4.1 | AC-19 | A.8.1 |
| Patching and OS versions | 7.3, 7.4 | - | A.8.1 |
| Apps | 2.1, 2.3 | CM-8 | A.8.1 |
| Remote lock and wipe; lost, stolen and offboarded devices | 4.11 | AC-19 | A.8.1 |
| Admin access | 5.4, 6.5 | - | - |
| Logging and evidence | 8.2 | - | - |
| Personal devices (BYOD) | 4.12 | AC-19 | A.8.1 |
In NIST SP 800-53 Rev. 5, AC-19 is Access Control for Mobile Devices (its enhancement AC-19(5) covers device encryption) and CM-8 is System Component Inventory. NIST SP 800-124 Rev. 2 (May 2023) is NIST's guide to managing the security of mobile devices in the enterprise, and a good read before scoping. In ISO/IEC 27001:2022 Annex A, control 5.9 covers the inventory of information and other assets and 8.1 covers user endpoint devices. SOC 2 and HIPAA audits also ask for device evidence such as encryption and access records, but neither names MDM controls, so they aren't mapped.
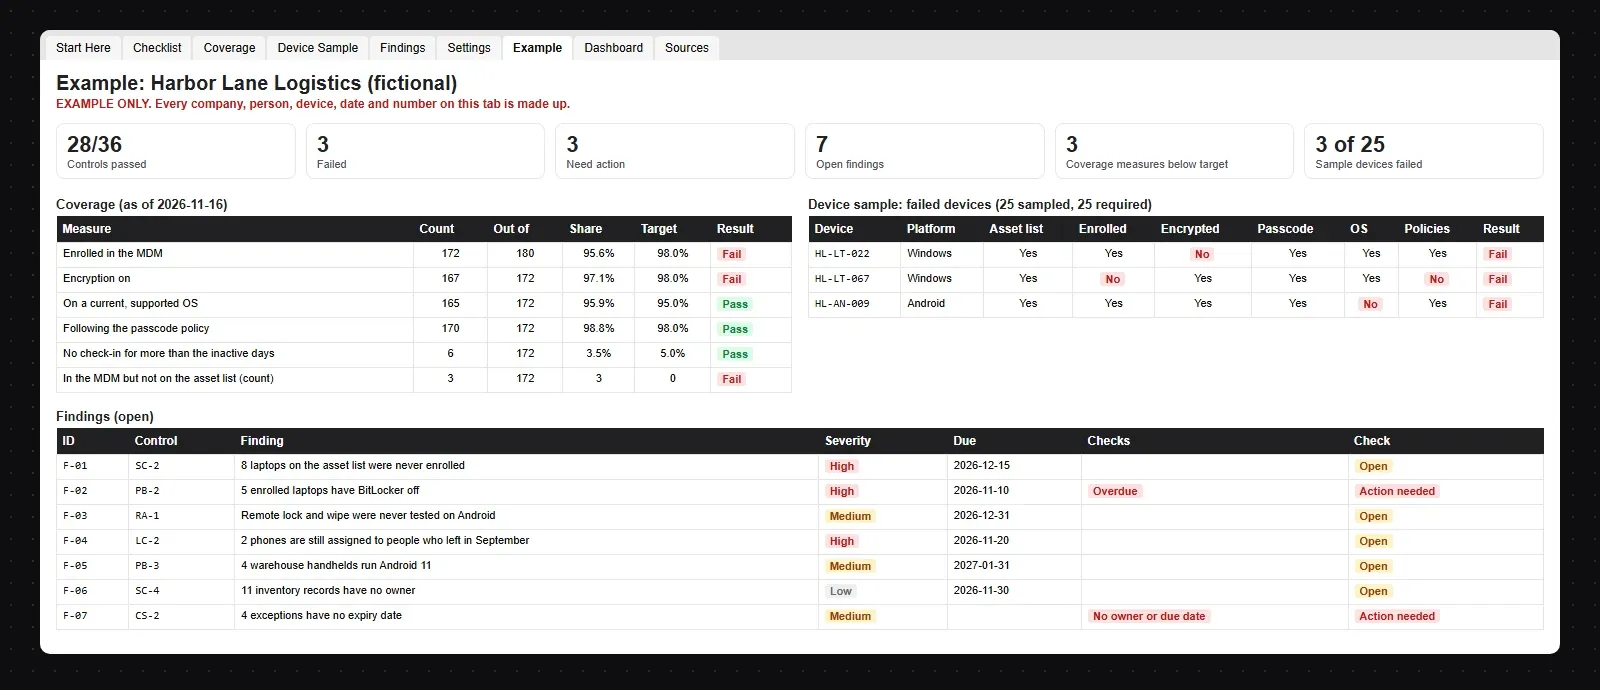
The download includes a finished audit for Harbor Lane Logistics (fictional), a made-up freight forwarder with 140 people and 180 company devices: 96 Windows laptops, 22 MacBooks, 48 Android phones and handhelds and 14 iPhones. The audit covers January to October 2026.
Coverage: 172 of 180 devices are enrolled (95.6%, under the 98% target), 167 of the 172 have encryption on (97.1%, under target), and 3 devices sit in the MDM without being on the asset list. OS currency (95.9%), the passcode policy (98.8%) and inactive devices (3.5%) are within target. The sample of 25 devices has 3 failures: a laptop with BitLocker off, a laptop that never enrolled, and a warehouse handheld on Android 11. So the sample fails.
Of 36 controls, 28 pass, 4 are partial and 3 fail. The findings log:
| ID | Control | Finding | Severity | Due |
|---|---|---|---|---|
| F-01 | SC-2 | 8 laptops on the asset list were never enrolled | High | 2026-12-15 |
| F-02 | PB-2 | 5 enrolled laptops have BitLocker off | High | 2026-11-10 |
| F-03 | RA-1 | Remote lock and wipe were never tested on Android | Medium | 2026-12-31 |
| F-04 | LC-2 | 2 phones are still assigned to people who left in September | High | 2026-11-20 |
| F-05 | PB-3 | 4 warehouse handhelds run Android 11 | Medium | 2027-01-31 |
| F-06 | SC-4 | 11 inventory records have no owner | Low | 2026-11-30 |
| F-07 | CS-2 | 4 exceptions have no expiry date | Medium | No date yet |
The fix plan starts with the overdue BitLocker finding (the policy was scoped to the office group only) and the two leavers' phones, then the eight laptops that never enrolled. Last year's patch finding was closed only after a retest in March, and the rest should close the same way.
The workbook has five working tabs. The Checklist comes prefilled with every control and flags a Fail or Partial with no owner or due date, an overdue fix and a Pass with no evidence reference. Coverage takes seven counts and compares each share with its target. Device Sample works out the required sample size and the result for each device and for the sample. Findings flags missing owners, overdue fixes and findings closed without retest evidence. A Dashboard shows the pass rate by domain, open findings by severity, coverage and the sample result. Formulas only, no macros.
trio.so is the MDM being audited here, so the console is where most of the evidence comes from. It doesn't run the audit, pick the sample or judge the result: that stays with you and your auditor. For each domain, this is what the trio.so console gives the auditor:
| What the console shows or exports | Checklist domain |
|---|---|
| A device inventory with each device's owner, serial number, installed apps and encryption status | Scope and inventory (SC-2, SC-4), Apps (AP-1) |
| Enrollment through Apple Business (formerly Apple Business Manager), Android Enterprise, and Entra join or bulk enrollment with a provisioning package on Windows | Enrollment and ownership (EN-1) |
| Passcode policies for iPhone, iPad and Android, BitLocker on Windows, FileVault on Mac and required storage encryption on Android | Policy baseline (PB-1, PB-2) |
| Policy status for each device: applied, failed or pending | Compliance status (CS-1) |
| An alert when a device reports an unencrypted disk | Policy baseline (PB-2) |
| Vulnerability findings matched to CVEs with CVSS, EPSS and CISA KEV data, and a risk score from 0 to 100 for each device | Patching (PT-2) |
| OS updates through Auto Patch policies and third-party fixes through remediation plans, with the result shown for each device | Patching (PT-1, PT-2) |
| Remote lock on Mac, iPhone, iPad and Android, and remote wipe of company-owned devices | Remote lock and wipe (RA-1), offboarding (LC-1, LC-2) |
| Console roles, and a CSV export of console members with their roles, status and last-active dates | Admin access (AD-1, AD-3, RA-2) |
| User sync from Microsoft Entra ID and Google Workspace and SCIM 2.0 provisioning; MFA and single sign-on for your users are in the Zero Trust plan | Admin access (AD-3), offboarding (LC-2) |
| A log of remote desktop sessions: who started each one, and when it started and ended | Logging (LG-1) |
| Wi-Fi profiles with WPA2 or WPA3 on Windows and Apple devices, and PKCS#12, SCEP and root certificates on Apple devices and Windows | Wi-Fi, VPN and certificates (NW-1, NW-2) |
| On personal iPhones, iPads and Macs, IT can't erase, lock or locate the device; on Android, work apps sit in their own work profile | Personal devices (BY-1, BY-2) |
| Compliance evidence exports for the audit file | Logging and evidence (LG-2) |
| For MSPs: several client companies in one console, each with its own devices, users and policies | MSPs running audits for clients |
It doesn't run the audit for you. You still pick the sample, test the controls and judge the results, and the vendor review (VN-1) is your review of trio.so. trio.so manages Windows, macOS, Linux, iOS/iPadOS and Android from one console. See mobile device management in trio.so, patch management and compliance evidence. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026.
trio.so shows each device's owner, serial number, apps and encryption status, policy results per device, CVE findings and patch results, and exports evidence for your audit file.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Free MDM rollout checklist in Word and PDF: requirements, APNs and platform prerequisites, a policy baseline, pilot and go-live forms, plus a tracker.

What J-SOX is, how it differs from US SOX, and a checklist of J-SOX requirements from scoping to the internal control report.
Free TISAX audit checklist in Word and PDF: assessment levels, labels, VDA ISA areas and the evidence to prepare, plus an Excel self-assessment tracker.
Learn how you can improve your resource allocation strategy & download the IT Resource Allocation Template to optimize your IT resource management.
Free IT audit checklist template in Excel, PDF and Word: 66 checks in 8 areas, an audit questionnaire, a findings tracker and a filled-in example.
Free IT contingency plan template in Word and Excel, with a filled-in example: BIA with MTD, RTO and RPO, call tree, recovery steps and test forms.
Free SDLC policy template with security work for every phase, release gates, a checklist, sign-off form, framework mapping and an Excel tracker.
Free NIS2 checklist in Excel, PDF and Word: check who is in scope, work through the ten Article 21 measures, supplier security and 24h/72h reporting.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients