




Templates
J-SOX Compliance Requirements: What It Is and a Checklist
What J-SOX is, how it differs from US SOX, and a checklist of J-SOX requirements from scoping to the internal control report.
Free MDM rollout checklist in Word and PDF: requirements, APNs and platform prerequisites, a policy baseline, pilot and go-live forms, plus a tracker.

Content writer, trio.so
An MDM rollout tends to go wrong in the same places: an Apple certificate created with someone's personal account, a firewall that quietly breaks enrollment, a pilot with no exit criteria, and staff who first hear about device management from a prompt on their phone. A checklist with an owner and a date on every item catches most of these early.
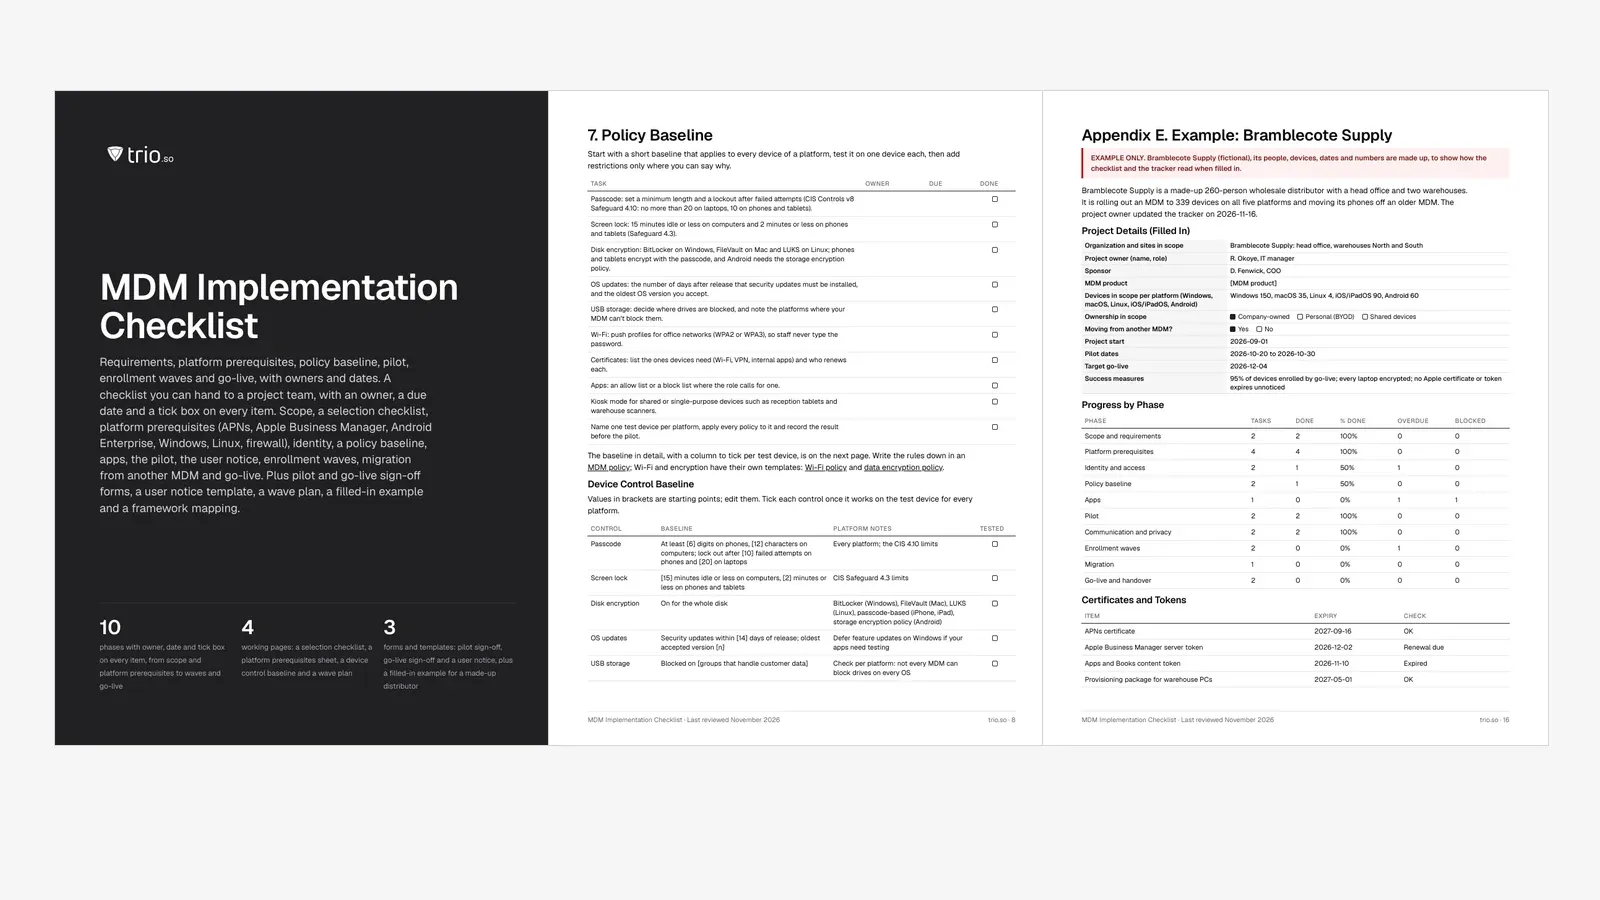
This one is for IT managers and sysadmins at companies of 20 to 1,000 people rolling out MDM for the first time or switching products, and for MSPs doing it for a client. The download has the checklist in Word and PDF, with a selection checklist, a platform prerequisites sheet, a device control baseline, pilot and go-live sign-off forms, a user notice template and a filled-in example. An Excel tracker covers tasks, certificate and token renewals, enrollment waves, the pilot result and risks.
In short
Our guide to mobile device management implementation explains each phase and ends with a 30/60/90-day plan. This page and its download are the working copy: the items to tick, who owns each one and when it is due. Read the guide for the reasoning behind a phase, and run the project from the checklist and the tracker.
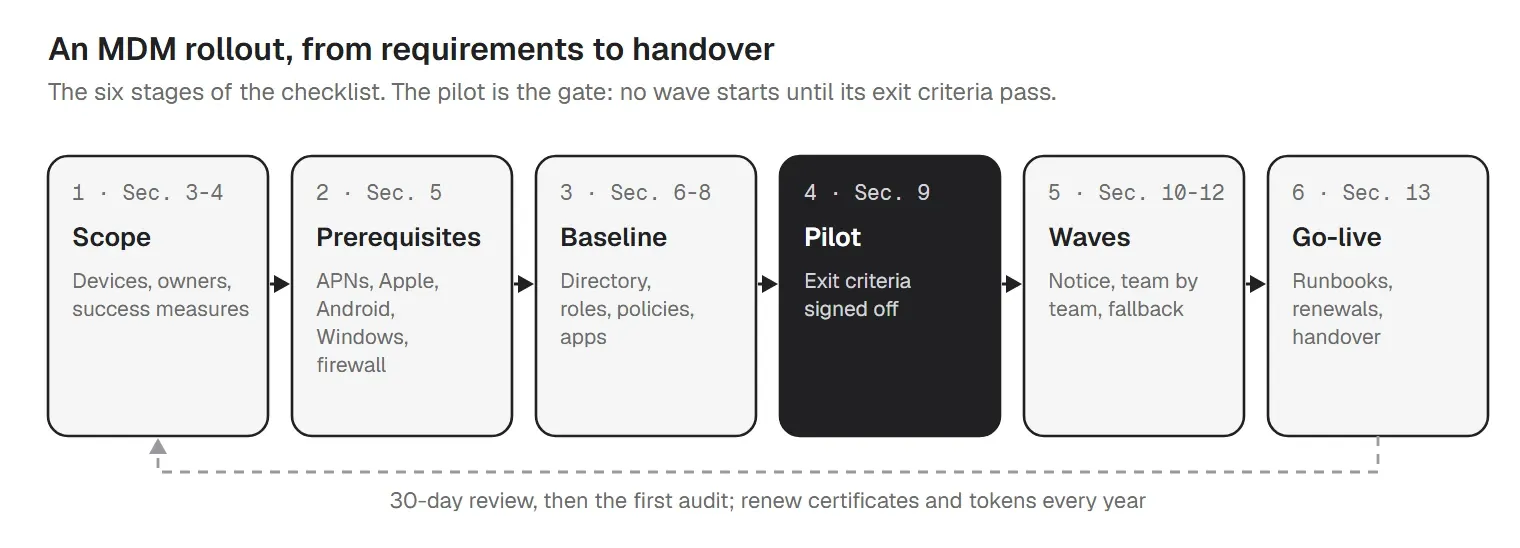
Choosing the product comes before the rollout. Section 4 of the download is a one-page selection checklist with columns for two products side by side. The must-haves:
Nice to have, depending on your fleet: kiosk mode, USB storage control, Wi-Fi and certificate profiles, remote desktop, single sign-on for users' apps, evidence exports for audits and, for MSPs, several client organizations in one console. Check prices against your device count with our guide to MDM pricing.
Start with numbers: devices per platform (Windows, macOS, Linux, iOS/iPadOS and Android), who owns each group of devices, and the user groups that need different setups, such as office staff, field staff and shared tablets. Count from purchase records and the user directory rather than from memory; the gap between the two usually turns up devices nobody listed. Then write three to five success measures you can check on go-live day, for example 95% of devices enrolled and every laptop encrypted, and name an owner for each platform. If personal devices are in scope, settle the rules in a BYOD policy before anyone enrolls one.
Several of these steps wait on another company or another team, so start them in week one.
| Platform | What you need | Watch for |
|---|---|---|
| Apple: APNs certificate | An Apple Push Notification service certificate from the Apple Push Certificates Portal, created with a company Apple Account that more than one person can reach. | Valid for 365 days. Renew it with the same Apple Account: a new certificate under a different account means enrolling every Apple device again. |
| Apple Business Manager or Apple School Manager | Your MDM added as an MDM server, its server token loaded into the MDM, devices assigned for automated device enrollment, and Apps and Books if you buy apps. | The server token and the Apps and Books token each expire after a year. Put both dates in the tracker. |
| Android | Android Enterprise bound to the MDM with a company Google account, enrollment tokens or QR codes per group, and zero-touch enrollment through your reseller for new company devices. | Decide per group: fully managed for company devices, a work profile for personal ones. |
| Windows | Microsoft Entra join with automatic MDM enrollment, or bulk enrollment with a provisioning package for shared and pre-staged PCs. | Check the MDM user scope in Entra ID before the pilot. |
| Linux | The distributions in scope, the agent's install script and token, and the people who hold root on those machines. | Plan how the script reaches each machine. |
For the firewall, Apple's enterprise network guide asks you to allow *.push.apple.com on TCP 443, 2197 and 5223, plus its enrollment and MDM hosts, or 17.0.0.0/8 if your firewall only takes IP ranges. Google's Android Enterprise list needs TCP 443 and TCP and UDP 5228 to 5230 to hosts such as play.google.com and fcm.googleapis.com. Both say intercepted HTTPS connections fail, so keep these hosts out of SSL inspection. Finish by enrolling one test device per platform from the office, from home and over mobile data. For the Apple side in more detail, see Apple Business Manager; for new devices that set themselves up, see zero-touch deployment.
Connect your directory (Microsoft Entra ID, Google Workspace, Okta or OneLogin) so users and groups sync into the MDM instead of being typed in, and decide whether accounts arrive by directory sync or SCIM provisioning. Map directory groups to device groups and policies, such as Finance laptops or Warehouse handhelds. In the console, give each admin a role with only the rights their job needs, turn on MFA for every admin account, and write down who may approve a remote wipe. Keep one break-glass admin account with its credentials stored offline for the day the identity provider is down.
Keep the first baseline short, apply it to one test device per platform, and add a restriction only when you can say why it is there. The download's baseline page has a column to tick for each test device:
| Control | Starting point | Notes |
|---|---|---|
| Passcode | At least [6] digits on phones, [12] characters on computers; lock out after [10] failed attempts on phones and [20] on laptops | Every platform; the CIS 4.10 limits |
| Screen lock | [15] minutes idle or less on computers, [2] minutes or less on phones and tablets | CIS Safeguard 4.3 limits |
| Disk encryption | On for the whole disk | BitLocker (Windows), FileVault (Mac), LUKS (Linux), passcode-based (iPhone, iPad), storage encryption policy (Android) |
| OS updates | Security updates within [14] days of release; oldest accepted version [n] | Defer feature updates on Windows if your apps need testing |
| USB storage | Blocked on [groups that handle customer data] | Check per platform: not every MDM can block drives on every OS |
| Wi-Fi | Office networks pushed as profiles, WPA2 or WPA3 | No shared passwords typed by staff |
| Certificates | [Wi-Fi, VPN, internal app] certificates pushed by the MDM | Note the renewal owner |
| Apps | Allow list or block list for [roles] | Only where the role needs it |
| Kiosk | One app or a fixed set of apps on [shared devices] | Reception tablets, scanners, shared PCs |
The screen lock and lockout values come from the CIS Controls v8. Safeguard 4.3 caps idle time at 15 minutes on computers and 2 minutes on mobile devices, and Safeguard 4.10 allows no more than 20 failed attempts on laptops and 10 on phones and tablets. Write the rules into an MDM policy; Wi-Fi and encryption have their own templates, the Wi-Fi policy and the data encryption policy.
List the required apps per group and platform, then pick a deployment method for each: an app catalog or package upload on computers, Apple Apps and Books on iPhone, iPad and Mac, and managed Google Play on Android. Buy or move licenses before the pilot. Apple licenses go through Apps and Books in Apple Business Manager, and a token still tied to an old MDM blocks the move. Decide which apps are required and which users install from the catalog, and test the first sign-in of every required app on the test devices.
Pick about 5 to 10% of users, with at least two devices on every platform and ownership type you plan to roll out. Include a manager and someone who calls the helpdesk often. Agree the exit criteria before the pilot starts; the tracker's defaults are:
Run it for at least two weeks, long enough to see an OS update and a password change. The pilot sign-off form records the results and the decision: go to wave 1, extend the pilot, or stop and rethink.
Send a notice at least a week before each wave: what changes, the date, what to do and who to ask. Say what IT can and can't see. On personal iPhones, iPads and Macs enrolled through Apple's personal enrollment, IT can't erase, lock or locate the device; on Android, work apps sit in their own work profile. The download has a notice template you can edit, and the implementation guide covers this conversation in its section on what MDM can and cannot track. If you have a works council or employee representatives, involve them before the pilot, and have HR or counsel review the notice.
Roll out by team or site, so each team changes over on one day and gets help on that day. Each wave gets a date, an owner, a planned device count per platform and a fallback for failed enrollments: a walk-up desk, a spare device or a booked call. The tracker works out each wave's enrollment % and marks it Behind target once its date has passed below the target, 95% by default. Don't start the next wave while the last one is behind.
After the last wave, check that every company device on the asset list is enrolled or has a recorded reason. CIS Safeguards 1.1 and 1.2 cover the asset inventory and devices that shouldn't be on the network. New starters after go-live follow the IT onboarding checklist.
MDM products rarely import each other's settings, so rebuild policies and apps as a fresh baseline and export the old device list with serial numbers first. Move one group at a time: remove it from the old MDM and enroll it in the new one on the same day. Company iPhones, iPads and Android devices usually need a reset, so plan backups and the time per device, and assign Apple devices to the new MDM server in Apple Business Manager before you reset them. Keep the old licenses until the last wave is done. Moving to trio.so? See switching to trio.so.
At go-live, the team that runs devices day to day takes over. Hand them runbooks for a lost or stolen device, a new starter, a leaver (the IT offboarding checklist covers the account side), a device replacement and a failed enrollment, plus the admin accounts and the patch schedule. Put the APNs certificate, the Apple Business Manager token and the Apps and Books token in a shared calendar a month before each expiry. Review enrollment, policy failures and tickets after 30 days, and schedule the first audit three to six months out with the MDM audit checklist.
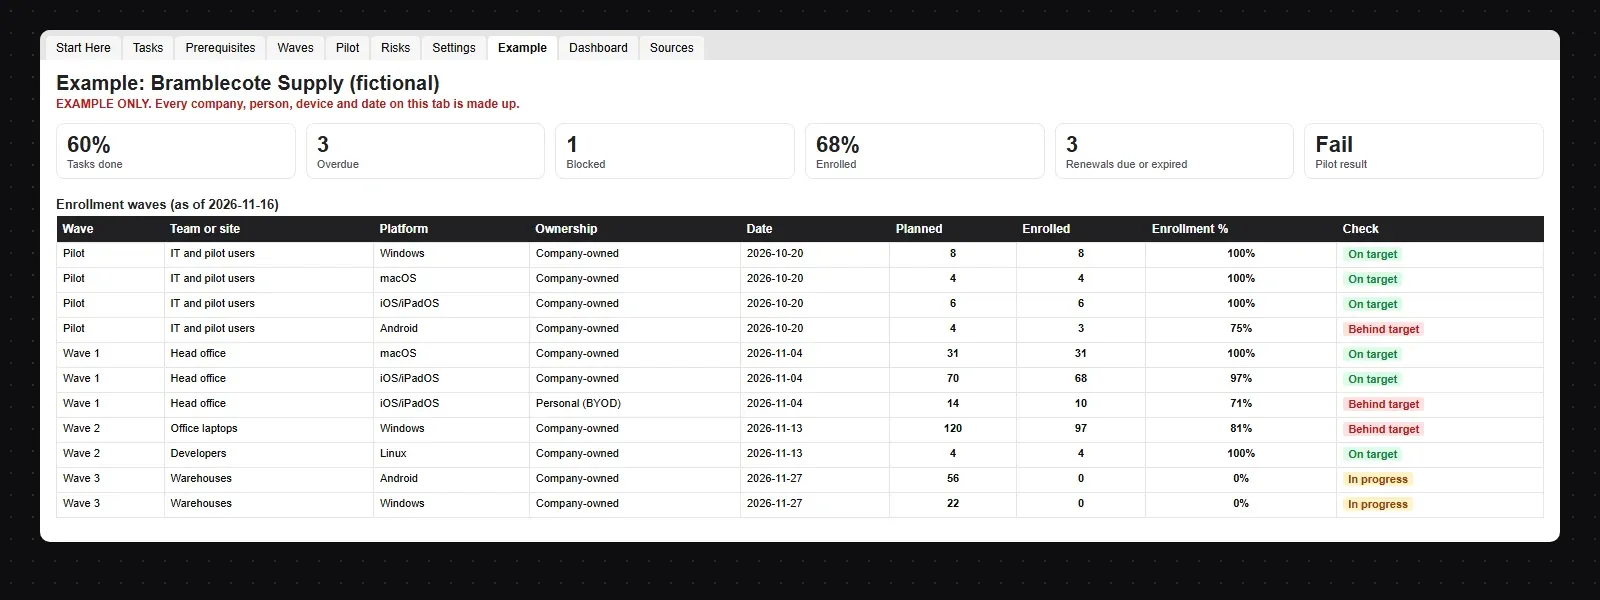
The download includes a filled-in tracker for Bramblecote Supply, a made-up 260-person distributor rolling out to 339 devices on all five platforms. On 16 November, 12 of its 20 tracked tasks were done and 68% of devices were enrolled:
| Wave | Platform | Enrolled | % | Check |
|---|---|---|---|---|
| Pilot | Windows (company-owned) | 8 of 8 | 100% | On target |
| Pilot | macOS (company-owned) | 4 of 4 | 100% | On target |
| Pilot | iOS/iPadOS (company-owned) | 6 of 6 | 100% | On target |
| Pilot | Android (company-owned) | 3 of 4 | 75% | Behind target |
| Wave 1 | macOS (company-owned) | 31 of 31 | 100% | On target |
| Wave 1 | iOS/iPadOS (company-owned) | 68 of 70 | 97% | On target |
| Wave 1 | iOS/iPadOS (personal) | 10 of 14 | 71% | Behind target |
| Wave 2 | Windows (company-owned) | 97 of 120 | 81% | Behind target |
| Wave 2 | Linux (company-owned) | 4 of 4 | 100% | On target |
| Wave 3 | Android (company-owned) | 0 of 56 | 0% | In progress |
| Wave 3 | Windows (company-owned) | 0 of 22 | 0% | In progress |
Wave 2's office laptops are three days past their date at 81%, because 23 of them need a firmware update first. The Apps and Books token expired on 10 November, and the Apple Business Manager token runs out two days before go-live. The pilot missed its enrollment target (91% against 95%) and was signed off with one fix. Every admin can still wipe devices, because the console roles are a week late.
The download's mapping (Appendix F) points each section to these references, as a reading aid:
| Framework | Where it shows up |
|---|---|
| CIS Controls v8 | 1.1 and 1.2 asset inventory and unauthorized assets; 4.1 secure configuration process; 4.3 automatic session locking; 4.10 device lockout after failed attempts; 4.11 remote wipe on portable devices; 4.12 separate enterprise workspaces on mobile devices. |
| NIST SP 800-124 Rev. 2 | Guidelines for Managing the Security of Mobile Devices in the Enterprise (May 2023): recommendations for deployment, use and disposal across the device lifecycle. |
Your auditor decides what counts for your scope. Once the MDM is live, the MDM audit checklist tests whether the controls work.
The workbook has one tab for each part of the checklist:
trio.so is an MDM you can roll out with this checklist. It covers the device side of every phase, from enrollment and the policy baseline to apps, updates and the runbooks after go-live. Scope, the pilot decision, the user notice and the works council stay with you. In practice that means:
It doesn't pick your scope, decide when the pilot passes or talk to your works council. It also doesn't record what people do on their devices: it shows the state of the device, not the activity of the person using it. It manages Windows, macOS, Linux, iOS/iPadOS and Android from one console. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026. Framework references are short pointers to the CIS Controls v8 and NIST SP 800-124 Rev. 2; network and certificate details come from Apple, Google and Microsoft documentation. The wording is ours. trio.so is not affiliated with or endorsed by the Center for Internet Security, NIST, Apple, Google or Microsoft.
trio.so manages Windows, macOS, Linux, iOS/iPadOS and Android in one console, with enrollment through Apple Business, Android Enterprise and Entra join, passcode and encryption policies, and each policy's status per device.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
What J-SOX is, how it differs from US SOX, and a checklist of J-SOX requirements from scoping to the internal control report.
Free TISAX audit checklist in Word and PDF: assessment levels, labels, VDA ISA areas and the evidence to prepare, plus an Excel self-assessment tracker.
Learn how you can improve your resource allocation strategy & download the IT Resource Allocation Template to optimize your IT resource management.
Free IT audit checklist template in Excel, PDF and Word: 66 checks in 8 areas, an audit questionnaire, a findings tracker and a filled-in example.
Free IT contingency plan template in Word and Excel, with a filled-in example: BIA with MTD, RTO and RPO, call tree, recovery steps and test forms.
Free SDLC policy template with security work for every phase, release gates, a checklist, sign-off form, framework mapping and an Excel tracker.
Free NIS2 checklist in Excel, PDF and Word: check who is in scope, work through the ten Article 21 measures, supplier security and 24h/72h reporting.
Learn how to create a comprehensive Request for Information (RFI) template tailored for IT admins.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients