



How-Tos
Mobile Device Management (MDM) Implementation Guide for SMBs
Learn how SMB IT managers and admins can secure, automate, and scale device management with the right MDM implementation strategy.
Device provisioning for employee laptops and phones: zero-touch with Apple Business, Windows Autopilot and Android Enterprise, a checklist, and fixes.

Content writer, trio.so
Device provisioning is the work of getting a new laptop, phone or tablet ready for the person who will use it: enrolling it in your management system, applying security settings, installing the apps their role needs and connecting it to their work account. Done well, it happens before or during the device's first start-up, so the employee unboxes a device that is already secure and ready to work. Today most of it can be automated: Apple Business for iPhones, iPads and Macs, Windows Autopilot for Windows PCs and Android Enterprise zero-touch or QR code enrollment for Android, all feeding the same set of standard configurations.
If you are the person who sets up devices for new joiners and you want them to arrive ready with as little hands-on work as possible, the six practices, the zero-touch guide and the checklist below are the parts to use. This post is about employee devices; network, IoT and cloud "provisioning" mean something different and are not covered here.
Device provisioning is setting up and preparing a device so it can be used safely inside your organization. According to Insight, it is "one of the first steps in the IT lifecycle process." It has two parts: enrollment and configuration.
Enrollment registers the device with your management system and links it to a user, a group or a location. For company-owned devices this can happen automatically during setup; for personal devices the employee usually starts it by signing in with a work account. Our guides to MDM enrollment and Windows device enrollment cover the steps for each platform.
Configuration applies your settings: Wi-Fi, email, passcode and encryption rules, restrictions, and the apps for the employee's role. On a well-run fleet, configuration comes from standard templates, so two people in the same team get the same setup.
These six practices apply whether you provision ten devices a year or ten a week.
Before you automate anything, write down what each type of device needs: the apps, settings and permissions for each role. Then turn that list into standard configurations, so every new device for the same role gets the same setup without anyone making it up on the day.
Use one management platform for every device type instead of a separate tool per operating system. One console means one place to enroll devices, apply policies, check status and push updates.
Test your provisioning flow before it reaches real employees, then keep watching it. A setup that worked last quarter can break when a token expires or an operating system update changes a setup screen.
Employees should know what will happen when they turn on a new device and who to call if it does not. IT staff need a written runbook for the cases automation does not cover.
Design the process so adding ten or a hundred new hires needs no extra manual steps. If a step only works because one person remembers to do it, it will fail when that person is away.
Provisioning is not set-and-forget. Review your templates and policies at least twice a year, and after every major operating system release.
Zero-touch provisioning means a device ships straight from the reseller to the employee and sets itself up on first start-up, without IT handling it. Each platform has its own route. For a deeper guide, see zero-touch deployment.
| Platform | Programme | What you need |
|---|---|---|
| iPhone, iPad, Mac | Automated Device Enrollment in Apple Business (formerly Apple Business Manager) | An Apple Business account, devices bought from Apple or an authorized reseller, and your MDM linked and set as the default service. See Apple DEP. |
| Windows PCs | Windows Autopilot | Microsoft Entra ID, devices registered by the reseller or by uploading hardware hashes, and an Autopilot profile. |
| Android | Android Enterprise zero-touch enrollment, or QR code enrollment | Devices from a zero-touch reseller, or a QR code from your MDM scanned on the welcome screen. See Android QR code enrollment. |
Roll out a new provisioning setup in three steps rather than all at once:
Track four numbers throughout: enrollment success rate, time from unboxing to a working device, help desk tickets per new device, and how many devices had to be set up again by hand.
Some devices cannot reach the internet on first start-up, for example at secure sites or remote locations. For those, provision locally and let the device catch up when it connects:
Once the device is online, your MDM delivers the remaining policies and apps.
| Symptom | Likely cause | Fix |
|---|---|---|
| Device does not enroll | Expired MDM token or certificate | Renew the token or certificate and sync again |
| Stuck on a setup screen | Firewall blocking Apple, Google or Microsoft addresses | Allow the vendor's enrollment addresses on the network |
| Apps do not install | No free license, or the app is not assigned to the user's group | Check the license count and group assignment |
| Wi-Fi will not connect | Captive portal, or the wrong network name in the profile | Use a network without a portal, or fix the Wi-Fi profile |
| Policy does not apply | Device is in the wrong group | Check group membership and reassign |
| Enrollment restarts in a loop | Outdated provisioning package | Rebuild the package and apply it again |
Before you roll out provisioning to everyone, confirm:
Personal devices are provisioned differently: the employee enrolls them, and only work apps and data are managed. Tell employees plainly what the company can and cannot see.
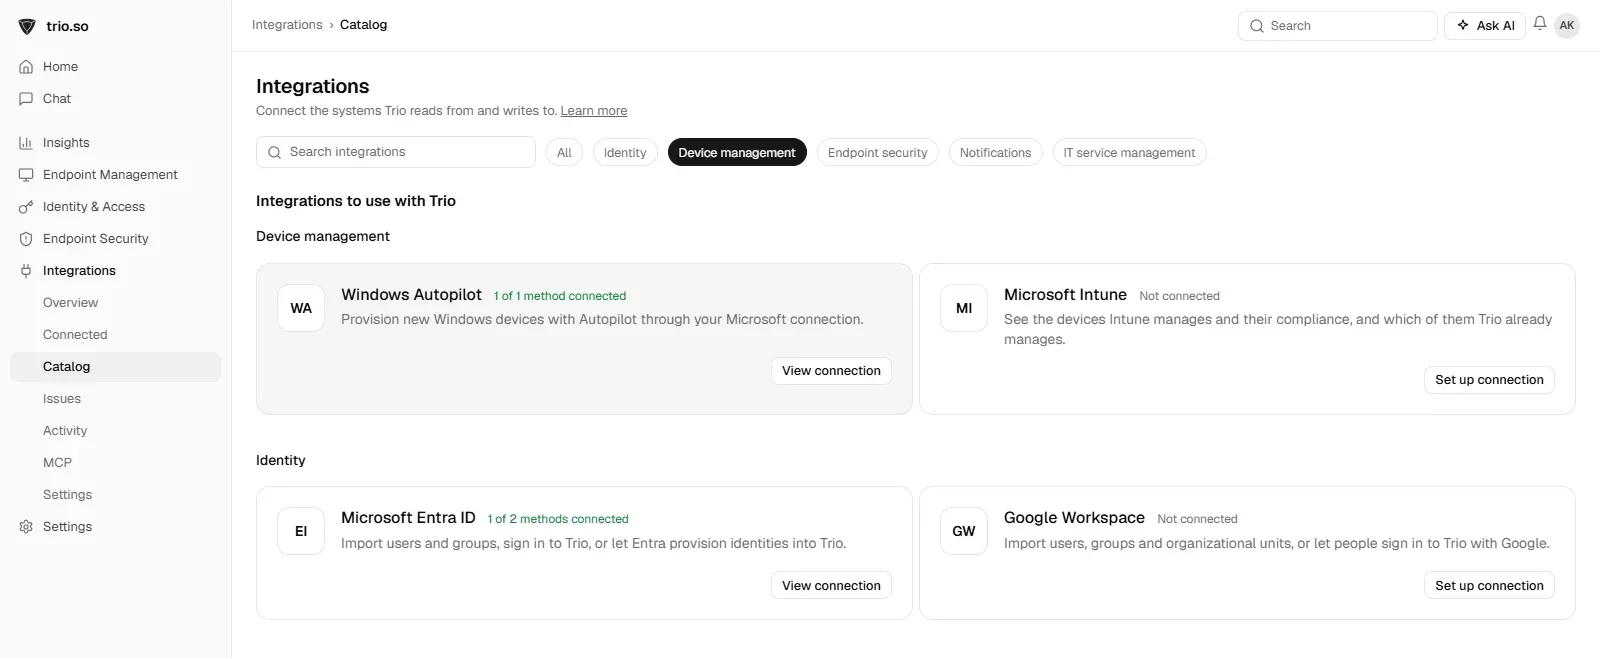
trio.so enrolls Windows PCs through Windows Autopilot, Entra join with automatic enrollment or a bulk provisioning package, Apple devices through Apple Business, and Android devices through Android Enterprise with a QR code or zero-touch enrollment. Policies and apps apply at first start-up, so a new laptop or phone reaches the employee ready to use. See Windows device management.
Good device provisioning means new employees start work on day one with a device that is already secure and set up for their role. Standardize your configurations, manage every platform from one place, automate enrollment with Apple Business, Windows Autopilot and Android Enterprise, and keep a checklist and a fallback for the cases automation misses. For the wider joiner process, see our guide to new hire onboarding.
Setting up a new device for the person who will use it: enrolling it in management, applying security settings, installing role apps and connecting it to their work account.
Enrollment is one part of provisioning: registering the device with your management system. Provisioning also includes the configuration and apps that make the device ready to use.
A device ships straight to the employee and sets itself up on first start-up, through Apple Business, Windows Autopilot or Android Enterprise zero-touch, without IT handling it.
Register it with Windows Autopilot or Apple Business, assign it to your MDM with the right profile for the employee's role, and ship it. On first start-up the employee signs in and the device enrolls and configures itself.
Preparing a device without an internet connection, for example with a Windows provisioning package on a USB stick, an Android QR code or Apple Configurator. The device gets the rest of its settings once it connects.
trio.so enrolls Windows PCs through Autopilot, Apple devices through Apple Business and Android through Android Enterprise, with your settings applied on first start-up.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Learn how SMB IT managers and admins can secure, automate, and scale device management with the right MDM implementation strategy.
An effective MDM strategy can improve an organization. Read on to learn how Mobile Device Management solutions can help you.
A mobile device management policy sets the governance rules for device use, security, and enforcement, here is how to structure one that works.
A crucial aspect of MDM solutions is MDM migration. This article will explore MDM migration, its types, benefits, challenges, and best practices.
On-premise MDMs have specific advantages to them, but are they better than cloud –based MDM solution? Read on to find out.
Cloud Mobile Device Management solutions are changing how IT administrators manage organizational devices. Let’s discuss how they achieve that.
What mobile device management (MDM) is, how it works on Apple, Android and Windows, what it can see on company and personal phones, and how to choose MDM.
Looking for MaaS360 alternatives? Discover top solutions that offer better features, pricing, and flexibility for IT teams.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients