



Explained
Mac Administrator Account: Find, Reset and Change the Admin Password
Find your Mac administrator name, reset a forgotten admin password from Recovery or your Apple Account, and make a user an admin, with notes for IT.
What a kernel extension policy does on macOS, how to allow a kext on Intel and Apple silicon Macs, system extensions vs kexts, and how MDM approves them.

Content writer, trio.so
A kernel extension policy is a setting, delivered to managed Macs by an MDM, that lists which kernel extensions (kexts) are allowed to load, by the developer's Team ID or by each extension's bundle ID, so users are not asked to approve them one by one. Kernel extensions are code that runs inside the macOS kernel, used by older security, VPN, storage and hardware tools. Apple no longer recommends them: since macOS 11 they cannot load on demand, every new one needs approval and a restart, and on Macs with Apple silicon the security policy must also be lowered to Reduced Security before any third-party kext can load. Most current tools use system extensions instead, which run outside the kernel and are approved with a separate system extension policy.
If your security or VPN tool keeps showing "System Extension Blocked" on your Macs, the steps below show how to allow it by hand and how to approve it for the whole fleet through MDM, and whether you still need a kernel extension at all.
A kernel extension is a bundle with a .kext extension that adds code to the macOS kernel, giving it low-level access to hardware and the system. That power is why Apple restricts it: a faulty kext can crash the whole Mac, and a malicious one has full control. Since macOS High Sierra, a new third-party kext needs the user's approval before it loads, and an MDM can grant that approval in advance with a kernel extension policy.
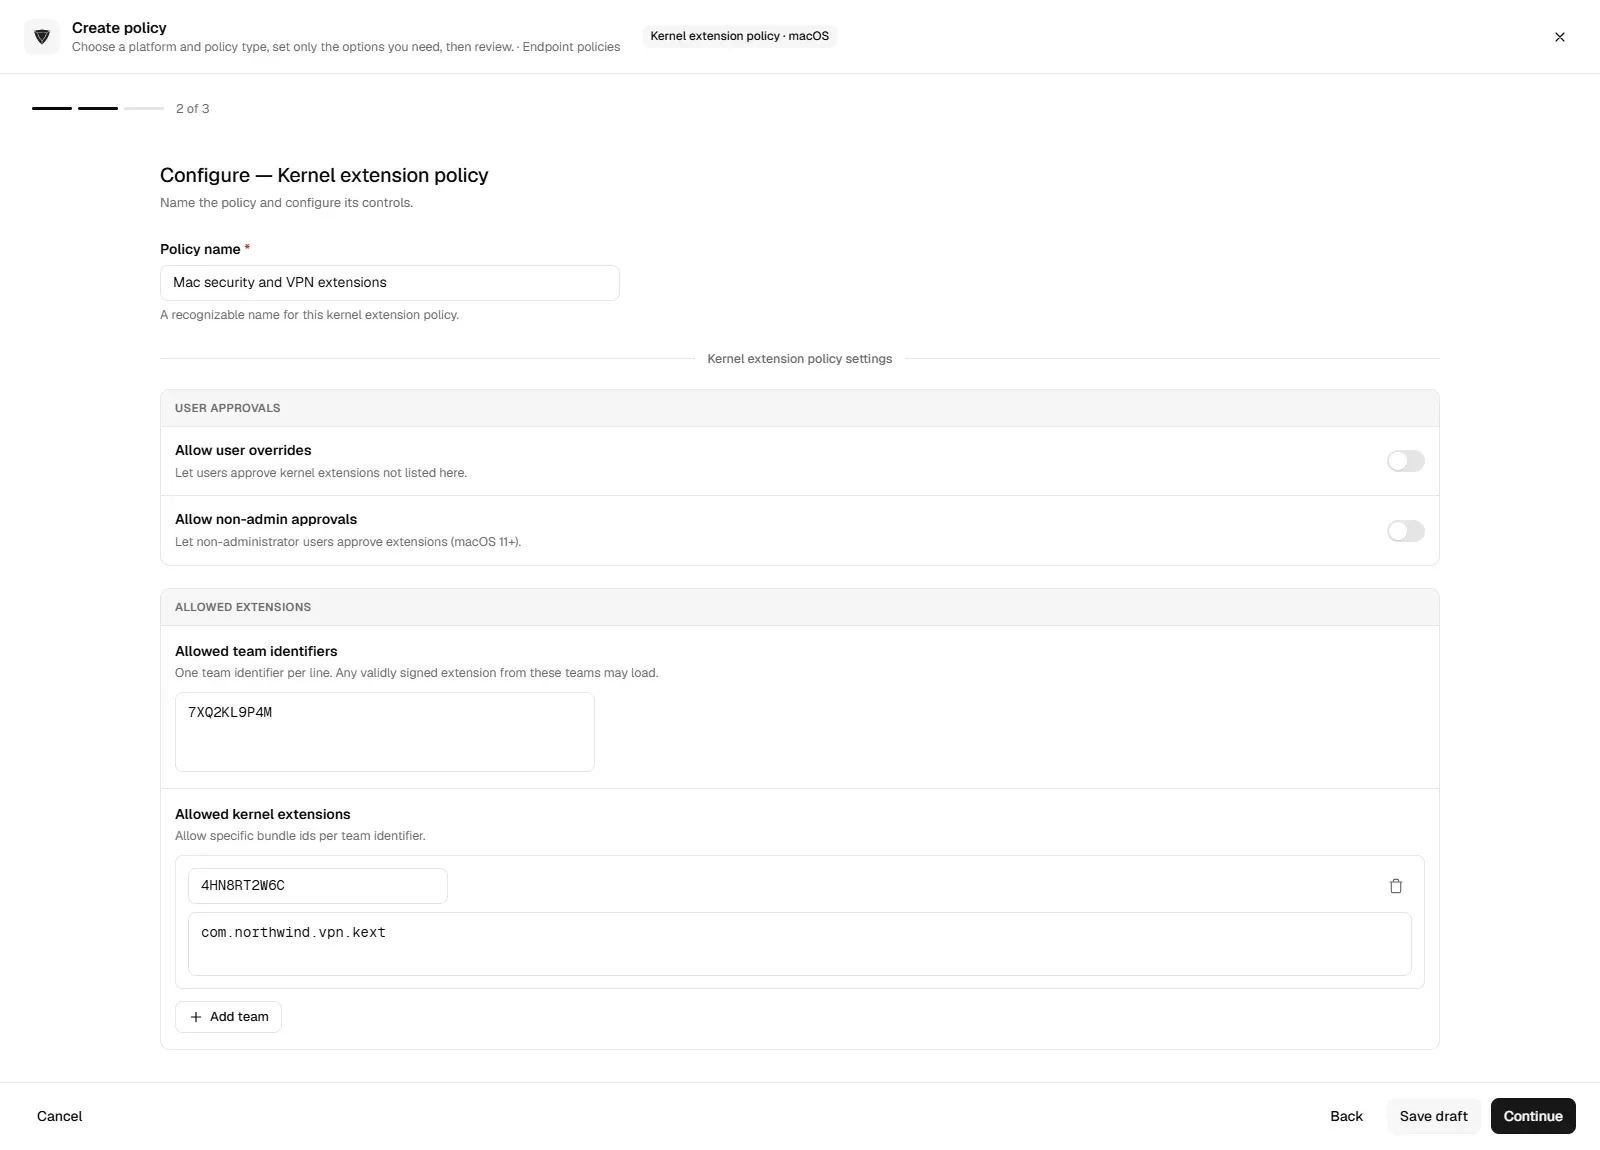
The policy can allow kexts in two ways:
It can also say whether users may approve kexts that are not on the list, and whether standard (non-administrator) users may approve them. Apple only accepts this policy from an MDM, on a Mac enrolled through Automated Device Enrollment or a user-approved enrollment.
Apple has moved developers to system extensions, which run in user space outside the kernel, so if one crashes the Mac keeps running. There are three kinds: network extensions (for VPNs, content filters and firewalls), endpoint security extensions (for antivirus and EDR tools), and driver extensions built with DriverKit (for hardware). Apple's deployment guide describes kernel extensions as no longer recommended for macOS, and on macOS 11 and later a kext that uses an API Apple has replaced with a system extension framework does not load at all.
| Kernel extension (kext) | System extension | |
|---|---|---|
| Where it runs | Inside the macOS kernel | In user space, outside the kernel |
| Effect of a crash | Can crash the whole Mac | Stops the extension; the Mac keeps running |
| Approval | Admin approval plus a restart; Reduced Security on Apple silicon | User approval in System Settings, no restart and no security change |
| Managed with | Kernel extension policy | System extension policy |
| Apple's status | No longer recommended | The recommended route |
Before you approve a kext, ask the vendor whether a current version uses a system extension instead. For the newer framework, see macOS system extensions.
Treat the policy as two things: a written rule for which kernel extensions your organization allows, and the MDM setting that enforces it.
kmutil showloaded to see loaded extensions, or check the vendor's documentation for the Team ID and bundle IDs.To find a Team ID, run codesign -dv --verbose=4 /Library/Extensions/Example.kext and read the TeamIdentifier line, or check System Information > Software > Extensions.
On a single Mac without an MDM policy, the user approves the extension by hand. The steps differ between Intel Macs and Macs with Apple silicon.
Reduced Security weakens some of the Mac's startup protections, so only do it on Macs that need the extension.
Third-party kernel extensions are installed in /Library/Extensions. Apple's own are in /System/Library/Extensions, which is protected and cannot be changed. On current macOS, a kext copied into the folder does not load by itself: it still needs approval and a restart, and macOS keeps approved third-party kexts in a separate collection that it rebuilds after each change.
System extensions are approved in a different place. When an app installs one, macOS asks the user to allow it in System Settings. On macOS 15 Sequoia and later, installed system extensions are listed in System Settings > General > Login Items & Extensions, grouped by type, such as Network Extensions and Endpoint Security Extensions; on earlier versions, the approval was in Privacy & Security. An MDM can approve system extensions in advance with a system extension policy, by Team ID, bundle ID and extension type, so users are not asked.
Many security tools also need privacy permissions such as Full Disk Access. Those are approved separately with a PPPC profile; see how to configure a privacy preferences profile.
"Modify system security policy" usually refers to the Startup Security Utility setting on Apple silicon described above. The security policy can only be changed in recoveryOS by an administrator, or, for Macs enrolled through Automated Device Enrollment, by the MDM itself.
Apple's deployment guide describes the MDM route: on a Mac enrolled through Automated Device Enrollment, the MDM can use the Mac's bootstrap token to set Reduced Security automatically when a kernel extension policy is applied, and then restart the Mac with the command that rebuilds its kernel cache. On a Mac enrolled another way, the MDM can only prompt the user to make the change in recoveryOS. Check that your MDM supports this and has the bootstrap token escrowed.
Older guides suggest sudo spctl --master-disable to turn off Gatekeeper. That changes which apps may open, not which kernel extensions may load, and it lowers security for every app, so do not use it to fix a kext problem.
There is no kernel extension policy on iPhone or iPad. iOS and iPadOS do not load third-party kernel extensions at all; only Apple's code runs in the kernel. Apps that need system-level functions use Apple's extension points instead, such as Network Extension for VPNs and content filters, and an MDM manages those through VPN, web content filter and DNS settings rather than a kext allowlist.
The iPhone and iPad rely on:
Together these mean the kind of kernel access a Mac kext has is not available to third parties on iOS.
Approving extensions on every Mac by hand means a support call for every install. trio.so sends kernel extension allowlists and system extension policies to managed Macs, by Team ID and bundle ID, so security and VPN tools load without asking users. See Apple device management.
Kernel extensions are on their way out on macOS, but many fleets still have one or two. Approve them with a narrow kernel extension policy from your MDM, deploy it before the software, handle the Apple silicon security step through the bootstrap token where your MDM supports it, and move each tool to a system extension as soon as the vendor offers one. On iPhone and iPad, there is nothing to approve: third-party kernel code does not run there.
Related reading: macOS system extensions, Mac MDM, privacy preferences profiles on macOS and best Apple MDM.
trio.so sends kernel and system extension policies to managed Macs, so security and VPN tools load without asking users.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Find your Mac administrator name, reset a forgotten admin password from Recovery or your Apple Account, and make a user an admin, with notes for IT.
Apple DEP is now Automated Device Enrollment in Apple Business. What it does, where to log in, what you need, and how zero-touch enrollment works.
Discover how to deploy and manage FileVault disk encryption on Mac using MDM. Learn how to enable, disable, and manage this built-in feature.
What Apple's Mac Evaluation Utility checks, how to download it through AppleSeed for IT, how to run it and read the report before a macOS upgrade.
What macOS system extensions are, how they differ from kernel extensions, the three types (DriverKit, network, endpoint security) and approval.
This article guides you through the essentials of macOS package distribution for your organization, including understanding distribution strategies.
Declarative device management is Apple's answer to MDM polling delays and unreliable compliance data — here's how it works and how to start using it.
A remote wipe on a Mac is only possible if the right tools are in place first — here is how MDM, Find My, and native macOS each handle device erasure.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients