



Explained
The Benefits of Integrating SCIM With MDM Software
This blog explores the benefits of integrating SCIM (System for Cross-domain Identity Management) Device Management solutions.
User provisioning and deprovisioning explained: joiner, mover and leaver steps, SCIM vs directory sync, and how to automate accounts from your directory.

Content writer, trio.so
User provisioning is the process of creating user accounts and giving people the access they need when they join, changing that access when they move roles, and removing it when they leave. The removal half is called deprovisioning. Done by hand, it means creating the same person in a dozen systems and hoping someone remembers to delete them later. Automated user provisioning does it from one source, usually your HR system or identity provider, using directory sync and the SCIM standard.
If you create and delete accounts by hand every time someone joins or leaves, this guide shows the joiner, mover and leaver steps, how SCIM and directory sync differ, and what to automate first.
User provisioning, often referred to as account provisioning, involves the creation, management, and deactivation of user accounts. It includes granting each user the right access to data and applications within an organisation. It is a core part of identity and access management: each person gets the access their job needs, and no more.
Provisioning covers three kinds of access:
Every account goes through the same three events. The table shows what should happen at each one.
| Event | Trigger | What happens |
|---|---|---|
| Joiner | New hire added in HR or the directory | Account created in the directory, added to groups for their role, accounts created in each connected app, device prepared |
| Mover | Role, team or location changes | Group memberships updated, access to the old role's apps removed, new apps added |
| Leaver | Leave date reached in HR or account disabled | Sign-in blocked, sessions ended, accounts deactivated in every app, licences reclaimed, device collected and wiped |
Movers are the step most companies get wrong. People collect access as they change roles and never lose the old access, which is how a long-serving employee ends up with rights to everything.
Deprovisioning is equally important as provisioning, yet it is often overlooked. It is the process of revoking access and recovering resources when an employee leaves the company or changes roles. The steps include:
Fast deprovisioning matters most for leavers who part on bad terms and for accounts in apps that are not connected to single sign-on, where blocking the directory account does not end access. For more, see deprovisioning in cybersecurity and the IT offboarding checklist.
Automated user provisioning uses software to create, update and remove accounts based on rules and a single source of truth. The most efficient setup for most companies:
The result is consistent access for every person in the same role, a new joiner who is ready on day one, and a leaver whose access ends everywhere when the HR record changes.
Both move users and groups from the identity provider into another system, but they work in opposite directions.
| SCIM provisioning | Directory sync | |
|---|---|---|
| Who starts it | The identity provider pushes changes to the app | The app pulls users and groups from the directory on a schedule |
| Speed | Near real time, as changes happen | At each sync run |
| Standard | SCIM 2.0, an open standard (RFC 7643 and 7644) | Each directory's own API |
| Typical use | Creating and deactivating accounts in SaaS apps | Keeping a full copy of users and groups for reporting and policy |
Many apps support both: SCIM for fast joins and leaves, directory sync for a full picture. For how to secure SCIM endpoints and tokens, see SCIM security.
Single sign-on (SSO) controls how a user signs in. SCIM controls whether the account exists at all. You need both: SSO without SCIM leaves accounts behind in apps after people leave, and SCIM without SSO still leaves people with separate passwords.
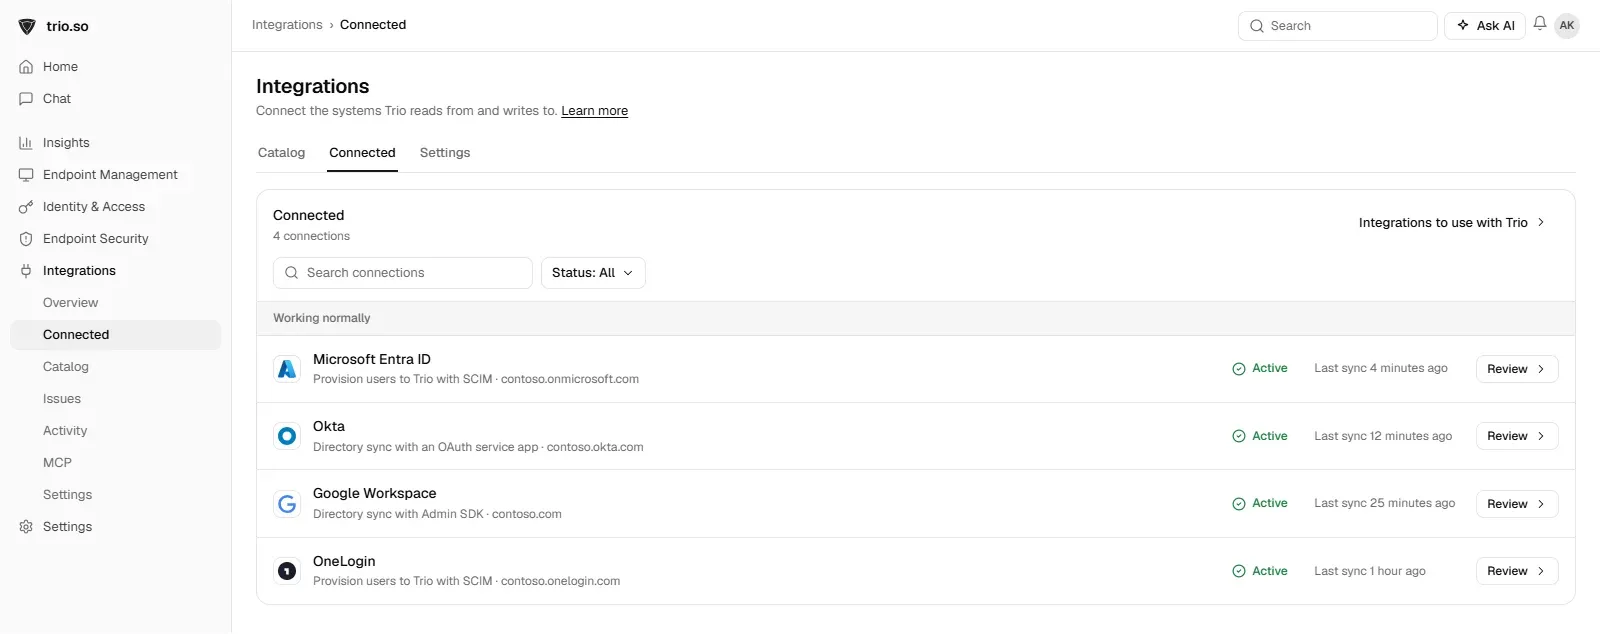
trio.so syncs users and groups from Google Workspace, Okta, Microsoft Entra ID, OneLogin, PingOne, BambooHR and JumpCloud, and accepts SCIM 2.0 provisioning from Entra ID, Okta and OneLogin. When a user is deprovisioned in the identity provider, they lose access, and their company devices can be wiped from the console. See single sign-on.
User provisioning is the process of creating user accounts and assigning access when people join, updating access when they change roles, and removing it when they leave.
Deprovisioning is the process of revoking access and recovering resources when an employee leaves the company or changes roles. It includes blocking sign-in, deactivating accounts, reclaiming licences and collecting and wiping devices.
SSO decides how a user signs in to an app. SCIM creates, updates and deactivates the user's account in that app. SSO alone does not remove accounts when people leave.
Automated user provisioning creates, changes and removes accounts automatically from a source of truth such as an HR system or identity provider, using rules, role groups, SCIM and directory sync.
Identity providers such as Microsoft Entra ID, Okta, OneLogin and Google Workspace provision users centrally to apps that support SCIM or directory sync. HR systems can feed the identity provider so accounts start and end with the employee record.
Related reading: SCIM security, identity management, deprovisioning in cybersecurity and the IT offboarding checklist.
trio.so syncs users from Google Workspace, Okta and Entra ID and takes SCIM 2.0 provisioning, so leavers lose access the day they leave.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
This blog explores the benefits of integrating SCIM (System for Cross-domain Identity Management) Device Management solutions.
Many organizations throughout different industries use LDAP. But how does LDAP work and what are its benefits for your organization?
What is identity and access management, and why does it matter? It’s your first line of defense against costly breaches and compliance failures.
Ten Microsoft Entra conditional access policy templates with what each does, the order to enable them in report-only mode, licensing, and a free download.
Looking to simplify machine identity management? This guide uncovers proven methods for credential rotation, monitoring, and unified policy enforcement.
Seven best practices for cloud identity and access management, from least privilege and MFA to permission reviews and access logs.
Discover expert insights on Directory Management, covering groups, active directory management, and more for IT professionals.
SCIM vs JIT user provisioning: how each method works, where they differ, and how to choose or combine them.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients