



How-Tos
How to Change MacBook Administrator Name with Ease
Learn how to change MacBook administrator name safely and easily. Follow our step-by-step guide and learn about an easy-to-use tool to simplify tasks.
Turn on two-factor authentication for your Apple Account on a Mac, and add MFA to the Mac login with Platform SSO, smart cards or an identity provider.

Content writer, trio.so
Two-factor authentication on a Mac usually means one of two things. For your Apple Account, turn it on in System Settings > [your name] > Sign-In & Security > Two-Factor Authentication; most Apple Accounts already have it. For logging in to the Mac itself, macOS has no built-in second factor at the login window, so companies add one with Platform Single Sign-on, smart cards or an identity provider's Mac login tool. Both are covered below.
If it already says On, you're done. Once it's on, signing in to your Apple Account on a new device asks for your password plus a six-digit code shown on one of your trusted devices or sent to your trusted phone number. Apple's own guide, Two-factor authentication for Apple Account, has the details.
For most accounts, no. Apple says that if an account was created with two-factor authentication, the extra protection can't be removed. If you turned it on yourself recently, Apple lets you go back within two weeks of enrolling.
Two-factor authentication relies on your trusted devices. Add an account recovery contact, or a recovery key, in Sign-In & Security so you can still get in if you lose them.
The Mac login window checks a local or network password. It does not ask for a second factor on its own. Companies that want MFA at the Mac login use one of these.
Platform SSO, part of macOS since macOS Ventura and expanded in macOS Sonoma, links the Mac's local account to the company's identity provider. Depending on how the identity provider sets it up, the user can sign in with their work password, with a hardware-bound key in the Secure Enclave, or with a smart card, and they get single sign-on to work apps afterwards. Apple describes it in its Platform Deployment guide. Microsoft Entra ID, Okta and other identity providers support it through their own apps, configured by the MDM.
macOS supports PIV-compatible smart cards and security keys for login. The user inserts the card and enters its PIN, which is two factors: something you have and something you know. It suits government and high-security environments that already issue cards.
Some identity providers ship a Mac login extension that replaces or wraps the login window and asks for the provider's MFA (push, code or key). Check the vendor's current macOS support before you roll it out, and always keep a tested way back in, such as a separate admin account or a recovery process, in case the second factor is unavailable.
| You want | Use |
|---|---|
| To protect a personal Apple Account | Apple Account two-factor authentication |
| Company login with work credentials and SSO to apps | Platform SSO with your identity provider |
| Hardware-based login in a high-security environment | Smart cards (PIV) |
| A specific push or code prompt at login | Your identity provider's Mac login tool, if it supports your macOS version |
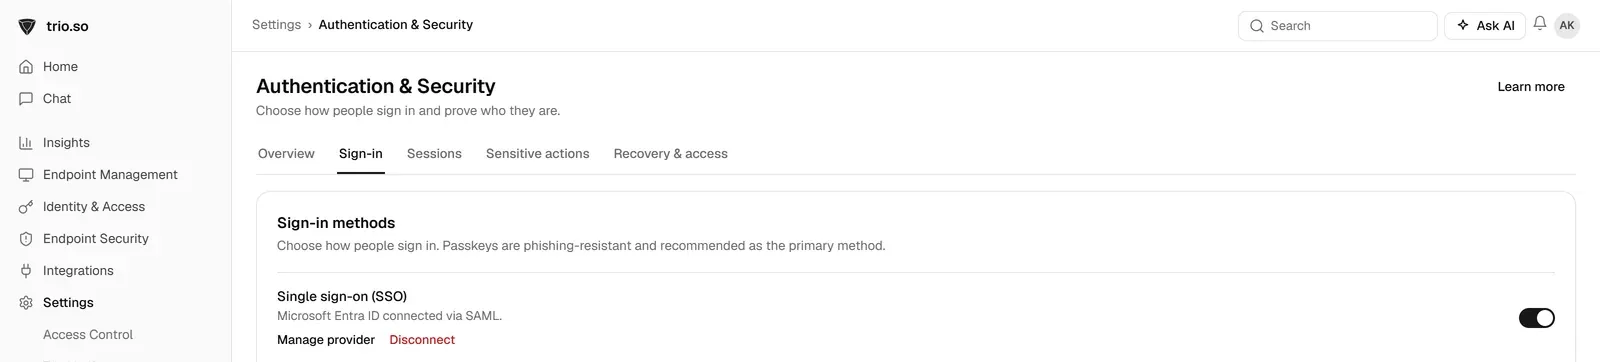
MFA at the login window is set up between the Mac and your identity provider. trio.so supports single sign on and Microsoft Entra ID for your users, so the same work identity covers the devices you manage. See single sign on.
Related reading: how to add a Mac to Active Directory and Mac administrator account.
trio.so supports single sign on and Microsoft Entra ID for your users.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Learn how to change MacBook administrator name safely and easily. Follow our step-by-step guide and learn about an easy-to-use tool to simplify tasks.
How account-driven User Enrollment works on iPhone, iPad and Mac: setup with Managed Apple Accounts, what IT can and cannot see, Intune steps and fixes.

Where the FileVault recovery key is stored, how to find it, and how IT admins escrow keys with MDM.

Change the user name on a Mac and rename the home folder in Apple's order, what can break afterwards, and how to roll back. Works on current macOS.

What a standard user can and cannot install on a Mac, and three ways to let them install software without making everyone an admin.
How to open System Preferences on a Mac? These are step-by-step methods to quickly access and navigate macOS settings like a pro.

How to set up a Privacy Preferences (PPPC) profile on macOS: what it can approve or only deny, the payload keys, MDM delivery, and the Mac settings.
What XProtect does on a Mac, whether it runs by itself, how to check its version and last update, and where it stops, with a fleet check for IT teams.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients