



Explained
Defense in Depth: 5 Layers of Security and How to Apply Them
What defense in depth means, the five layers from perimeter to people, how it differs from layered security, and how to apply it in a small IT team.
What unauthorized access to a computer system is, the seven ways attackers get in, how to spot it, and a checklist to prevent it on devices and accounts.

Content writer, trio.so
Unauthorized access is when someone gets into a computer, network, application or data without permission, either by breaking in from outside or by using access they were never meant to have. Attackers usually get in one of seven ways: phishing, weak or stolen passwords, malware, unpatched vulnerabilities, social engineering, misconfigured access controls and insiders. Stolen credentials and exploited vulnerabilities were the two most common ways into breached organizations in Verizon's 2025 Data Breach Investigations Report. Most of it is stopped by the same short list: multi-factor authentication, prompt patching, least-privilege access, encrypted devices and someone watching the sign-in logs.
If you met the term in a policy, an audit finding or after an incident and want to know what it means in practice, the seven ways below each end with how to stop them, and the checklist near the end pulls it together.
NIST defines it as a situation where "a person gains logical or physical access without permission to a network, system, application, data, or other resource". Logical access means signing in or connecting; physical access means touching the device, the server room or the cable. A shorter definition used in US government guidance is "any access that violates the stated security policy", which also covers employees who open data their role does not allow.
Unauthorized access is also a crime in most countries, for example under the US Computer Fraud and Abuse Act and the UK Computer Misuse Act. For your own organization, it usually triggers incident response and, if personal data was reached, breach notification duties. This is not legal advice; check the rules that apply to you.
Common examples:
Phishing emails, texts (smishing) and calls trick people into entering their password on a fake sign-in page, approving a sign-in prompt, or opening a malicious attachment. Verizon's 2025 report puts phishing at 16% of breaches as the first step, and many credential-abuse breaches start with a phish too. Variants include pharming, which sends people to a fake website even when they type the right address.
How to stop it: turn on multi-factor authentication, preferably phishing-resistant methods such as passkeys or security keys for admins; filter email; and make it easy for staff to report a suspicious message quickly.
Credential abuse was the most common way in for the breaches Verizon analyzed in 2025, at 22%. Attackers reuse passwords leaked from other sites (credential stuffing), try common passwords across many accounts (password spraying), or guess at one account until it gives way (brute force). One reused password can open email, VPN and cloud apps at once.
How to stop it: require MFA on every account that supports it, starting with email, remote access and admins; use a password manager so every password is unique; lock out or slow down repeated failed sign-ins; and remove accounts nobody uses. See two-factor authentication on a Mac for one example.
Malware gives attackers a foothold on a device: keyloggers capture passwords, remote access trojans open a back door, and information stealers copy saved browser passwords and session cookies, which can let an attacker skip MFA altogether. It arrives through attachments, malicious downloads, fake software updates and infected USB drives.
How to stop it: run endpoint protection on every computer, keep browsers and apps updated, make everyday users standard users so malware cannot install itself system-wide, and block USB storage where it is not needed; see how to disable USB ports.
An unpatched flaw lets an attacker run code or bypass sign-in without needing a password at all. Exploitation of vulnerabilities was the way in for 20% of breaches in Verizon's 2025 report, up 34% on the year before, with VPNs, firewalls and other internet-facing edge devices a growing share of the targets. CISA keeps a public list of vulnerabilities known to be exploited, the KEV catalog, for exactly this reason.
How to stop it: keep an inventory of what you run, patch operating systems and third-party apps promptly, and patch anything on the KEV list or facing the internet first. See vulnerability management and patch management.
Social engineering targets people rather than systems: a caller pretending to be IT who asks a user to read out a code, a fake supplier who asks the help desk to reset an account, or someone who follows staff through a secure door. Shoulder surfing, watching someone type a password in a café or on a train, is the low-tech version.
How to stop it: give the help desk a verification process for password and MFA resets, never share sign-in codes, use privacy screens and screen locks in public, and make it normal to question unexpected requests.
Default admin passwords, cloud storage shared with "anyone with the link", remote desktop open to the internet, and accounts with far more rights than they need all give attackers an easy way in, or let a small intrusion become a large one. Most are not attacks at all until someone finds them.
How to stop it: change default credentials, close services that do not need to face the internet, review sharing settings, and give each account only the access its job needs. Excessive permissions explains how access builds up and how to remove it, and the least privilege access model describes the approach.
Not every case of unauthorized access comes from outside. An employee may copy customer data before leaving, look up records out of curiosity, or make a mistake that exposes data, and a departed employee's account may still work. Insiders already have some access, so the risk is how far beyond their role they can go.
How to stop it: remove access on the day someone leaves, review access regularly, log access to sensitive data and alert on unusual activity, and use data loss prevention for the data that matters most.
Most intrusions leave traces in sign-in and security logs before any damage is done. Look for:
Collect these logs in one place and decide who reviews alerts. If you find signs of unauthorized access, reset the affected credentials, revoke sessions, isolate the device if needed and follow your incident response plan.
| Way in | Main defenses |
|---|---|
| Phishing | MFA, phishing-resistant methods for admins, email filtering, quick reporting |
| Weak or stolen passwords | MFA, password manager, lockout of repeated failures, removal of unused accounts |
| Malware | Endpoint protection, updates, standard user accounts, USB storage control |
| Vulnerabilities | Inventory, prompt patching, KEV and internet-facing systems first |
| Social engineering | Verified reset process, never share codes, screen locks |
| Misconfigured access | No default passwords, closed unneeded services, least privilege |
| Insiders | Same-day offboarding, regular access reviews, logging, data loss prevention |
And for every device that holds company data:
For the wider picture across networks, servers and cloud services, see IT infrastructure security.
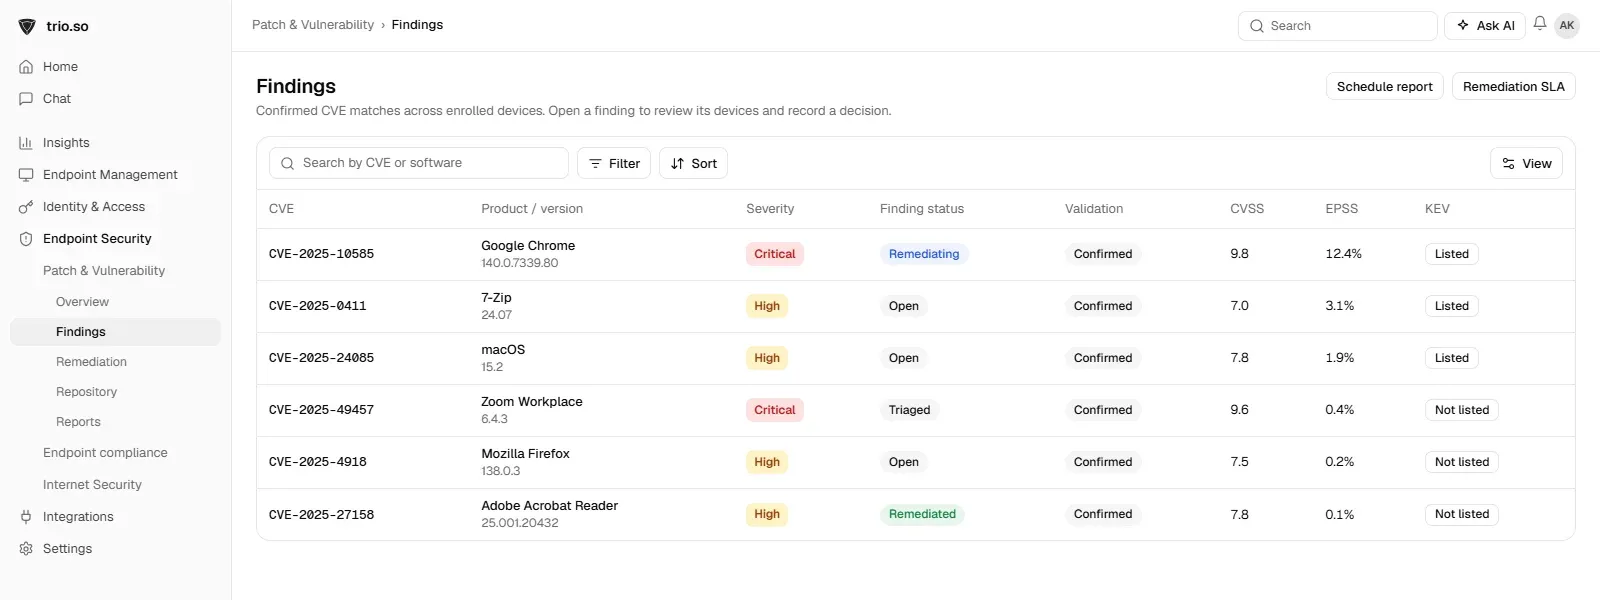
Several of the seven ways in are closed on the devices themselves. trio.so patches operating systems and third-party apps with the CVE severity of each finding, shows which devices are encrypted, and limits access to its own console with multi-factor authentication at sign-in and built-in and custom roles for IT staff.
Most unauthorized access comes through stolen passwords, missing patches and access nobody removed. Turn on MFA, patch what attackers are exploiting, give people only the access they need, encrypt devices, and watch the sign-in logs, and most of the seven ways in are closed.
trio.so patches devices with CVE severity for each finding, shows which are encrypted, and limits console access with roles and MFA.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
What defense in depth means, the five layers from perimeter to people, how it differs from layered security, and how to apply it in a small IT team.
Learn how to prevent pharming attacks with these 7 effective strategies. Safeguard your data and protect against sophisticated cyber threats.
Protect your organization from remote code execution (RCE) attacks with these 5 best practices.
Learn about the indicator lifecycle in cybersecurity and enhance threat detection, streamline incident response, and strengthen security.
Learn how to detect a cyber security breach effectively with tips, detection methods, and best practices for IT professionals.
Four verified IT security quotes from Richard Clarke, Kevin Mitnick, Bruce Schneier and Ginni Rometty, with sources and one practical step for your team from each.
We'll explore cybersecurity tabletop exercises, their significance in today's threat landscape, & how to leverage them to bolster your cyber resilience.
Read this blog on how to prevent DNS cache poisoning attacks with best practices and tools. Learn strategies for IT professionals to secure DNS systems.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients