



Templates
Effective Social Media Usage Policy Template (Free Download)
We'll explore what a social media usage policy template is, what it should include, and how it can benefit your organization.
Free data loss prevention (DLP) policy template in Word and PDF, with an Excel tracker: 17 sections, starter DLP rules, a handling matrix and examples.

Content writer, trio.so
A data loss prevention (DLP) policy says which data needs protecting, how each kind may be stored and shared, which channels are allowed, what your DLP tools check, and what happens when data gets out. This free template gives you that policy as an editable Word document with 17 sections, written for a company of 50 to 1,000 people.
Every decision sits in [brackets], with a default you can keep or change. The download also includes a PDF guide with worked examples and an Excel tracker for your data inventory, DLP rules, incidents with a notification clock, exceptions, device controls and training, mapped to NIST SP 800-53, ISO/IEC 27001, CIS Controls, PCI DSS and GDPR.
In short
A data loss prevention policy, or DLP policy, is a document approved by management that sets the rules for keeping sensitive data inside the company. It names the data that matters, gives each data set an owner and a class, lists the approved ways to store and share it, sets the endpoint controls, and says what the DLP tools do when a rule matches. The tool settings and rule details change often, so they live in runbooks and in the tracker.
Data leakage and data loss are close but not the same: leakage is data reaching someone who should not have it, while loss also covers data you can no longer reach, such as a lost laptop. That is why some teams call it a data leakage prevention policy. This template covers both.
"DLP policies" can also mean the individual rules inside a DLP tool, such as "block emails with card numbers to outside addresses". The policy document sets the rules for those rules: who owns them, how they go live and how false positives are handled. Appendix B of the template gives you nine starter rules.
The template has 17 sections in four parts: setting the rules, knowing your data, controlling each channel, and watching and responding.
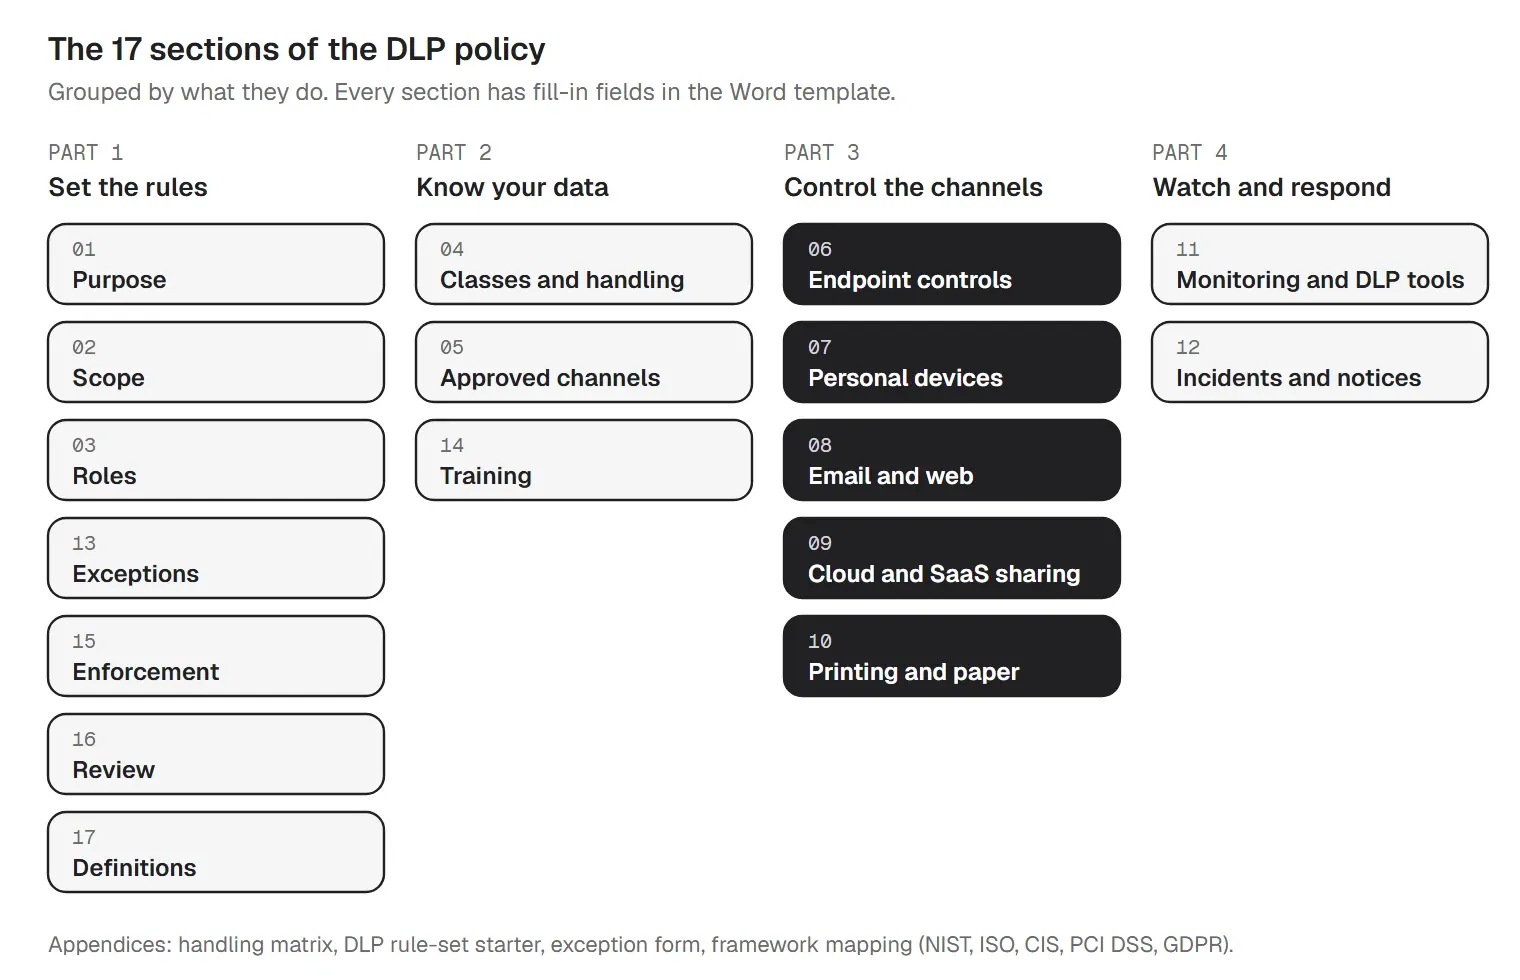
Appendices add a classification and handling matrix, a DLP rule-set starter, an exception request form and a framework mapping table.
Most data leaves through ordinary channels: an attachment to the wrong address, a sharing link set to "anyone", a file copied to a USB drive, a lost laptop. No single tool covers all of them. Content inspection, the part that recognises a card number in an email or a spreadsheet of customer data in a shared folder, needs a DLP tool or the DLP features in your email and cloud suite. Both Microsoft Purview and Google Workspace include DLP rules in some plans, so check your licence before you buy a separate product.
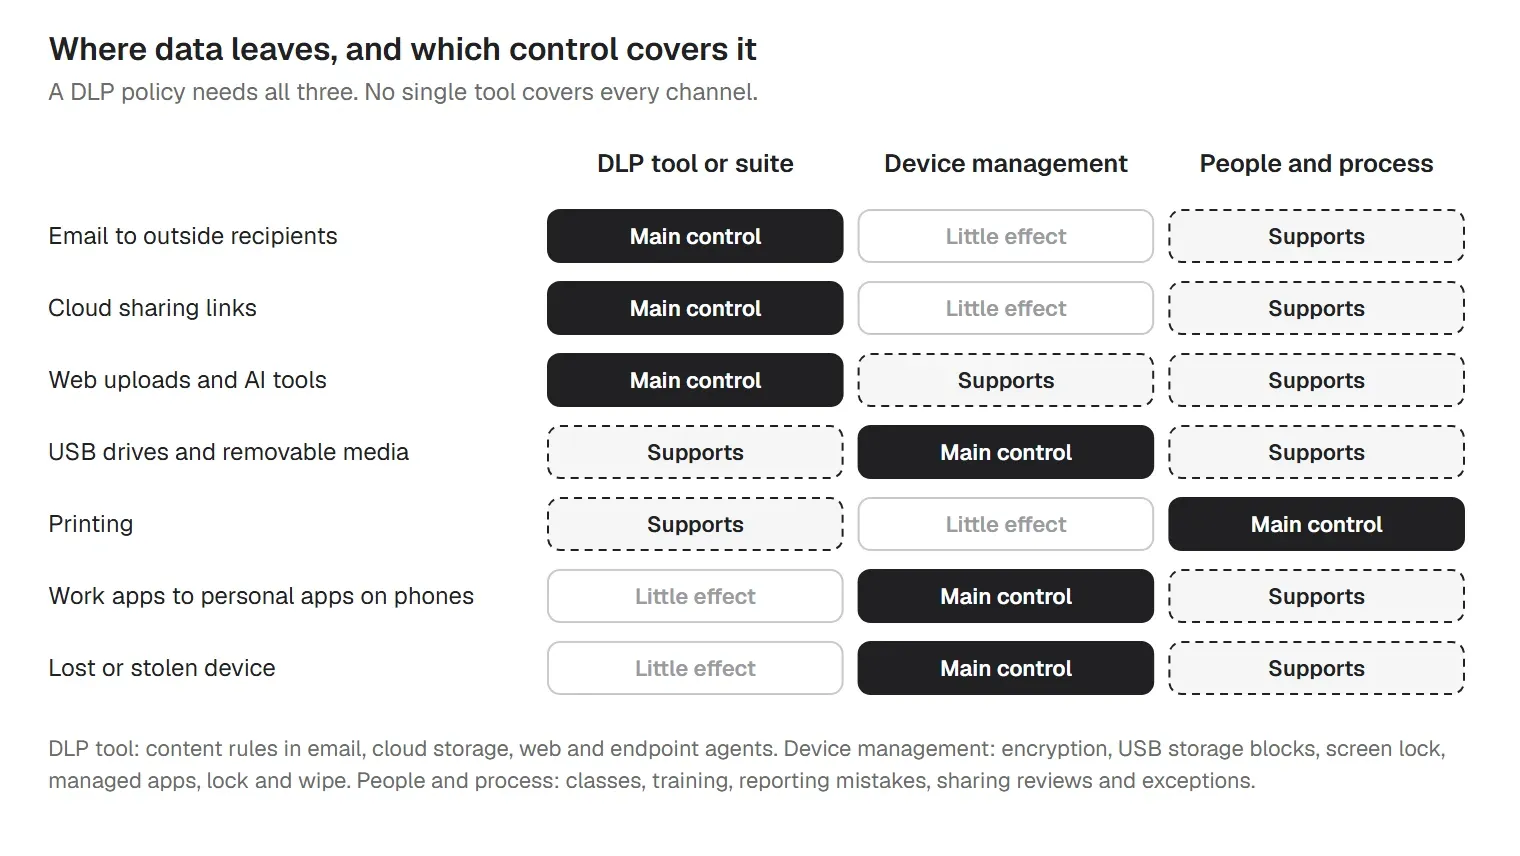
Device management covers the endpoint: disk encryption, USB storage blocks, screen lock, managed apps on phones, and lock or wipe when a device goes missing. People and process cover the rest, such as printing, sharing reviews and reporting a misdirected email at once. If you don't have a DLP tool yet, do sections 4 to 10 first and add content rules when a tool is in place.
Four classes are enough for most companies: Restricted (card numbers, national IDs, health records, keys, core source code), Confidential (personal data, contracts, customer lists), Internal and Public. Every data set gets an owner and one class, and a file with mixed data takes the highest class.
The class only matters if it changes what people may do. Appendix A of the template turns the classes into a handling matrix. Here are five of its ten rows:
| Action | Restricted | Confidential | Internal | Public |
|---|---|---|---|---|
| Email outside the company | Not allowed, except encrypted email to recipients the data owner approves | Encrypted email or a secure link to named people | Allowed for a business need | Allowed |
| Sharing from cloud storage outside the company | Named people only, with data owner approval, expiring in [30] days | Named people only, expiring in [90] days | Named people only | Allowed, including public links |
| USB drives and other removable media | Not allowed | Company encrypted drives only, with approval | Company encrypted drives only | Allowed |
| Personal devices | Not allowed | Managed apps only, no local copies | Managed apps or the browser | Allowed |
| AI tools and chatbots | Not allowed | Approved company AI tools only | Approved company AI tools only | Allowed |
Record each Restricted and Confidential data set in the tracker's Data inventory tab, with the systems it lives in and the DLP rules that protect it. The Dashboard counts the sensitive data sets that have no rule yet.
A DLP rule pairs a detector (a pattern, keyword list, sensitivity label or document fingerprint) with a channel and an action. Turning every rule on in Block mode on day one stops real work and teaches people to work around the tool. Microsoft's own guidance is to run new policies in simulation mode first and use policy tips to warn users before moving to more restrictive modes. The template uses three vendor-neutral modes:
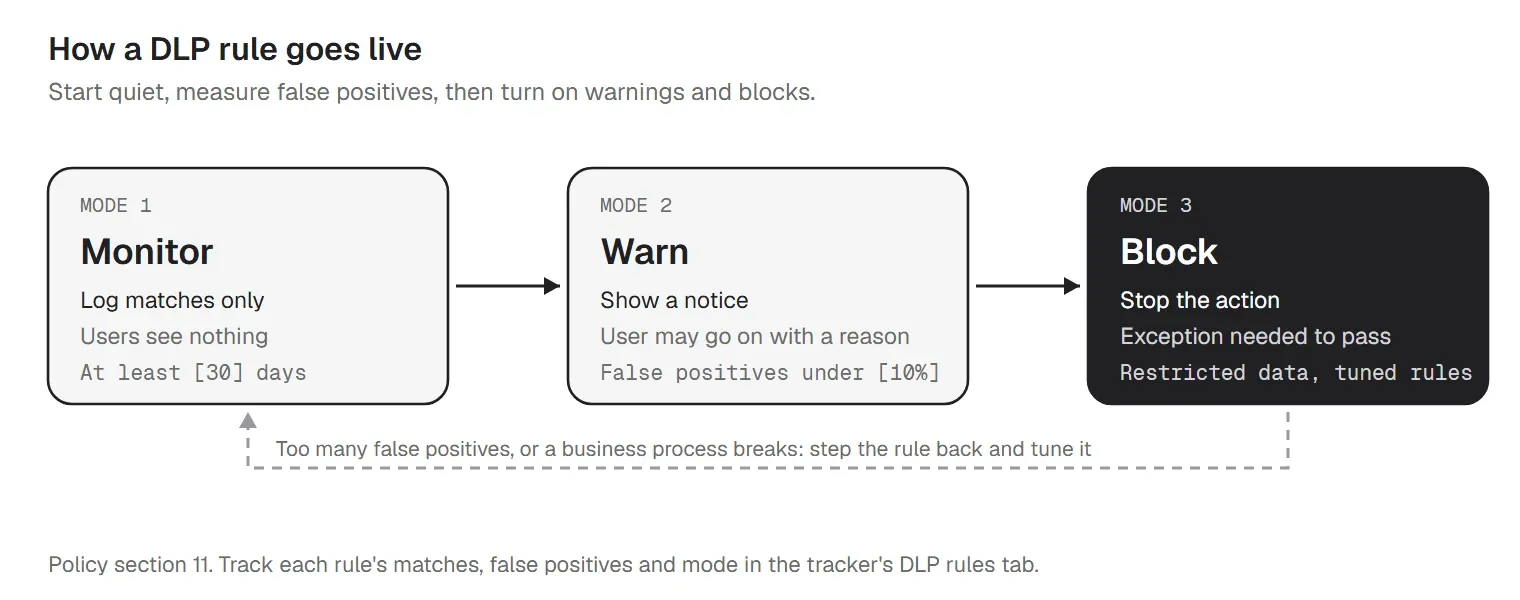
False positives decide when a rule moves up. Review new matches every week, record matches and false positives per rule, and tune (add nearby keywords, raise the count, exclude test data). A rule moves up only when its false-positive rate stays below [10%] for two reviews. The tracker's DLP rules tab calculates the rate and flags each rule as Tuning, Ready to move up, At target or Too noisy.
These are the nine starter rules in Appendix B:
| ID | Data type | Detector | Start | Target |
|---|---|---|---|---|
| DLP-01 | Payment card numbers | 13 to 19 digits that pass the Luhn check, near words such as card, Visa or expiry | Monitor | Block |
| DLP-02 | National ID numbers | The format and checksum for each country you work in, for example US Social Security or UK National Insurance numbers, near ID words | Monitor | Block at [5] or more in one item; Warn below |
| DLP-03 | Bank account numbers | IBANs with a valid checksum; account and routing numbers near bank words | Monitor | Warn |
| DLP-04 | Health data | Medical record numbers, or diagnosis and drug terms next to a name or ID | Monitor | Block |
| DLP-05 | Passwords, keys and tokens | Private key headers, cloud access key formats, connection strings that contain a password | Warn | Block |
| DLP-06 | Source code | Code file types and repository exports; fingerprints of your main repositories | Monitor | Warn |
| DLP-07 | Customer lists | Files or messages with [100] or more email addresses or customer IDs | Monitor | Warn |
| DLP-08 | Restricted documents | Restricted sensitivity label | Warn | Block |
| DLP-09 | Confidential documents | Confidential sensitivity label | Monitor | Warn |
Tell staff that DLP checks company email, files and devices, limit who can read alert content, and check local law and any works council agreements before you monitor.
A clause that says "sensitive data must be protected" gives an auditor nothing to test. Each clause should name the data, the channel, the action and a number. Six from the template:
Two worked examples show how the policy plays out. In the first, a sales rep leaves a company laptop on a train and reports it within the hour. The device inventory shows BitLocker and screen lock on. IT sends a remote wipe and logs a High incident, and the privacy lead records it as a personal data breach that is unlikely to result in a risk, because the data was encrypted. The EDPB's breach examples include a similar case: stolen encrypted tablets, no notification needed, but the breach is still documented. With encryption off, the same laptop could mean notifying the regulator within 72 hours and telling every customer on it.
In the second, a spreadsheet with 300 customer email addresses goes to the wrong outside address. Rule DLP-07 is still in Monitor mode, so it only logs the match. The sender reports it, the recipient confirms deletion in writing, and the incident is logged as Medium. The review moves DLP-07 to Warn, so the next sender sees a notice before the email goes.
Section 12 of the template sets the response: contain (remove the link, recall the message, disable the account, lock or wipe the device), assess (what data, which class, how many people, was it encrypted), grade the severity and log it. If personal data is involved, the privacy lead takes over the notification decision at once.
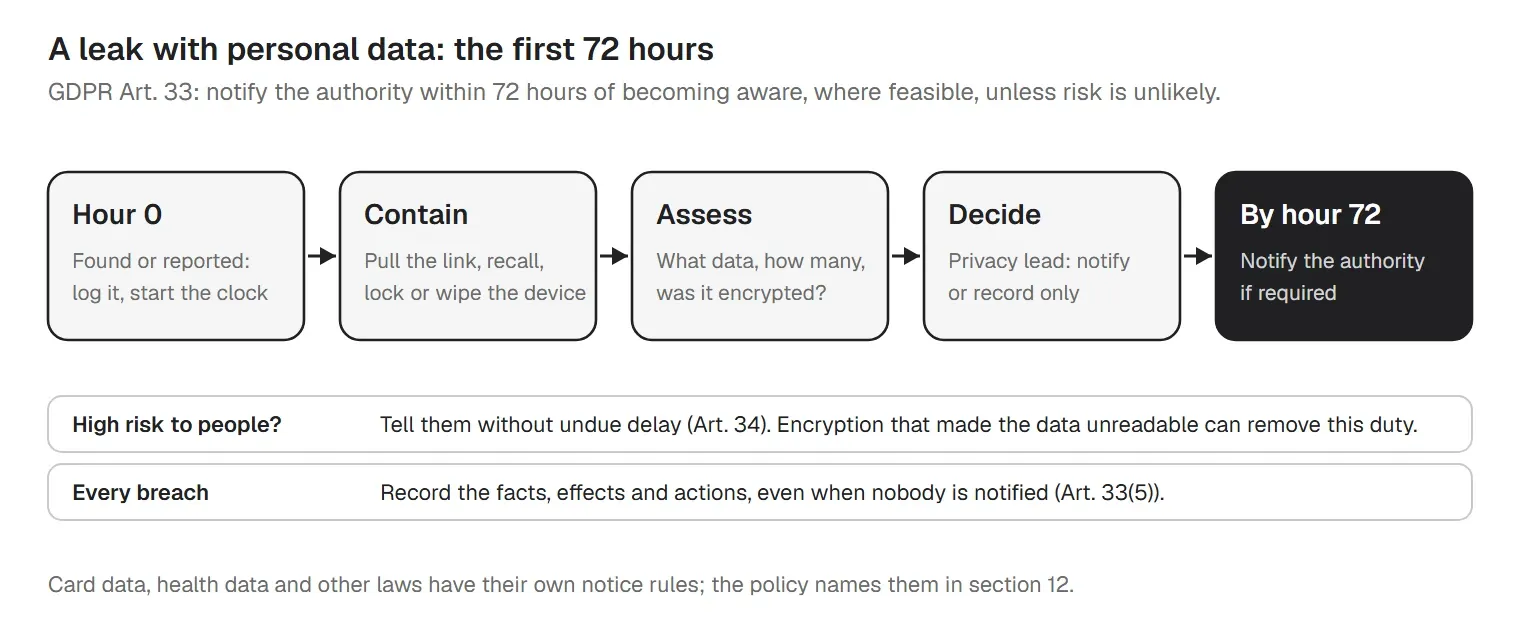
Under GDPR Art. 33, the supervisory authority must be notified without undue delay and, where feasible, within 72 hours of becoming aware of a personal data breach, unless it is unlikely to result in a risk to people. Art. 34 requires telling the people affected when the risk to them is high, unless measures such as encryption made the data unintelligible. Every breach is recorded, notified or not. Card data, health data and other laws have their own notice rules; the template leaves them in brackets for you to fill in. The tracker's Incidents tab calculates the deadline from the time you became aware and shows the hours left.
A small team can get from nothing to working DLP in about a quarter if it goes in this order:
If you also need a policy for the cloud services your data sits in, our cloud security policy template covers vendor approval, identity and logging. For a wider look at DLP strategy on mobile devices, see data loss prevention with MDM.
Each section of the template maps to five frameworks by ID, so you can show an auditor where a control lives in your policy:
| Section | NIST SP 800-53 | ISO 27001 Annex A | CIS v8.1 | PCI DSS | GDPR |
|---|---|---|---|---|---|
| 1. Purpose | PL-1, MP-1 | 5.1, 8.12 | 3.1 | 12.1 | Art. 32 |
| 2. Scope | CM-8, RA-2 | 5.9, 5.12 | 1.1, 2.1, 3.2 | 12.5 | Art. 32 |
| 3. Roles and responsibilities | PM-2, AC-6 | 5.2 | 3.1, 6.8 | 12.4 | Not mapped |
| 4. Data classification and handling | RA-2, MP-3, SI-12 | 5.12, 5.13 | 3.4, 3.7 | 3.2 | Art. 32 |
| 5. Approved channels and storage | AC-3, AC-4, AC-21 | 5.10, 5.14 | 3.3, 3.12 | 3.4, 4.2 | Art. 32 |
| 6. Endpoint controls | AC-11, AC-19, AC-19(5), CM-8, MP-7, SC-28 | 7.7, 7.10, 8.1, 8.12 | 1.1, 2.1, 3.6, 3.9, 4.3, 4.10, 4.11, 10.3 | 3.5, 9.4 | Art. 32 |
| 7. Personal devices and remote work | AC-17, AC-19, AC-20, AC-20(2) | 6.7, 8.1 | 3.3 | 12.2 | Art. 32 |
| 8. Email and web | AC-4, SC-7(10), SC-8, SI-4(4) | 5.14, 8.12 | 3.10, 3.13 | 4.2 | Art. 32 |
| 9. Cloud and SaaS sharing | AC-3, AC-21, AC-22 | 5.14, 5.23, 8.12 | 3.3, 3.13 | 3.4 | Art. 32 |
| 10. Printing and physical copies | MP-2, MP-4, MP-5, MP-6 | 7.7, 7.10, 7.14 | 3.5 | 9.4 | Art. 32 |
| 11. Monitoring and DLP tooling | SI-4, SI-4(4), SC-7(10), AU-2, AU-6, AU-12 | 8.12, 8.15, 8.16 | 3.13, 3.14, 8.2 | 10.2 | Art. 32 |
| 12. Incident handling and breach notification | IR-4, IR-6, IR-8, IR-9 | 5.24, 5.25, 5.26, 5.28 | 17.2, 17.4 | 12.10 | Art. 33, 34 |
| 13. Exceptions | CA-5, PM-9 | Clause 6.1.3 | Not mapped | Not mapped | Not mapped |
| 14. Training and awareness | AT-2, AT-2(2), AT-3, PL-4, PS-6 | 6.3, 5.10 | 14.1, 14.4, 14.5 | 12.6 | Art. 32 |
| 15. Enforcement | PS-8 | 6.4 | Not mapped | Not mapped | Not mapped |
| 16. Review | PL-1, CA-7 | 5.35, 5.36 | 3.1 | 12.1 | Art. 32 |
The IDs point to the source documents; check the current official text before you rely on a mapping. For framework checklists, see our ISO 27001 checklist and GDPR compliance checklist.
When an auditor or a customer asks how you prevent data leakage, expect to show:
The Excel tracker keeps all of this in one file, and its Dashboard counts what's missing: sensitive data sets with no rule, rules too noisy to keep, notices overdue, device controls below target and expired exceptions.
trio.so is not a DLP tool. It doesn't inspect files or messages, classify your data, block uploads or watch data moving through email, web and cloud apps. A DLP policy needs a DLP tool for that, or the DLP features in your email and cloud suite. trio.so handles the endpoint controls around it, and if you run Forcepoint DLP, it puts Forcepoint's incidents on the device record.
It is device management for Windows, macOS, iOS and Android, from one console. For a DLP policy, it covers:
Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed October 2026. Framework names and control IDs identify their publishers' documents; descriptions are our own summaries. trio.so is not affiliated with or endorsed by NIST, ISO, IEC, CIS, PCI SSC, the European Union, Microsoft, Google or Forcepoint. This article is guidance, not legal advice. The bracketed defaults are our recommendation, not a requirement of any framework.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
We'll explore what a social media usage policy template is, what it should include, and how it can benefit your organization.
Learn how to create a Mobile Application Security Policy Template to safeguard your organization's mobile apps with secure development practices.
This blog post provides a guide to creating an Access Control Policy Template to help organizations secure resources and manage access.
Create an effective Service Level Agreement (SLA) template to ensure a clear and mutually beneficial service relationship between providers and clients.
Free IT governance policy template in Word and PDF, with an Excel tracker: 17 sections, a RACI, decision rights, KPIs and a framework example.
Free Wi-Fi policy template in Word and PDF, with an Excel tracker: 17 sections on SSIDs, WPA3, guest terms of use, BYOD and rogue AP checks.
Given the cyberthreats organizations face today, it’s wise to implement an antivirus policy template. Read on to learn more about what it contains.
A free compliance checklist template for IT teams: ten areas with owners, status and evidence, plus an Excel workbook, framework crosswalk and Word guide.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients