

Templates
NIST 800-171 Compliance Checklist: 110 Requirements and SPRS
A NIST 800-171 compliance checklist with all 110 Rev. 2 requirements, their SPRS points, Rev. 3 changes, CMMC status and a self-assessment guide. Free Excel.
Read this blog to download our free GLBA compliance checklist and get started on protecting customer data and meeting regulatory standards effortlessly.
Content writer, trio.so
The Gramm-Leach-Bliley Act (GLBA), also known as the Leach-Bliley Act, mandates stringent data protection standards for organizations offering financial products or services. Complying with the GLBA isn’t merely a legal necessity; it’s an essential part of risk management for financial institutions. Achieving GLBA compliance ensures the security of nonpublic personal information (NPI), protecting sensitive data like Social Security numbers, financial account details, and other critical customer information. By following a well-structured GLBA compliance checklist, IT teams can streamline their efforts to protect customer data and avoid potential penalties. Moreover, ensuring GLBA compliance goes beyond preventing data breaches; it builds customer trust and demonstrates an organization’s commitment to data protection. With cyber threats constantly evolving, this checklist serves as a vital tool in maintaining compliance and fortifying data security. For related insights, explore our resources on IT compliance.
Before beginning the compliance journey, understanding the three main components of the GLBA—the Financial Privacy Rule, the Safeguards Rule, and the Pretexting Provisions—is vital. There are various types of compliances that organizations must address under the GLBA, including privacy, security, and fraud prevention. These categories ensure comprehensive protection of nonpublic personal information (NPI).
The Pretexting Provisions further underline the need to prevent unauthorized access to NPI. By incorporating policies to counter social engineering attacks, IT teams can protect customer data effectively. Regular training for employees on these provisions can significantly reduce risks. For additional guidance, check out our article on compliance training best practices. 
A strong GLBA risk assessment is the foundation of compliance. It identifies vulnerabilities, evaluates potential threats, and helps establish a solid foundation for risk management. Start by analyzing all data flows and access points within your organization’s network. Assess the risk levels associated with NPI and document these risks in detail. This process not only ensures the security of sensitive data but also helps prioritize critical areas that require immediate attention. Regularly updating risk assessments ensures the organization adapts to emerging threats. IT teams should also involve third-party service providers to ensure the security of outsourced processes. For instance, reviewing vendor agreements and monitoring their compliance efforts can prevent gaps in data protection. Organizations can benefit from compliance automation tools to streamline these assessments and ensure no critical area is overlooked. Automation reduces manual errors, enhances accuracy, and saves valuable time.
No data security strategy is complete without a well-defined incident response plan. In the current cyberthreat landscape, it’s crucial to have procedures ready to address potential data breaches. Develop a step-by-step guide detailing how to identify, report, and mitigate data breaches. Include roles and responsibilities for each team member involved in the process. This plan should be tested periodically to confirm its effectiveness during real-life incidents. Practice drills can help teams stay prepared for any eventuality. Integrating detection technologies such as intrusion prevention systems and ensuring timely reporting of breaches will help protect customer data and comply with the GLBA. Automated alerts can further enhance your organization’s response time, minimizing potential damage. For additional tools, consider implementing compliance monitoring software.
Using a GLBA compliance audit checklist simplifies the compliance process by providing IT teams with a structured approach. This checklist should cover key areas such as:
By addressing these compliance requirements systematically, organizations can avoid common pitfalls and achieve GLBA compliance more efficiently. Automating these steps using automated compliance software can enhance efficiency and accuracy. With automation, tracking and documenting compliance efforts become significantly easier, helping during audits.
Simplify the process of complying with the GLBA by downloading our comprehensive checklist. This tool provides actionable steps to help IT teams stay on top of GLBA compliance requirements. This downloadable checklist includes detailed guidance on safeguarding NPI, maintaining data privacy, and adhering to incident response protocols. It’s an invaluable resource for organizations looking to streamline compliance efforts and ensure no critical aspect is overlooked.
Managing the complexity of GLBA compliance can be daunting. Trio, an easy-to-use Mobile Device Management (MDM) solution, is here to help organizations meet GLBA compliance requirements efficiently.
Trio’s user-friendly platform also simplifies GLBA risk assessments and audits, providing IT professionals with actionable insights. By centralizing device management and automating compliance efforts, Trio empowers organizations to achieve GLBA compliance without unnecessary complexity. Ready to see Trio in action? Book a free demo today.
In conclusion, achieving GLBA compliance is critical for any organization handling financial services, as it protects sensitive customer information and builds trust. By following a structured GLBA compliance checklist, conducting thorough risk assessments, and developing a solid incident response plan, IT teams can ensure they meet regulatory requirements effectively. Leveraging tools like Trio's Mobile Device Management (MDM) solution can simplify the compliance process, helping organizations stay on top of data security, policy enforcement, and audits. Downloading the GLBA compliance checklist is the first step toward streamlining your efforts and safeguarding your organization’s future in an increasingly complex digital landscape.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
A NIST 800-171 compliance checklist with all 110 Rev. 2 requirements, their SPRS points, Rev. 3 changes, CMMC status and a self-assessment guide. Free Excel.
A SOC 2 compliance checklist for IT teams: 69 controls mapped to the Trust Services Criteria, with the evidence auditors sample. Free PDF and Excel.
Learn what each Conditional Access policy template does and when to use it. Download ready-to-use ACP templates for identity security.
Complete SAMA compliance checklist for Saudi financial institutions. Domain-by-domain requirements, obligations, and practical implementation steps.
The NCA compliance checklist your team actually needs: ECC-2:2024 domains, NCNICC-1:2025, and what auditors look for as evidence.
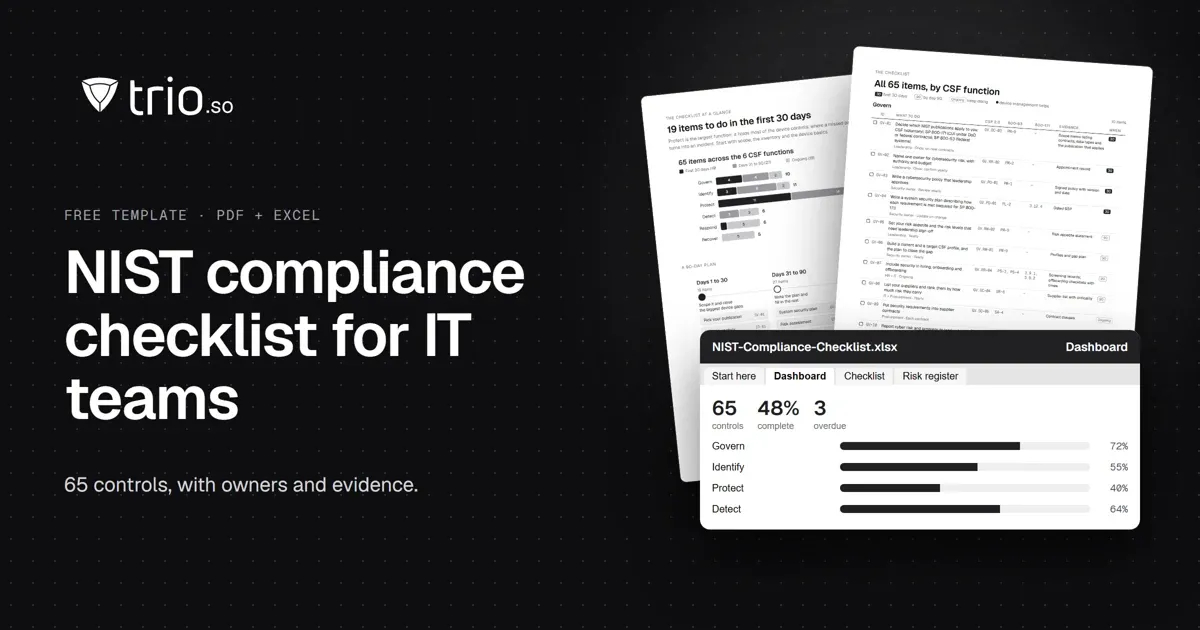
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Feeling overwhelmed by CCPA? Use this comprehensive CCPA Compliance Checklist to secure customer data on mobile devices. Discover how MDM simplifies compliance.
Need an MDM audit checklist? Our guide covers 7 key areas & compliance strategies to ensure your mobile device management is secure and efficient.