



Templates
NIST 800-171 Compliance Checklist: 110 Requirements and SPRS
A NIST 800-171 compliance checklist with all 110 Rev. 2 requirements, their SPRS points, Rev. 3 changes, CMMC status and a self-assessment guide. Free Excel.
The full NIST 800-53 Rev. 5 controls list: 20 families, the Low, Moderate and High baselines, and a step-by-step checklist. Free Excel and PDF.

Content writer, trio.so
NIST SP 800-53 is the catalog of security and privacy controls behind federal systems, FedRAMP and many corporate security programs. Revision 5 has 20 control families and, in the current release 5.2.0, 1,014 active controls and enhancements. Nobody implements all of them: you pick a baseline, tailor it, and prove each control works.
This page gives you the NIST 800-53 controls list in a form you can use. You get the 20 families with their counts, the Low, Moderate and High baselines, a checklist that follows the Risk Management Framework, and the controls that live on laptops and phones.
Download the full list as an Excel workbook: every control and enhancement with its NIST text, the baselines it belongs to, a baseline picker, and columns for status, owner and evidence. A short PDF guide comes with it.
In short
NIST Special Publication 800-53, "Security and Privacy Controls for Information Systems and Organizations", is a catalog of safeguards. Each control says what to do, such as "Develop and document an inventory of system components". It leaves the how to you, with organization-defined values you fill in, like how many minutes of inactivity before a screen locks.
Revision 5 came out in September 2020. It dropped "Federal" from the title, made the controls outcome-based, merged privacy controls into the catalog, and added the Supply Chain Risk Management (SR) and PII Processing and Transparency (PT) families. NIST has updated it since, most recently with release 5.1.1 in November 2023 and release 5.2.0 in August 2025, which is current.
If you handle Controlled Unclassified Information (CUI) under a DoD contract, the document you need is SP 800-171, which is derived from 800-53. See our NIST 800-171 compliance checklist.
There is no 800-53 certification. NIST does not certify organizations. A federal system gets an authorization to operate (ATO) from the agency, and a cloud service gets a FedRAMP authorization. Our guide to NIST compliance explains how the three NIST documents fit together.
Every control ID starts with its family's two-letter code: AC-02 is Account Management in the Access Control family, and AC-02(01) is its first enhancement. Release 5.1.1 added the leading zero, so you'll see AC-2 and AC-02 for the same control.
| ID | Family and what it covers | Controls | Enhancements | In Moderate |
|---|---|---|---|---|
| AC | Access Control Accounts, least privilege, remote access, session and device lock, mobile devices | 23 | 108 | 39 |
| AT | Awareness and Training Security and privacy awareness training, role-based training | 5 | 10 | 6 |
| AU | Audit and Accountability What gets logged, how long logs are kept, who reviews them | 15 | 41 | 16 |
| CA | Assessment, Authorization, and Monitoring Control assessments, the ATO, the POA&M, continuous monitoring | 8 | 17 | 10 |
| CM | Configuration Management Baseline configurations, settings, change control, inventory, allowed software | 14 | 42 | 24 |
| CP | Contingency Planning Contingency plans, backups, alternate sites, recovery | 12 | 37 | 23 |
| IA | Identification and Authentication Identifying and authenticating users and devices, MFA, passwords | 13 | 46 | 24 |
| IR | Incident Response Incident response plans, handling, reporting and testing | 9 | 31 | 13 |
| MA | Maintenance Controlled maintenance, tools and maintenance staff | 7 | 21 | 9 |
| MP | Media Protection Protecting, transporting and sanitizing media, including USB storage | 8 | 12 | 7 |
| PE | Physical and Environmental Protection Physical access, visitors, power, fire and environmental protection | 22 | 29 | 18 |
| PL | Planning Security and privacy plans, rules of behavior, architecture | 8 | 3 | 7 |
| PM | Program Management The organization-wide program; not in the security baselines | 32 | 5 | 0 |
| PS | Personnel Security Screening, transfers and terminations, access agreements | 9 | 8 | 9 |
| PT | Personally Identifiable Information Processing and Transparency How personal data is processed: authority, purpose, consent, notices | 8 | 13 | 0 |
| RA | Risk Assessment Categorization, risk assessments, vulnerability scanning | 9 | 13 | 10 |
| SA | System and Services Acquisition Buying and building systems securely, developer testing | 17 | 91 | 17 |
| SC | System and Communications Protection Boundary protection, encryption in transit and at rest | 47 | 92 | 25 |
| SI | System and Information Integrity Patching, malware protection, system monitoring, integrity | 22 | 80 | 18 |
| SR | Supply Chain Risk Management Supply chain risk plans, supplier assessments, provenance | 12 | 15 | 12 |
| Total | 300 | 714 | 287 |
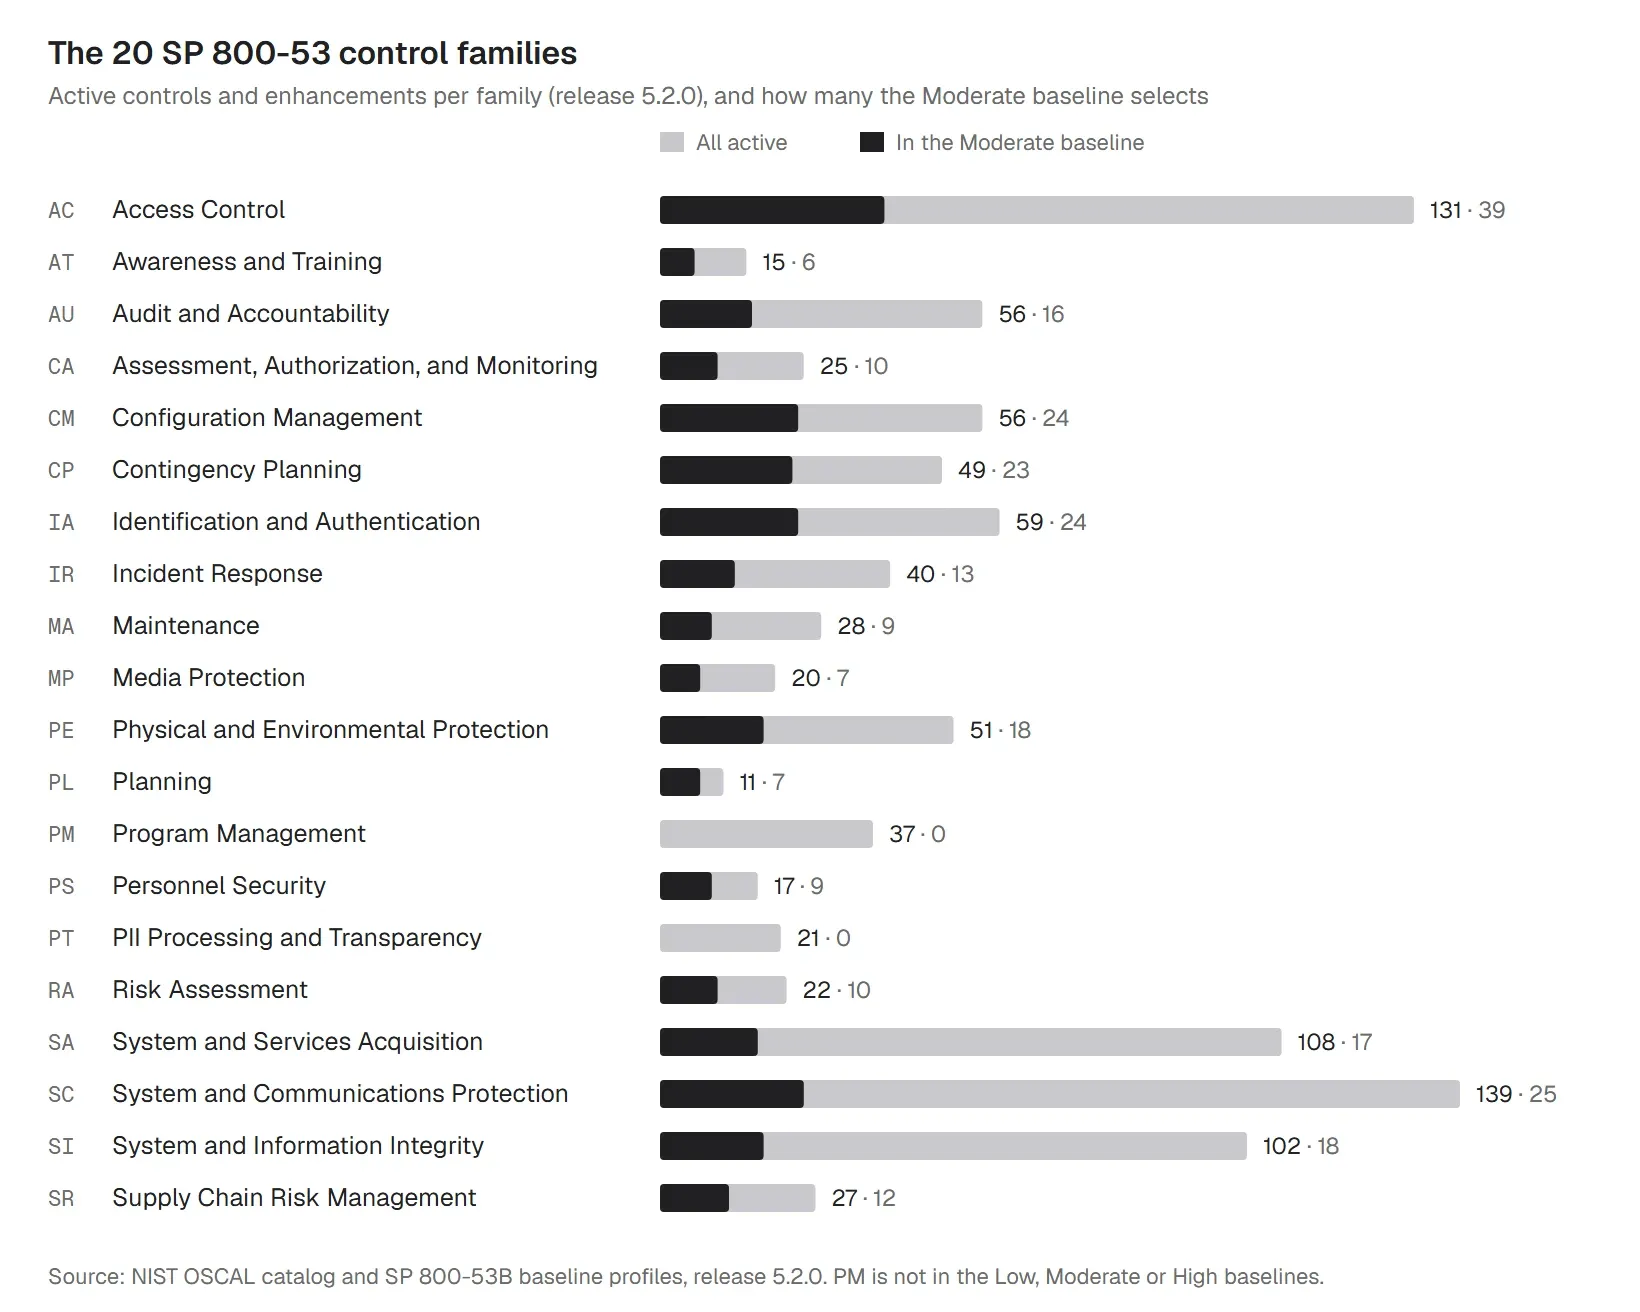
The catalog has 1,196 entries in total, but 182 of them are withdrawn: moved or folded into other controls. That's why you'll see "1,196 controls" on some sites. The number in force is 1,014. The Excel workbook has a tab listing every withdrawn item and where it went.
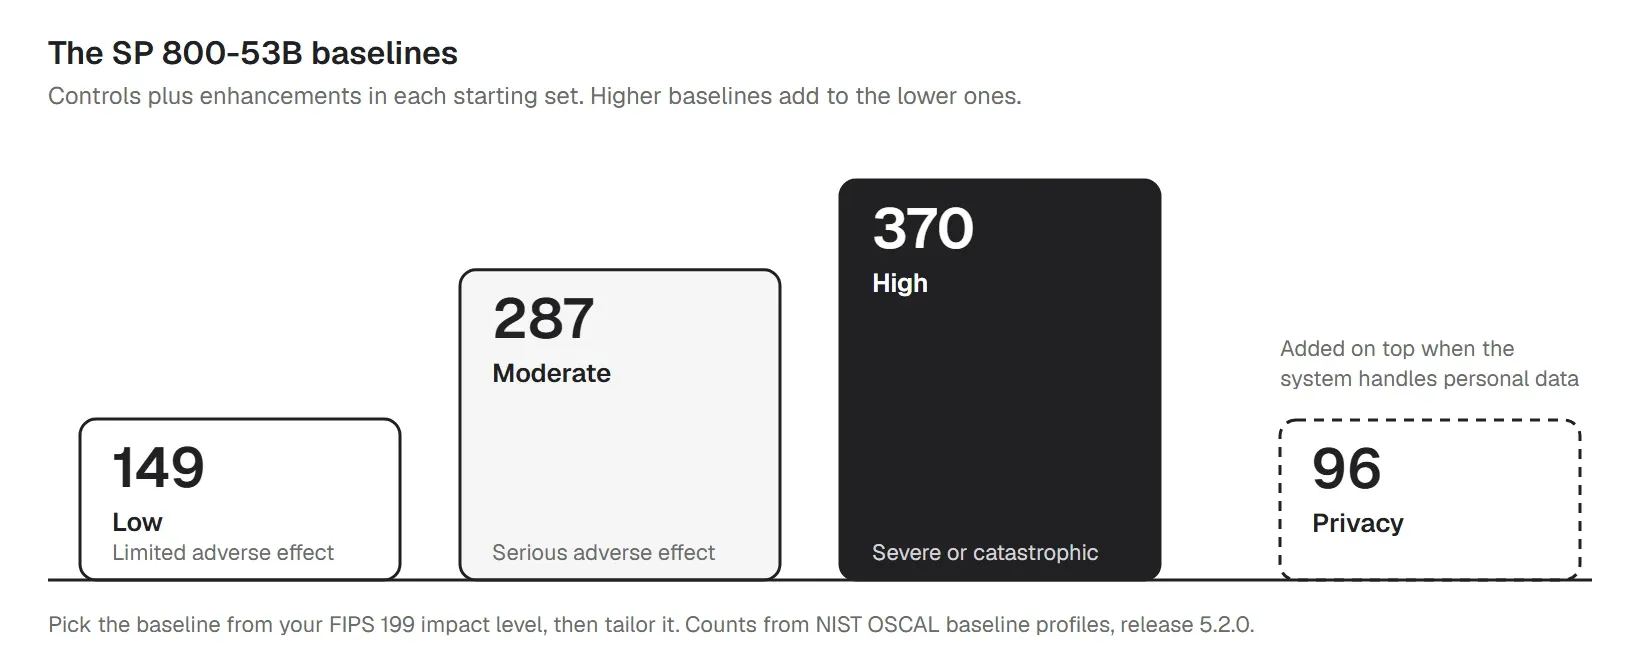
SP 800-53B gives you a starting set of controls for each impact level. You find your level with FIPS 199: rate the harm if the system's confidentiality, integrity or availability were lost as Low, Moderate or High. The highest of the three sets the baseline.
| Baseline | Controls plus enhancements | When it applies |
|---|---|---|
| Low | 149 | A loss would have a limited adverse effect. |
| Moderate | 287 | A loss would have a serious adverse effect. |
| High | 370 | A loss would have a severe or catastrophic effect. |
| Privacy | 96 | The system processes personal data. Used alongside a security baseline. |
Two things often trip people up. First, controls aren't labeled Low, Moderate or High: the baselines select them, and the same control can appear in all three with more enhancements at the higher levels. Second, the Program Management (PM) family isn't in the Low, Moderate or High baselines (the Privacy baseline selects some PM controls). You implement it once for the whole organization.
800-53 is used through the Risk Management Framework (SP 800-37). The checklist below follows its seven steps. The control IDs are the main 800-53 controls behind each step.
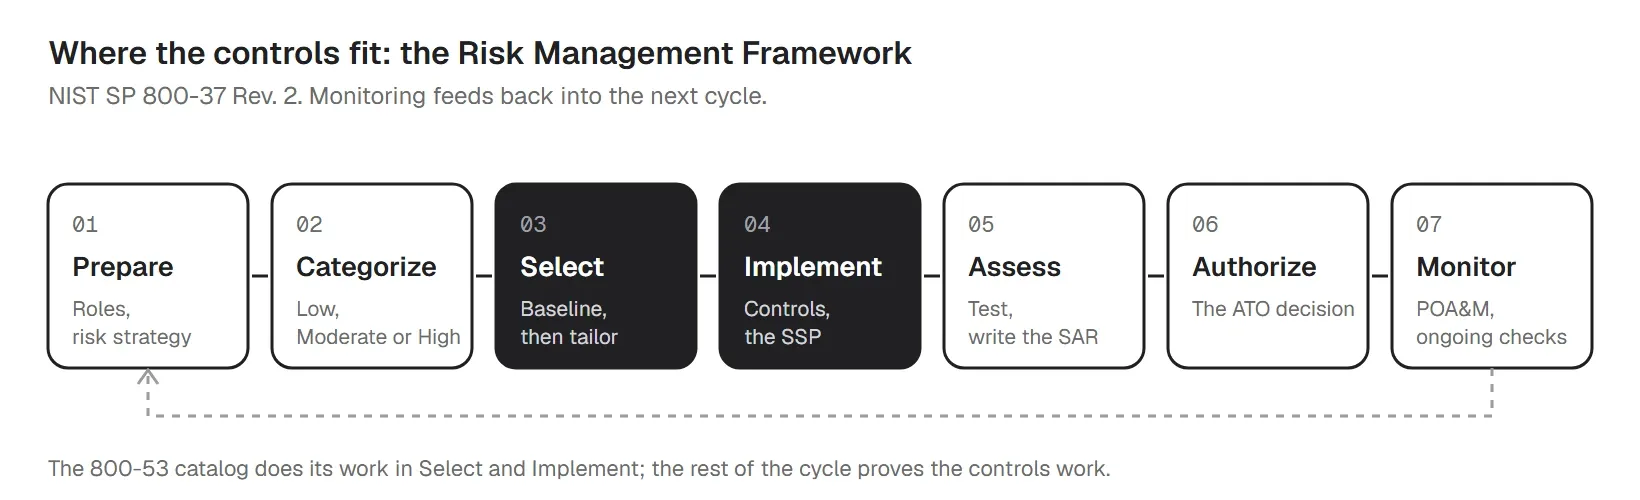
| What to do | 800-53 | |
|---|---|---|
| ☐ | Name the authorizing official, the system owner and the security owner. | PM-02, PM-10 |
| ☐ | Define the system boundary: what's in it, and what's inherited. | PL-02 |
| ☐ | Write the risk management strategy and the risk tolerance. | PM-09 |
| What to do | 800-53 | |
|---|---|---|
| ☐ | List the information types the system handles. | RA-02 |
| ☐ | Rate confidentiality, integrity and availability with FIPS 199, and get the result approved. | RA-02 |
| What to do | 800-53 | |
|---|---|---|
| ☐ | Start from the matching baseline. | PL-10 |
| ☐ | Tailor it, and fill in the organization-defined values. | PL-11 |
| ☐ | Add the Privacy baseline if the system processes personal data. | PL-10, PT-01 |
| ☐ | Write the continuous monitoring strategy. | CA-07 |
| What to do | 800-53 | |
|---|---|---|
| ☐ | Keep a complete inventory of hardware and software. | CM-08 |
| ☐ | Set baseline configurations and enforce them on every device. | CM-02, CM-06 |
| ☐ | Turn on MFA for privileged and non-privileged accounts. | IA-02(01), IA-02(02) |
| ☐ | Encrypt data at rest on laptops and mobile devices. | SC-28, AC-19(05) |
| ☐ | Patch on a schedule and scan for vulnerabilities. | SI-02, RA-05 |
| ☐ | Log security events and review them. | AU-02, AU-06 |
| ☐ | Back up, and test a restore. | CP-09, CP-04 |
| ☐ | Describe each control in the system security plan (SSP). | PL-02 |
| What to do | 800-53 | |
|---|---|---|
| ☐ | Test each control and record the results in a security assessment report (SAR). | CA-02 |
| ☐ | Open a POA&M item for every weakness, with an owner and a date. | CA-05 |
| What to do | 800-53 | |
|---|---|---|
| ☐ | Give the SSP, SAR and POA&M to the authorizing official for a decision. | CA-06 |
| What to do | 800-53 | |
|---|---|---|
| ☐ | Assess a share of the controls every year. | CA-07 |
| ☐ | Check changes for security impact before they go live. | CM-04 |
| ☐ | Keep the SSP, SAR and POA&M current. | CA-07, PL-02 |
The Implement step is where the bulk of the work sits, so the Excel workbook lists every control in your baseline with a status, an owner and an evidence column. The PDF has this same checklist on two printable pages.
Release 5.2.0 came out on August 27, 2025. It is a minor release that responds to Executive Order 14306 on software update and patch security. It added three items:
| ID | Name | What it asks for |
|---|---|---|
| SA-15(13) | Logging Syntax | Developers use a consistent, documented logging syntax. |
| SA-24 | Design for Cyber Resiliency | Design systems to meet defined cyber resiliency goals and objectives. |
| SI-02(07) | Root Cause Analysis | Find the root cause of flaws, act on it and check the fix works. |
None of the three is in a baseline, so a baseline-driven program doesn't have to add them unless tailoring calls for it. The release also widened SI-07(12) integrity verification to all organization-defined software and updated the discussion text of several patching controls. SP 800-53B had no content changes.
Many 800-53 controls are policies and plans. A smaller set is enforced on each device, and assessors can often test those with a report. Most of them are in the Moderate baseline; CM-07(04) is in no baseline, so you add it when tailoring.
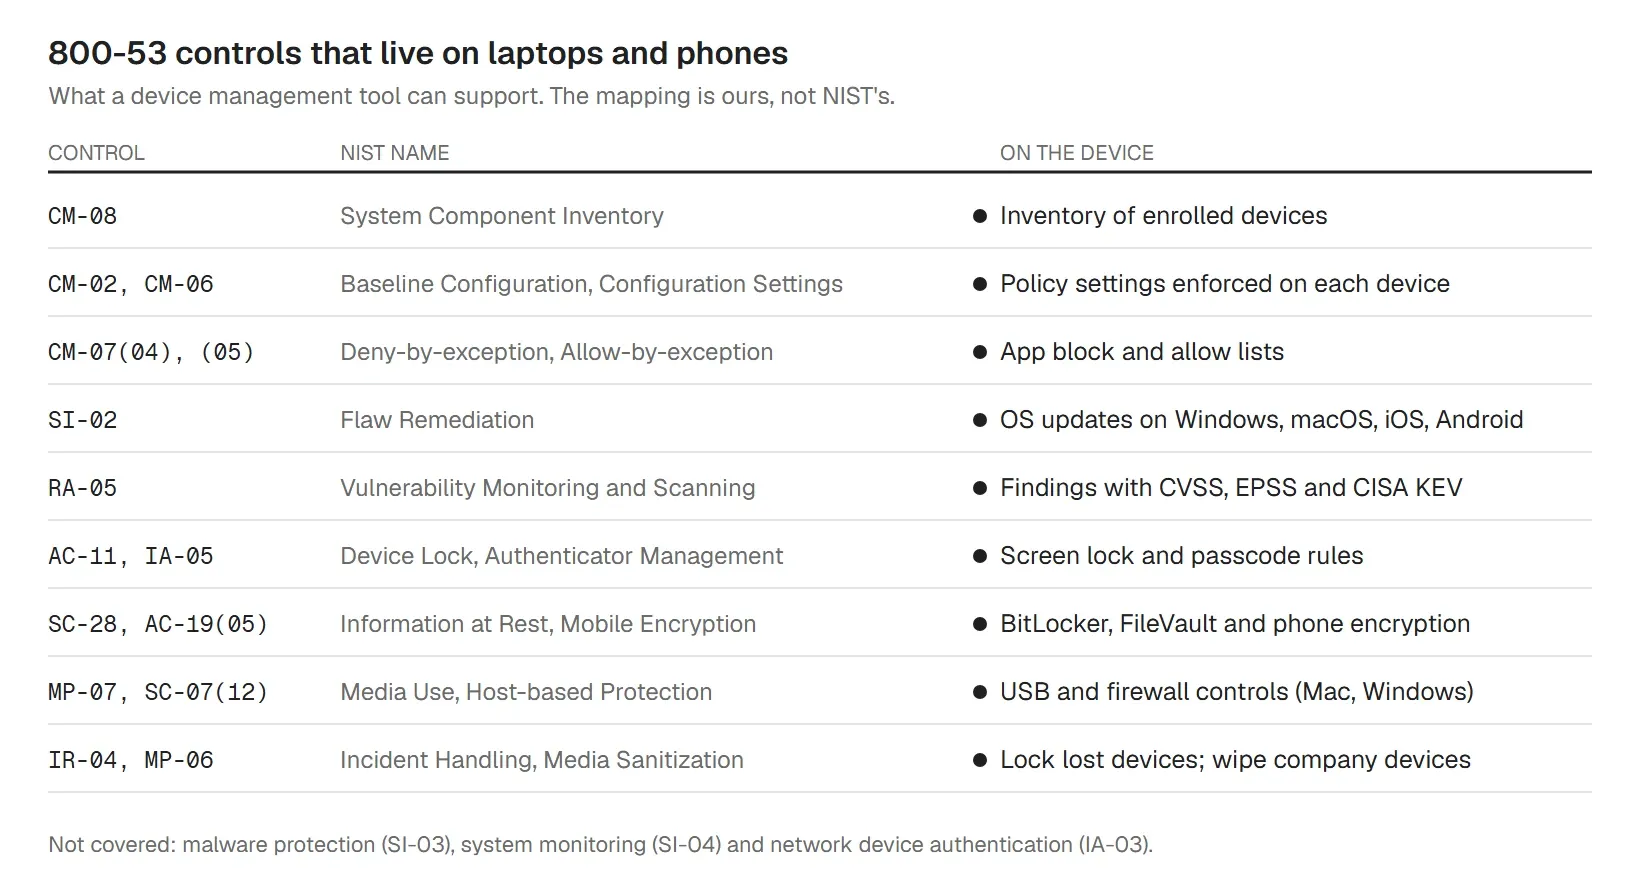
Some controls are not device-management work: malware protection (SI-03) comes from your EDR or antivirus, system monitoring (SI-04) from your detection tools, and device authentication to the network (IA-03) from network access control.
An assessor tests controls by examining documents, interviewing people and testing systems. Keep these current and dated:
| Evidence | Controls | Suggested refresh |
|---|---|---|
| System security plan (SSP), with the boundary and how each control is implemented | PL-02 | On every significant change |
| Security categorization, approved | RA-02 | On every significant change |
| Hardware and software inventory export | CM-08 | Monthly |
| Configuration baseline and a compliance report against it | CM-02, CM-06 | Monthly |
| Patch status and vulnerability scan results | SI-02, RA-05 | Monthly |
| Encryption status per device | SC-28 | Monthly |
| Access reviews and MFA enrollment | AC-02, IA-02 | Quarterly |
| Incident response plan and test results | IR-08, IR-03 | Yearly |
| Backup restore test | CP-09, CP-04 | Yearly |
| Security assessment report (SAR) and the POA&M | CA-02, CA-05 | Yearly, POA&M monthly |
The frequencies are suggestions. Your organization-defined values and your assessor set the real ones.
| SP 800-53 Rev. 5 | SP 800-171 | CSF 2.0 | |
|---|---|---|---|
| What it is | Catalog of controls | Requirements for protecting CUI | Outcomes to aim for |
| Size | 1,014 controls and enhancements, 20 families | 110 requirements (Rev. 2); 97 in Rev. 3 | 6 functions, 106 subcategories |
| Who must use it | Federal systems | Contractors with CUI | Voluntary for most |
| Proof | Authorization to operate | SPRS score, CMMC | Self-assessment |
They are built to work together: the CSF says what outcomes you need, 800-53 supplies the controls, and 800-171 is derived from 800-53 for contractors. Our NIST compliance checklist maps one set of tasks to all three, and NIST vs ISO 27001 compares 800-53 with ISO.
More NIST guides for IT teams
Your 800-53 program, its documents and its authorization stay with your organization. trio.so supports the device controls from one console:
14-day free trial. No credit card required.
Sources. Last reviewed October 2026. Counts are taken from NIST's OSCAL catalog and baseline profiles, release 5.2.0. The device mapping is ours, not NIST's. This article is guidance, not legal advice.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.
Every organization today needs a solution to automate time-consuming tasks and strengthen security. Without the right tools, manual processes drain resources and leave gaps in protection. trio.so is designed to solve this problem, automating key tasks, boosting security, and ensuring compliance with ease.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
A NIST 800-171 compliance checklist with all 110 Rev. 2 requirements, their SPRS points, Rev. 3 changes, CMMC status and a self-assessment guide. Free Excel.
A SOC 2 compliance checklist for IT teams: 69 controls mapped to the Trust Services Criteria, with the evidence auditors sample. Free PDF and Excel.
Ten Microsoft Entra conditional access policy templates with what each does, the order to enable them in report-only mode, licensing, and a free download.
SAMA compliance checklist for the SAMA CSF: 4 domains and 32 subdomains, maturity levels 0 to 5, evidence and owners, with a free PDF and Excel tracker.
NCA ECC compliance checklist for ECC-2:2024: all 108 controls by domain, the evidence to keep and the device controls, with a free PDF and Excel tracker.
A NIST compliance checklist for IT teams: 65 controls by CSF 2.0 function, mapped to SP 800-53 and 800-171, with an SPRS calculator. Free PDF and Excel.
Feeling overwhelmed by CCPA? Use this comprehensive CCPA Compliance Checklist to secure customer data on mobile devices. Discover how MDM simplifies compliance.
Need an MDM audit checklist? Our guide covers 7 key areas & compliance strategies to ensure your mobile device management is secure and efficient.
14 day free trial. No credit card required.
trio.so for MSPs: one console, separate clients