

Explained
10 Best Practices for Effective IT Vendor Management
Learn the best practices for IT vendor management, covering roles, responsibilities, and frameworks to improve vendor relationships.
With five years of experience in the tech industry and content writing, Atena writes about IT management, emerging technologies, and practical solutions to everyday IT challenges. At trio.so, she focuses on making complex technical topics accessible and helping businesses understand how unified agentic IT management can simplify their operations.
Atena on LinkedInLearn the best practices for IT vendor management, covering roles, responsibilities, and frameworks to improve vendor relationships.
Discover the importance of a data encryption policy template for your organization's security. Learn how to protect sensitive information effectively.
Learn how to create a bastion host for your cloud infrastructure. Follow our step-by-step guide to enhance security and control access.
Get a clear view of the five types of employees most likely to leak or misuse company data and practical steps to reduce the chances of insider threats.
Need help with PostgreSQL and Active Directory connection? This step-by-step guide simplifies the process.
A free penetration testing policy template, with the benefits of a formal policy and the components it should include.
Learn about email security protocols to prevent phishing attacks. From SPF and DKIM to secure email gateways, protect your email systems today!
Confused about FISMA vs FedRAMP compliance? This guide breaks down the top 7 security factors to help you make informed decisions.
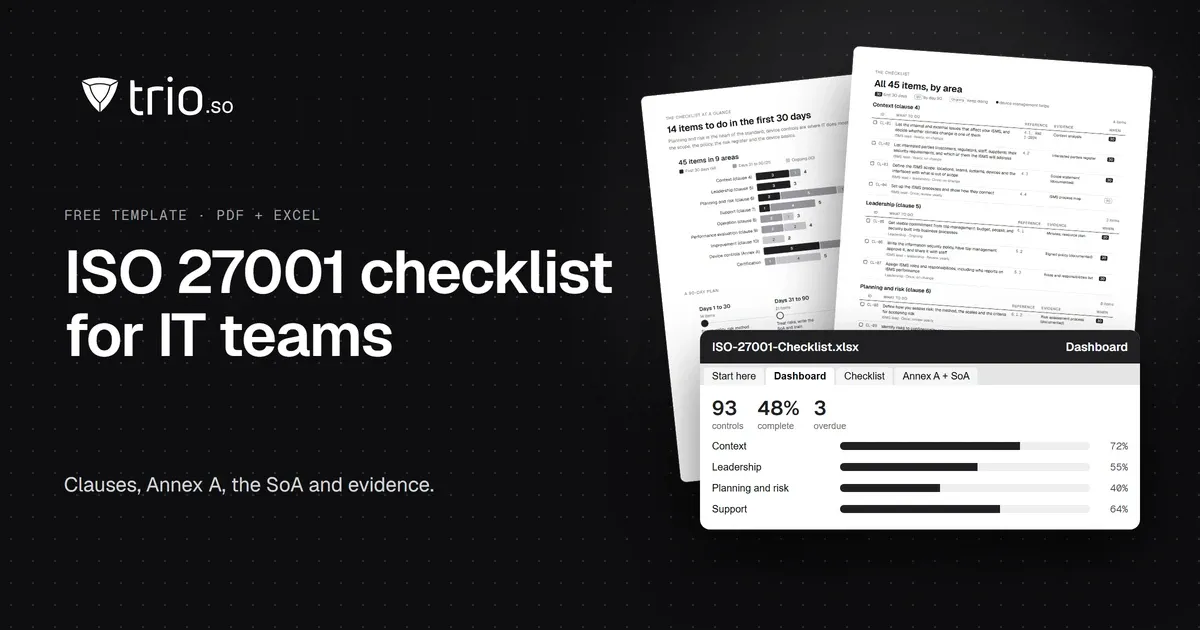
An ISO 27001 checklist for IT teams: clauses 4 to 10, all 93 Annex A controls with an SoA template, risk register and device controls. Free PDF and Excel.

Learn the essentials of Federal Risk and Authorization Management Program compliance and the benefits for cloud service providers.
Discover essential confidentiality best practices to protect sensitive data, mitigate risks, and ensure regulatory compliance in today's digital landscape.
Learn about the Federal Information Security Management Act’s security controls, and why they are essential for compliance.