



Templates
PCI Compliance Checklist for PCI DSS v4.0.1 (PDF + Excel)
PCI compliance checklist for PCI DSS v4.0.1: the 12 requirements, the 51 future-dated items, CDE scoping and SAQ vs ROC, with a free PDF and Excel tracker.
PCI compliance audit guide for PCI DSS v4.0.1: QSA, ISA or SAQ, ROC vs AOC, ASV scans, pen tests, the evidence auditors ask for and how to prepare.

Content writer, trio.so
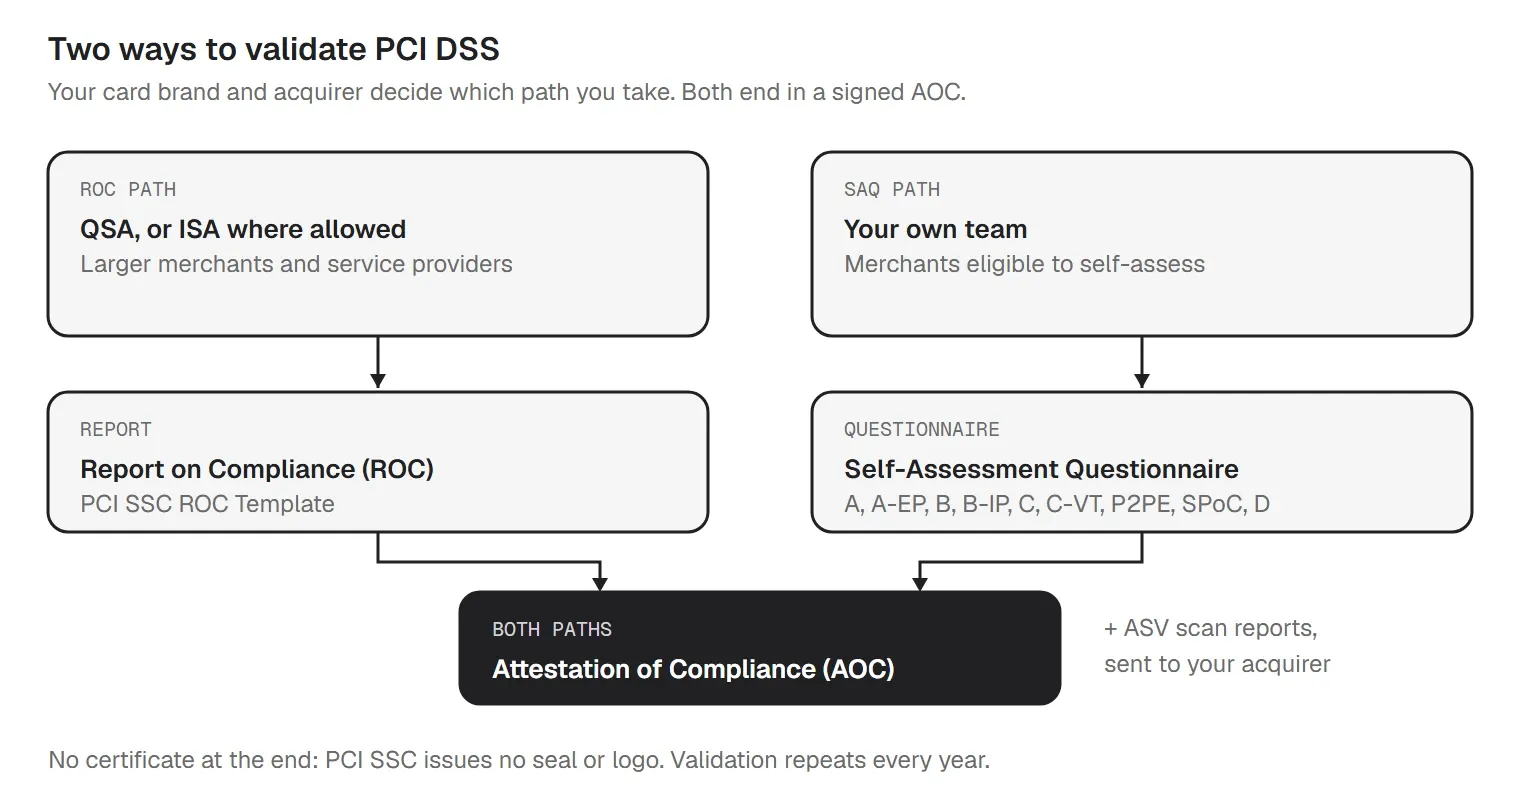
A PCI compliance audit is the yearly check that your business protects card data the way PCI DSS requires. The standard itself calls it an assessment. Depending on your size and how you take payments, a Qualified Security Assessor (QSA) audits you and writes a Report on Compliance (ROC), or your own team completes a Self-Assessment Questionnaire (SAQ). Either way, you sign an Attestation of Compliance (AOC) and send it to your acquiring bank.
This guide covers who audits whom under PCI DSS v4.0.1, the documents an audit produces, the scans and penetration tests behind it, the evidence assessors ask for under each of the 12 requirements, and how to prepare.
In short
PCI DSS is published by the PCI Security Standards Council (PCI SSC), founded by American Express, Discover, JCB International, Mastercard and Visa. It applies to any business that stores, processes or transmits cardholder data, or could affect its security (PCI SSC). A PCI audit checks whether the controls it asks for are in place in your cardholder data environment (CDE): the people, processes and systems that handle card data, plus the systems connected to them.
PCI SSC doesn't audit anyone or enforce the standard. Each card brand runs its own compliance program and decides who validates and how, usually through your acquiring bank (PCI SSC FAQ 1212).
Three points trip people up:
Four roles show up in a PCI DSS audit. PCI SSC publishes the lists of QSA companies and ASVs on its website (PCI SSC listings).
| Role | Who they are | What they produce |
|---|---|---|
| Qualified Security Assessor (QSA) | An independent assessor company qualified by PCI SSC; usually what people mean by a PCI compliance auditor | The ROC and the assessor's sections of the AOC |
| Internal Security Assessor (ISA) | One of your own employees, trained and qualified by PCI SSC | Your assessment, where your acquirer or card brand accepts an ISA |
| Your own team | Whoever owns PCI DSS at your company | An SAQ and AOC, if you are eligible to self-assess |
| Approved Scanning Vendor (ASV) | A scanning company on PCI SSC's ASV list | Quarterly external vulnerability scans only |
Which route you take depends on your merchant level, which each card brand defines; PCI DSS doesn't. Visa expects an annual ROC by a QSA from Level 1 merchants, with over 6 million Visa transactions a year, and an SAQ from Levels 2 and 3, all three with quarterly ASV scans. For Level 4, under 20,000 e-commerce transactions and other merchants up to 1 million, Visa recommends an SAQ and leaves the rules to the acquirer (Visa). Service providers handling more than 300,000 Visa transactions a year need a QSA-led ROC too.
Mastercard, American Express, Discover and JCB set their own levels, and your acquirer decides how its program applies to you, so ask it in writing. For levels and SAQ types from a smaller merchant's point of view, see PCI compliance for small business.
Every PCI audit ends in paperwork on PCI SSC's templates, and the three names get mixed up.
| Document | Who completes it | What it is |
|---|---|---|
| Report on Compliance (ROC) | A QSA, or an ISA where allowed | The full assessment report, written on PCI SSC's mandatory ROC Template. It records how each requirement was tested and what the assessor found. |
| Self-Assessment Questionnaire (SAQ) | You | A questionnaire for businesses that are eligible to self-assess. Each type (A, A-EP, B, B-IP, C, C-VT, P2PE, SPoC, D) fits one payment setup and lists only the requirements that apply to it. |
| Attestation of Compliance (AOC) | You, plus the QSA or ISA if one assessed you | The signed statement of your compliance status. It goes to your acquirer or the card brand with the ROC or SAQ and any ASV scan reports. |
The PCI DSS attestation of compliance comes in a merchant and a service provider version, and the official forms are available only from the PCI SSC website (Document Library). PCI DSS doesn't treat the AOC as sensitive, so service providers share theirs with customers. Requirement 12.8.4 asks you to check your service providers' PCI DSS status at least every 12 months, and their AOC is the usual way to do it.
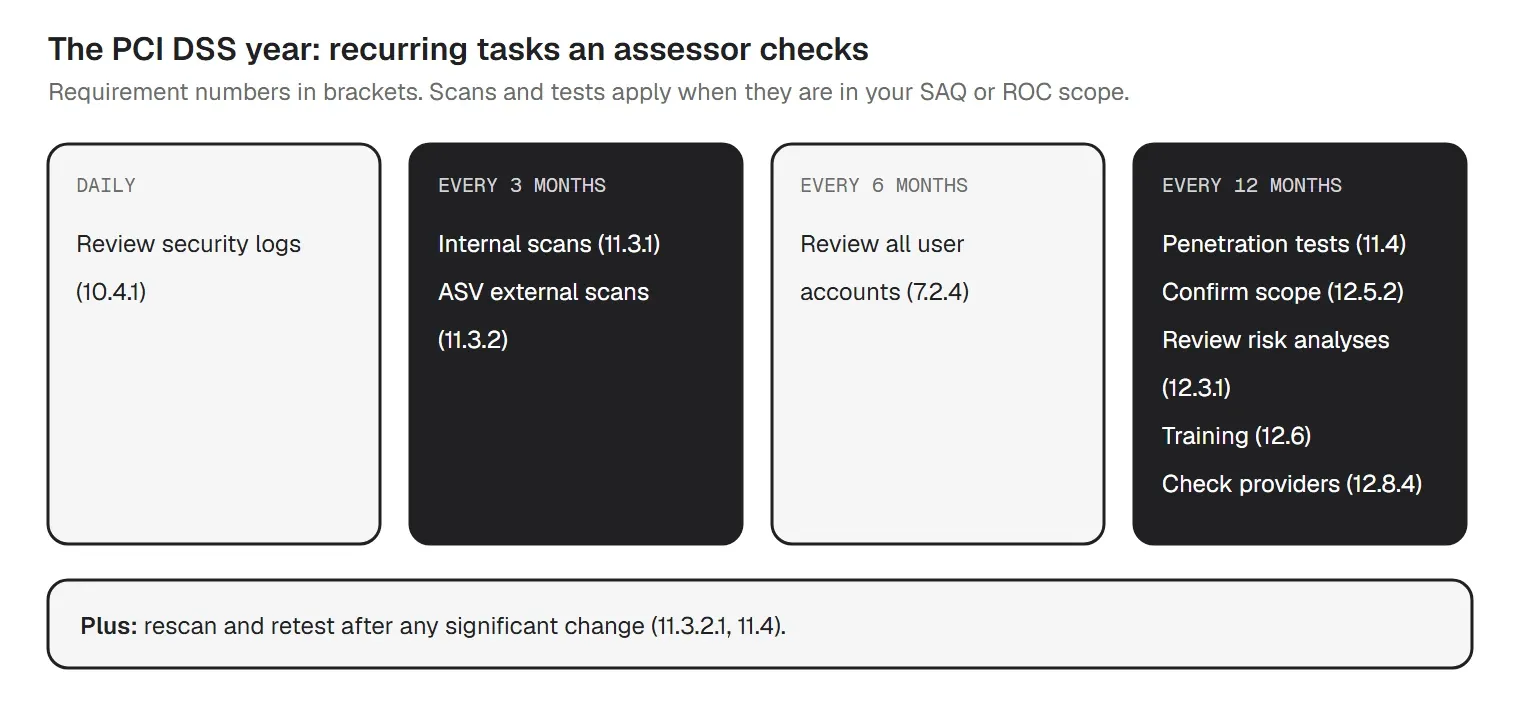
Requirement 11 sets the testing that runs between assessments, and your assessor will want results from across the year.
| Test | Requirement | How often | Who runs it |
|---|---|---|---|
| Internal vulnerability scans | 11.3.1 | At least every three months; high-risk and critical findings fixed and rescanned | Your team or a provider. Scans must be authenticated (11.3.1.2). |
| External vulnerability scans | 11.3.2 | At least every three months, with a passing result | An ASV |
| Penetration tests, internal and external | 11.4.2, 11.4.3 | At least every 12 months and after significant changes | A qualified tester who is organizationally independent; not necessarily a QSA or ASV |
| Segmentation tests | 11.4.5 | Every 12 months and after changes, if segmentation reduces your scope (every six months for service providers) | As for penetration tests |
A PCI ASV scan is an external scan of your internet-facing systems by a company on PCI SSC's ASV list. It has to pass under the ASV Program Guide's rules, so you fix findings and rescan until it does. After a significant change you scan again, and that rescan can be done by qualified, independent staff instead of an ASV (11.3.2.1). Which tests apply depends on your SAQ or ROC scope: SAQ D covers every requirement, penetration testing included, while shorter SAQs leave out tests that don't fit their payment setup.
PCI DSS v4.0.1 groups 12 principal requirements under six goals, and an assessor works through every one that applies to you. If your audit checklist still names "firewall configuration" or "anti-virus software" as requirements, it was written for v3.2.1, which was retired on 31 March 2024. v4.0 was retired on 31 December 2024, and v4.0.1, published in June 2024, is the only active version (PCI SSC).
| No. | Requirement | Evidence an assessor typically asks for |
|---|---|---|
| 1 | Install and Maintain Network Security Controls | Network and card data flow diagrams, rule sets, records of rule reviews |
| 2 | Apply Secure Configurations to All System Components | Configuration standards per system type, changed vendor defaults, settings on sampled systems |
| 3 | Protect Stored Account Data | Retention policy, where card numbers (PAN) are stored and how they are made unreadable, key management |
| 4 | Protect Cardholder Data with Strong Cryptography During Transmission Over Open, Public Networks | Encryption settings for data in transit, the inventory of trusted keys and certificates (4.2.1.1) |
| 5 | Protect All Systems and Networks from Malicious Software | Anti-malware coverage and updates, anti-phishing controls (5.4.1) |
| 6 | Develop and Maintain Secure Systems and Software | Critical patches within one month (6.3.3), custom software records, payment-page script inventory (6.4.3) |
| 7 | Restrict Access to System Components and Cardholder Data by Business Need to Know | Access policy, role definitions, six-monthly account reviews (7.2.4) |
| 8 | Identify Users and Authenticate Access to System Components | Unique IDs, 12-character passwords (8.3.6), MFA into the CDE (8.4.2), inactive accounts removed within 90 days |
| 9 | Restrict Physical Access to Cardholder Data | Visitor and media records, the list and inspection log of card-reading devices (9.5.1) |
| 10 | Log and Monitor All Access to System Components and Cardholder Data | Daily log reviews, automated review (10.4.1.1), 12 months of logs with three immediately available |
| 11 | Test Security of Systems and Networks Regularly | A year of internal and ASV scans, penetration test reports, payment-page change detection (11.6.1) |
| 12 | Support Information Security with Organizational Policies and Programs | Policy, targeted risk analyses (12.3.1), scope confirmation (12.5.2), training, service providers, incident response plan |
In v4, the first section of every requirement (1.1, 2.1 and so on) asks for documented policies, procedures and roles, so expect to show those for all 12. For every sub-requirement as a working list, use our PCI compliance checklist.
PCI DSS doesn't set a length for the assessment itself. The yearly cycle is fixed, though: scope confirmation, four quarters of scans and a yearly penetration test have to fit inside it, so start the gap assessment months before your AOC is due.
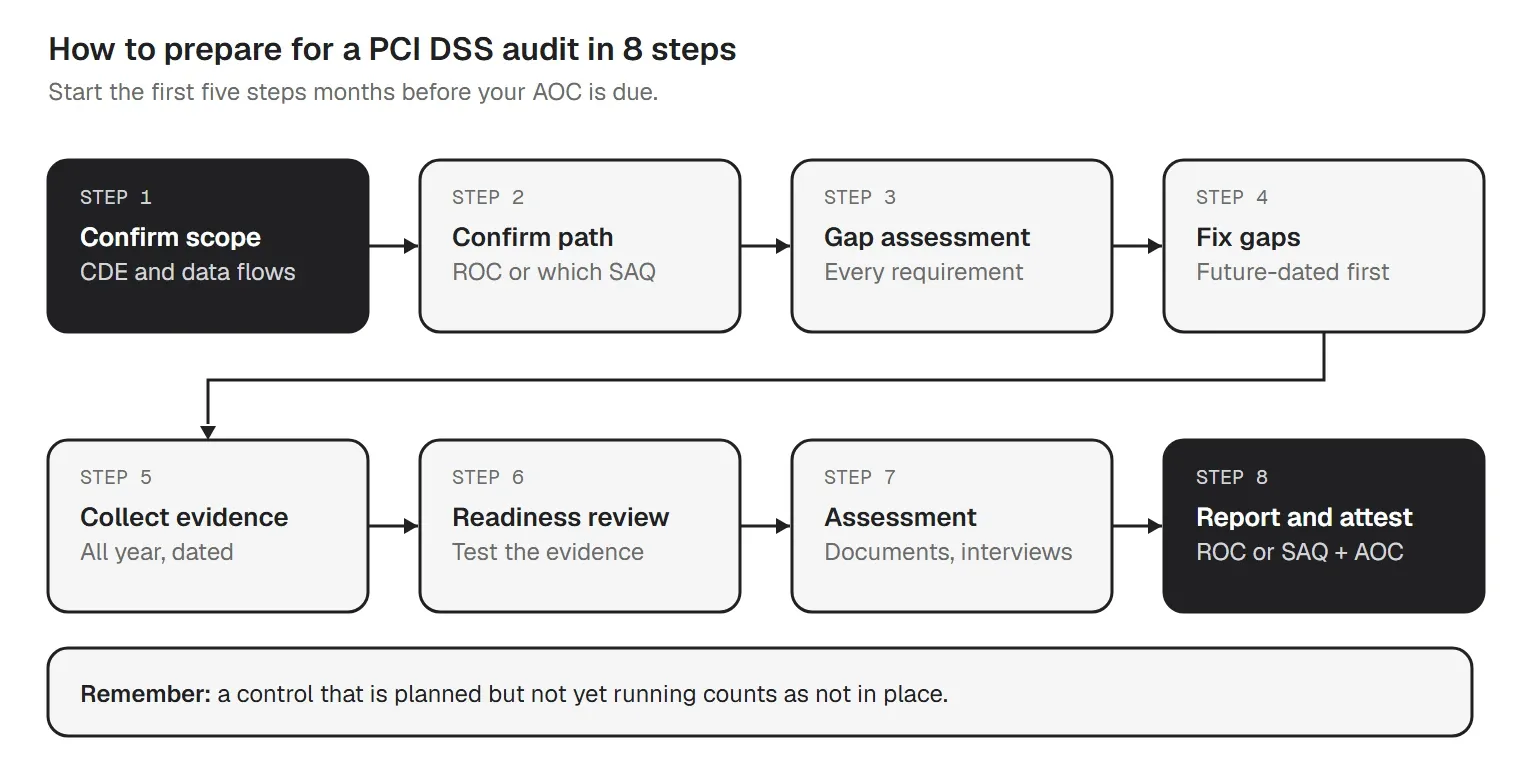
Map where card data enters, moves and is stored, and list every system in or connected to the CDE. Requirement 12.5.2 asks you to confirm scope at least every 12 months and after significant changes (every six months for service providers, 12.5.2.1). Tokenization, P2PE terminals and hosted payment pages keep card data off your systems, and shrinking scope usually saves more than anything else.
Ask your acquirer whether you need a ROC or an SAQ, which SAQ type, and when the AOC is due. If a QSA will assess you, agree on dates and evidence format early.
Mark every applicable requirement in place, not in place or not applicable. PCI SSC's free Prioritized Approach tool sorts the requirements into six milestones if you need an order to work in (FAQ 1170).
Start with card data you store but don't need, then the future-dated requirements below. A control that is scheduled but not yet running counts as not in place.
Scan reports, log and access reviews, training records and policy approvals all carry dates. File them by requirement number as you go.
Ask your QSA whether it offers one. Otherwise, have someone who didn't build a control try to show it working from the evidence alone.
The assessor reviews documents and settings, interviews the people who run each control and samples systems and locations. Keep each requirement's owner on hand.
The QSA writes the ROC, or you complete the SAQ. The signed AOC goes to your acquirer with any ASV scan reports.
PCI DSS v4.0 added 64 new requirements. 13 applied straight away, and the other 51 were best practice until 31 March 2025; since then they count in every assessment (Summary of Changes). v4.0.1 only clarified wording. A program built for v3.2.1 will usually have gaps here:
Check two older problems at the same time: a CDE that has grown since the scope was last written down, and evidence that covers one quarter but not the other three.
If every applicable requirement is in place, the signed AOC goes to your acquirer or the card brand with the ROC or SAQ and any ASV reports. If something isn't in place, you have options before the report is final:
Consequences come from the card brands and your merchant agreement, not from PCI SSC. Its guide for small merchants lists financial penalties, lawsuits and losing the ability to accept cards as possible outcomes after a breach (Guide to Safe Payments). Then the cycle starts again, and next year's assessor will ask for the same evidence.
More PCI DSS guides for IT teams
Assessors sample the laptops, desktops and phones in scope, and each one has to match your configuration standard. trio.so is device management software that enforces and reports those device settings on Windows, Mac, iOS and Android from one console:
See how trio.so handles the device side of PCI DSS, area by area, with the evidence you can show your assessor.
trio.so does not assess, certify or validate PCI DSS compliance, and PCI SSC is clear that no single product can make an organization compliant (FAQ 1258). Your QSA, ISA or SAQ process validates compliance. Network security controls, logging, vulnerability scans, MFA, anti-malware and payment-page scripts need other tools and processes. Learn more about compliance automation.
Plans start at $5 per device.
14-day free trial. No credit card required.
For related work, see vulnerability management, third-party risk management and device encryption.
Sources. Last reviewed October 2026, against PCI DSS v4.0.1 (June 2024), the current version on 26 October 2026. This article is guidance, not legal or assessment advice; your acquirer, card brand and assessor have the final word. PCI DSS is © PCI Security Standards Council, LLC. Requirement numbers and titles are used for reference; descriptions are our own paraphrase. trio.so is not affiliated with or endorsed by PCI SSC.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
PCI compliance checklist for PCI DSS v4.0.1: the 12 requirements, the 51 future-dated items, CDE scoping and SAQ vs ROC, with a free PDF and Excel tracker.
Discover automated PCI DSS compliance tools - what they do, key features, and how to choose the right solution for your business needs.
PCI compliance for small business under PCI DSS v4.0.1: merchant levels, which SAQ you need, what drives the cost, and how PCI fines work for merchants.
Complete POS security guide covering threats, malware protection, mobile vulnerabilities, PCI DSS compliance, and implementation best practices.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients