



Explained
MDM vs. EMM vs. UEM: What Is the Difference?
MDM vs EMM vs UEM in one table: what each manages, how they differ from MAM, which one a small IT team needs, and how the categories evolved.
EMM explained: what enterprise mobility management covers (MDM, apps, content and identity), how it works on personal devices and how it relates to UEM.

Content writer, trio.so
EMM, short for enterprise mobility management, is the set of tools and policies a company uses to manage employees' mobile devices, the apps on them, the work content they hold and who can sign in. It grew out of mobile device management (MDM) and adds control of apps, documents and identity, so IT can protect work data on both company-owned and personal phones and tablets. Today EMM is usually part of a wider unified endpoint management (UEM) tool that also manages laptops and desktops.
If you met the term in a vendor comparison or an RFP and want to know what it covers and whether you need it, this guide gives you the definition, the four parts of EMM, how it works on personal devices and how it relates to MDM and UEM.
EMM stands for enterprise mobility management. "Enterprise" means it is built for organizations, "mobility" means phones and tablets used away from a desk, and "management" covers setting them up, securing them and taking work data back when needed. Vendors use "EMM system", "EMM solution" and "EMM platform" for the same thing: software that does this from one console.
An EMM solution combines four areas:
| Component | What it controls | Example |
|---|---|---|
| Mobile device management (MDM) | The device itself: enrollment, passcode, encryption, restrictions, Wi-Fi, lock and wipe | Requiring a six-digit passcode on every company phone |
| Mobile application management (MAM) | Work apps and their data, not the whole device | Installing the company CRM app and removing it when someone leaves |
| Mobile content management (MCM) | Work documents and files on the device | Letting staff open work files only in approved apps |
| Mobile identity management (MIM) | Who can sign in, with what, and to which apps | Single sign-on to work apps with multi-factor authentication |
MDM is the base layer. It enrolls the device, applies security settings and can lock or wipe it. On company-owned phones, MDM can control almost everything. For more, see mobile device management.
MAM manages apps rather than the device: which work apps are installed, how they are configured and what happens to their data. It is the part that makes personal devices workable, because IT can manage the work apps without touching the rest of the phone. See mobile application management.
MCM covers the work files themselves: where they can be opened, whether they can be shared and how they are removed. On modern phones much of this is handled by the operating system's separation of work and personal apps.
Identity decides who gets access. In practice this means signing in with a work account from a central directory, single sign-on to work apps and multi-factor authentication, so a lost password alone does not open the company's data.
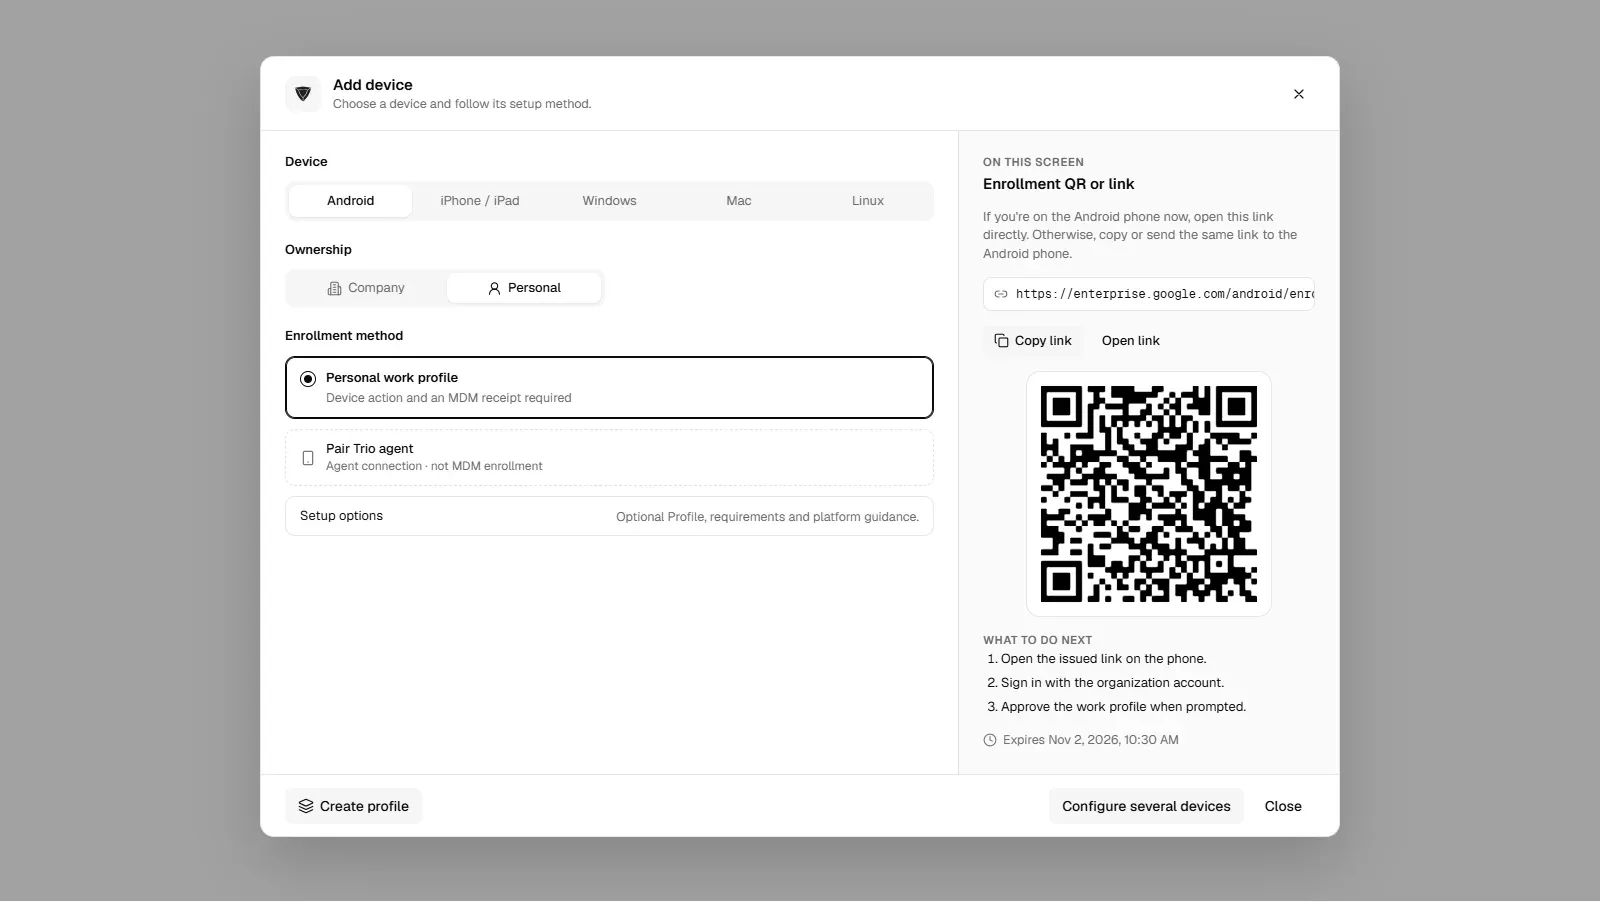
EMM treats company-owned and personal devices differently, and both Apple and Google build that difference into their operating systems:
This split is why EMM matters for companies that allow bring-your-own-device (BYOD). It protects work data without giving IT control over an employee's personal phone.
MDM manages the device. EMM adds app, content and identity controls on top of MDM, mainly for phones and tablets. UEM goes one step further and brings laptops and desktops into the same console, so Windows PCs, Macs and Linux machines are managed next to iPhones, iPads and Android devices.
Most tools sold as "EMM" or "MDM" today are really UEM, and for a small company with both laptops and phones, UEM is the category to look at. For the full comparison, see MDM vs. EMM vs. UEM and unified endpoint management.
Any organization where work data lives on phones or tablets: field teams, sales staff, frontline workers on shared devices, and any company that lets staff read work email on their own phones. If you only have a few company phones and no personal devices, basic MDM may be enough. Once personal devices, shared devices or more than a handful of apps are involved, you need the app and identity controls of EMM.
EMM features are found in most mobile and endpoint management products, including Microsoft Intune, Omnissa Workspace ONE, Samsung Knox Manage, SOTI MobiControl, and smaller UEM tools built for small and mid-sized teams. When you compare them, look past the label and check the four components above, which platforms each one actually supports and how it handles personal devices.
trio.so is unified endpoint management that includes EMM. It manages iPhones, iPads and Android devices, keeps work apps and data in a separate work profile on personal Android phones and removes it when the phone is unenrolled. On a personal iPhone or iPad, IT cannot erase, lock or locate the device and sees only the work apps it installed. It deploys apps and syncs users and groups from Google Workspace, Okta, Microsoft Entra ID and other directories. Plans start at $5 per device.
Enterprise mobility management: the tools and policies a company uses to manage mobile devices, their apps, work content and sign-in, on both company-owned and personal phones and tablets.
Enterprise mobility management.
MDM manages the device itself. EMM includes MDM and adds management of apps, content and identity, which makes it suitable for personal devices as well as company-owned ones.
No. UEM includes everything in EMM and also manages laptops and desktops, so every device type is in one console. Most products sold today are UEM.
Microsoft Intune, Omnissa Workspace ONE, Samsung Knox Manage and SOTI MobiControl offer EMM features, as do many UEM tools for smaller teams.
Related reading: MDM vs. EMM vs. UEM, mobile application management, Android work profile and unified endpoint management.
trio.so manages iPhones, iPads and Android devices, keeps work data in a separate work profile on personal Android phones and installs the apps each team needs.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
MDM vs EMM vs UEM in one table: what each manages, how they differ from MAM, which one a small IT team needs, and how the categories evolved.
Delve into the intricacies of Mobile Content Management (MCM) and its relationship with mobile device management systems.
Why Is EMM Important? Explore the significance of EMM in your business. EMM is the key to a competitive edge in the mobile business landscape.
Unlike full-device VPN, per-app VPN tunnels only the apps you choose — and without MDM enforcement, users can bypass it entirely on unmanaged devices.
What is SIEM integration, and how does it improve threat detection? Learn practical steps, tools, and tips for SMBs in this concise guide.
What is enterprise web content filtering, and why does it matter for SMBs? It protects users, boosts productivity, and simplifies IT management.
How to add an MDM server to Apple Business Manager, now Apple Business: upload the key, get the token, set defaults, assign devices, and when you need it.
Discover top 6 challenges in Active Directory Integration for Dynamic Access Management & learn how to overcome them with best solutions & practices.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients