



Explained
What Is Application Whitelisting and Why Is It Important?
Learn how application whitelisting enhances your business security. MDM simplifies implementation, protecting your devices and data efficiently.
App sideloading bypasses official app store protections, exposing devices to malware and data leaks. Learn the risks and how to manage them.

Content writer, trio.so
Sideloading means installing an app from somewhere other than the device's official app store, such as an APK file downloaded from a website on Android or an alternative marketplace on iPhone. The app skips the checks Google Play and Apple's App Store run before they list software. Sideloading itself is legal in most countries; what makes it risky is that nobody vetted the app.
Every time an employee installs an app from outside the official store, your organization takes on risk it may not know about.
On Android, sideloading has been possible since day one. On iPhones, Apple opened the door to it in the EU in 2024, after the Digital Markets Act required alternative app marketplaces, and in Japan in December 2025 under the Mobile Software Competition Act. For IT teams managing company devices, both platforms now demand attention.
This article covers the security risks of sideloaded apps, how sideloading works on Android and iOS, what Google's new developer verification rules mean, and how device management tools give you control.
When you download an app from Google Play or the Apple App Store, that app goes through automated malware scans, permission reviews, and content checks before it reaches your device. Sideloading skips all of that. You're downloading an APK file (on Android) or using an alternative marketplace (on iOS) to install software that hasn't passed those gatekeeping checks.
People sideload apps for all kinds of reasons. Developers use it to test builds before release. Businesses use it to distribute internal tools that don't belong on public stores. Some users sideload to access apps that aren't available in their region.
Sideloading as a mechanism is neutral. A developer testing a beta build and an attacker distributing malware use the exact same installation path. And once a device is compromised, everything on it (email, contacts, credentials, corporate data) is at risk. According to Zimperium's 2025 Global Mobile Threat Report, sideloaded apps are present on 23.5% of enterprise devices, and that number is climbing.
No, not in itself, in most countries. Installing an app from outside the official store is something Android has always allowed, and the EU and Japan now require Apple to allow it on iPhone through approved alternative marketplaces. What can be illegal is what you sideload: a pirated copy of a paid app breaks copyright law, and some apps break local laws whichever way they are installed. On a company device, your employer's policy may also forbid it, even where the law does not.
Sideloading cybersecurity risks go well beyond theoretical concerns. The threats are specific, documented, and hitting real organizations. If you manage devices for a business of any size, these are the risks your team needs to understand.
This is the biggest and most direct threat. Google's own analysis found over 50 times more malware in apps from internet-sideloaded sources compared to apps on Google Play. Malicious actors package banking trojans, spyware, and ransomware into APKs that look like legitimate tools. The Zimperium research team found that riskware and trojans account for 80% of the malware observed in sideloaded apps.
A sideloaded app can request permissions your users don't think to question. A flashlight app asking for access to contacts and files should raise flags, but outside the app store review process, no one is checking. The data those apps collect can end up on external servers before anyone notices.
Apps from official stores receive automatic security patches. Sideloaded apps don't. If a vulnerability is discovered in a sideloaded app, there's no built-in mechanism to push a fix. The app stays vulnerable until someone manually installs an update, and that rarely happens on time.
If your organization handles protected health information (HIPAA), payment card data (PCI DSS), or personal data under GDPR, sideloaded apps can put you out of compliance. An unvetted app accessing sensitive data creates an audit trail gap that regulators don't overlook.
Attackers take popular, trusted apps, inject malicious code into them, and redistribute the modified versions through third-party download sites. The app looks and works like the original, but it's silently exfiltrating data or logging keystrokes in the background.
Pirated versions of paid apps are a common reason people sideload. These cracked copies frequently carry embedded malware. Users think they're getting a free productivity tool. What they're really getting is a backdoor into their device.
Official stores verify developer identities, respond to abuse reports, and remove offending apps quickly. With sideloaded software, there's often no way to trace the developer. If the app causes harm, you have no recourse and no one to hold responsible.
| Risk Factor | Official App Store | Sideloaded App |
|---|---|---|
| Malware Screening | Automated scans + human review | None by default |
| Developer Identity | Verified and traceable | Often anonymous |
| Automatic Updates | Yes | Manual only |
| Permission Review | Checked before listing | No external review |
| Malware Removal | Remote removal possible | User must uninstall manually |
| Compliance Audit Trail | Documented and verifiable | Gaps in tracking |
| Accountability | Store can ban developers | No enforcement mechanism |
The mechanics of sideloading differ between Android and iOS, and both are changing fast.
Android has supported sideloading since its first version. How do you sideload apps on Android? You download an APK file from a website, file-sharing service, or direct link. Then you open the file, and Android prompts you to allow installation from that specific source. Starting with Android 8, this permission is granted per app rather than as a blanket device setting, which gives users slightly more control. Knowing how to sideload apps on Android is straightforward for end users, which is exactly why IT admins need controls in place.
Google Play Protect does scan sideloaded apps for known malware after installation. But this is reactive, not preventive. A brand-new malicious app with no detection history will pass through without a flag.
The biggest change for Android app sideloading is Google's developer verification requirement. Its protections took effect on 30 September 2026 in Brazil, Indonesia, Singapore and Thailand: on certified Android devices there, apps must come from verified developers, whether they come from the Play Store or are sideloaded. Google plans to extend this globally in 2027. Experienced users will still be able to install unverified apps through a high-friction flow designed to resist social engineering. Developers can still use ADB (Android Debug Bridge) for testing.
One thing to keep in mind: verification confirms who built the app, not what the app does. A verified developer can still ship software that requests excessive permissions, sends data to external servers, or violates your compliance requirements. That's the gap MDM fills, through allowlists, software policies, and compliance monitoring that evaluate app behavior on your devices, not just the identity behind the code.
For years, the answer to how to sideload apps on iPhone was simple: you couldn't, at least not without jailbreaking. Apple's closed ecosystem kept app installation limited to the App Store. IT teams never had to worry about third-party app sources on iOS devices.
That changed in March 2024. Under the EU's Digital Markets Act, Apple was forced to allow alternative app marketplaces on iOS 17.4 and later for users in the European Union. Sideloading apps on iOS is now possible there through approved third-party marketplaces, and developers can distribute apps directly from their websites too. Apple brought similar changes to Japan with iOS 26.2 in December 2025, to comply with the Mobile Software Competition Act.
Apple added safeguards: sideloaded iOS apps go through a "Notarization" process, marketplace developers must be authorized, and users see clear disclosures before installing. But notarization checks for malware signatures and basic threats. It doesn't evaluate app behavior after installation, flag apps that exfiltrate data to unauthorized servers, or catch excessive permission requests that are technically allowed under Apple's guidelines. For IT admins, that gap means you can't rely on Apple's notarization alone to protect corporate data on managed devices. Other countries are considering similar rules, so iPhone sideloading is something every IT team should plan for.
You need practical ways to manage sideloading across your device fleet. MDM (mobile device management) tools and a clear mobile device management policy are the foundation.
On Android, you can disable the "Install from Unknown Sources" setting fleet-wide through your MDM. On iOS, admins can turn off app installs from alternative marketplaces with an MDM restriction on supervised devices. These are the most direct defenses.
Rather than trying to block every possible threat, define which apps your organization approves. An allowlist means only those specific apps can run on managed devices. A blocklist prevents known risky apps from operating. Both approaches give you granular control without banning everything.
For organizations supporting bring-your-own-device programs, work profiles create a walled-off container for corporate apps and data. Even if an employee sideloads a questionable app on their personal profile, corporate data in the work profile stays isolated and encrypted.
One of the most common legitimate reasons for sideloading is distributing custom, in-house apps. The better approach is using Managed Google Play for Android or Apple's enterprise app distribution for iOS. These channels let you push private apps to devices through official store infrastructure. Your apps still get scanned by Play Protect or Apple's Notarization, and they remain private to your organization.
Technology alone won't stop sideloading. Your staff needs to understand why it matters. A well-documented mobile device management implementation plan should include clear rules about which app sources are approved, consequences for violations, and training that explains the risks in plain terms.
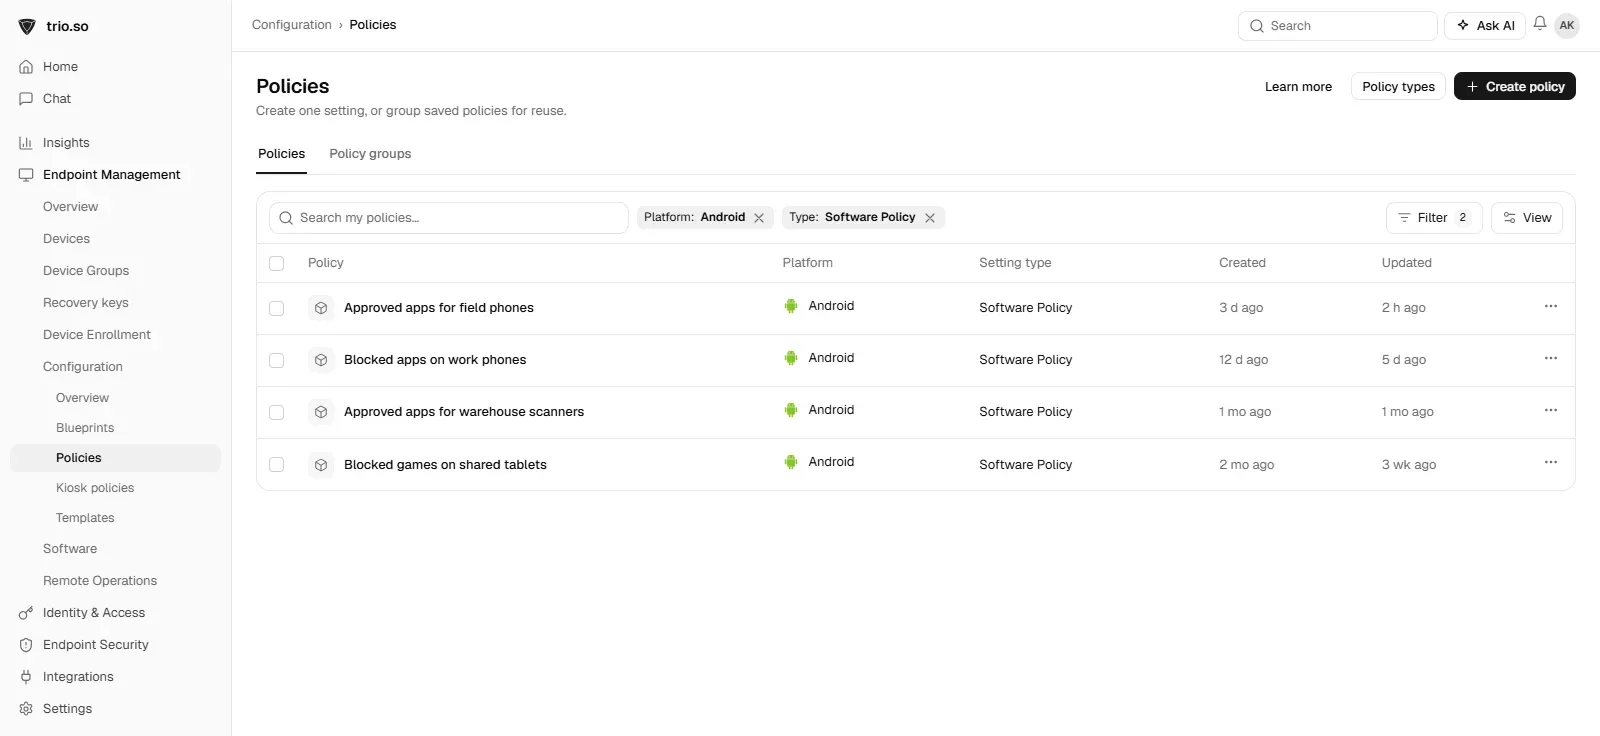
Blocking unknown sources and keeping a list of approved apps is policy work, not phone-by-phone work. trio.so can limit managed Android devices to approved apps with an allow list policy, or block specific apps with a block list. See Android device management, and the guides on whitelisting and blocking apps on Android.
App sideloading isn't going away. Android is making it safer with developer verification, and iOS is opening up to it under regulatory pressure. For IT admins, the question isn't if your users will encounter sideloaded apps. It's if you have the controls in place when they do.
The combination of a clear policy, employee training, and an MDM tool that gives you real enforcement is what separates organizations that stay secure from those that learn about the risks the hard way. Start by auditing your fleet for sideloaded apps, then build the policies and tools to keep your devices and data protected.
Related reading: how to block apps on Android, how to whitelist an app on Android and mobile application management.
trio.so can limit managed Android devices to approved apps with one policy.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Learn how application whitelisting enhances your business security. MDM simplifies implementation, protecting your devices and data efficiently.
What application blacklisting (blocklisting) is, how it compares with allowlisting, where it works and fails, and how to block apps across devices.
Are you ready to shield your systems? Windows Defender Application Control enforces strict allowlisting policies to combat modern cyber threats.
Device lockdown locks the whole device to approved apps; browser lockdown locks only a browser to approved sites. When to use each, by platform.
How to lock a Fire tablet to one app: what Fire OS can do on its own, when you need a kiosk app or MDM, and how Fire OS differs from Android.
What enterprise software is, examples, and how IT manages it across company devices: inventory, deployment, updates, install control and licenses.
Interactive kiosk software boosts user interaction and operational efficiency, with MDM solutions like trio.so enhancing these advantages further.
Lock an iPad or iPhone to one app with Single App Mode, Guided Access or Autonomous Single App Mode, and set up iPad kiosk mode across a whole fleet.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients