



Explained
Enterprise Software Management: What It Is and How IT Handles It
What enterprise software is, examples, and how IT manages it across company devices: inventory, deployment, updates, install control and licenses.
How to deploy an application to many devices: manual installs, imaging, scripts and Group Policy, or MDM, and what each platform needs to roll out.

Content writer, trio.so
Application deployment, for IT teams, means getting the same apps installed, configured and kept up to date on many company laptops, desktops and phones without installing each one by hand. There are four ways to do it: install manually, build the apps into a disk image, push installers with scripts, Group Policy or Configuration Manager, or use a mobile device management (MDM) or unified endpoint management (UEM) tool with an app catalog. Each platform needs its own package type: MSI or the Windows Package Manager (winget) on Windows, App Store apps and PKG or DMG installers on Macs, App Store apps with Apple Business licences on iPhones and iPads, and managed Google Play on Android.
If you have a few apps to get onto a growing number of laptops and phones, the comparison table and the per-platform section give you the short answer; the rest of the post covers how to roll out without breaking anything. (This post is about devices; deploying code to servers or the cloud is a different job.)
Application deployment, often called software deployment, is the process of delivering an app to the devices that need it: installing it silently, applying its settings, keeping it updated and removing it when it is no longer needed. In developer teams the same term means releasing code to servers through a pipeline; for IT, it means the apps on employees' devices.
A deployment has four parts: the package (the installer in a format the platform accepts), the targets (which devices or users get it), the method that delivers it, and the report that tells you where it installed and where it failed.
Deploying apps centrally instead of installing them by hand pays off in four ways:
Someone downloads the installer and runs it on each device, or the user does it themselves. It needs no tools and is fine for a handful of devices, but it does not scale, versions drift apart, and users often need administrator rights to install, which is a security risk of its own (see Mac administrator accounts).
IT builds a reference machine with the operating system and standard apps, captures it as a disk image and copies that image to new computers. Every device starts identical, but the image goes out of date the moment it is captured, needs maintaining for each hardware model, and only covers apps present on day one. Modern Macs do not support traditional imaging, and on Windows most teams have moved to setting up the manufacturer's installation automatically instead (see zero-touch deployment). Imaging still has a place for labs and specialized machines.
On Windows, apps can be pushed silently from a central place:
msiexec /i app.msi /qn for an MSI, or the Windows Package Manager.To install an app with the Windows Package Manager, for example:
winget install --id 7zip.7zip --silent --accept-package-agreements --accept-source-agreementsOn Macs, the equivalent is a script that runs sudo installer -pkg /path/App.pkg -target /. These methods work well for computers on the office network, and less well for laptops that rarely come in, or for phones.
A mobile device management or unified endpoint management tool keeps a catalog of approved apps and installs them on enrolled devices over the internet, wherever the device is. It works for laptops, desktops, phones and tablets, reports install status per device, updates apps and removes them when a device leaves. This is the method most small and mid-size IT teams use today, especially with remote staff. See mobile device management.
Application virtualization and streaming, where apps run from a server or a container instead of being installed, is a fifth option some organizations use for a few legacy apps; for most fleets it is a specialist tool rather than the main method.
| Method | Best for | Platforms | Effort |
|---|---|---|---|
| Manual installation | A few devices, one-off installs | Any | High per device |
| Imaging | Labs, identical hardware | Mainly Windows | High to maintain |
| Scripts, Group Policy, Configuration Manager | Domain-joined Windows PCs in the office | Windows (scripts on Mac too) | Medium, needs the network |
| MDM or UEM with an app catalog | Mixed fleets, remote staff, phones | Windows, Mac, iPhone, iPad, Android | Low once set up |
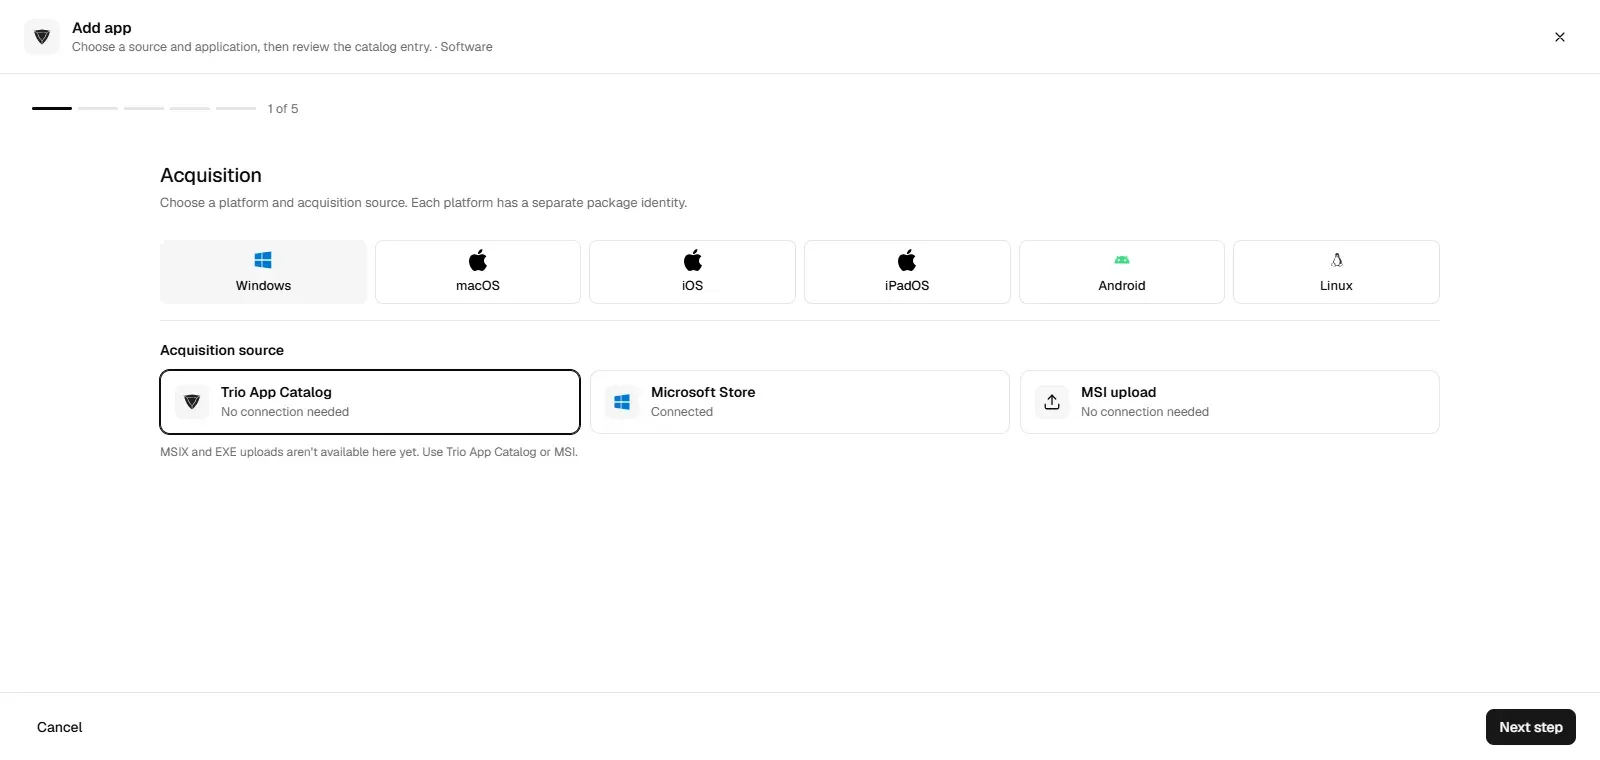
trio.so deploys apps to Windows, Mac, iPhone, iPad and Android devices from one console: catalog apps and MSI installers on Windows, App Store apps and uploaded installers on Macs, App Store apps licensed through Apple Business on iPhones and iPads, and managed Google Play apps on Android. Nobody has to install them by hand. See mobile device management.
Manual installs and imaging still have their place, but for a fleet of laptops and phones, especially with remote staff, an MDM or UEM with an app catalog is the method that keeps up. Whatever you use, package the app properly, target groups instead of devices, test on a pilot group, roll out in stages and check the install report.
Related reading: managed Google Play, Apple VPP token, zero-touch deployment and patch management.
trio.so installs apps on Windows PCs, Macs, iPhones, iPads and Android devices from one catalog, so nobody installs them by hand.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
What enterprise software is, examples, and how IT manages it across company devices: inventory, deployment, updates, install control and licenses.
What is mobile application management? MAM controls company apps and data without managing the whole device. See how it works, and how it differs from MDM.
This guide delves into the importance of Over-The-Air update solutions for IT administrators, their components, and their implementation process.
What an application catalog is, what belongs in one, how it delivers apps to Windows, Mac, iPhone, iPad, Android and Linux, and how self-service works.
Software upgrade best practices for IT teams: update vs upgrade, a pre-upgrade checklist, staged rollouts, backups and rollback, and OS feature upgrades.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients