



Templates
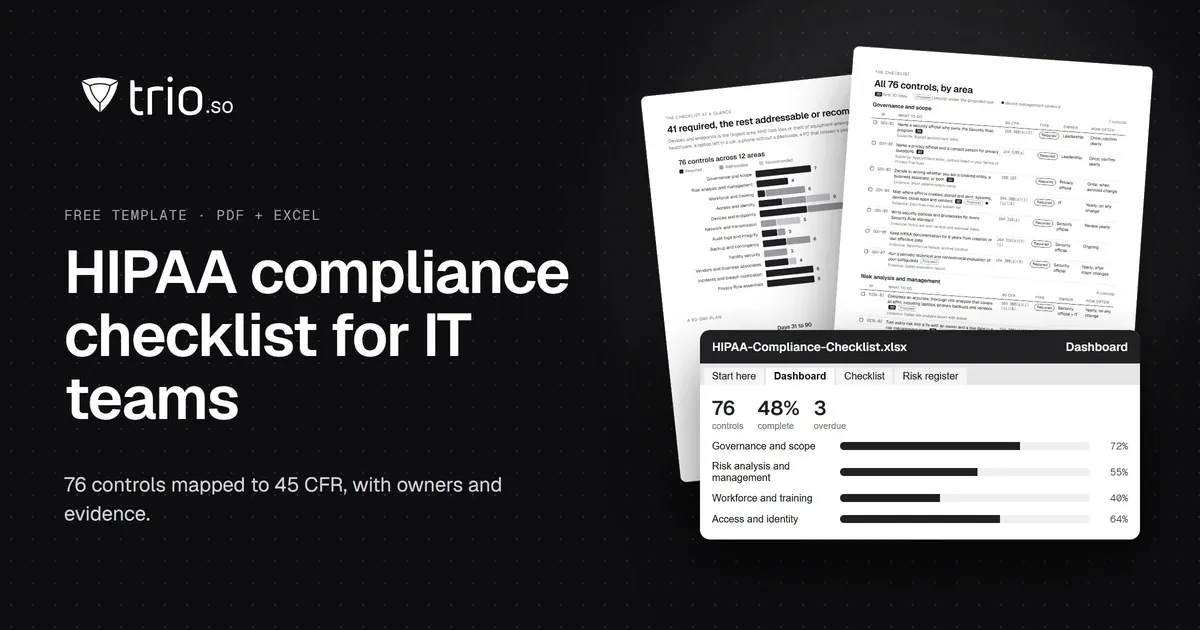
HIPAA Compliance Checklist for IT Teams (PDF + Excel)
A HIPAA compliance checklist for IT teams: 76 controls mapped to 45 CFR, each with the evidence auditors ask for. Free PDF and Excel tracker.
Use this guide for everything you need to know about the HIPAA Minimum Necessary Standard and how IT professionals can ensure compliance in protecting PHI.

Content writer, trio.so
Protecting patient privacy in healthcare has become more than just an ethical requirement—it's the law. The Health Insurance Portability and Accountability Act (HIPAA) lays down clear guidelines for how Protected Health Information (PHI) must be handled. Among these, the HIPAA minimum necessary standard stands out as a critical aspect of ensuring data privacy and security. But what does this standard really mean, and how does it apply in an IT context? In this blog, we'll break down the HIPAA minimum necessary standard in terms that make sense for IT professionals. We will define it, explore its applications, and provide practical examples. By the end, you'll know exactly how this standard fits into your IT compliance strategy and we'll offer a solution that can streamline your efforts.
The HIPAA minimum necessary standard is designed to ensure that only the minimum amount of protected health information (PHI) required to accomplish a specific task is disclosed. This standard applies to all covered entities, including healthcare providers, health plans, and business associates. When we define this standard, it’s important to note that it applies primarily to the disclosure and use of PHI in situations that don't involve treatment. For example, disclosures for payment purposes, health care operations, and requests for protected health information must adhere to this standard. Notably, HIPAA includes the minimum necessary standard to limit the access and exposure of sensitive medical information, safeguarding patient privacy. The rule requires that entities take reasonable steps to ensure that only individuals with a legitimate need to access PHI are granted access. 
It's essential to understand the scope of where the HIPAA minimum necessary standard applies. It governs the release of PHI in most scenarios, except for a few key exceptions. Specifically, the minimum necessary standard does not apply to:
The HIPAA minimum necessary standard applies to situations such as health care operations, requests for protected health for payment, and for disclosures to or requests by other entities that perform tasks on behalf of the covered entity, such as claims processing or IT support.
A common question from IT professionals is, "How does this standard apply in a practical, day-to-day setting?" Let’s explore some Minimum Necessary Rule examples:
Another critical area where the HIPAA minimum necessary standard applies is in human subject research. When researchers access protected health information (PHI) for studies, the rule restricts them to accessing only the types of PHI that are necessary for their research, and no more. This means they can't collect full medical records unless absolutely essential to the study. The HIPAA minimum necessary standard applies here to balance patient privacy with scientific progress. By limiting access to only the required medical data, the law safeguards patient confidentiality while allowing researchers to carry out vital studies. 
To further strengthen your organization’s HIPAA compliance strategy, it’s important to consider broader compliance frameworks that may overlap with HIPAA requirements. For instance, SOC 2 Compliance provides guidelines for security, availability, processing integrity, confidentiality, and privacy, all of which align well with HIPAA's focus on safeguarding PHI. Moreover, integrating NIST Compliance can help strengthen your organization's security posture, particularly through standards that support data protection and cybersecurity controls. If your organization handles email communication involving PHI, adhering to email compliance is another key area that should not be overlooked, especially when encrypting sensitive patient information. Finally, investing in compliance training and using a HIPAA compliance checklist can ensure that all team members—from IT professionals to healthcare providers—are well-prepared to handle PHI properly under HIPAA's minimum necessary standard. A thorough checklist helps identify gaps in compliance and ensures that no essential requirements are missed.
Maintaining compliance with HIPAA's minimum necessary requirement can be challenging, especially when managing vast amounts of sensitive data. This is where an MDM solution like trio.so can make a significant impact. trio.so helps organizations ensure that the minimum necessary standard HIPAA privacy rule is met by providing enhanced data control capabilities. Through trio.so's solution, IT administrators can:
By integrating trio.so into your healthcare IT infrastructure, you can ensure that the minimum necessary standard HIPAA privacy rule is adhered to, while still maintaining operational efficiency. Want to learn more? Try out trio.so with a free demo today.
More HIPAA guides for IT teams
In summary, the HIPAA minimum necessary standard is a cornerstone of patient privacy protection. It requires that covered entities take proactive steps to limit the disclosure of protected health information (PHI) to the minimum necessary for accomplishing specific tasks, while still allowing the necessary exchange of medical data for operations and compliance. For IT professionals, understanding the nuances of this standard and implementing tools like trio.so can ensure compliance while safeguarding sensitive medical information. As you work to align your systems with HIPAA requirements, be mindful of how access is controlled and the type of data shared.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
A HIPAA compliance checklist for IT teams: 76 controls mapped to 45 CFR, each with the evidence auditors ask for. Free PDF and Excel tracker.
How to do a HIPAA risk assessment in 8 steps: scope, inventory, threats, scoring and the risk management plan. Free Excel worksheet with 21 starter risks.
HIPAA technical safeguards are the 5 standards in 45 CFR 164.312. What each one requires, required vs addressable, and the device settings that meet it.

HIPAA compliance and cell phones is possible, but SMS, unmanaged BYOD, and unencrypted devices create real exposure most teams overlook.

HIPAA compliance for SMBs requires administrative, physical, and technical safeguards. Learn how to protect patient data, and avoid costly penalties.
Discover the 7 key differences between HITRUST and HIPAA in this comprehensive guide. Learn about HITRUST vs HIPAA certification and requirements.

Explore HIPAA violation fines and penalties, their impact on healthcare organizations, and how to ensure compliance while protecting patient privacy.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients