



Templates
Application Access Request Form Template (Word, Excel + PDF)
Free application access request form in Word and PDF, with a change and removal form, a filled-in example and an Excel log that flags expired access.
Free IT offboarding checklist with an Excel tracker: access removal, device return and wipe, admin and BYOD steps, plus sample offboarding emails.

Content writer, trio.so
An IT offboarding checklist is the list of steps IT follows when someone leaves: remove their access to every system, collect and wipe their devices, hand their data to a new owner and record that each step was done. It turns "we think their access is gone" into dates you can show.
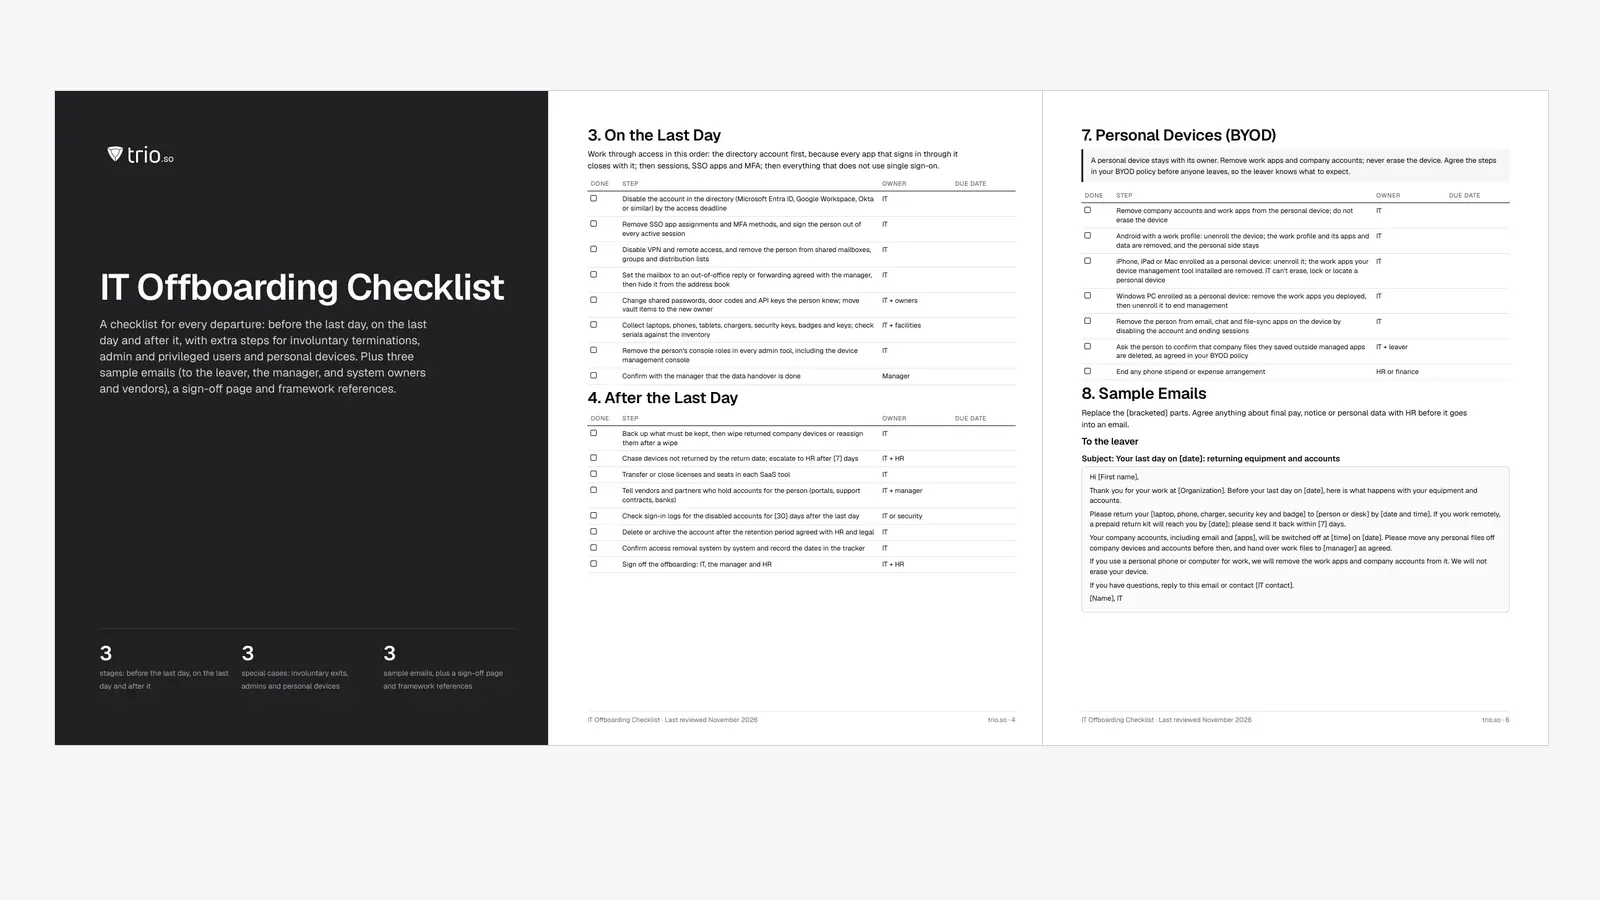
This free template gives you a checklist in PDF and Word with steps for before the last day, the last day itself and the weeks after, plus extra steps for involuntary terminations, admins and personal devices, three sample offboarding emails and a sign-off page. An Excel tracker follows every leaver, system and device, and flags access still on after the deadline, devices that have not come back and leavers with no data owner.
In short
Offboarding is shared work. HR owns the employment side: notice, final pay, benefits and the exit interview. IT owns accounts, devices, data and the evidence that all of it was closed. The handoff happens when HR tells IT the name, the last day and the type of departure, and everything in this template starts from that message.
The IT side has four parts, and each one is a security control as much as an admin task:
Our overview of onboarding and offboarding covers the whole employee lifecycle, and the guide to employee offboarding automation looks at connecting HR and identity systems so fewer steps depend on memory. This post is the IT team's checklist. Its twin for new starters is the IT onboarding checklist, so what you hand out on day one is what you take back at the end.
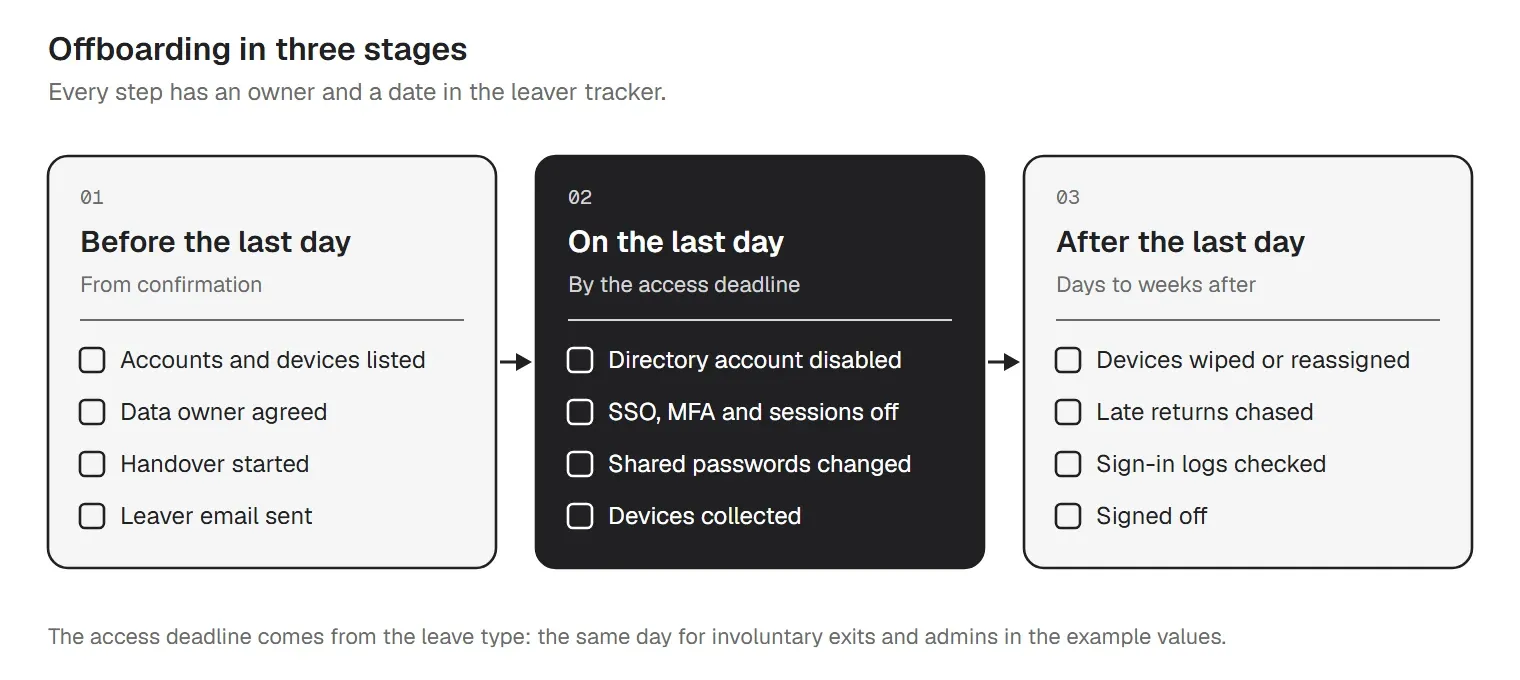
A departure is a short project with a fixed end date. The template splits it into three stages, each with an owner for every step:
| Stage | When | Main steps |
|---|---|---|
| Before the last day | From the moment the departure is confirmed | Inventory accounts and devices, agree the data owner, start the handover, send the leaver email |
| On the last day | By the access deadline | Disable the directory account, end sessions, remove SSO and MFA, change shared passwords, collect devices |
| After the last day | Days to weeks after | Wipe or reassign devices, chase late returns, transfer licenses, check sign-in logs, sign off |
The access deadline matters most. The workbook sets it from the leave type: in the example values, the day after the last day for voluntary departures and contract ends, and the same day for involuntary exits and admins. NIST SP 800-53 control PS-4 asks organizations to disable access within a time period they define, so write your number down.
Most offboarding mistakes are planning mistakes: an account nobody knew about, a laptop nobody asked for. Use the days before the last day to build the list:
The workbook's systems checklist helps with the third step: each system a leaver may use, how to remove access, its owner, whether it signs in through SSO and what evidence to keep. Fill it once, and every offboarding starts from the same list. Take the device list from your inventory with serial numbers; our guide to device inventory management covers keeping it current.
Most access hangs off one account. Disable the directory account first, and every app that signs in through single sign-on closes with it. Then deal with the rest:
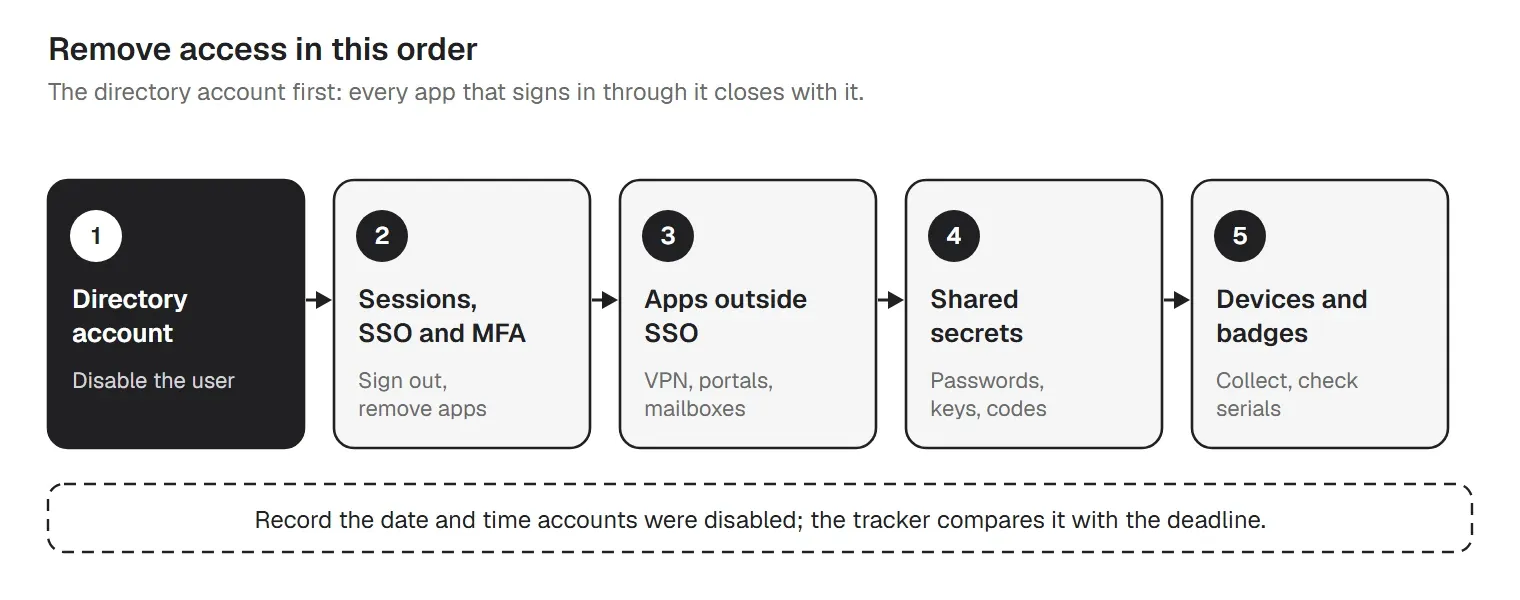
This is the offboarding security checklist auditors care about. The tracker stores the date and time each leaver's accounts were disabled and compares it with their deadline. A row shows Access still on once the deadline has passed with no date recorded, and Disabled late if the date came after it. If you use SCIM, check that deprovisioning reached each connected app (deprovisioning in cybersecurity covers the gaps). For mail and Drive ownership, see our Google Workspace offboarding guide.
Every company device a leaver had should come back, be backed up if needed, and be wiped before it goes to someone else. The workbook's device return log has one row per device, with the serial number, ownership, the date it came back and what happened to it: wiped, reassigned after a wipe, retired or kept by agreement. Pick the leaver's name and the log fills in their last day and the return date, then flags devices that are not back in time and returned devices still waiting for a wipe.
A wipe is the step that protects the data on a device you can't recover, and the step that makes a returned device safe to hand on. For phones and laptops under device management, a remote wipe resets the device to factory settings; our guide to remote wiping a mobile device explains how it works per platform. NIST SP 800-88 Rev. 2 counts a factory reset as a clear technique for many devices, and drives that leave your control need a method that fits the data, which our asset disposal policy template covers. Record each device's status in your inventory too, as your IT asset management policy describes.
Before you wipe, back up what must be kept, including anything legal or HR asked you to hold. Ask HR and legal how long to keep a leaver's data; it depends on your contracts and local law, so the template leaves it as a value to fill in.
A personal phone or laptop goes home with its owner, so the goal is to remove company access and work apps without touching anything personal. What that looks like depends on how the device was enrolled:
| Device | What unenrolling does | What IT can't do |
|---|---|---|
| Android with a work profile | Removes the work profile with its apps and data. The personal side of the phone stays. | See or erase the personal side. |
| iPhone, iPad or Mac enrolled as personal | Removes the work apps your device management tool installed and ends management. | Erase, lock or locate the device. |
| Windows PC enrolled as personal | Ends management of the work apps and updates; remove the work apps you deployed before you unenroll. | Erase the device. |
Disabling the person's accounts and ending their sessions also closes email, chat and file-sync apps on the device. Ask the leaver to confirm that company files they saved outside managed apps are deleted, as your BYOD policy should say, and end any phone stipend. Our guide to the Android work profile explains how the work profile keeps work apps and data separate from the personal side of an Android phone. Write these steps into the policy before anyone leaves, so the leaver knows what to expect.
When someone is dismissed, or leaves on bad terms, the timing changes. Access goes during the termination meeting, not after it. HR gives IT the date and time of the meeting in advance, and only the people who need it know. The template's steps for this case:
In the workbook, an involuntary leave type sets a same-day deadline, so any delay shows up at once. Keep the record factual and dated in case the departure is disputed later.
An administrator can change systems, create accounts and read most data, so their offboarding is the one to get right. A checklist for IT administrator termination adds these steps to the standard ones:
The step people miss is access the admin created rather than was given: a service account, an API key or a mail rule in their name. In the tracker, marking a leaver as privileged sets the privileged deadline from Settings (the same day in the example values) whatever their leave type. Our access control policy template sets the rules for privileged accounts in the first place.
The last day is not the end. The steps after it close the loose ends and produce the record:
The tracker counts the closing steps still open for each leaver after the last day (MFA and SSO removed, shared passwords rotated, data handed over, access removal confirmed). A row turns to Ready for sign-off when no flag and no open step is left, and to Closed once you enter the sign-off date. Periodic access reviews catch anything the offboarding missed; our user access review template runs them system by system.
Three emails cover most departures. Replace the bracketed parts, and agree anything about pay, notice or personal data with HR first. The same text is in the PDF, the Word file and the workbook.
Send it once the departure is confirmed: what to return, when access ends and what happens to their files.
Subject: Your last day on [date]: returning equipment and accounts
Hi [First name],
Thank you for your work at [Organization]. Before your last day on [date], here is what happens with your equipment and accounts.
Please return your [laptop, phone, charger, security key and badge] to [person or desk] by [date and time]. If you work remotely, a prepaid return kit will reach you by [date]; please send it back within [7] days.
Your company accounts, including email and [apps], will be switched off at [time] on [date]. Please move any personal files off company devices and accounts before then, and hand over work files to [manager] as agreed.
If you use a personal phone or computer for work, we will remove the work apps and company accounts from it. We will not erase your device.
If you have questions, reply to this email or contact [IT contact].
[Name], IT
It asks for the data owner, unlisted accounts and the mailbox decision in one go.
Subject: Offboarding [Name]: what we need from you by [date]
Hi [Manager name],
[Name]'s last day is [date] ([voluntary / involuntary / contract end]). To close their IT offboarding on time, please confirm the following by [date]:
1. Who takes over their files, mailbox, projects and recurring tasks.
2. Any systems, vendor portals or shared accounts they use that are not on the attached list.
3. Whether their mailbox should forward to someone, and for how long (we will confirm the period with HR).
4. That the knowledge handover is complete, on or before the last day.
Access will be removed at [time] on [date]. Devices are due back by [date].
Thanks,
[Name], IT
For systems outside single sign-on and accounts held by vendors, ask for removal and a confirmed date.
Subject: Remove access for [Name], effective [date and time]
Hello,
[Name] ([email address], [role]) leaves [Organization] on [date]. Please remove their access to [system or service] effective [date and time], including any API keys, shared logins or support contacts in their name.
Please transfer anything they own in [system] to [new owner, email].
Reply to confirm when the access has been removed, so we can record the date. Ticket: [ID].
Thank you,
[Name], IT, [Organization]
For the rules on a leaver's mailbox after they go, see our terminated employee email policy.
Auditors test offboarding by sampling: they take the HR list of leavers and ask, for a few names, when each account was disabled and whether the devices came back. The checklist lines up with these references:
| Framework | What it asks for at offboarding |
|---|---|
| ISO/IEC 27001:2022 Annex A | 5.11 Return of assets, 5.18 Access rights, 6.5 Responsibilities after termination or change of employment, 8.10 Information deletion. |
| NIST SP 800-53 Rev. 5 | PS-4 Personnel Termination: disable access within a set time, revoke credentials, hold an exit interview, retrieve property and keep access to the person's information. PS-5 covers transfers. |
| SOC 2 | CC6.2 and CC6.3: remove credentials and access when they are no longer authorized. |
| NIST SP 800-88 Rev. 2 | Clear, purge or destroy data on devices before reuse or disposal. |
A tracker with a dated row per leaver answers that sample quickly. The mapping in the PDF and Word file is a general guide: your audit scope and your auditor decide what counts.
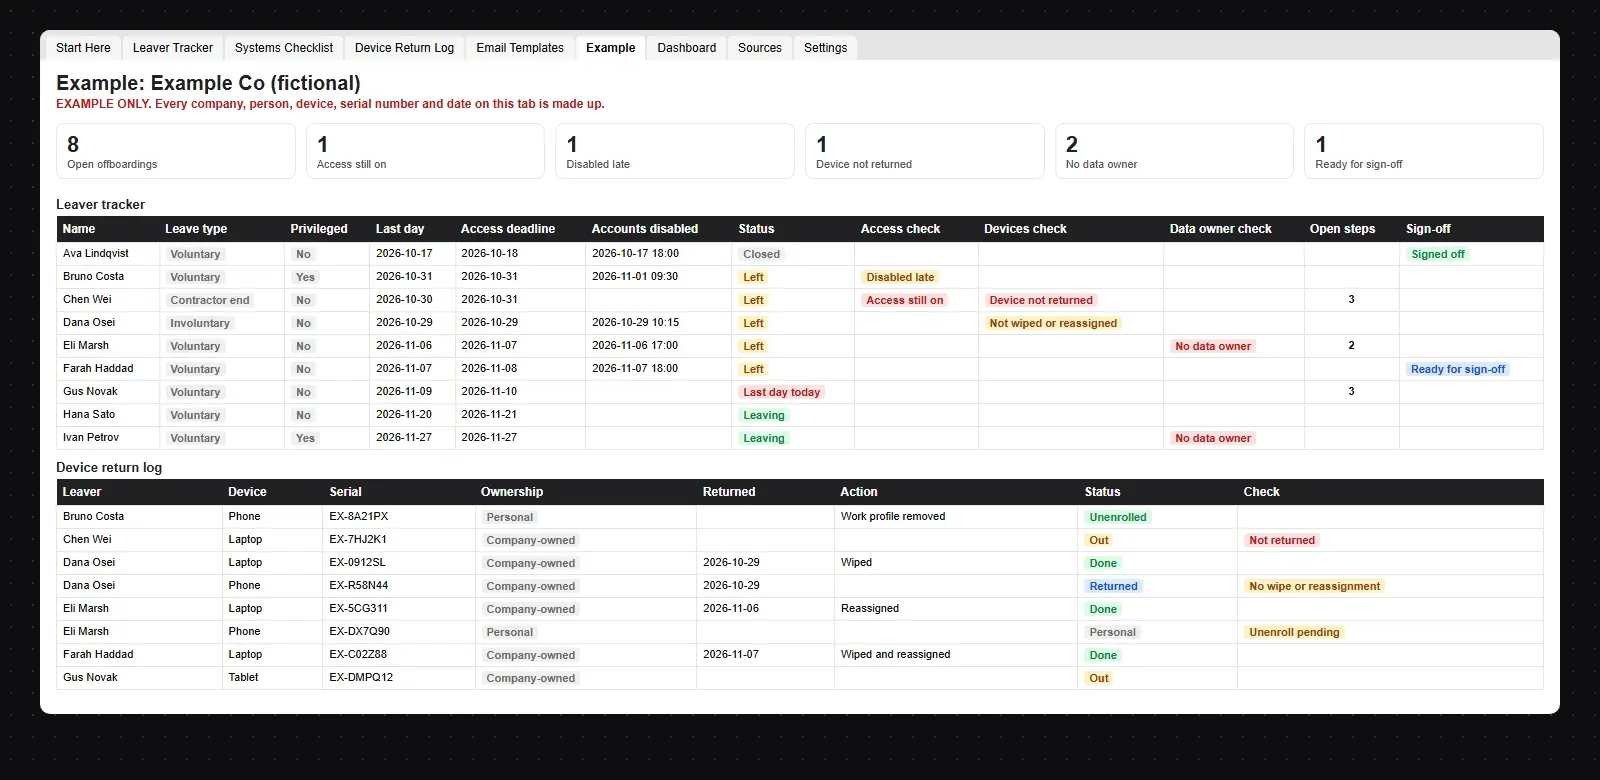
The example shows a made-up company with 9 leavers and 14 devices, including a contractor whose access is still on and whose laptop is missing, an admin disabled a day late, a phone waiting for a wipe and a personal iPhone still to unenroll.
trio.so does not run an offboarding workflow or approval chain: the checklist and the workbook carry the steps and the sign-offs. It covers the identity and device steps of the checklist. For those steps, trio.so gives you:
It covers Windows, macOS, Linux, iOS/iPadOS and Android from one console. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026. Framework names, control numbers and titles are used as references only; the checklist wording, formulas and example are ours. trio.so is not affiliated with or endorsed by ISO, NIST or the AICPA.
trio.so syncs users from your directory with SCIM 2.0 deprovisioning, shows each device's owner and serial number, wipes company-owned devices and unenrolls personal ones without erasing them.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Free application access request form in Word and PDF, with a change and removal form, a filled-in example and an Excel log that flags expired access.
A free IT budget template in Excel with a PDF guide: 11 cost categories, a worked 50-person example, and how to plan, forecast and track your IT budget.
A free IT maintenance schedule in Excel and an IT maintenance plan in Word and PDF: 17 tasks by frequency with owners, a checklist and notice email templates.
Free knowledge transfer plan in Word and PDF with an Excel tracker: KT timeline, handover document per system, checklist and a filled-in IT example.
Discover how a comprehensive Internet Usage Policy can safeguard your organization's security and productivity with our detailed guide.
Free IT onboarding checklist for new hires: accounts, access, device setup, day-one sign-in, apps, training and the first 30 days, in Excel, PDF and Word.
Free BYOD policy template with sample language for every section, a one-page simple version, a consent form and an Excel device register (Word + PDF).
Free remote work policy in Word and PDF: eligibility, a device security baseline, Wi-Fi and VPN rules, forms, a self-check and an Excel tracker.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients