



Templates
Social Media Policy Template for Employees (Free Word)
Free social media policy template for employees in Word and PDF: personal and official accounts, account security and a hacked-account checklist.
Free remote access policy template in Word and PDF: approved methods, RDP and MFA rules, vendor access, logging, an acknowledgment form and an Excel register.

Content writer, trio.so
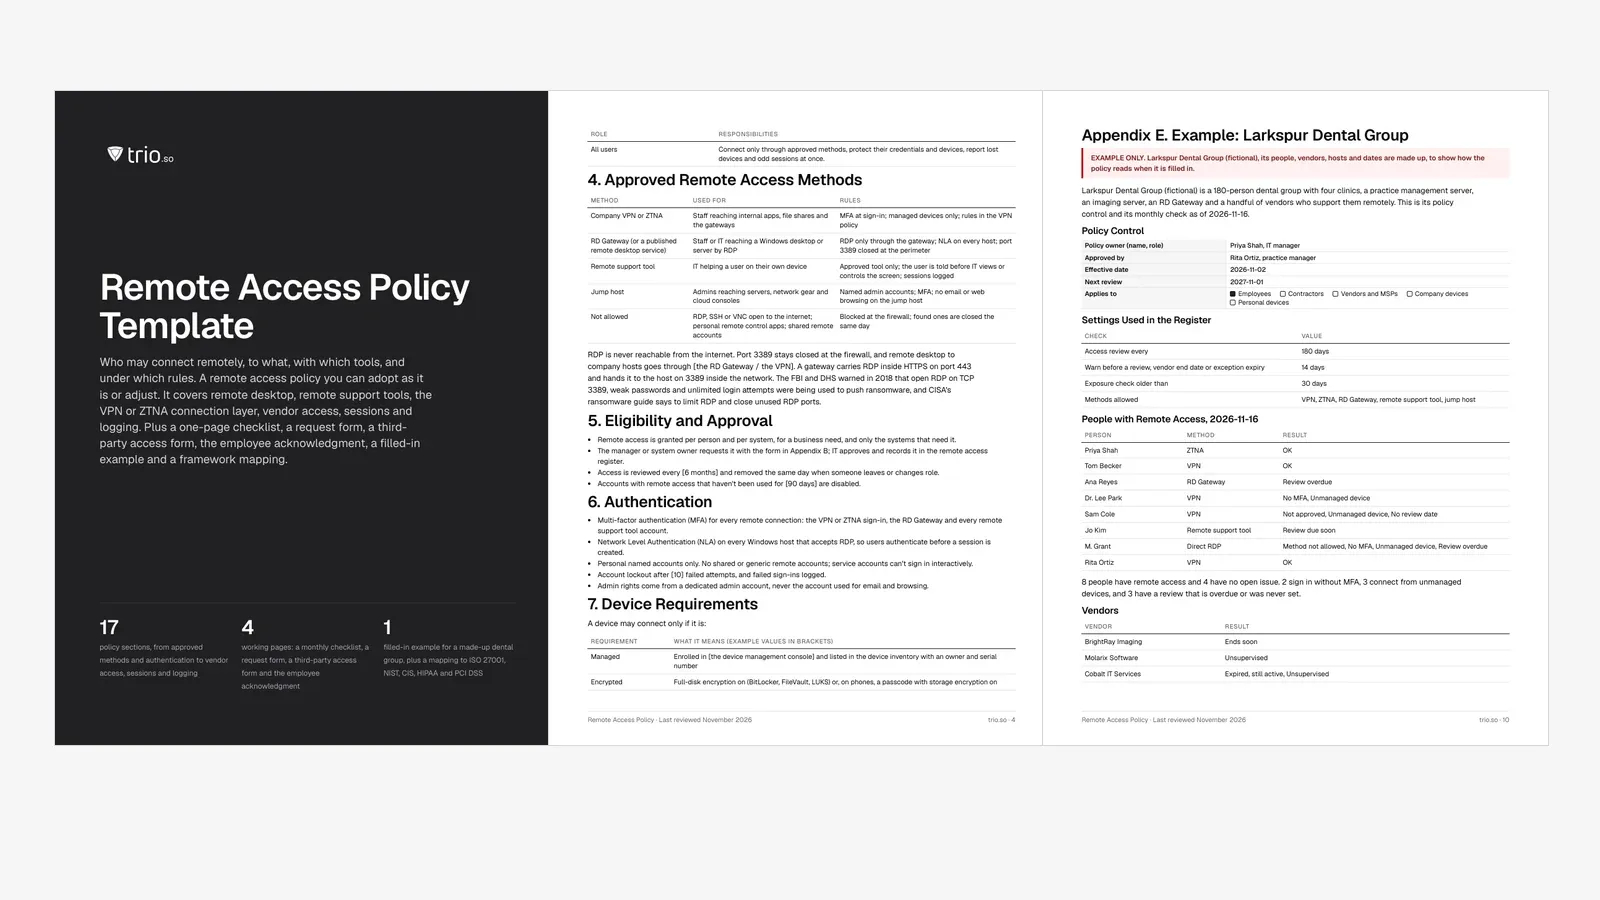
A remote access policy template gives you a written rule set for everyone who connects to company systems from outside the office: staff on remote desktop, IT on a remote support tool, admins on servers, and vendors who log in to fix the software they sold you. It says which methods are allowed, how people sign in, which devices may connect, what happens during a session, how vendor access is time-boxed and what gets logged.
This guide goes through each part for an IT manager or security lead at a company of 20 to 1,000 people, writing or updating remote access rules for ISO 27001, SOC 2, HIPAA, PCI DSS or a cyber insurance renewal. The download has the policy in Word and PDF, a one-page checklist, a request form, a third-party access form, the employee acknowledgment form, a filled-in example and an Excel register.
In short
A remote access policy is the document that decides who may reach company systems from outside the network, what they may reach and how. Some companies call it a remote access security policy or a remote access control policy; older templates, including the earlier version of this one, call it a remote desktop access policy because RDP was the main way in. The rules now cover more than RDP: the VPN or zero trust layer people connect through, the remote support tools IT uses on users' laptops, admin access to servers and cloud consoles, and vendor access.
Three other documents sit next to it. The VPN policy sets the rules for the VPN itself (clients, protocols, split tunneling). The access control policy decides who may open which data once they are in. The remote work policy covers working from home in general: hours, equipment, expenses. The remote access policy is the one that governs the connection itself.
Start from what you actually run. If a vendor connects through its own remote tool today, write that down and either allow it with an exception or replace it before the policy takes effect.
The template has 17 sections: purpose; scope and definitions; roles; approved remote access methods; eligibility and approval; authentication; device requirements; session rules; third-party and vendor access; privileged remote access; VPN and the connection layer; logging and monitoring; personal devices; lost or stolen devices; exceptions; enforcement; and review. Four forms follow: a monthly checklist, a remote access request, a third-party access form and the employee acknowledgment.
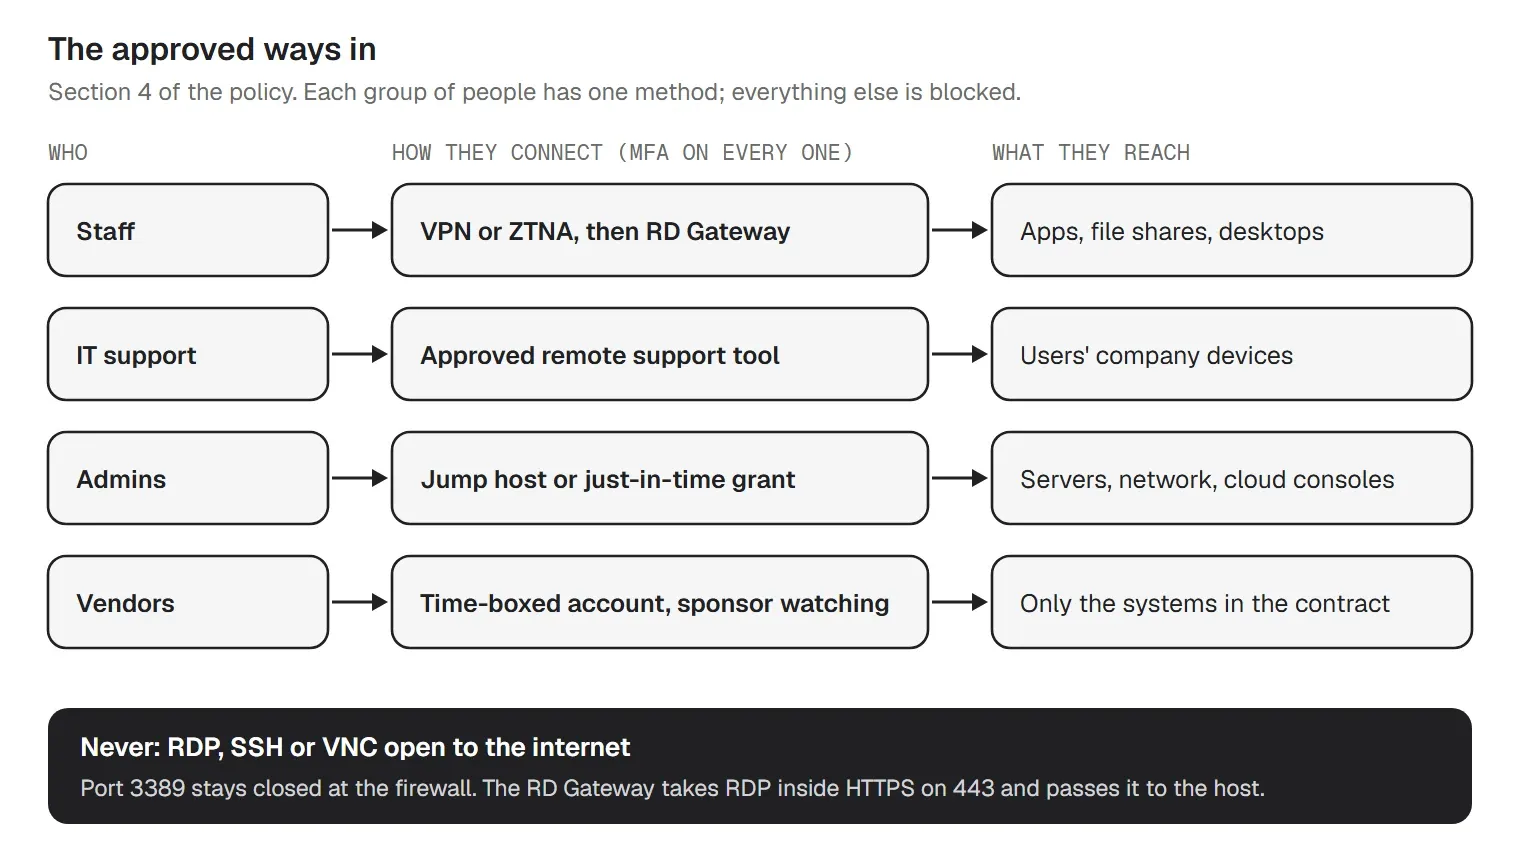
Section 4 lists each approved method, what it is for and its rules:
| Method | Used for | Rules |
|---|---|---|
| Company VPN or ZTNA | Staff reaching internal apps, file shares and the gateways | MFA at sign-in; managed devices only; rules in the VPN policy |
| RD Gateway (or a published remote desktop service) | Staff or IT reaching a Windows desktop or server by RDP | RDP only through the gateway; NLA on every host; port 3389 closed at the perimeter |
| Remote support tool | IT helping a user on their own device | Approved tool only; the user is told before IT views or controls the screen; sessions logged |
| Jump host | Admins reaching servers, network gear and cloud consoles | Named admin accounts; MFA; no email or web browsing on the jump host |
| Not allowed | RDP, SSH or VNC open to the internet; personal remote control apps; shared remote accounts | Blocked at the firewall; found ones are closed the same day |
The banned row is there for a reason. In 2018 the FBI and DHS warned that attackers were getting into companies through RDP left open on TCP port 3389, helped by weak passwords and unlimited login attempts, and were using that access to deploy ransomware. CISA's #StopRansomware Guide still lists limiting RDP and closing unused RDP ports among its first steps. A Remote Desktop Gateway solves the access problem without the exposure: users connect to the gateway over HTTPS on port 443, sign in with MFA, and the gateway passes the session to the host inside the network.
Pick one remote support tool and run it from your managed console. If every technician uses a different free app, nobody can tell which sessions were legitimate.
Section 6 sets how people sign in:
Network Level Authentication makes the user prove who they are before Windows builds a remote session, so an unauthenticated attacker can't reach the login screen. It is on by default in current Windows versions; the policy keeps it that way and makes any exception a written one.
Section 7 lists what a device needs before it may connect:
| Requirement | What it means (example values in brackets) |
|---|---|
| Managed | Enrolled in [the device management console] and listed in the device inventory with an owner and serial number |
| Encrypted | Full-disk encryption on (BitLocker, FileVault, LUKS) or, on phones, a passcode with storage encryption on |
| Patched | Operating system and third-party updates installed within [14 days], critical fixes within [72 hours] |
| Protected | Endpoint protection running and its alerts reviewed |
| Locked | Screen lock after [5 minutes] idle; the device is never left signed in and unattended |
"Managed" is the requirement that makes the others checkable: a device in your management console shows its owner, encryption status and patch level, so you can tell before you grant access. Our data encryption policy template sets the encryption rules in detail.
Section 8 covers what happens once someone is connected:
| Rule | Requirement |
|---|---|
| Idle timeout | Remote sessions disconnect after [15 minutes] without input; PCI DSS asks for re-authentication after 15 minutes idle in the cardholder data environment |
| Session length | VPN and gateway sessions re-authenticate after [12 hours] |
| Clipboard and drive redirection | Off by default on RD Gateway and hosts that hold sensitive data; on only with an approved need |
| Printing and file transfer | No local printing or file copy from systems with sensitive data over remote desktop |
| Support sessions | IT tells the user before viewing or controlling their device and gets their agreement when the user is present; unattended access only to company devices, with a ticket |
| Recording | Record or keep a transcript of privileged and vendor sessions where your tools allow it; tell users which sessions are recorded |
Clipboard and drive redirection are how files leave a remote desktop session. Turning them off on systems that hold patient records or card data closes that path. Remote support sessions need their own rule because IT is looking at a user's screen, which may show personal messages: tell the user first, and keep unattended access for company devices with a ticket behind it.
For Windows hosts, our guide on enabling Remote Desktop with Group Policy shows where NLA, timeouts and redirection are set.
Vendor accounts are a common gap: a support contract ends, and the vendor's VPN account keeps working for another year. Section 9 sets these rules:
PCI DSS v4.0.1 requirement 8.2.7 says accounts that third parties use for remote access are enabled only for the time they are needed and monitored while in use. The same rule fits any vendor account. The register's Third-Party Access tab flags any vendor whose end date has passed while the account is still on. Our vendor management policy template covers the contract side, and third-party risk management the wider assessment.
Admin access to servers, network devices, cloud consoles and the device management console carries more risk than an employee opening a file share. Section 10 says:
Just-in-time access fits here: instead of a standing admin account, a person gets access to one server for the hours the task needs, and the grant ends by itself. If your tools don't offer that, a dedicated admin account with MFA and a reviewed admin list is the minimum.
Most remote access starts with a connection layer: a company VPN or a zero trust network access (ZTNA) service that checks the user and device before each application. Section 11 of the template says staff connect through it with MFA from managed devices, and stops there. Which VPN clients and protocols you allow, split versus full tunneling, always-on VPN and VPN accounts belong in the VPN policy template, which pairs with this one. For the choice between the two models, see zero trust vs VPN; for a first setup, how to set up a VPN for a small business.
Section 12 asks for a log of every remote sign-in, failed or successful, with the session's start and end, the user, the source and the target system, and a weekly look for odd hours, new countries and repeated failures. It also asks for a monthly check that nothing answers on RDP, SSH or VNC from the internet, which is what the register's Exposure Check tab records.
Personal devices (section 13) connect only as the BYOD policy allows, to a short list of apps, never with full network access or admin rights. When a device is lost (section 14), IT cuts the user's VPN sessions and tokens first, then locks or wipes the device and records what it held. The data breach response plan takes over if data may be exposed, and an incident report records the event.
Some systems can't follow every rule. An imaging viewer may need NLA off until its next upgrade, or a billing team may need a longer session timeout for large uploads. Section 15 lets the policy owner approve an exception with a compensating control and an expiry date no more than 12 months out, and says no exception ever allows RDP open to the internet. Section 16 lets IT suspend remote access at once if an account looks compromised, and section 17 sets a yearly review.
Appendix A is a one-page monthly check with 14 lines. Six of them:
Appendix D is the form every user signs before getting remote access. It lists six commitments in plain words: connect only through approved methods, use MFA and never share an account, connect only from allowed devices, lock the screen, report a lost device or a session you didn't start, and accept that sessions are logged. Signed forms go in the HR file, and a new form is signed when the policy changes in a way that affects users.
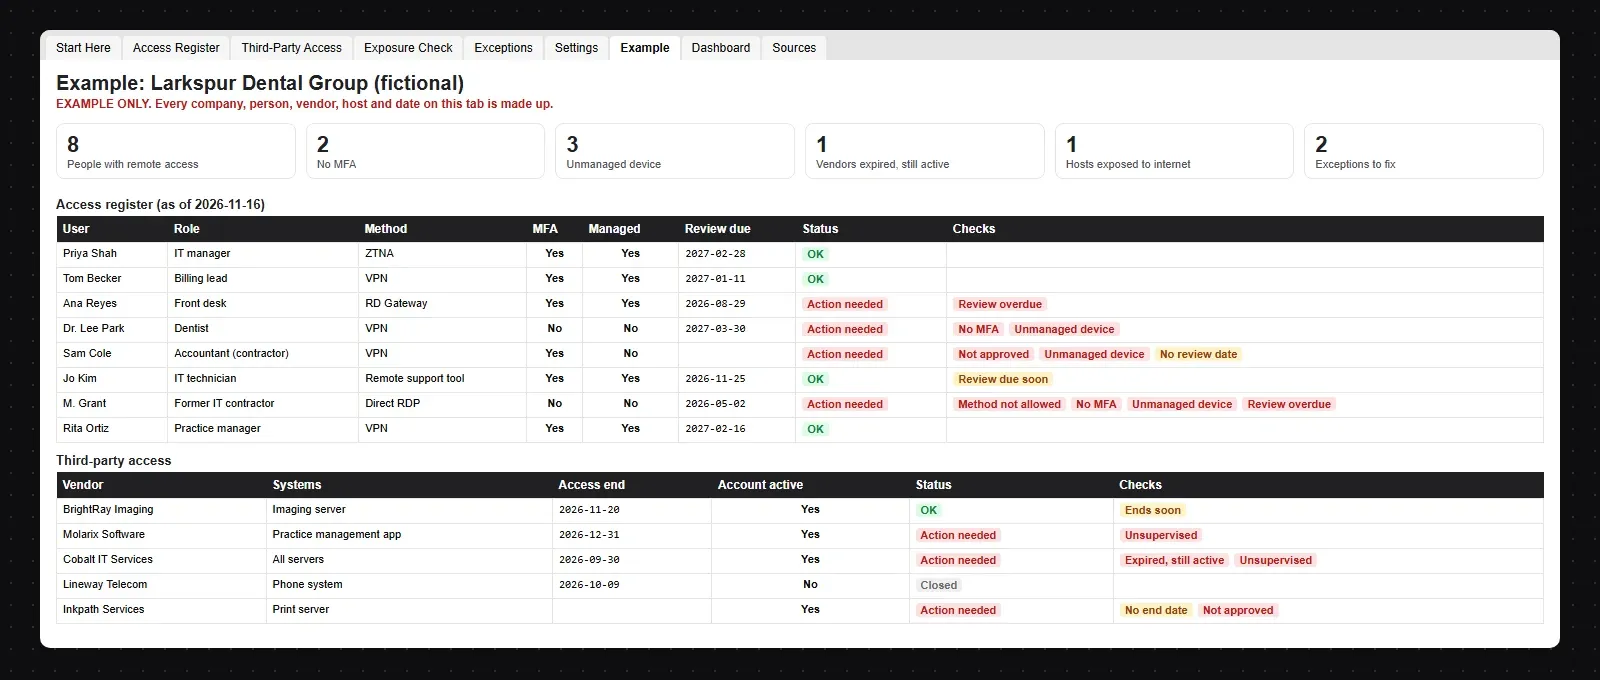
The download includes the policy filled in for Larkspur Dental Group (fictional), a made-up 180-person dental group with four clinics, a practice management server, an imaging server and an RD Gateway. Part of its monthly check on 16 November:
| Person | Method | Result |
|---|---|---|
| Ana Reyes | RD Gateway | Review overdue |
| Dr. Lee Park | VPN | No MFA, Unmanaged device |
| Sam Cole | VPN | Not approved, Unmanaged device, No review date |
| M. Grant | Direct RDP | Method not allowed, No MFA, Unmanaged device, Review overdue |
8 people have remote access and 4 have no open issue. The worst row is a former IT contractor whose contract ended in June: the account still connects by direct RDP, without MFA, to the backup server. The same check found that server answering on port 3389 from the internet, through a firewall rule made for that contractor.
| Vendor | Result |
|---|---|
| BrightRay Imaging | Ends soon |
| Molarix Software | Unsupervised |
| Cobalt IT Services | Expired, still active, Unsupervised |
| Lineway Telecom | Closed |
| Inkpath Services | No end date, Not approved |
The former MSP's contract ended on 30 September and its VPN account is still active. The practice software vendor's sessions aren't watched, and the exception that allowed that expired in August. A printer service was set up by the front desk with no end date and no approval.
The workbook turns the policy into a monthly list of things to fix:
Every common framework has remote access rules, and none of them names a product. The template's mapping table (Appendix F) points each section to these references:
| Framework | Where remote access appears |
|---|---|
| ISO/IEC 27001:2022 | A.6.7 remote working, A.8.5 secure authentication and A.8.20 networks security, with A.5.15 and A.8.2 for access and privileged rights, A.5.19 and A.5.20 for suppliers and A.8.15 for logging. |
| NIST | SP 800-46 Rev. 2 (telework, remote access and BYOD security) and SP 800-53 Rev. 5 AC-17 remote access, whose enhancements cover monitoring, cryptographic protection, managed access points and privileged commands. |
| CIS Controls v8.1 | 6.4 MFA for remote network access, 12.7 remote devices on a VPN connected to your AAA infrastructure, 13.5 access control for remote assets. |
| HIPAA Security Rule | 164.312(a)(2)(iii) logoff after inactivity (addressable), 164.312(b) audit controls, 164.312(d) person or entity authentication, 164.312(e)(1) transmission security. |
| PCI DSS v4.0.1 | 8.2.7 third-party remote access accounts, 8.2.8 re-authentication after 15 minutes idle, 8.4.3 MFA for remote network access from outside your network. |
Cyber insurance questionnaires ask the same things in plainer words: is RDP exposed, is MFA on for remote access, is vendor access controlled. The mapping is a general guide; your auditor or counsel decides what counts for your scope.
trio.so is not a VPN, a ZTNA service or an RD Gateway. What it covers is the device side of this policy and its own remote tools: keeping the devices people connect from managed, encrypted and patched, and giving IT remote desktop and terminal sessions that only the right roles can start and that leave a record. In practice that means:
It manages Windows, macOS, Linux, iOS/iPadOS and Android from one console. Our page on remote control in MDM shows how remote sessions work from a device console. Plans start at $5 per device.
14-day free trial. No credit card required.
Sources. Last reviewed November 2026. Framework references are short pointers to ISO/IEC 27001:2022, NIST SP 800-46 and SP 800-53, the CIS Controls, the HIPAA Security Rule and PCI DSS v4.0.1; the wording of every section is ours. trio.so is not affiliated with or endorsed by ISO, NIST, the Center for Internet Security, HHS or the PCI Security Standards Council.
trio.so gives IT remote desktop and a remote terminal for Windows, macOS and Linux, limited to roles with the remote desktop permission, with every session start and end in the audit log.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.
trio.so brings device management, patching and security policies for Windows, macOS, Linux, iOS/iPadOS and Android into one console. Enroll a device and see it in the console within minutes.





Have questions? We've got answers. This section covers some of the most commonly asked questions related to this topic.
Related
The related industry news, interviews, technologies, and resources.
Free social media policy template for employees in Word and PDF: personal and official accounts, account security and a hacked-account checklist.
Free mobile app security policy in Word and PDF: approved app sources, app vetting, blocked apps and permissions, plus an Excel app register.
Free access control policy template with joiner, mover and leaver steps, an RBAC matrix, privileged access rules and ISO 27001 and NIST mapping.
Create an effective Service Level Agreement (SLA) template to ensure a clear and mutually beneficial service relationship between providers and clients.
Free IT governance policy template in Word and PDF, with an Excel tracker: 17 sections, a RACI, decision rights, KPIs and a framework example.
Free Wi-Fi policy template in Word and PDF, with an Excel tracker: 17 sections on SSIDs, WPA3, guest terms of use, BYOD and rogue AP checks.
Free antivirus and anti-malware policy template in Word and PDF, with a baseline checklist, a filled-in example and an Excel endpoint coverage tracker.
A free compliance checklist template for IT teams: ten areas with owners, status and evidence, plus an Excel workbook, framework crosswalk and Word guide.
14-day free trial. No credit card required.
trio.so for MSPs: one console, separate clients